Security Hub CSPM
| Version | 7.1.5 (View all) |
| Managed integration release status |
|
| Subscription level What's this? |
Basic |
| Ingestion method(s) | API, AWS CloudWatch, AWS S3 |
| Minimum Kibana version(s) | 9.4.0 |
You can use this integration as an Elastic Managed integration on Elastic Cloud Hosted deployments running this version or later.
The AWS Security Hub CSPM integration collects and parses data from AWS Security Hub REST APIs.
Extra AWS charges on API requests will be generated by this integration. Check API Requests for more details.
Agentless integrations allow you to collect data without having to manage Elastic Agent in your cloud. They make manual agent deployment unnecessary, so you can focus on your data instead of the agent that collects it. For more information, refer to Agentless integrations and the Agentless integrations FAQ. Agentless deployments are only supported in Elastic Serverless and Elastic Cloud environments. This functionality is in beta and is subject to change. Beta features are not subject to the support SLA of official GA features.
- The minimum compatible version of this module is
Elastic Agent 9.4.0. - This module is tested against
AWS Security Hub API version 1.0.
The data streams authenticate with the standard AWS credential methods described in AWS Credentials: an access key pair, temporary security credentials, a shared credentials file, or an IAM role to assume. To create an access key pair:
- Login to https://console.aws.amazon.com/.
- Go to https://console.aws.amazon.com/iam/ to access the IAM console.
- On the navigation menu, choose Users.
- Choose your IAM user name.
- Select Create access key from the Security Credentials tab.
- To see the new access key, choose Show.
- For the current integration package, it is recommended to have interval in hours.
- AWS credentials are required; any of the supported credential methods listed above can be used.
- Findings Full Posture data stream request all the historical findings every 24 hours.
- The Findings and Findings Full Posture data streams collect from the
GetFindingsAPI using the CEL input with native AWS SigV4 signing (auth.aws). The Insights data stream also signs requests withauth.aws.
The Findings and Findings Full Posture data streams page through the GetFindings API using the CEL input, which caps the number of pages fetched per collection interval at the Maximum Executions value (each page returns up to 100 findings). When an account holds more findings than the cap allows, the agent logs reached maximum number of CEL executions: will continue at next periodic evaluation and stops paging for that interval.
For the Findings stream this is usually self-correcting: collection is incremental, so the next interval resumes where the previous one stopped. For Findings Full Posture, which re-reads the full current posture on each run, a very large account may not finish a sweep within one interval.
To resolve this, increase Maximum Executions in the data stream's advanced settings (it must be a positive integer). For the Findings stream, shortening the collection interval also reduces the pages per run, since each run then covers fewer new findings. For Findings Full Posture the interval does not change the sweep size; instead raise Maximum Executions or narrow the result set with the Findings Filters setting.
This is the securityhub_findings data stream. Findings are collected incrementally using the finding's UpdatedAt timestamp, which the integration manages automatically.
Use the Findings Filters setting to apply additional server-side AwsSecurityFindingFilters so that only matching findings are collected (for example, to restrict collection by SeverityLabel or RecordState). Provide a YAML or JSON object using the AWS AwsSecurityFindingFilters shape; the UpdatedAt filter is reserved for incremental collection and takes precedence over any UpdatedAt supplied here.
Example
{
"@timestamp": "2018-08-31T00:15:09.000Z",
"agent": {
"ephemeral_id": "5e7fb029-e3ac-4031-81d7-6128857c791d",
"id": "109a7ecc-0a7c-4861-bac4-c3f80aa1fe09",
"name": "elastic-agent-15024",
"type": "filebeat",
"version": "9.4.0"
},
"aws": {
"securityhub_findings": {
"action": {
"port_probe": {
"blocked": false,
"details": {
"local": {
"ip": {
"address_v4": "1.128.0.0"
},
"port": {
"name": "HTTP",
"number": 80
}
},
"remote_ip": {
"city": {
"name": "Example City"
},
"country": {
"name": "Example Country"
},
"geolocation": {
"latitude": 0,
"longitude": 0
},
"organization": {
"asn": "64496",
"asn_organization": "ExampleASO",
"internet_provider": "ExampleOrg",
"internet_service_provider": "ExampleISP"
}
}
}
}
},
"aws_account_id": "111111111111",
"company": {
"name": "AWS"
},
"compliance": {
"related_requirements": [
"Req1",
"Req2"
],
"status": "PASSED",
"status_reasons": {
"description": "CloudWatch alarms do not exist in the account",
"reason_code": "CLOUDWATCH_ALARMS_NOT_PRESENT"
}
},
"confidence": 42,
"criticality": 99,
"description": "The version of openssl found on instance i-abcd1234 is known to contain a vulnerability.",
"first_observed_at": "2017-03-22T13:22:13.933Z",
"generator": {
"id": "acme-vuln-9ab348"
},
"last_observed_at": "2017-03-23T13:22:13.933Z",
"malware": {
"name": "Stringler",
"path": "/usr/sbin/stringler",
"state": "OBSERVED",
"type": "COIN_MINER"
},
"network": {
"open_port_range": {
"begin": 443,
"end": 443
}
},
"network_path": {
"component": {
"id": "abc-01a234bc56d8901ee",
"type": "AWS::EC2::InternetGateway"
},
"egress": {
"destination": {
"address": "1.128.0.0/24",
"port_ranges": {
"begin": 443,
"end": 443
}
},
"protocol": "TCP",
"source": {
"address": "175.16.199.1/24"
}
},
"ingress": {
"destination": {
"address": "175.16.199.1/24",
"port_ranges": {
"begin": 443,
"end": 443
}
},
"protocol": "TCP",
"source": {
"address": "175.16.199.1/24"
}
}
},
"note": {
"text": "Don't forget to check under the mat.",
"updated_at": "2018-08-31T00:15:09.000Z",
"updated_by": "jsmith"
},
"patch_summary": {
"failed": {
"count": 0
},
"id": "pb-123456789098",
"installed": {
"count": 100,
"other": {
"count": 1023
},
"pending_reboot": 0,
"rejected": {
"count": 0
}
},
"missing": {
"count": 100
},
"operation": {
"end_time": "2018-09-27T23:39:31.000Z",
"start_time": "2018-09-27T23:37:31.000Z",
"type": "Install"
},
"reboot_option": "RebootIfNeeded"
},
"product": {
"arn": "arn:aws:securityhub:us-east-1:111111111111:product/111111111111/default",
"fields": {
"Service_Name": "cloudtrail.amazonaws.com",
"aws/inspector/AssessmentTargetName": "My prod env",
"aws/inspector/AssessmentTemplateName": "My daily CVE assessment",
"aws/inspector/RulesPackageName": "Common Vulnerabilities and Exposures",
"generico/secure-pro/Count": "6"
},
"name": "Security Hub"
},
"provider_fields": {
"confidence": 42,
"criticality": 99,
"related_findings": {
"id": "123e4567-e89b-12d3-a456-426655440000",
"product": {
"arn": "arn:aws:securityhub:us-west-2::product/aws/guardduty"
}
},
"severity": {
"label": "MEDIUM",
"original": "MEDIUM"
},
"types": "Software and Configuration Checks/Vulnerabilities/CVE"
},
"record_state": "ACTIVE",
"region": "us-east-1",
"related_findings": {
"id": [
"123e4567-e89b-12d3-a456-426655440000",
"AcmeNerfHerder-111111111111-x189dx7824"
],
"product": {
"arn": [
"arn:aws:securityhub:us-west-2::product/aws/guardduty",
"arn:aws:securityhub:us-west-2::product/aws/guardduty"
]
}
},
"remediation": {
"recommendation": {
"text": "Run sudo yum update and cross your fingers and toes.",
"url": "http://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html"
}
},
"resources": {
"Details": {
"IamInstanceProfileArn": "arn:aws:iam::123456789012:role/IamInstanceProfileArn",
"ImageId": "ami-79fd7eee",
"IpV4Addresses": [
"175.16.199.1"
],
"IpV6Addresses": [
"2a02:cf40::"
],
"KeyName": "testkey",
"LaunchedAt": "2018-09-29T01:25:54Z",
"MetadataOptions": {
"HttpEndpoint": "enabled",
"HttpProtocolIpv6": "enabled",
"HttpPutResponseHopLimit": 1,
"HttpTokens": "optional",
"InstanceMetadataTags": "disabled"
},
"NetworkInterfaces": [
{
"NetworkInterfaceId": "eni-e5aa89a3"
}
],
"SubnetId": "PublicSubnet",
"Type": "i3.xlarge",
"VirtualizationType": "hvm",
"VpcId": "TestVPCIpv6"
},
"Id": "i-cafebabe",
"Partition": "aws",
"Region": "us-west-2",
"Tags": {
"billingCode": "Lotus-1-2-3",
"needsPatching": "true"
},
"Type": "AwsEc2Instance"
},
"sample": true,
"schema": {
"version": "2018-10-08"
},
"severity": {
"label": "CRITICAL",
"original": "8.3"
},
"source_url": "http://threatintelweekly.org/backdoors/8888",
"threat_intel_indicators": {
"category": "BACKDOOR",
"source": "Threat Intel Weekly",
"source_url": "http://threatintelweekly.org/backdoors/8888",
"value": "175.16.199.1"
},
"title": "EC2.20 Both VPN tunnels for an AWS Site-to-Site VPN connection should be up",
"types": "Software and Configuration Checks/Vulnerabilities/CVE",
"updated_at": "2018-08-31T00:15:09.000Z",
"user_defined_fields": {
"comeBackToLater": "Check this again on Monday",
"reviewedByCio": "true"
},
"verification_state": "UNKNOWN",
"vulnerabilities": {
"cvss": {
"base_score": [
4.7,
4.7
],
"base_vector": [
"AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N",
"AV:L/AC:M/Au:N/C:C/I:N/A:N"
],
"version": [
"V3",
"V2"
]
},
"related_vulnerabilities": "CVE-2020-12345",
"vendor": {
"created_at": "2020-01-16T00:01:43.000Z",
"severity": "Medium",
"updated_at": "2020-01-16T00:01:43.000Z",
"url": "https://alas.aws.amazon.com/ALAS-2020-1337.html"
},
"vulnerable_packages": {
"architecture": "x86_64",
"epoch": "1",
"name": "openssl",
"release": "16.amzn2.0.3",
"version": "1.0.2k"
}
},
"workflow": {
"state": "NEW",
"status": "NEW"
}
}
},
"cloud": {
"account": {
"id": "111111111111"
},
"instance": {
"id": "i-cafebabe",
"name": "i-cafebabe"
},
"provider": "aws",
"region": "us-east-1"
},
"data_stream": {
"dataset": "aws.securityhub_findings",
"namespace": "90434",
"type": "logs"
},
"destination": {
"domain": "example2.com",
"ip": [
"1.128.0.0",
"2a02:cf40::"
],
"port": 80
},
"ecs": {
"version": "8.11.0"
},
"elastic_agent": {
"id": "109a7ecc-0a7c-4861-bac4-c3f80aa1fe09",
"snapshot": false,
"version": "9.4.0"
},
"event": {
"action": "port_probe",
"agent_id_status": "verified",
"category": [
"configuration"
],
"dataset": "aws.securityhub_findings",
"id": "us-west-2/111111111111/98aebb2207407c87f51e89943f12b1ef",
"ingested": "2026-10-08T06:40:37Z",
"kind": "state",
"module": "aws",
"original": "{\"Action\":{\"ActionType\":\"PORT_PROBE\",\"PortProbeAction\":{\"Blocked\":false,\"PortProbeDetails\":[{\"LocalIpDetails\":{\"IpAddressV4\":\"1.128.0.0\"},\"LocalPortDetails\":{\"Port\":80,\"PortName\":\"HTTP\"},\"RemoteIpDetails\":{\"City\":{\"CityName\":\"Example City\"},\"Country\":{\"CountryName\":\"Example Country\"},\"GeoLocation\":{\"Lat\":0,\"Lon\":0},\"Organization\":{\"Asn\":64496,\"AsnOrg\":\"ExampleASO\",\"Isp\":\"ExampleISP\",\"Org\":\"ExampleOrg\"}}}]}},\"AwsAccountId\":\"111111111111\",\"CompanyName\":\"AWS\",\"Compliance\":{\"RelatedRequirements\":[\"Req1\",\"Req2\"],\"Status\":\"PASSED\",\"StatusReasons\":[{\"Description\":\"CloudWatch alarms do not exist in the account\",\"ReasonCode\":\"CLOUDWATCH_ALARMS_NOT_PRESENT\"}]},\"Confidence\":42,\"CreatedAt\":\"2017-03-22T13:22:13.933Z\",\"Criticality\":99,\"Description\":\"The version of openssl found on instance i-abcd1234 is known to contain a vulnerability.\",\"FindingProviderFields\":{\"Confidence\":42,\"Criticality\":99,\"RelatedFindings\":[{\"Id\":\"123e4567-e89b-12d3-a456-426655440000\",\"ProductArn\":\"arn:aws:securityhub:us-west-2::product/aws/guardduty\"}],\"Severity\":{\"Label\":\"MEDIUM\",\"Original\":\"MEDIUM\"},\"Types\":[\"Software and Configuration Checks/Vulnerabilities/CVE\"]},\"FirstObservedAt\":\"2017-03-22T13:22:13.933Z\",\"GeneratorId\":\"acme-vuln-9ab348\",\"Id\":\"us-west-2/111111111111/98aebb2207407c87f51e89943f12b1ef\",\"LastObservedAt\":\"2017-03-23T13:22:13.933Z\",\"Malware\":[{\"Name\":\"Stringler\",\"Path\":\"/usr/sbin/stringler\",\"State\":\"OBSERVED\",\"Type\":\"COIN_MINER\"}],\"Network\":{\"DestinationDomain\":\"example2.com\",\"DestinationIpV4\":\"1.128.0.0\",\"DestinationIpV6\":\"2a02:cf40::\",\"DestinationPort\":\"80\",\"Direction\":\"IN\",\"OpenPortRange\":{\"Begin\":443,\"End\":443},\"Protocol\":\"TCP\",\"SourceDomain\":\"example1.com\",\"SourceIpV4\":\"1.128.0.0\",\"SourceIpV6\":\"2a02:cf40::\",\"SourceMac\":\"00:0d:83:b1:c0:8e\",\"SourcePort\":\"42\"},\"NetworkPath\":[{\"ComponentId\":\"abc-01a234bc56d8901ee\",\"ComponentType\":\"AWS::EC2::InternetGateway\",\"Egress\":{\"Destination\":{\"Address\":[\"1.128.0.0/24\"],\"PortRanges\":[{\"Begin\":443,\"End\":443}]},\"Protocol\":\"TCP\",\"Source\":{\"Address\":[\"175.16.199.1/24\"]}},\"Ingress\":{\"Destination\":{\"Address\":[\"175.16.199.1/24\"],\"PortRanges\":[{\"Begin\":443,\"End\":443}]},\"Protocol\":\"TCP\",\"Source\":{\"Address\":[\"175.16.199.1/24\"]}}}],\"Note\":{\"Text\":\"Don't forget to check under the mat.\",\"UpdatedAt\":\"2018-08-31T00:15:09Z\",\"UpdatedBy\":\"jsmith\"},\"PatchSummary\":{\"FailedCount\":\"0\",\"Id\":\"pb-123456789098\",\"InstalledCount\":\"100\",\"InstalledOtherCount\":\"1023\",\"InstalledPendingReboot\":\"0\",\"InstalledRejectedCount\":\"0\",\"MissingCount\":\"100\",\"Operation\":\"Install\",\"OperationEndTime\":\"2018-09-27T23:39:31Z\",\"OperationStartTime\":\"2018-09-27T23:37:31Z\",\"RebootOption\":\"RebootIfNeeded\"},\"Process\":{\"LaunchedAt\":\"2018-09-27T22:37:31Z\",\"Name\":\"syslogd\",\"ParentPid\":56789,\"Path\":\"/usr/sbin/syslogd\",\"Pid\":12345,\"TerminatedAt\":\"2018-09-27T23:37:31Z\"},\"ProductArn\":\"arn:aws:securityhub:us-east-1:111111111111:product/111111111111/default\",\"ProductFields\":{\"Service_Name\":\"cloudtrail.amazonaws.com\",\"aws/inspector/AssessmentTargetName\":\"My prod env\",\"aws/inspector/AssessmentTemplateName\":\"My daily CVE assessment\",\"aws/inspector/RulesPackageName\":\"Common Vulnerabilities and Exposures\",\"generico/secure-pro/Count\":\"6\"},\"ProductName\":\"Security Hub\",\"RecordState\":\"ACTIVE\",\"Region\":\"us-east-1\",\"RelatedFindings\":[{\"Id\":\"123e4567-e89b-12d3-a456-426655440000\",\"ProductArn\":\"arn:aws:securityhub:us-west-2::product/aws/guardduty\"},{\"Id\":\"AcmeNerfHerder-111111111111-x189dx7824\",\"ProductArn\":\"arn:aws:securityhub:us-west-2::product/aws/guardduty\"}],\"Remediation\":{\"Recommendation\":{\"Text\":\"Run sudo yum update and cross your fingers and toes.\",\"Url\":\"http://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html\"}},\"Resources\":[{\"Details\":{\"IamInstanceProfileArn\":\"arn:aws:iam::123456789012:role/IamInstanceProfileArn\",\"ImageId\":\"ami-79fd7eee\",\"IpV4Addresses\":[\"175.16.199.1\"],\"IpV6Addresses\":[\"2a02:cf40::\"],\"KeyName\":\"testkey\",\"LaunchedAt\":\"2018-09-29T01:25:54Z\",\"MetadataOptions\":{\"HttpEndpoint\":\"enabled\",\"HttpProtocolIpv6\":\"enabled\",\"HttpPutResponseHopLimit\":1,\"HttpTokens\":\"optional\",\"InstanceMetadataTags\":\"disabled\"},\"NetworkInterfaces\":[{\"NetworkInterfaceId\":\"eni-e5aa89a3\"}],\"SubnetId\":\"PublicSubnet\",\"Type\":\"i3.xlarge\",\"VirtualizationType\":\"hvm\",\"VpcId\":\"TestVPCIpv6\"},\"Id\":\"i-cafebabe\",\"Partition\":\"aws\",\"Region\":\"us-west-2\",\"Tags\":{\"billingCode\":\"Lotus-1-2-3\",\"needsPatching\":\"true\"},\"Type\":\"AwsEc2Instance\"}],\"Sample\":true,\"SchemaVersion\":\"2018-10-08\",\"Severity\":{\"Label\":\"CRITICAL\",\"Original\":\"8.3\"},\"SourceUrl\":\"http://threatintelweekly.org/backdoors/8888\",\"ThreatIntelIndicators\":[{\"Category\":\"BACKDOOR\",\"LastObservedAt\":\"2018-09-27T23:37:31Z\",\"Source\":\"Threat Intel Weekly\",\"SourceUrl\":\"http://threatintelweekly.org/backdoors/8888\",\"Type\":\"IPV4_ADDRESS\",\"Value\":\"175.16.199.1\"}],\"Threats\":[{\"FilePaths\":[{\"FileName\":\"b.txt\",\"FilePath\":\"/tmp/b.txt\",\"Hash\":\"sha256\",\"ResourceId\":\"arn:aws:ec2:us-west-2:123456789012:volume/vol-032f3bdd89aee112f\"}],\"ItemCount\":3,\"Name\":\"Iot.linux.mirai.vwisi\",\"Severity\":\"HIGH\"}],\"Title\":\"EC2.20 Both VPN tunnels for an AWS Site-to-Site VPN connection should be up\",\"Types\":[\"Software and Configuration Checks/Vulnerabilities/CVE\"],\"UpdatedAt\":\"2018-08-31T00:15:09Z\",\"UserDefinedFields\":{\"comeBackToLater\":\"Check this again on Monday\",\"reviewedByCio\":\"true\"},\"VerificationState\":\"UNKNOWN\",\"Vulnerabilities\":[{\"Cvss\":[{\"BaseScore\":4.7,\"BaseVector\":\"AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N\",\"Version\":\"V3\"},{\"BaseScore\":4.7,\"BaseVector\":\"AV:L/AC:M/Au:N/C:C/I:N/A:N\",\"Version\":\"V2\"}],\"Id\":\"CVE-2020-12345\",\"ReferenceUrls\":[\"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-12418\",\"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17563\"],\"RelatedVulnerabilities\":[\"CVE-2020-12345\"],\"Vendor\":{\"Name\":\"Alas\",\"Url\":\"https://alas.aws.amazon.com/ALAS-2020-1337.html\",\"VendorCreatedAt\":\"2020-01-16T00:01:43Z\",\"VendorSeverity\":\"Medium\",\"VendorUpdatedAt\":\"2020-01-16T00:01:43Z\"},\"VulnerablePackages\":[{\"Architecture\":\"x86_64\",\"Epoch\":\"1\",\"Name\":\"openssl\",\"Release\":\"16.amzn2.0.3\",\"Version\":\"1.0.2k\"}]}],\"Workflow\":{\"Status\":\"NEW\"},\"WorkflowState\":\"NEW\"}",
"outcome": "success",
"type": [
"info"
]
},
"host": {
"id": "i-cafebabe"
},
"input": {
"type": "httpjson"
},
"network": {
"direction": "inbound",
"protocol": "tcp"
},
"observer": {
"vendor": "AWS Security Hub CSPM"
},
"organization": {
"name": "AWS"
},
"process": {
"end": "2018-09-27T23:37:31.000Z",
"executable": "/usr/sbin/syslogd",
"name": "syslogd",
"parent": {
"pid": 56789
},
"pid": 12345,
"start": "2018-09-27T22:37:31.000Z"
},
"related": {
"ip": [
"1.128.0.0",
"2a02:cf40::"
]
},
"resource": {
"id": "i-cafebabe",
"name": "i-cafebabe",
"type": "AwsEc2Instance"
},
"result": {
"evaluation": "passed"
},
"rule": {
"description": "The version of openssl found on instance i-abcd1234 is known to contain a vulnerability.",
"id": "acme-vuln-9ab348",
"name": "EC2.20 Both VPN tunnels for an AWS Site-to-Site VPN connection should be up",
"reference": "http://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html",
"remediation": "Run sudo yum update and cross your fingers and toes.\r\nhttp://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html",
"ruleset": [
"Req1",
"Req2"
]
},
"source": {
"domain": "example1.com",
"ip": [
"1.128.0.0",
"2a02:cf40::"
],
"mac": "00-0D-83-B1-C0-8E",
"port": 42
},
"tags": [
"run_as_cel",
"preserve_original_event",
"forwarded",
"aws_securityhub_findings"
],
"threat": {
"indicator": {
"last_seen": "2018-09-27T23:37:31.000Z",
"type": "ipv4-addr"
}
},
"url": {
"domain": "threatintelweekly.org",
"full": "http://threatintelweekly.org/backdoors/8888",
"original": "http://threatintelweekly.org/backdoors/8888",
"path": "/backdoors/8888",
"scheme": "http"
},
"vulnerability": {
"id": "CVE-2020-12345",
"reference": [
"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-12418",
"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17563"
],
"scanner": {
"vendor": "Alas"
},
"score": {
"base": 4.7,
"version": "V2"
}
}
}
ECS Field Reference
Please refer to the following document for detailed information on ECS fields.
Exported fields
| Field | Description | Type |
|---|---|---|
| @timestamp | Date/time when the event originated. This is the date/time extracted from the event, typically representing when the event was generated by the source. If the event source has no original timestamp, this value is typically populated by the first time the event was received by the pipeline. Required field for all events. | date |
| aws.securityhub_findings.action.aws_api_call.affected_resources | Identifies the resources that were affected by the API call. | flattened |
| aws.securityhub_findings.action.aws_api_call.api | The name of the API method that was issued. | keyword |
| aws.securityhub_findings.action.aws_api_call.caller.type | Indicates whether the API call originated from a remote IP address(remoteip) or from a DNS domain(domain). | keyword |
| aws.securityhub_findings.action.aws_api_call.domain_details.domain | The name of the DNS domain that issued the API call. | keyword |
| aws.securityhub_findings.action.aws_api_call.first_seen | An ISO8601-formatted timestamp that indicates when the API call was first observed. | date |
| aws.securityhub_findings.action.aws_api_call.last_seen | An ISO8601-formatted timestamp that indicates when the API call was most recently observed. | date |
| aws.securityhub_findings.action.aws_api_call.remote_ip.city.name | The name of the city. | keyword |
| aws.securityhub_findings.action.aws_api_call.remote_ip.country.code | The 2-letter ISO 3166 country code for the country. | keyword |
| aws.securityhub_findings.action.aws_api_call.remote_ip.country.name | The name of the country. | keyword |
| aws.securityhub_findings.action.aws_api_call.remote_ip.geolocation.latitude | The longitude of the location. | double |
| aws.securityhub_findings.action.aws_api_call.remote_ip.geolocation.longitude | The latitude of the location. | double |
| aws.securityhub_findings.action.aws_api_call.remote_ip.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings.action.aws_api_call.remote_ip.organization.asn | The Autonomous System Number(ASN) of the internet provider. | keyword |
| aws.securityhub_findings.action.aws_api_call.remote_ip.organization.asn_organization | The name of the organization that registered the ASN. | keyword |
| aws.securityhub_findings.action.aws_api_call.remote_ip.organization.internet_provider | The ISP information for the internet provider. | keyword |
| aws.securityhub_findings.action.aws_api_call.remote_ip.organization.internet_service_provider | The name of the internet provider. | keyword |
| aws.securityhub_findings.action.aws_api_call.service.name | The name of the Amazon Web Services service that the API method belongs to. | keyword |
| aws.securityhub_findings.action.dns_request.blocked | Indicates whether the DNS request was blocked. | boolean |
| aws.securityhub_findings.action.dns_request.domain | The DNS domain that is associated with the DNS request. | keyword |
| aws.securityhub_findings.action.dns_request.protocol | The protocol that was used for the DNS request. | keyword |
| aws.securityhub_findings.action.network_connection.blocked | Indicates whether the network connection attempt was blocked. | boolean |
| aws.securityhub_findings.action.network_connection.direction | The direction of the network connection request(IN or OUT). | keyword |
| aws.securityhub_findings.action.network_connection.local.port.name | The port name of the local connection. | keyword |
| aws.securityhub_findings.action.network_connection.local.port.number | The number of the port. | long |
| aws.securityhub_findings.action.network_connection.protocol | The protocol used to make the network connection request. | keyword |
| aws.securityhub_findings.action.network_connection.remote.port.name | The port name of the remote connection. | keyword |
| aws.securityhub_findings.action.network_connection.remote.port.number | The number of the port. | long |
| aws.securityhub_findings.action.network_connection.remote_ip.city.name | The name of the city. | keyword |
| aws.securityhub_findings.action.network_connection.remote_ip.country.code | The 2-letter ISO 3166 country code for the country. | keyword |
| aws.securityhub_findings.action.network_connection.remote_ip.country.name | The name of the country. | keyword |
| aws.securityhub_findings.action.network_connection.remote_ip.geolocation.latitude | The longitude of the location. | double |
| aws.securityhub_findings.action.network_connection.remote_ip.geolocation.longitude | The latitude of the location. | double |
| aws.securityhub_findings.action.network_connection.remote_ip.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings.action.network_connection.remote_ip.organization.asn | The Autonomous System Number(ASN) of the internet provider. | keyword |
| aws.securityhub_findings.action.network_connection.remote_ip.organization.asn_organization | The name of the organization that registered the ASN. | keyword |
| aws.securityhub_findings.action.network_connection.remote_ip.organization.internet_provider | The ISP information for the internet provider. | keyword |
| aws.securityhub_findings.action.network_connection.remote_ip.organization.internet_service_provider | The name of the internet provider. | keyword |
| aws.securityhub_findings.action.port_probe.blocked | Indicates whether the port probe was blocked. | boolean |
| aws.securityhub_findings.action.port_probe.details.local.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings.action.port_probe.details.local.port.name | The port name of the local connection. | keyword |
| aws.securityhub_findings.action.port_probe.details.local.port.number | The number of the port. | long |
| aws.securityhub_findings.action.port_probe.details.remote_ip.city.name | The name of the city. | keyword |
| aws.securityhub_findings.action.port_probe.details.remote_ip.country.code | The 2-letter ISO 3166 country code for the country. | keyword |
| aws.securityhub_findings.action.port_probe.details.remote_ip.country.name | The name of the country. | keyword |
| aws.securityhub_findings.action.port_probe.details.remote_ip.geolocation.latitude | The longitude of the location. | double |
| aws.securityhub_findings.action.port_probe.details.remote_ip.geolocation.longitude | The latitude of the location. | double |
| aws.securityhub_findings.action.port_probe.details.remote_ip.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings.action.port_probe.details.remote_ip.organization.asn | The Autonomous System Number(ASN) of the internet provider. | keyword |
| aws.securityhub_findings.action.port_probe.details.remote_ip.organization.asn_organization | The name of the organization that registered the ASN. | keyword |
| aws.securityhub_findings.action.port_probe.details.remote_ip.organization.internet_provider | The ISP information for the internet provider. | keyword |
| aws.securityhub_findings.action.port_probe.details.remote_ip.organization.internet_service_provider | The name of the internet provider. | keyword |
| aws.securityhub_findings.action.type | The type of action that was detected. | keyword |
| aws.securityhub_findings.aws_account_id | The Amazon Web Services account ID that a finding is generated in. | keyword |
| aws.securityhub_findings.company.name | The name of the company for the product that generated the finding. | keyword |
| aws.securityhub_findings.compliance.related_requirements | For a control, the industry or regulatory framework requirements that are related to the control. | keyword |
| aws.securityhub_findings.compliance.security_control_id | Unique identifier of a control across standards. | keyword |
| aws.securityhub_findings.compliance.status | The result of a standards check. | keyword |
| aws.securityhub_findings.compliance.status_reasons.description | The corresponding description for the status reason code. | keyword |
| aws.securityhub_findings.compliance.status_reasons.reason_code | A code that represents a reason for the control status. | keyword |
| aws.securityhub_findings.confidence | A finding's confidence. Confidence is defined as the likelihood that a finding accurately identifies the behavior or issue that it was intended to identify. | long |
| aws.securityhub_findings.created_at | Indicates when the security-findings provider created the potential security issue that a finding captured. | date |
| aws.securityhub_findings.criticality | The level of importance assigned to the resources associated with the finding. | long |
| aws.securityhub_findings.description | A finding's description. | keyword |
| aws.securityhub_findings.first_observed_at | Indicates when the security-findings provider first observed the potential security issue that a finding captured. | date |
| aws.securityhub_findings.generator.id | The identifier for the solution-specific component(a discrete unit of logic) that generated a finding. In various security-findings providers' solutions, this generator can be called a rule, a check, a detector, a plugin, etc. | keyword |
| aws.securityhub_findings.id | The security findings provider-specific identifier for a finding. | keyword |
| aws.securityhub_findings.last_observed_at | Indicates when the security-findings provider most recently observed the potential security issue that a finding captured. | date |
| aws.securityhub_findings.malware.name | The name of the malware that was observed. | keyword |
| aws.securityhub_findings.malware.path | The file system path of the malware that was observed. | keyword |
| aws.securityhub_findings.malware.state | The state of the malware that was observed. | keyword |
| aws.securityhub_findings.malware.type | The type of the malware that was observed. | keyword |
| aws.securityhub_findings.network.destination.domain | The destination domain of network-related information about a finding. | keyword |
| aws.securityhub_findings.network.destination.ip.v4 | The destination IPv4 address of network-related information about a finding. | ip |
| aws.securityhub_findings.network.destination.ip.v6 | The destination IPv6 address of network-related information about a finding. | ip |
| aws.securityhub_findings.network.destination.port | The destination port of network-related information about a finding. | long |
| aws.securityhub_findings.network.direction | The direction of network traffic associated with a finding. | keyword |
| aws.securityhub_findings.network.open_port_range.begin | The first port in the port range. | long |
| aws.securityhub_findings.network.open_port_range.end | The last port in the port range. | long |
| aws.securityhub_findings.network.protocol | The protocol of network-related information about a finding. | keyword |
| aws.securityhub_findings.network.source.domain | The source domain of network-related information about a finding. | keyword |
| aws.securityhub_findings.network.source.ip.v4 | The source IPv4 address of network-related information about a finding. | ip |
| aws.securityhub_findings.network.source.ip.v6 | The source IPv6 address of network-related information about a finding. | ip |
| aws.securityhub_findings.network.source.mac | The source media access control(MAC) address of network-related information about a finding. | keyword |
| aws.securityhub_findings.network.source.port | The source port of network-related information about a finding. | long |
| aws.securityhub_findings.network_path.component.id | The identifier of a component in the network path. | keyword |
| aws.securityhub_findings.network_path.component.type | The type of component. | keyword |
| aws.securityhub_findings.network_path.egress.destination.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings.network_path.egress.destination.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings.network_path.egress.destination.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings.network_path.egress.protocol | The protocol used for the component. | keyword |
| aws.securityhub_findings.network_path.egress.source.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings.network_path.egress.source.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings.network_path.egress.source.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings.network_path.ingress.destination.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings.network_path.ingress.destination.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings.network_path.ingress.destination.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings.network_path.ingress.protocol | The protocol used for the component. | keyword |
| aws.securityhub_findings.network_path.ingress.source.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings.network_path.ingress.source.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings.network_path.ingress.source.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings.note.text | The text of a note. | keyword |
| aws.securityhub_findings.note.updated_at | The timestamp of when the note was updated. | date |
| aws.securityhub_findings.note.updated_by | The principal that created a note. | keyword |
| aws.securityhub_findings.patch_summary.failed.count | The number of patches from the compliance standard that failed to install. | long |
| aws.securityhub_findings.patch_summary.id | The identifier of the compliance standard that was used to determine the patch compliance status. | keyword |
| aws.securityhub_findings.patch_summary.installed.count | The number of patches from the compliance standard that were installed successfully. | long |
| aws.securityhub_findings.patch_summary.installed.other.count | The number of installed patches that are not part of the compliance standard. | long |
| aws.securityhub_findings.patch_summary.installed.pending_reboot | The number of patches that were applied, but that require the instance to be rebooted in order to be marked as installed. | long |
| aws.securityhub_findings.patch_summary.installed.rejected.count | The number of patches that are installed but are also on a list of patches that the customer rejected. | long |
| aws.securityhub_findings.patch_summary.missing.count | The number of patches that are part of the compliance standard but are not installed. The count includes patches that failed to install. | long |
| aws.securityhub_findings.patch_summary.operation.end_time | Indicates when the operation completed. | date |
| aws.securityhub_findings.patch_summary.operation.start_time | Indicates when the operation started. | date |
| aws.securityhub_findings.patch_summary.operation.type | The type of patch operation performed. For Patch Manager, the values are SCAN and INSTALL. | keyword |
| aws.securityhub_findings.patch_summary.reboot_option | The reboot option specified for the instance. | keyword |
| aws.securityhub_findings.process.launched_at | Indicates when the process was launched. | date |
| aws.securityhub_findings.process.name | The name of the process. | keyword |
| aws.securityhub_findings.process.parent.pid | The parent process ID. | long |
| aws.securityhub_findings.process.path | The path to the process executable. | keyword |
| aws.securityhub_findings.process.pid | The process ID. | long |
| aws.securityhub_findings.process.terminated_at | Indicates when the process was terminated. | date |
| aws.securityhub_findings.processed_at | Indicates when AWS Security Hub received a finding and begins to process it. | date |
| aws.securityhub_findings.product.arn | The ARN generated by Security Hub that uniquely identifies a product that generates findings. This can be the ARN for a third-party product that is integrated with Security Hub, or the ARN for a custom integration. | keyword |
| aws.securityhub_findings.product.fields | A data type where security-findings providers can include additional solution-specific details that aren't part of the defined AwsSecurityFinding format. | flattened |
| aws.securityhub_findings.product.name | The name of the product that generated the finding. | keyword |
| aws.securityhub_findings.provider_fields.confidence | A finding's confidence. Confidence is defined as the likelihood that a finding accurately identifies the behavior or issue that it was intended to identify. | long |
| aws.securityhub_findings.provider_fields.criticality | The level of importance assigned to the resources associated with the finding. | long |
| aws.securityhub_findings.provider_fields.related_findings.id | The product-generated identifier for a related finding. | keyword |
| aws.securityhub_findings.provider_fields.related_findings.product.arn | The ARN of the product that generated a related finding. | keyword |
| aws.securityhub_findings.provider_fields.severity.label | The severity label assigned to the finding by the finding provider. | keyword |
| aws.securityhub_findings.provider_fields.severity.normalized | The normalized severity of a finding provider. | keyword |
| aws.securityhub_findings.provider_fields.severity.original | The finding provider's original value for the severity. | keyword |
| aws.securityhub_findings.provider_fields.severity.product | The finding provider's product for the severity. | keyword |
| aws.securityhub_findings.provider_fields.types | One or more finding types in the format of namespace/category/classifier that classify a finding. | keyword |
| aws.securityhub_findings.record_state | The record state of a finding. | keyword |
| aws.securityhub_findings.region | The Region from which the finding was generated. | keyword |
| aws.securityhub_findings.related_findings.id | The product-generated identifier for a related finding. | keyword |
| aws.securityhub_findings.related_findings.product.arn | The ARN of the product that generated a related finding. | keyword |
| aws.securityhub_findings.remediation.recommendation.text | Describes the recommended steps to take to remediate an issue identified in a finding. | text |
| aws.securityhub_findings.remediation.recommendation.url | A URL to a page or site that contains information about how to remediate a finding. | keyword |
| aws.securityhub_findings.resources | A set of resource data types that describe the resources that the finding refers to. | flattened |
| aws.securityhub_findings.sample | Indicates whether the finding is a sample finding. | boolean |
| aws.securityhub_findings.schema.version | The schema version that a finding is formatted for. | keyword |
| aws.securityhub_findings.severity.label | The severity value of the finding. | keyword |
| aws.securityhub_findings.severity.normalized | The normalized severity of a finding. | keyword |
| aws.securityhub_findings.severity.original | The native severity from the finding product that generated the finding. | keyword |
| aws.securityhub_findings.severity.product | The native severity as defined by the Amazon Web Services service or integrated partner product that generated the finding. | keyword |
| aws.securityhub_findings.source_url | A URL that links to a page about the current finding in the security-findings provider's solution. | keyword |
| aws.securityhub_findings.threat_intel_indicators.category | The category of a threat intelligence indicator. | keyword |
| aws.securityhub_findings.threat_intel_indicators.last_observed_at | Indicates when the most recent instance of a threat intelligence indicator was observed. | date |
| aws.securityhub_findings.threat_intel_indicators.source | The source of the threat intelligence indicator. | keyword |
| aws.securityhub_findings.threat_intel_indicators.source_url | The URL to the page or site where you can get more information about the threat intelligence indicator. | keyword |
| aws.securityhub_findings.threat_intel_indicators.type | The type of threat intelligence indicator. | keyword |
| aws.securityhub_findings.threat_intel_indicators.value | The value of a threat intelligence indicator. | keyword |
| aws.securityhub_findings.title | A finding's title. | text |
| aws.securityhub_findings.types | One or more finding types in the format of namespace/category/classifier that classify a finding. | keyword |
| aws.securityhub_findings.updated_at | Indicates when the security-findings provider last updated the finding record. | date |
| aws.securityhub_findings.user_defined_fields | A list of name/value string pairs associated with the finding. These are custom, user-defined fields added to a finding. | flattened |
| aws.securityhub_findings.verification_state | Indicates the veracity of a finding. | keyword |
| aws.securityhub_findings.vulnerabilities.cvss.adjustments.metric | The metric to adjust. | keyword |
| aws.securityhub_findings.vulnerabilities.cvss.adjustments.reason | The reason for the adjustment. | keyword |
| aws.securityhub_findings.vulnerabilities.cvss.base_score | The base CVSS score. | double |
| aws.securityhub_findings.vulnerabilities.cvss.base_vector | The base scoring vector for the CVSS score. | keyword |
| aws.securityhub_findings.vulnerabilities.cvss.source | The origin of the original CVSS score and vector. | keyword |
| aws.securityhub_findings.vulnerabilities.cvss.version | The version of CVSS for the CVSS score. | keyword |
| aws.securityhub_findings.vulnerabilities.id | The identifier of the vulnerability. | keyword |
| aws.securityhub_findings.vulnerabilities.reference_urls | A list of URLs that provide additional information about the vulnerability. | keyword |
| aws.securityhub_findings.vulnerabilities.related_vulnerabilities | List of vulnerabilities that are related to this vulnerability. | keyword |
| aws.securityhub_findings.vulnerabilities.vendor.created_at | Indicates when the vulnerability advisory was created. | date |
| aws.securityhub_findings.vulnerabilities.vendor.name | The name of the vendor. | keyword |
| aws.securityhub_findings.vulnerabilities.vendor.severity | The severity that the vendor assigned to the vulnerability. | keyword |
| aws.securityhub_findings.vulnerabilities.vendor.updated_at | Indicates when the vulnerability advisory was last updated. | date |
| aws.securityhub_findings.vulnerabilities.vendor.url | The URL of the vulnerability advisory. | keyword |
| aws.securityhub_findings.vulnerabilities.vulnerable_packages.architecture | The architecture used for the software package. | keyword |
| aws.securityhub_findings.vulnerabilities.vulnerable_packages.epoch | The epoch of the software package. | keyword |
| aws.securityhub_findings.vulnerabilities.vulnerable_packages.file_path | The file system path to the package manager inventory file. | keyword |
| aws.securityhub_findings.vulnerabilities.vulnerable_packages.name | The name of the software package. | keyword |
| aws.securityhub_findings.vulnerabilities.vulnerable_packages.package_manager | The source of the package. | keyword |
| aws.securityhub_findings.vulnerabilities.vulnerable_packages.release | The release of the software package. | keyword |
| aws.securityhub_findings.vulnerabilities.vulnerable_packages.version | The version of the software package. | keyword |
| aws.securityhub_findings.workflow.state | The workflow state of a finding. | keyword |
| aws.securityhub_findings.workflow.status | The status of the investigation into the finding. | keyword |
| cloud.image.id | Image ID for the cloud instance. | keyword |
| cloud.provider | Name of the cloud provider. Example values are aws, azure, gcp, or digitalocean. | constant_keyword |
| data_stream.dataset | The field can contain anything that makes sense to signify the source of the data. Examples include nginx.access, prometheus, endpoint etc. For data streams that otherwise fit, but that do not have dataset set we use the value "generic" for the dataset value. event.dataset should have the same value as data_stream.dataset. Beyond the Elasticsearch data stream naming criteria noted above, the dataset value has additional restrictions: * Must not contain - * No longer than 100 characters |
constant_keyword |
| data_stream.namespace | A user defined namespace. Namespaces are useful to allow grouping of data. Many users already organize their indices this way, and the data stream naming scheme now provides this best practice as a default. Many users will populate this field with default. If no value is used, it falls back to default. Beyond the Elasticsearch index naming criteria noted above, namespace value has the additional restrictions: * Must not contain - * No longer than 100 characters |
constant_keyword |
| data_stream.type | An overarching type for the data stream. Currently allowed values are "logs" and "metrics". We expect to also add "traces" and "synthetics" in the near future. | constant_keyword |
| event.dataset | Name of the dataset. If an event source publishes more than one type of log or events (e.g. access log, error log), the dataset is used to specify which one the event comes from. It's recommended but not required to start the dataset name with the module name, followed by a dot, then the dataset name. | constant_keyword |
| event.kind | This is one of four ECS Categorization Fields, and indicates the highest level in the ECS category hierarchy. event.kind gives high-level information about what type of information the event contains, without being specific to the contents of the event. For example, values of this field distinguish alert events from metric events. The value of this field can be used to inform how these kinds of events should be handled. They may warrant different retention, different access control, it may also help understand whether the data is coming in at a regular interval or not. |
keyword |
| event.module | Name of the module this data is coming from. If your monitoring agent supports the concept of modules or plugins to process events of a given source (e.g. Apache logs), event.module should contain the name of this module. |
constant_keyword |
| host.containerized | If the host is a container. | boolean |
| host.os.build | OS build information. | keyword |
| host.os.codename | OS codename, if any. | keyword |
| input.type | Input type | keyword |
| log.offset | Log offset | long |
| observer.vendor | Vendor name of the observer. | constant_keyword |
| resource.id | keyword | |
| resource.name | keyword | |
| resource.type | keyword | |
| result.evaluation | keyword | |
| rule.remediation | keyword | |
| url.user_info | keyword |
This is the securityhub_findings_full_posture data stream. It requests the full set of current findings every 24 hours rather than collecting incrementally.
Use the Findings Filters setting to control which findings are collected via server-side AwsSecurityFindingFilters. The default excludes archived (RecordState) and suppressed (WorkflowStatus) findings to reflect the current security posture; editing or clearing this setting replaces those defaults.
Example
{
"@timestamp": "2026-10-08T09:45:18.016Z",
"agent": {
"ephemeral_id": "da907710-96ed-4796-a683-bbb67185cba0",
"id": "e24eab75-d622-4dc0-bb71-d16de5bfa21d",
"name": "elastic-agent-10539",
"type": "filebeat",
"version": "9.4.0"
},
"aws": {
"securityhub_findings_full_posture": {
"action": {
"port_probe": {
"blocked": false,
"details": {
"local": {
"ip": {
"address_v4": "1.128.0.0"
},
"port": {
"name": "HTTP",
"number": 80
}
},
"remote_ip": {
"city": {
"name": "Example City"
},
"country": {
"name": "Example Country"
},
"geolocation": {
"latitude": 0,
"longitude": 0
},
"organization": {
"asn": "64496",
"asn_organization": "ExampleASO",
"internet_provider": "ExampleOrg",
"internet_service_provider": "ExampleISP"
}
}
}
}
},
"aws_account_id": "111111111111",
"company": {
"name": "AWS"
},
"compliance": {
"related_requirements": [
"Req1",
"Req2"
],
"status": "PASSED",
"status_reasons": {
"description": "CloudWatch alarms do not exist in the account",
"reason_code": "CLOUDWATCH_ALARMS_NOT_PRESENT"
}
},
"confidence": 42,
"criticality": 99,
"description": "The version of openssl found on instance i-abcd1234 is known to contain a vulnerability.",
"first_observed_at": "2017-03-22T13:22:13.933Z",
"generator": {
"id": "acme-vuln-9ab348"
},
"last_observed_at": "2017-03-23T13:22:13.933Z",
"malware": {
"name": "Stringler",
"path": "/usr/sbin/stringler",
"state": "OBSERVED",
"type": "COIN_MINER"
},
"network": {
"open_port_range": {
"begin": 443,
"end": 443
}
},
"network_path": {
"component": {
"id": "abc-01a234bc56d8901ee",
"type": "AWS::EC2::InternetGateway"
},
"egress": {
"destination": {
"address": "1.128.0.0/24",
"port_ranges": {
"begin": 443,
"end": 443
}
},
"protocol": "TCP",
"source": {
"address": "175.16.199.1/24"
}
},
"ingress": {
"destination": {
"address": "175.16.199.1/24",
"port_ranges": {
"begin": 443,
"end": 443
}
},
"protocol": "TCP",
"source": {
"address": "175.16.199.1/24"
}
}
},
"note": {
"text": "Don't forget to check under the mat.",
"updated_at": "2018-08-31T00:15:09.000Z",
"updated_by": "jsmith"
},
"patch_summary": {
"failed": {
"count": 0
},
"id": "pb-123456789098",
"installed": {
"count": 100,
"other": {
"count": 1023
},
"pending_reboot": 0,
"rejected": {
"count": 0
}
},
"missing": {
"count": 100
},
"operation": {
"end_time": "2018-09-27T23:39:31.000Z",
"start_time": "2018-09-27T23:37:31.000Z",
"type": "Install"
},
"reboot_option": "RebootIfNeeded"
},
"product": {
"arn": "arn:aws:securityhub:us-east-1:111111111111:product/111111111111/default",
"fields": {
"Service_Name": "cloudtrail.amazonaws.com",
"aws/inspector/AssessmentTargetName": "My prod env",
"aws/inspector/AssessmentTemplateName": "My daily CVE assessment",
"aws/inspector/RulesPackageName": "Common Vulnerabilities and Exposures",
"generico/secure-pro/Count": "6"
},
"name": "Security Hub"
},
"provider_fields": {
"confidence": 42,
"criticality": 99,
"related_findings": {
"id": "123e4567-e89b-12d3-a456-426655440000",
"product": {
"arn": "arn:aws:securityhub:us-west-2::product/aws/guardduty"
}
},
"severity": {
"label": "MEDIUM",
"original": "MEDIUM"
},
"types": "Software and Configuration Checks/Vulnerabilities/CVE"
},
"record_state": "ACTIVE",
"region": "us-east-1",
"related_findings": {
"id": [
"123e4567-e89b-12d3-a456-426655440000",
"AcmeNerfHerder-111111111111-x189dx7824"
],
"product": {
"arn": [
"arn:aws:securityhub:us-west-2::product/aws/guardduty",
"arn:aws:securityhub:us-west-2::product/aws/guardduty"
]
}
},
"remediation": {
"recommendation": {
"text": "Run sudo yum update and cross your fingers and toes.",
"url": "http://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html"
}
},
"resources": {
"Details": {
"IamInstanceProfileArn": "arn:aws:iam::123456789012:role/IamInstanceProfileArn",
"ImageId": "ami-79fd7eee",
"IpV4Addresses": [
"175.16.199.1"
],
"IpV6Addresses": [
"2a02:cf40::"
],
"KeyName": "testkey",
"LaunchedAt": "2018-09-29T01:25:54Z",
"MetadataOptions": {
"HttpEndpoint": "enabled",
"HttpProtocolIpv6": "enabled",
"HttpPutResponseHopLimit": 1,
"HttpTokens": "optional",
"InstanceMetadataTags": "disabled"
},
"NetworkInterfaces": [
{
"NetworkInterfaceId": "eni-e5aa89a3"
}
],
"SubnetId": "PublicSubnet",
"Type": "i3.xlarge",
"VirtualizationType": "hvm",
"VpcId": "TestVPCIpv6"
},
"Id": "i-cafebabe",
"Partition": "aws",
"Region": "us-west-2",
"Tags": {
"billingCode": "Lotus-1-2-3",
"needsPatching": "true"
},
"Type": "AwsEc2Instance"
},
"sample": true,
"schema": {
"version": "2018-10-08"
},
"severity": {
"label": "CRITICAL",
"original": "8.3"
},
"source_url": "http://threatintelweekly.org/backdoors/8888",
"threat_intel_indicators": {
"category": "BACKDOOR",
"source": "Threat Intel Weekly",
"source_url": "http://threatintelweekly.org/backdoors/8888",
"value": "175.16.199.1"
},
"title": "EC2.20 Both VPN tunnels for an AWS Site-to-Site VPN connection should be up",
"types": "Software and Configuration Checks/Vulnerabilities/CVE",
"updated_at": "2018-08-31T00:15:09.000Z",
"user_defined_fields": {
"comeBackToLater": "Check this again on Monday",
"reviewedByCio": "true"
},
"verification_state": "UNKNOWN",
"vulnerabilities": {
"cvss": {
"base_score": [
4.7,
4.7
],
"base_vector": [
"AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N",
"AV:L/AC:M/Au:N/C:C/I:N/A:N"
],
"version": [
"V3",
"V2"
]
},
"related_vulnerabilities": "CVE-2020-12345",
"vendor": {
"created_at": "2020-01-16T00:01:43.000Z",
"severity": "Medium",
"updated_at": "2020-01-16T00:01:43.000Z",
"url": "https://alas.aws.amazon.com/ALAS-2020-1337.html"
},
"vulnerable_packages": {
"architecture": "x86_64",
"epoch": "1",
"name": "openssl",
"release": "16.amzn2.0.3",
"version": "1.0.2k"
}
},
"workflow": {
"state": "NEW",
"status": "NEW"
}
}
},
"cloud": {
"account": {
"id": "111111111111"
},
"instance": {
"id": "i-cafebabe",
"name": "i-cafebabe"
},
"provider": "aws",
"region": "us-east-1"
},
"data_stream": {
"dataset": "aws.securityhub_findings_full_posture",
"namespace": "20994",
"type": "logs"
},
"destination": {
"domain": "example2.com",
"ip": [
"1.128.0.0",
"2a02:cf40::"
],
"port": 80
},
"ecs": {
"version": "8.11.0"
},
"elastic_agent": {
"id": "e24eab75-d622-4dc0-bb71-d16de5bfa21d",
"snapshot": false,
"version": "9.4.0"
},
"event": {
"action": "port_probe",
"agent_id_status": "verified",
"category": [
"configuration"
],
"dataset": "aws.securityhub_findings_full_posture",
"id": "us-west-2/111111111111/98aebb2207407c87f51e89943f12b1ef",
"ingested": "2026-10-08T09:45:18Z",
"kind": "state",
"module": "aws",
"original": "{\"Action\":{\"ActionType\":\"PORT_PROBE\",\"PortProbeAction\":{\"Blocked\":false,\"PortProbeDetails\":[{\"LocalIpDetails\":{\"IpAddressV4\":\"1.128.0.0\"},\"LocalPortDetails\":{\"Port\":80,\"PortName\":\"HTTP\"},\"RemoteIpDetails\":{\"City\":{\"CityName\":\"Example City\"},\"Country\":{\"CountryName\":\"Example Country\"},\"GeoLocation\":{\"Lat\":0,\"Lon\":0},\"Organization\":{\"Asn\":64496,\"AsnOrg\":\"ExampleASO\",\"Isp\":\"ExampleISP\",\"Org\":\"ExampleOrg\"}}}]}},\"AwsAccountId\":\"111111111111\",\"CompanyName\":\"AWS\",\"Compliance\":{\"RelatedRequirements\":[\"Req1\",\"Req2\"],\"Status\":\"PASSED\",\"StatusReasons\":[{\"Description\":\"CloudWatch alarms do not exist in the account\",\"ReasonCode\":\"CLOUDWATCH_ALARMS_NOT_PRESENT\"}]},\"Confidence\":42,\"CreatedAt\":\"2017-03-22T13:22:13.933Z\",\"Criticality\":99,\"Description\":\"The version of openssl found on instance i-abcd1234 is known to contain a vulnerability.\",\"FindingProviderFields\":{\"Confidence\":42,\"Criticality\":99,\"RelatedFindings\":[{\"Id\":\"123e4567-e89b-12d3-a456-426655440000\",\"ProductArn\":\"arn:aws:securityhub:us-west-2::product/aws/guardduty\"}],\"Severity\":{\"Label\":\"MEDIUM\",\"Original\":\"MEDIUM\"},\"Types\":[\"Software and Configuration Checks/Vulnerabilities/CVE\"]},\"FirstObservedAt\":\"2017-03-22T13:22:13.933Z\",\"GeneratorId\":\"acme-vuln-9ab348\",\"Id\":\"us-west-2/111111111111/98aebb2207407c87f51e89943f12b1ef\",\"LastObservedAt\":\"2017-03-23T13:22:13.933Z\",\"Malware\":[{\"Name\":\"Stringler\",\"Path\":\"/usr/sbin/stringler\",\"State\":\"OBSERVED\",\"Type\":\"COIN_MINER\"}],\"Network\":{\"DestinationDomain\":\"example2.com\",\"DestinationIpV4\":\"1.128.0.0\",\"DestinationIpV6\":\"2a02:cf40::\",\"DestinationPort\":\"80\",\"Direction\":\"IN\",\"OpenPortRange\":{\"Begin\":443,\"End\":443},\"Protocol\":\"TCP\",\"SourceDomain\":\"example1.com\",\"SourceIpV4\":\"1.128.0.0\",\"SourceIpV6\":\"2a02:cf40::\",\"SourceMac\":\"00:0d:83:b1:c0:8e\",\"SourcePort\":\"42\"},\"NetworkPath\":[{\"ComponentId\":\"abc-01a234bc56d8901ee\",\"ComponentType\":\"AWS::EC2::InternetGateway\",\"Egress\":{\"Destination\":{\"Address\":[\"1.128.0.0/24\"],\"PortRanges\":[{\"Begin\":443,\"End\":443}]},\"Protocol\":\"TCP\",\"Source\":{\"Address\":[\"175.16.199.1/24\"]}},\"Ingress\":{\"Destination\":{\"Address\":[\"175.16.199.1/24\"],\"PortRanges\":[{\"Begin\":443,\"End\":443}]},\"Protocol\":\"TCP\",\"Source\":{\"Address\":[\"175.16.199.1/24\"]}}}],\"Note\":{\"Text\":\"Don't forget to check under the mat.\",\"UpdatedAt\":\"2018-08-31T00:15:09Z\",\"UpdatedBy\":\"jsmith\"},\"PatchSummary\":{\"FailedCount\":\"0\",\"Id\":\"pb-123456789098\",\"InstalledCount\":\"100\",\"InstalledOtherCount\":\"1023\",\"InstalledPendingReboot\":\"0\",\"InstalledRejectedCount\":\"0\",\"MissingCount\":\"100\",\"Operation\":\"Install\",\"OperationEndTime\":\"2018-09-27T23:39:31Z\",\"OperationStartTime\":\"2018-09-27T23:37:31Z\",\"RebootOption\":\"RebootIfNeeded\"},\"Process\":{\"LaunchedAt\":\"2018-09-27T22:37:31Z\",\"Name\":\"syslogd\",\"ParentPid\":56789,\"Path\":\"/usr/sbin/syslogd\",\"Pid\":12345,\"TerminatedAt\":\"2018-09-27T23:37:31Z\"},\"ProductArn\":\"arn:aws:securityhub:us-east-1:111111111111:product/111111111111/default\",\"ProductFields\":{\"Service_Name\":\"cloudtrail.amazonaws.com\",\"aws/inspector/AssessmentTargetName\":\"My prod env\",\"aws/inspector/AssessmentTemplateName\":\"My daily CVE assessment\",\"aws/inspector/RulesPackageName\":\"Common Vulnerabilities and Exposures\",\"generico/secure-pro/Count\":\"6\"},\"ProductName\":\"Security Hub\",\"RecordState\":\"ACTIVE\",\"Region\":\"us-east-1\",\"RelatedFindings\":[{\"Id\":\"123e4567-e89b-12d3-a456-426655440000\",\"ProductArn\":\"arn:aws:securityhub:us-west-2::product/aws/guardduty\"},{\"Id\":\"AcmeNerfHerder-111111111111-x189dx7824\",\"ProductArn\":\"arn:aws:securityhub:us-west-2::product/aws/guardduty\"}],\"Remediation\":{\"Recommendation\":{\"Text\":\"Run sudo yum update and cross your fingers and toes.\",\"Url\":\"http://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html\"}},\"Resources\":[{\"Details\":{\"IamInstanceProfileArn\":\"arn:aws:iam::123456789012:role/IamInstanceProfileArn\",\"ImageId\":\"ami-79fd7eee\",\"IpV4Addresses\":[\"175.16.199.1\"],\"IpV6Addresses\":[\"2a02:cf40::\"],\"KeyName\":\"testkey\",\"LaunchedAt\":\"2018-09-29T01:25:54Z\",\"MetadataOptions\":{\"HttpEndpoint\":\"enabled\",\"HttpProtocolIpv6\":\"enabled\",\"HttpPutResponseHopLimit\":1,\"HttpTokens\":\"optional\",\"InstanceMetadataTags\":\"disabled\"},\"NetworkInterfaces\":[{\"NetworkInterfaceId\":\"eni-e5aa89a3\"}],\"SubnetId\":\"PublicSubnet\",\"Type\":\"i3.xlarge\",\"VirtualizationType\":\"hvm\",\"VpcId\":\"TestVPCIpv6\"},\"Id\":\"i-cafebabe\",\"Partition\":\"aws\",\"Region\":\"us-west-2\",\"Tags\":{\"billingCode\":\"Lotus-1-2-3\",\"needsPatching\":\"true\"},\"Type\":\"AwsEc2Instance\"}],\"Sample\":true,\"SchemaVersion\":\"2018-10-08\",\"Severity\":{\"Label\":\"CRITICAL\",\"Original\":\"8.3\"},\"SourceUrl\":\"http://threatintelweekly.org/backdoors/8888\",\"ThreatIntelIndicators\":[{\"Category\":\"BACKDOOR\",\"LastObservedAt\":\"2018-09-27T23:37:31Z\",\"Source\":\"Threat Intel Weekly\",\"SourceUrl\":\"http://threatintelweekly.org/backdoors/8888\",\"Type\":\"IPV4_ADDRESS\",\"Value\":\"175.16.199.1\"}],\"Threats\":[{\"FilePaths\":[{\"FileName\":\"b.txt\",\"FilePath\":\"/tmp/b.txt\",\"Hash\":\"sha256\",\"ResourceId\":\"arn:aws:ec2:us-west-2:123456789012:volume/vol-032f3bdd89aee112f\"}],\"ItemCount\":3,\"Name\":\"Iot.linux.mirai.vwisi\",\"Severity\":\"HIGH\"}],\"Title\":\"EC2.20 Both VPN tunnels for an AWS Site-to-Site VPN connection should be up\",\"Types\":[\"Software and Configuration Checks/Vulnerabilities/CVE\"],\"UpdatedAt\":\"2018-08-31T00:15:09Z\",\"UserDefinedFields\":{\"comeBackToLater\":\"Check this again on Monday\",\"reviewedByCio\":\"true\"},\"VerificationState\":\"UNKNOWN\",\"Vulnerabilities\":[{\"Cvss\":[{\"BaseScore\":4.7,\"BaseVector\":\"AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N\",\"Version\":\"V3\"},{\"BaseScore\":4.7,\"BaseVector\":\"AV:L/AC:M/Au:N/C:C/I:N/A:N\",\"Version\":\"V2\"}],\"Id\":\"CVE-2020-12345\",\"ReferenceUrls\":[\"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-12418\",\"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17563\"],\"RelatedVulnerabilities\":[\"CVE-2020-12345\"],\"Vendor\":{\"Name\":\"Alas\",\"Url\":\"https://alas.aws.amazon.com/ALAS-2020-1337.html\",\"VendorCreatedAt\":\"2020-01-16T00:01:43Z\",\"VendorSeverity\":\"Medium\",\"VendorUpdatedAt\":\"2020-01-16T00:01:43Z\"},\"VulnerablePackages\":[{\"Architecture\":\"x86_64\",\"Epoch\":\"1\",\"Name\":\"openssl\",\"Release\":\"16.amzn2.0.3\",\"Version\":\"1.0.2k\"}]}],\"Workflow\":{\"Status\":\"NEW\"},\"WorkflowState\":\"NEW\"}",
"outcome": "success",
"type": [
"info"
]
},
"host": {
"id": "i-cafebabe"
},
"input": {
"type": "httpjson"
},
"network": {
"direction": "inbound",
"protocol": "tcp"
},
"observer": {
"vendor": "AWS Security Hub CSPM"
},
"organization": {
"name": "AWS"
},
"process": {
"end": "2018-09-27T23:37:31.000Z",
"executable": "/usr/sbin/syslogd",
"name": "syslogd",
"parent": {
"pid": 56789
},
"pid": 12345,
"start": "2018-09-27T22:37:31.000Z"
},
"related": {
"ip": [
"1.128.0.0",
"2a02:cf40::"
]
},
"resource": {
"id": "i-cafebabe",
"name": "i-cafebabe",
"type": "AwsEc2Instance"
},
"result": {
"evaluation": "passed"
},
"rule": {
"description": "The version of openssl found on instance i-abcd1234 is known to contain a vulnerability.",
"id": "acme-vuln-9ab348",
"name": "EC2.20 Both VPN tunnels for an AWS Site-to-Site VPN connection should be up",
"reference": "http://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html",
"remediation": "Run sudo yum update and cross your fingers and toes.\r\nhttp://myfp.com/recommendations/dangerous_things_and_how_to_fix_them.html",
"ruleset": [
"Req1",
"Req2"
]
},
"source": {
"domain": "example1.com",
"ip": [
"1.128.0.0",
"2a02:cf40::"
],
"mac": "00-0D-83-B1-C0-8E",
"port": 42
},
"tags": [
"run_as_cel",
"preserve_original_event",
"forwarded",
"aws_securityhub_findings_full_posture"
],
"threat": {
"indicator": {
"last_seen": "2018-09-27T23:37:31.000Z",
"type": "ipv4-addr"
}
},
"url": {
"domain": "threatintelweekly.org",
"full": "http://threatintelweekly.org/backdoors/8888",
"original": "http://threatintelweekly.org/backdoors/8888",
"path": "/backdoors/8888",
"scheme": "http"
},
"vulnerability": {
"id": "CVE-2020-12345",
"reference": [
"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-12418",
"http://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-17563"
],
"scanner": {
"vendor": "Alas"
},
"score": {
"base": 4.7,
"version": "V2"
}
}
}
ECS Field Reference
Please refer to the following document for detailed information on ECS fields.
Exported fields
| Field | Description | Type |
|---|---|---|
| @timestamp | Date/time when the event originated. This is the date/time extracted from the event, typically representing when the event was generated by the source. If the event source has no original timestamp, this value is typically populated by the first time the event was received by the pipeline. Required field for all events. | date |
| aws.securityhub_findings_full_posture.action.aws_api_call.affected_resources | Identifies the resources that were affected by the API call. | flattened |
| aws.securityhub_findings_full_posture.action.aws_api_call.api | The name of the API method that was issued. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.caller.type | Indicates whether the API call originated from a remote IP address(remoteip) or from a DNS domain(domain). | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.domain_details.domain | The name of the DNS domain that issued the API call. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.first_seen | An ISO8601-formatted timestamp that indicates when the API call was first observed. | date |
| aws.securityhub_findings_full_posture.action.aws_api_call.last_seen | An ISO8601-formatted timestamp that indicates when the API call was most recently observed. | date |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.city.name | The name of the city. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.country.code | The 2-letter ISO 3166 country code for the country. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.country.name | The name of the country. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.geolocation.latitude | The longitude of the location. | double |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.geolocation.longitude | The latitude of the location. | double |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.organization.asn | The Autonomous System Number(ASN) of the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.organization.asn_organization | The name of the organization that registered the ASN. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.organization.internet_provider | The ISP information for the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.remote_ip.organization.internet_service_provider | The name of the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.aws_api_call.service.name | The name of the Amazon Web Services service that the API method belongs to. | keyword |
| aws.securityhub_findings_full_posture.action.dns_request.blocked | Indicates whether the DNS request was blocked. | boolean |
| aws.securityhub_findings_full_posture.action.dns_request.domain | The DNS domain that is associated with the DNS request. | keyword |
| aws.securityhub_findings_full_posture.action.dns_request.protocol | The protocol that was used for the DNS request. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.blocked | Indicates whether the network connection attempt was blocked. | boolean |
| aws.securityhub_findings_full_posture.action.network_connection.direction | The direction of the network connection request(IN or OUT). | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.local.port.name | The port name of the local connection. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.local.port.number | The number of the port. | long |
| aws.securityhub_findings_full_posture.action.network_connection.protocol | The protocol used to make the network connection request. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote.port.name | The port name of the remote connection. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote.port.number | The number of the port. | long |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.city.name | The name of the city. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.country.code | The 2-letter ISO 3166 country code for the country. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.country.name | The name of the country. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.geolocation.latitude | The longitude of the location. | double |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.geolocation.longitude | The latitude of the location. | double |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.organization.asn | The Autonomous System Number(ASN) of the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.organization.asn_organization | The name of the organization that registered the ASN. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.organization.internet_provider | The ISP information for the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.network_connection.remote_ip.organization.internet_service_provider | The name of the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.blocked | Indicates whether the port probe was blocked. | boolean |
| aws.securityhub_findings_full_posture.action.port_probe.details.local.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings_full_posture.action.port_probe.details.local.port.name | The port name of the local connection. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.details.local.port.number | The number of the port. | long |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.city.name | The name of the city. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.country.code | The 2-letter ISO 3166 country code for the country. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.country.name | The name of the country. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.geolocation.latitude | The longitude of the location. | double |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.geolocation.longitude | The latitude of the location. | double |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.ip.address_v4 | The IP address. | ip |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.organization.asn | The Autonomous System Number(ASN) of the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.organization.asn_organization | The name of the organization that registered the ASN. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.organization.internet_provider | The ISP information for the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.port_probe.details.remote_ip.organization.internet_service_provider | The name of the internet provider. | keyword |
| aws.securityhub_findings_full_posture.action.type | The type of action that was detected. | keyword |
| aws.securityhub_findings_full_posture.aws_account_id | The Amazon Web Services account ID that a finding is generated in. | keyword |
| aws.securityhub_findings_full_posture.company.name | The name of the company for the product that generated the finding. | keyword |
| aws.securityhub_findings_full_posture.compliance.related_requirements | For a control, the industry or regulatory framework requirements that are related to the control. | keyword |
| aws.securityhub_findings_full_posture.compliance.security_control_id | Unique identifier of a control across standards. | keyword |
| aws.securityhub_findings_full_posture.compliance.status | The result of a standards check. | keyword |
| aws.securityhub_findings_full_posture.compliance.status_reasons.description | The corresponding description for the status reason code. | keyword |
| aws.securityhub_findings_full_posture.compliance.status_reasons.reason_code | A code that represents a reason for the control status. | keyword |
| aws.securityhub_findings_full_posture.confidence | A finding's confidence. Confidence is defined as the likelihood that a finding accurately identifies the behavior or issue that it was intended to identify. | long |
| aws.securityhub_findings_full_posture.created_at | Indicates when the security-findings provider created the potential security issue that a finding captured. | date |
| aws.securityhub_findings_full_posture.criticality | The level of importance assigned to the resources associated with the finding. | long |
| aws.securityhub_findings_full_posture.description | A finding's description. | keyword |
| aws.securityhub_findings_full_posture.first_observed_at | Indicates when the security-findings provider first observed the potential security issue that a finding captured. | date |
| aws.securityhub_findings_full_posture.generator.id | The identifier for the solution-specific component(a discrete unit of logic) that generated a finding. In various security-findings providers' solutions, this generator can be called a rule, a check, a detector, a plugin, etc. | keyword |
| aws.securityhub_findings_full_posture.id | The security findings provider-specific identifier for a finding. | keyword |
| aws.securityhub_findings_full_posture.last_observed_at | Indicates when the security-findings provider most recently observed the potential security issue that a finding captured. | date |
| aws.securityhub_findings_full_posture.malware.name | The name of the malware that was observed. | keyword |
| aws.securityhub_findings_full_posture.malware.path | The file system path of the malware that was observed. | keyword |
| aws.securityhub_findings_full_posture.malware.state | The state of the malware that was observed. | keyword |
| aws.securityhub_findings_full_posture.malware.type | The type of the malware that was observed. | keyword |
| aws.securityhub_findings_full_posture.network.destination.domain | The destination domain of network-related information about a finding. | keyword |
| aws.securityhub_findings_full_posture.network.destination.ip.v4 | The destination IPv4 address of network-related information about a finding. | ip |
| aws.securityhub_findings_full_posture.network.destination.ip.v6 | The destination IPv6 address of network-related information about a finding. | ip |
| aws.securityhub_findings_full_posture.network.destination.port | The destination port of network-related information about a finding. | long |
| aws.securityhub_findings_full_posture.network.direction | The direction of network traffic associated with a finding. | keyword |
| aws.securityhub_findings_full_posture.network.open_port_range.begin | The first port in the port range. | long |
| aws.securityhub_findings_full_posture.network.open_port_range.end | The last port in the port range. | long |
| aws.securityhub_findings_full_posture.network.protocol | The protocol of network-related information about a finding. | keyword |
| aws.securityhub_findings_full_posture.network.source.domain | The source domain of network-related information about a finding. | keyword |
| aws.securityhub_findings_full_posture.network.source.ip.v4 | The source IPv4 address of network-related information about a finding. | ip |
| aws.securityhub_findings_full_posture.network.source.ip.v6 | The source IPv6 address of network-related information about a finding. | ip |
| aws.securityhub_findings_full_posture.network.source.mac | The source media access control(MAC) address of network-related information about a finding. | keyword |
| aws.securityhub_findings_full_posture.network.source.port | The source port of network-related information about a finding. | long |
| aws.securityhub_findings_full_posture.network_path.component.id | The identifier of a component in the network path. | keyword |
| aws.securityhub_findings_full_posture.network_path.component.type | The type of component. | keyword |
| aws.securityhub_findings_full_posture.network_path.egress.destination.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings_full_posture.network_path.egress.destination.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings_full_posture.network_path.egress.destination.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings_full_posture.network_path.egress.protocol | The protocol used for the component. | keyword |
| aws.securityhub_findings_full_posture.network_path.egress.source.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings_full_posture.network_path.egress.source.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings_full_posture.network_path.egress.source.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings_full_posture.network_path.ingress.destination.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings_full_posture.network_path.ingress.destination.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings_full_posture.network_path.ingress.destination.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings_full_posture.network_path.ingress.protocol | The protocol used for the component. | keyword |
| aws.securityhub_findings_full_posture.network_path.ingress.source.address | The IP addresses of the destination. | keyword |
| aws.securityhub_findings_full_posture.network_path.ingress.source.port_ranges.begin | The first port in the port range. | long |
| aws.securityhub_findings_full_posture.network_path.ingress.source.port_ranges.end | The last port in the port range. | long |
| aws.securityhub_findings_full_posture.note.text | The text of a note. | keyword |
| aws.securityhub_findings_full_posture.note.updated_at | The timestamp of when the note was updated. | date |
| aws.securityhub_findings_full_posture.note.updated_by | The principal that created a note. | keyword |
| aws.securityhub_findings_full_posture.patch_summary.failed.count | The number of patches from the compliance standard that failed to install. | long |
| aws.securityhub_findings_full_posture.patch_summary.id | The identifier of the compliance standard that was used to determine the patch compliance status. | keyword |
| aws.securityhub_findings_full_posture.patch_summary.installed.count | The number of patches from the compliance standard that were installed successfully. | long |
| aws.securityhub_findings_full_posture.patch_summary.installed.other.count | The number of installed patches that are not part of the compliance standard. | long |
| aws.securityhub_findings_full_posture.patch_summary.installed.pending_reboot | The number of patches that were applied, but that require the instance to be rebooted in order to be marked as installed. | long |
| aws.securityhub_findings_full_posture.patch_summary.installed.rejected.count | The number of patches that are installed but are also on a list of patches that the customer rejected. | long |
| aws.securityhub_findings_full_posture.patch_summary.missing.count | The number of patches that are part of the compliance standard but are not installed. The count includes patches that failed to install. | long |
| aws.securityhub_findings_full_posture.patch_summary.operation.end_time | Indicates when the operation completed. | date |
| aws.securityhub_findings_full_posture.patch_summary.operation.start_time | Indicates when the operation started. | date |
| aws.securityhub_findings_full_posture.patch_summary.operation.type | The type of patch operation performed. For Patch Manager, the values are SCAN and INSTALL. | keyword |
| aws.securityhub_findings_full_posture.patch_summary.reboot_option | The reboot option specified for the instance. | keyword |
| aws.securityhub_findings_full_posture.process.launched_at | Indicates when the process was launched. | date |
| aws.securityhub_findings_full_posture.process.name | The name of the process. | keyword |
| aws.securityhub_findings_full_posture.process.parent.pid | The parent process ID. | long |
| aws.securityhub_findings_full_posture.process.path | The path to the process executable. | keyword |
| aws.securityhub_findings_full_posture.process.pid | The process ID. | long |
| aws.securityhub_findings_full_posture.process.terminated_at | Indicates when the process was terminated. | date |
| aws.securityhub_findings_full_posture.processed_at | Indicates when AWS Security Hub received a finding and begins to process it. | date |
| aws.securityhub_findings_full_posture.product.arn | The ARN generated by Security Hub that uniquely identifies a product that generates findings. This can be the ARN for a third-party product that is integrated with Security Hub, or the ARN for a custom integration. | keyword |
| aws.securityhub_findings_full_posture.product.fields | A data type where security-findings providers can include additional solution-specific details that aren't part of the defined AwsSecurityFinding format. | flattened |
| aws.securityhub_findings_full_posture.product.name | The name of the product that generated the finding. | keyword |
| aws.securityhub_findings_full_posture.provider_fields.confidence | A finding's confidence. Confidence is defined as the likelihood that a finding accurately identifies the behavior or issue that it was intended to identify. | long |
| aws.securityhub_findings_full_posture.provider_fields.criticality | The level of importance assigned to the resources associated with the finding. | long |
| aws.securityhub_findings_full_posture.provider_fields.related_findings.id | The product-generated identifier for a related finding. | keyword |
| aws.securityhub_findings_full_posture.provider_fields.related_findings.product.arn | The ARN of the product that generated a related finding. | keyword |
| aws.securityhub_findings_full_posture.provider_fields.severity.label | The severity label assigned to the finding by the finding provider. | keyword |
| aws.securityhub_findings_full_posture.provider_fields.severity.normalized | The normalized severity of a finding provider. | keyword |
| aws.securityhub_findings_full_posture.provider_fields.severity.original | The finding provider's original value for the severity. | keyword |
| aws.securityhub_findings_full_posture.provider_fields.severity.product | The finding provider's product for the severity. | keyword |
| aws.securityhub_findings_full_posture.provider_fields.types | One or more finding types in the format of namespace/category/classifier that classify a finding. | keyword |
| aws.securityhub_findings_full_posture.record_state | The record state of a finding. | keyword |
| aws.securityhub_findings_full_posture.region | The Region from which the finding was generated. | keyword |
| aws.securityhub_findings_full_posture.related_findings.id | The product-generated identifier for a related finding. | keyword |
| aws.securityhub_findings_full_posture.related_findings.product.arn | The ARN of the product that generated a related finding. | keyword |
| aws.securityhub_findings_full_posture.remediation.recommendation.text | Describes the recommended steps to take to remediate an issue identified in a finding. | text |
| aws.securityhub_findings_full_posture.remediation.recommendation.url | A URL to a page or site that contains information about how to remediate a finding. | keyword |
| aws.securityhub_findings_full_posture.resources | A set of resource data types that describe the resources that the finding refers to. | flattened |
| aws.securityhub_findings_full_posture.sample | Indicates whether the finding is a sample finding. | boolean |
| aws.securityhub_findings_full_posture.schema.version | The schema version that a finding is formatted for. | keyword |
| aws.securityhub_findings_full_posture.severity.label | The severity value of the finding. | keyword |
| aws.securityhub_findings_full_posture.severity.normalized | The normalized severity of a finding. | keyword |
| aws.securityhub_findings_full_posture.severity.original | The native severity from the finding product that generated the finding. | keyword |
| aws.securityhub_findings_full_posture.severity.product | The native severity as defined by the Amazon Web Services service or integrated partner product that generated the finding. | keyword |
| aws.securityhub_findings_full_posture.source_url | A URL that links to a page about the current finding in the security-findings provider's solution. | keyword |
| aws.securityhub_findings_full_posture.threat_intel_indicators.category | The category of a threat intelligence indicator. | keyword |
| aws.securityhub_findings_full_posture.threat_intel_indicators.last_observed_at | Indicates when the most recent instance of a threat intelligence indicator was observed. | date |
| aws.securityhub_findings_full_posture.threat_intel_indicators.source | The source of the threat intelligence indicator. | keyword |
| aws.securityhub_findings_full_posture.threat_intel_indicators.source_url | The URL to the page or site where you can get more information about the threat intelligence indicator. | keyword |
| aws.securityhub_findings_full_posture.threat_intel_indicators.type | The type of threat intelligence indicator. | keyword |
| aws.securityhub_findings_full_posture.threat_intel_indicators.value | The value of a threat intelligence indicator. | keyword |
| aws.securityhub_findings_full_posture.title | A finding's title. | text |
| aws.securityhub_findings_full_posture.types | One or more finding types in the format of namespace/category/classifier that classify a finding. | keyword |
| aws.securityhub_findings_full_posture.updated_at | Indicates when the security-findings provider last updated the finding record. | date |
| aws.securityhub_findings_full_posture.user_defined_fields | A list of name/value string pairs associated with the finding. These are custom, user-defined fields added to a finding. | flattened |
| aws.securityhub_findings_full_posture.verification_state | Indicates the veracity of a finding. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.cvss.adjustments.metric | The metric to adjust. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.cvss.adjustments.reason | The reason for the adjustment. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.cvss.base_score | The base CVSS score. | double |
| aws.securityhub_findings_full_posture.vulnerabilities.cvss.base_vector | The base scoring vector for the CVSS score. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.cvss.source | The origin of the original CVSS score and vector. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.cvss.version | The version of CVSS for the CVSS score. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.id | The identifier of the vulnerability. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.reference_urls | A list of URLs that provide additional information about the vulnerability. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.related_vulnerabilities | List of vulnerabilities that are related to this vulnerability. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vendor.created_at | Indicates when the vulnerability advisory was created. | date |
| aws.securityhub_findings_full_posture.vulnerabilities.vendor.name | The name of the vendor. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vendor.severity | The severity that the vendor assigned to the vulnerability. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vendor.updated_at | Indicates when the vulnerability advisory was last updated. | date |
| aws.securityhub_findings_full_posture.vulnerabilities.vendor.url | The URL of the vulnerability advisory. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vulnerable_packages.architecture | The architecture used for the software package. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vulnerable_packages.epoch | The epoch of the software package. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vulnerable_packages.file_path | The file system path to the package manager inventory file. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vulnerable_packages.name | The name of the software package. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vulnerable_packages.package_manager | The source of the package. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vulnerable_packages.release | The release of the software package. | keyword |
| aws.securityhub_findings_full_posture.vulnerabilities.vulnerable_packages.version | The version of the software package. | keyword |
| aws.securityhub_findings_full_posture.workflow.state | The workflow state of a finding. | keyword |
| aws.securityhub_findings_full_posture.workflow.status | The status of the investigation into the finding. | keyword |
| cloud.image.id | Image ID for the cloud instance. | keyword |
| cloud.provider | constant_keyword | |
| data_stream.dataset | The field can contain anything that makes sense to signify the source of the data. Examples include nginx.access, prometheus, endpoint etc. For data streams that otherwise fit, but that do not have dataset set we use the value "generic" for the dataset value. event.dataset should have the same value as data_stream.dataset. Beyond the Elasticsearch data stream naming criteria noted above, the dataset value has additional restrictions: * Must not contain - * No longer than 100 characters |
constant_keyword |
| data_stream.namespace | A user defined namespace. Namespaces are useful to allow grouping of data. Many users already organize their indices this way, and the data stream naming scheme now provides this best practice as a default. Many users will populate this field with default. If no value is used, it falls back to default. Beyond the Elasticsearch index naming criteria noted above, namespace value has the additional restrictions: * Must not contain - * No longer than 100 characters |
constant_keyword |
| data_stream.type | An overarching type for the data stream. Currently allowed values are "logs" and "metrics". We expect to also add "traces" and "synthetics" in the near future. | constant_keyword |
| event.dataset | Name of the dataset. If an event source publishes more than one type of log or events (e.g. access log, error log), the dataset is used to specify which one the event comes from. It's recommended but not required to start the dataset name with the module name, followed by a dot, then the dataset name. | constant_keyword |
| event.kind | This is one of four ECS Categorization Fields, and indicates the highest level in the ECS category hierarchy. event.kind gives high-level information about what type of information the event contains, without being specific to the contents of the event. For example, values of this field distinguish alert events from metric events. The value of this field can be used to inform how these kinds of events should be handled. They may warrant different retention, different access control, it may also help understand whether the data is coming in at a regular interval or not. |
keyword |
| event.module | Name of the module this data is coming from. If your monitoring agent supports the concept of modules or plugins to process events of a given source (e.g. Apache logs), event.module should contain the name of this module. |
constant_keyword |
| host.containerized | If the host is a container. | boolean |
| host.os.build | OS build information. | keyword |
| host.os.codename | OS codename, if any. | keyword |
| input.type | Input type | keyword |
| log.offset | Log offset | long |
| observer.vendor | constant_keyword | |
| resource.id | keyword | |
| resource.name | keyword | |
| resource.type | keyword | |
| result.evaluation | keyword | |
| rule.remediation | keyword | |
| url.user_info | keyword |
This is the securityhub_insights data stream.
Example
{
"@timestamp": "2025-12-09T09:35:13.696Z",
"agent": {
"ephemeral_id": "301055f2-e64f-49af-9475-186afec36268",
"id": "fa813af5-4a32-4079-8743-a3f152e25625",
"name": "elastic-agent-12387",
"type": "filebeat",
"version": "8.19.4"
},
"aws": {
"securityhub_insights": {
"filters": {
"aws_account_id": [
{
"Comparison": "string",
"Value": "string"
}
],
"company": {
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"compliance": {
"status": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"confidence": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
],
"created_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"criticality": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
],
"description": [
{
"Comparison": "string",
"Value": "string"
}
],
"finding_provider_fields": {
"confidence": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
],
"criticality": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
],
"related_findings": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
],
"product": {
"arn": [
{
"Comparison": "string",
"Value": "string"
}
]
}
},
"severity": {
"label": [
{
"Comparison": "string",
"Value": "string"
}
],
"original": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"types": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"first_observed_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"generator": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"id": [
{
"Comparison": "string",
"Value": "string"
}
],
"keyword": [
{
"Value": "string"
}
],
"last_observed_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"malware": {
"name": [
{
"Comparison": "string",
"Value": "string"
}
],
"path": [
{
"Comparison": "string",
"Value": "string"
}
],
"state": [
{
"Comparison": "string",
"Value": "string"
}
],
"type": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"network": {
"destination": {
"domain": [
{
"Comparison": "string",
"Value": "string"
}
],
"ip": {
"v4": [
{
"Cidr": "string"
}
],
"v6": [
{
"Cidr": "string"
}
]
},
"port": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
]
},
"direction": [
{
"Comparison": "string",
"Value": "string"
}
],
"protocol": [
{
"Comparison": "string",
"Value": "string"
}
],
"source": {
"domain": [
{
"Comparison": "string",
"Value": "string"
}
],
"ip": {
"v4": [
{
"Cidr": "string"
}
],
"v6": [
{
"Cidr": "string"
}
]
},
"mac": [
{
"Comparison": "string",
"Value": "string"
}
],
"port": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
]
}
},
"note": {
"text": [
{
"Comparison": "string",
"Value": "string"
}
],
"updated_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"updated_by": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"process": {
"launched_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"name": [
{
"Comparison": "string",
"Value": "string"
}
],
"parent": {
"pid": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
]
},
"path": [
{
"Comparison": "string",
"Value": "string"
}
],
"pid": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
],
"terminated_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
]
},
"product": {
"arn": [
{
"Comparison": "string",
"Value": "string"
}
],
"fields": [
{
"Comparison": "string",
"Key": "string",
"Value": "string"
}
],
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"recommendation_text": [
{
"Comparison": "string",
"Value": "string"
}
],
"record_state": [
{
"Comparison": "string",
"Value": "string"
}
],
"region": [
{
"Comparison": "string",
"Value": "string"
}
],
"related_findings": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
],
"product": {
"arn": [
{
"Comparison": "string",
"Value": "string"
}
]
}
},
"resource": {
"aws_ec2_instance": {
"iam_instance_profile": {
"arn": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"image": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"ip": {
"v4_addresses": [
{
"Cidr": "string"
}
],
"v6_addresses": [
{
"Cidr": "string"
}
]
},
"key": {
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"launched_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"subnet": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"type": [
{
"Comparison": "string",
"Value": "string"
}
],
"vpc": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
]
}
},
"aws_iam_access_key": {
"created_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"principal": {
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"status": [
{
"Comparison": "string",
"Value": "string"
}
],
"user": {
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
}
},
"aws_iam_user": {
"user": {
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
}
},
"aws_s3_bucket": {
"owner": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
],
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
}
},
"container": {
"image": {
"id": [
{
"Comparison": "string",
"Value": "string"
}
],
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"launched_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"name": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"details_other": [
{
"Comparison": "string",
"Key": "string",
"Value": "string"
}
],
"id": [
{
"Comparison": "string",
"Value": "string"
}
],
"partition": [
{
"Comparison": "string",
"Value": "string"
}
],
"region": [
{
"Comparison": "string",
"Value": "string"
}
],
"tags": [
{
"Comparison": "string",
"Key": "string",
"Value": "string"
}
],
"type": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"sample": [
{
"Value": true
}
],
"severity": {
"label": [
{
"Comparison": "string",
"Value": "string"
}
],
"normalized": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
],
"product": [
{
"Eq": 20,
"Gte": 20,
"Lte": 20
}
]
},
"source_url": [
{
"Comparison": "string",
"Value": "string"
}
],
"threat_intel_indicator": {
"category": [
{
"Comparison": "string",
"Value": "string"
}
],
"last_observed_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"source": [
{
"Comparison": "string",
"Value": "string"
}
],
"source_url": [
{
"Comparison": "string",
"Value": "string"
}
],
"type": [
{
"Comparison": "string",
"Value": "string"
}
],
"value": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"title": [
{
"Comparison": "string",
"Value": "string"
}
],
"type": [
{
"Comparison": "string",
"Value": "string"
}
],
"updated_at": [
{
"date_range": {
"unit": "string",
"value": 20
},
"end": "2020-07-10T15:00:00.000Z",
"start": "2020-07-10T15:00:00.000Z"
}
],
"user_defined_fields": [
{
"Comparison": "string",
"Key": "string",
"Value": "string"
}
],
"verification": {
"state": [
{
"Comparison": "string",
"Value": "string"
}
]
},
"workflow": {
"state": [
{
"Comparison": "string",
"Value": "string"
}
],
"status": [
{
"Comparison": "string",
"Value": "string"
}
]
}
},
"group_by_attribute": "string",
"insight_arn": "string",
"name": "string"
}
},
"data_stream": {
"dataset": "aws.securityhub_insights",
"namespace": "32954",
"type": "logs"
},
"ecs": {
"version": "8.11.0"
},
"elastic_agent": {
"id": "fa813af5-4a32-4079-8743-a3f152e25625",
"snapshot": false,
"version": "8.19.4"
},
"event": {
"agent_id_status": "verified",
"created": "2025-12-09T09:35:13.696Z",
"dataset": "aws.securityhub_insights",
"ingested": "2025-12-09T09:35:16Z",
"kind": "event",
"original": "{\"Filters\":{\"AwsAccountId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"CompanyName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ComplianceStatus\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"Confidence\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"CreatedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"Criticality\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"Description\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"FindingProviderFieldsConfidence\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"FindingProviderFieldsCriticality\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"FindingProviderFieldsRelatedFindingsId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"FindingProviderFieldsRelatedFindingsProductArn\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"FindingProviderFieldsSeverityLabel\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"FindingProviderFieldsSeverityOriginal\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"FindingProviderFieldsTypes\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"FirstObservedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"GeneratorId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"Id\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"Keyword\":[{\"Value\":\"string\"}],\"LastObservedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"MalwareName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"MalwarePath\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"MalwareState\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"MalwareType\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"NetworkDestinationDomain\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"NetworkDestinationIpV4\":[{\"Cidr\":\"string\"}],\"NetworkDestinationIpV6\":[{\"Cidr\":\"string\"}],\"NetworkDestinationPort\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"NetworkDirection\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"NetworkProtocol\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"NetworkSourceDomain\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"NetworkSourceIpV4\":[{\"Cidr\":\"string\"}],\"NetworkSourceIpV6\":[{\"Cidr\":\"string\"}],\"NetworkSourceMac\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"NetworkSourcePort\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"NoteText\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"NoteUpdatedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"NoteUpdatedBy\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ProcessLaunchedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"ProcessName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ProcessParentPid\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"ProcessPath\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ProcessPid\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"ProcessTerminatedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"ProductArn\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ProductFields\":[{\"Comparison\":\"string\",\"Key\":\"string\",\"Value\":\"string\"}],\"ProductName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"RecommendationText\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"RecordState\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"Region\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"RelatedFindingsId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"RelatedFindingsProductArn\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsEc2InstanceIamInstanceProfileArn\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsEc2InstanceImageId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsEc2InstanceIpV4Addresses\":[{\"Cidr\":\"string\"}],\"ResourceAwsEc2InstanceIpV6Addresses\":[{\"Cidr\":\"string\"}],\"ResourceAwsEc2InstanceKeyName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsEc2InstanceLaunchedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"ResourceAwsEc2InstanceSubnetId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsEc2InstanceType\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsEc2InstanceVpcId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsIamAccessKeyCreatedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"ResourceAwsIamAccessKeyPrincipalName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsIamAccessKeyStatus\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsIamAccessKeyUserName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsIamUserUserName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsS3BucketOwnerId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceAwsS3BucketOwnerName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceContainerImageId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceContainerImageName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceContainerLaunchedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"ResourceContainerName\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceDetailsOther\":[{\"Comparison\":\"string\",\"Key\":\"string\",\"Value\":\"string\"}],\"ResourceId\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourcePartition\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceRegion\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ResourceTags\":[{\"Comparison\":\"string\",\"Key\":\"string\",\"Value\":\"string\"}],\"ResourceType\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"Sample\":[{\"Value\":true}],\"SeverityLabel\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"SeverityNormalized\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"SeverityProduct\":[{\"Eq\":20,\"Gte\":20,\"Lte\":20}],\"SourceUrl\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ThreatIntelIndicatorCategory\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ThreatIntelIndicatorLastObservedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"ThreatIntelIndicatorSource\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ThreatIntelIndicatorSourceUrl\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ThreatIntelIndicatorType\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"ThreatIntelIndicatorValue\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"Title\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"Type\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"UpdatedAt\":[{\"DateRange\":{\"Unit\":\"string\",\"Value\":20},\"End\":\"2020-07-10 15:00:00.000\",\"Start\":\"2020-07-10 15:00:00.000\"}],\"UserDefinedFields\":[{\"Comparison\":\"string\",\"Key\":\"string\",\"Value\":\"string\"}],\"VerificationState\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"WorkflowState\":[{\"Comparison\":\"string\",\"Value\":\"string\"}],\"WorkflowStatus\":[{\"Comparison\":\"string\",\"Value\":\"string\"}]},\"GroupByAttribute\":\"string\",\"InsightArn\":\"string\",\"Name\":\"string\"}",
"type": [
"info"
]
},
"input": {
"type": "httpjson"
},
"observer": {
"vendor": "AWS Security Hub CSPM"
},
"tags": [
"preserve_original_event",
"forwarded",
"aws_securityhub_insights"
]
}
ECS Field Reference
Please refer to the following document for detailed information on ECS fields.
Exported fields
| Field | Description | Type |
|---|---|---|
| @timestamp | Event timestamp. | date |
| aws.securityhub_insights.filters.aws_account_id | The Amazon Web Services account ID that a finding is generated in. | flattened |
| aws.securityhub_insights.filters.company.name | The name of the findings provider(company) that owns the solution(product) that generates findings. | flattened |
| aws.securityhub_insights.filters.compliance.status | Exclusive to findings that are generated as the result of a check run against a specific rule in a supported standard, such as CIS Amazon Web Services Foundations. Contains security standard-related finding details. | flattened |
| aws.securityhub_insights.filters.confidence | A finding's confidence. Confidence is defined as the likelihood that a finding accurately identifies the behavior or issue that it was intended to identify. | flattened |
| aws.securityhub_insights.filters.created_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.created_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.created_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.created_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.criticality | The level of importance assigned to the resources associated with the finding. | flattened |
| aws.securityhub_insights.filters.description | A finding's description. | flattened |
| aws.securityhub_insights.filters.finding_provider_fields.confidence | The finding provider value for the finding confidence. Confidence is defined as the likelihood that a finding accurately identifies the behavior or issue that it was intended to identify. | flattened |
| aws.securityhub_insights.filters.finding_provider_fields.criticality | The finding provider value for the level of importance assigned to the resources associated with the findings. | flattened |
| aws.securityhub_insights.filters.finding_provider_fields.related_findings.id | The finding identifier of a related finding that is identified by the finding provider. | flattened |
| aws.securityhub_insights.filters.finding_provider_fields.related_findings.product.arn | The ARN of the solution that generated a related finding that is identified by the finding provider. | flattened |
| aws.securityhub_insights.filters.finding_provider_fields.severity.label | The finding provider value for the severity label. | flattened |
| aws.securityhub_insights.filters.finding_provider_fields.severity.original | The finding provider's original value for the severity. | flattened |
| aws.securityhub_insights.filters.finding_provider_fields.types | One or more finding types that the finding provider assigned to the finding. Uses the format of namespace/category/classifier that classify a finding. | flattened |
| aws.securityhub_insights.filters.first_observed_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.first_observed_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.first_observed_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.first_observed_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.generator.id | The identifier for the solution-specific component(a discrete unit of logic) that generated a finding. In various security-findings providers' solutions, this generator can be called a rule, a check, a detector, a plugin, etc. | flattened |
| aws.securityhub_insights.filters.id | The security findings provider-specific identifier for a finding. | flattened |
| aws.securityhub_insights.filters.keyword | A keyword for a finding. | flattened |
| aws.securityhub_insights.filters.last_observed_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.last_observed_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.last_observed_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.last_observed_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.malware.name | The name of the malware that was observed. | flattened |
| aws.securityhub_insights.filters.malware.path | The filesystem path of the malware that was observed. | flattened |
| aws.securityhub_insights.filters.malware.state | The state of the malware that was observed. | flattened |
| aws.securityhub_insights.filters.malware.type | The type of the malware that was observed. | flattened |
| aws.securityhub_insights.filters.network.destination.domain | The destination domain of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.destination.ip.v4 | The destination IPv4 address of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.destination.ip.v6 | The destination IPv6 address of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.destination.port | The destination port of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.direction | Indicates the direction of network traffic associated with a finding. | flattened |
| aws.securityhub_insights.filters.network.protocol | The protocol of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.source.domain | The source domain of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.source.ip.v4 | The source IPv4 address of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.source.ip.v6 | The source IPv6 address of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.source.mac | The source media access control(MAC) address of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.network.source.port | The source port of network-related information about a finding. | flattened |
| aws.securityhub_insights.filters.note.text | The text of a note. | flattened |
| aws.securityhub_insights.filters.note.updated_at.by | The principal that created a note. | flattened |
| aws.securityhub_insights.filters.note.updated_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.note.updated_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.note.updated_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.note.updated_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.note.updated_by | The text of a note. | flattened |
| aws.securityhub_insights.filters.process.launched_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.process.launched_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.process.launched_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.process.launched_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.process.name | The name of the process. | flattened |
| aws.securityhub_insights.filters.process.parent.pid | The parent process ID. | flattened |
| aws.securityhub_insights.filters.process.path | The path to the process executable. | flattened |
| aws.securityhub_insights.filters.process.pid | The process ID. | flattened |
| aws.securityhub_insights.filters.process.terminated_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.process.terminated_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.process.terminated_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.process.terminated_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.product.arn | The ARN generated by Security Hub that uniquely identifies a third-party company(security findings provider) after this provider's product(solution that generates findings) is registered with Security Hub. | flattened |
| aws.securityhub_insights.filters.product.fields | A data type where security-findings providers can include additional solution-specific details that aren't part of the defined AwsSecurityFinding format. | flattened |
| aws.securityhub_insights.filters.product.name | The name of the solution(product) that generates findings. | flattened |
| aws.securityhub_insights.filters.recommendation_text | The recommendation of what to do about the issue described in a finding. | flattened |
| aws.securityhub_insights.filters.record_state | The updated record state for the finding. | flattened |
| aws.securityhub_insights.filters.region | The Region from which the finding was generated. | flattened |
| aws.securityhub_insights.filters.related_findings.id | The solution-generated identifier for a related finding. | flattened |
| aws.securityhub_insights.filters.related_findings.product.arn | The ARN of the solution that generated a related finding. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.iam_instance_profile.arn | The IAM profile ARN of the instance. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.image.id | The Amazon Machine Image(AMI) ID of the instance. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.ip.v4_addresses | The IPv4 addresses associated with the instance. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.ip.v6_addresses | The IPv6 addresses associated with the instance. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.key.name | The key name associated with the instance. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.launched_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.launched_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.launched_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.launched_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.subnet.id | The identifier of the subnet that the instance was launched in. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.type | The instance type of the instance. | flattened |
| aws.securityhub_insights.filters.resource.aws_ec2_instance.vpc.id | The identifier of the VPC that the instance was launched in. | flattened |
| aws.securityhub_insights.filters.resource.aws_iam_access_key.created_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.resource.aws_iam_access_key.created_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.resource.aws_iam_access_key.created_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.resource.aws_iam_access_key.created_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.resource.aws_iam_access_key.principal.name | The name of the principal that is associated with an IAM access key. | flattened |
| aws.securityhub_insights.filters.resource.aws_iam_access_key.status | The status of the IAM access key related to a finding. | flattened |
| aws.securityhub_insights.filters.resource.aws_iam_access_key.user.name | The user associated with the IAM access key related to a finding. | flattened |
| aws.securityhub_insights.filters.resource.aws_iam_user.user.name | The name of an IAM user. | flattened |
| aws.securityhub_insights.filters.resource.aws_s3_bucket.owner.id | The canonical user ID of the owner of the S3 bucket. | flattened |
| aws.securityhub_insights.filters.resource.aws_s3_bucket.owner.name | The display name of the owner of the S3 bucket. | flattened |
| aws.securityhub_insights.filters.resource.container.image.id | The identifier of the image related to a finding. | flattened |
| aws.securityhub_insights.filters.resource.container.image.name | The name of the image related to a finding. | flattened |
| aws.securityhub_insights.filters.resource.container.launched_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.resource.container.launched_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.resource.container.launched_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.resource.container.launched_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.resource.container.name | The name of the container related to a finding. | flattened |
| aws.securityhub_insights.filters.resource.details_other | The details of a resource that doesn't have a specific subfield for the resource type defined. | flattened |
| aws.securityhub_insights.filters.resource.id | The canonical identifier for the given resource type. | flattened |
| aws.securityhub_insights.filters.resource.partition | The canonical Amazon Web Services partition name that the Region is assigned to. | flattened |
| aws.securityhub_insights.filters.resource.region | The canonical Amazon Web Services external Region name where this resource is located. | flattened |
| aws.securityhub_insights.filters.resource.tags | A list of Amazon Web Services tags associated with a resource at the time the finding was processed. | flattened |
| aws.securityhub_insights.filters.resource.type | Specifies the type of the resource that details are provided for. | flattened |
| aws.securityhub_insights.filters.sample | Indicates whether or not sample findings are included in the filter results. | flattened |
| aws.securityhub_insights.filters.severity.label | The label of a finding's severity. | flattened |
| aws.securityhub_insights.filters.severity.normalized | The normalized severity of a finding. | flattened |
| aws.securityhub_insights.filters.severity.product | The native severity as defined by the security-findings provider's solution that generated the finding. | flattened |
| aws.securityhub_insights.filters.source_url | A URL that links to a page about the current finding in the security-findings provider's solution. | flattened |
| aws.securityhub_insights.filters.threat_intel_indicator.category | The category of a threat intelligence indicator. | flattened |
| aws.securityhub_insights.filters.threat_intel_indicator.last_observed_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.threat_intel_indicator.last_observed_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.threat_intel_indicator.last_observed_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.threat_intel_indicator.last_observed_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.threat_intel_indicator.source | The source of the threat intelligence. | flattened |
| aws.securityhub_insights.filters.threat_intel_indicator.source_url | The URL for more details from the source of the threat intelligence. | flattened |
| aws.securityhub_insights.filters.threat_intel_indicator.type | The type of a threat intelligence indicator. | flattened |
| aws.securityhub_insights.filters.threat_intel_indicator.value | The value of a threat intelligence indicator. | flattened |
| aws.securityhub_insights.filters.title | A finding's title. | flattened |
| aws.securityhub_insights.filters.type | A finding type in the format of namespace/category/classifier that classifies a finding. | flattened |
| aws.securityhub_insights.filters.updated_at.date_range.unit | A date range unit for the date filter. | keyword |
| aws.securityhub_insights.filters.updated_at.date_range.value | A date range value for the date filter. | long |
| aws.securityhub_insights.filters.updated_at.end | An end date for the date filter. | date |
| aws.securityhub_insights.filters.updated_at.start | A start date for the date filter. | date |
| aws.securityhub_insights.filters.user_defined_fields | A list of name/value string pairs associated with the finding. These are custom, user-defined fields added to a finding. | flattened |
| aws.securityhub_insights.filters.verification.state | The veracity of a finding. | flattened |
| aws.securityhub_insights.filters.workflow.state | The workflow state of a finding. | flattened |
| aws.securityhub_insights.filters.workflow.status | The status of the investigation into a finding. | flattened |
| aws.securityhub_insights.group_by_attribute | The grouping attribute for the insight's findings. Indicates how to group the matching findings, and identifies the type of item that the insight applies to. For example, if an insight is grouped by resource identifier, then the insight produces a list of resource identifiers. | keyword |
| aws.securityhub_insights.insight_arn | The ARN of a Security Hub insight. | keyword |
| aws.securityhub_insights.name | The name of a Security Hub insight. | keyword |
| cloud.image.id | Image ID for the cloud instance. | keyword |
| data_stream.dataset | Data stream dataset. | constant_keyword |
| data_stream.namespace | Data stream namespace. | constant_keyword |
| data_stream.type | Data stream type. | constant_keyword |
| event.module | Event module. | constant_keyword |
| host.containerized | If the host is a container. | boolean |
| host.os.build | OS build information. | keyword |
| host.os.codename | OS codename, if any. | keyword |
| input.type | Input type | keyword |
| log.offset | Log offset | long |
| observer.vendor | Vendor name of the observer. | constant_keyword |
This integration includes one or more Kibana dashboards that visualizes the data collected by the integration. The screenshots below illustrate how the ingested data is displayed.
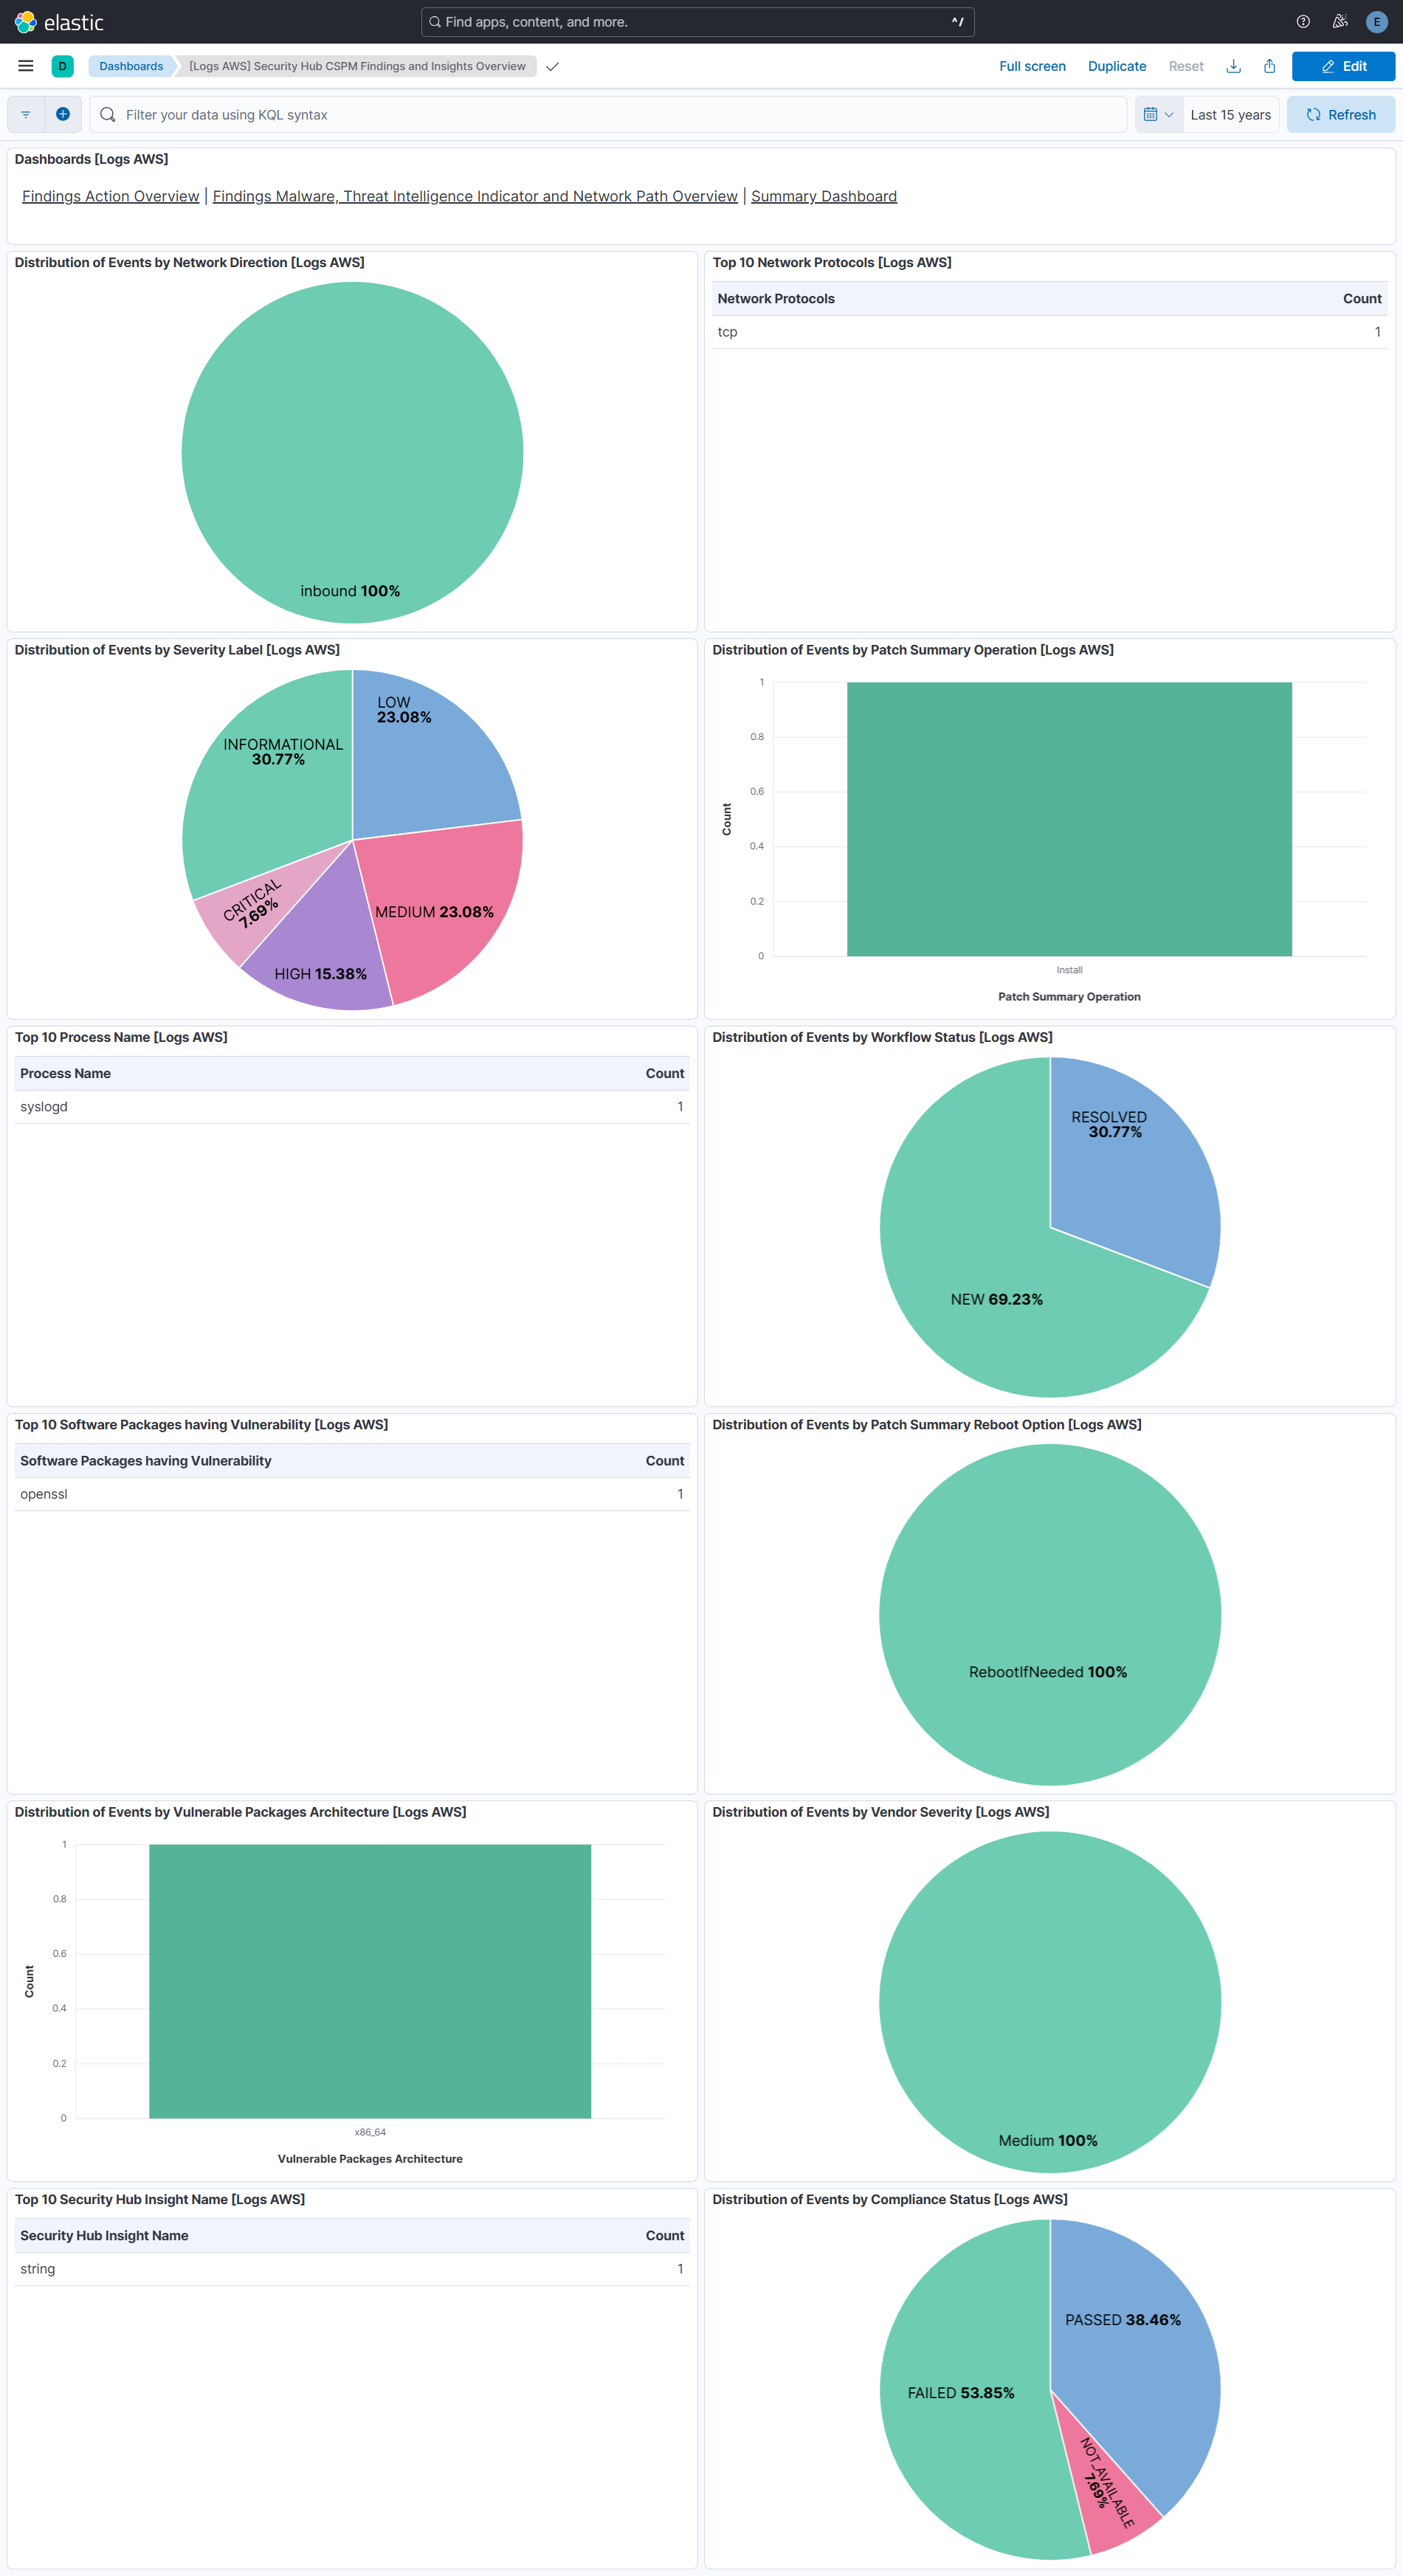
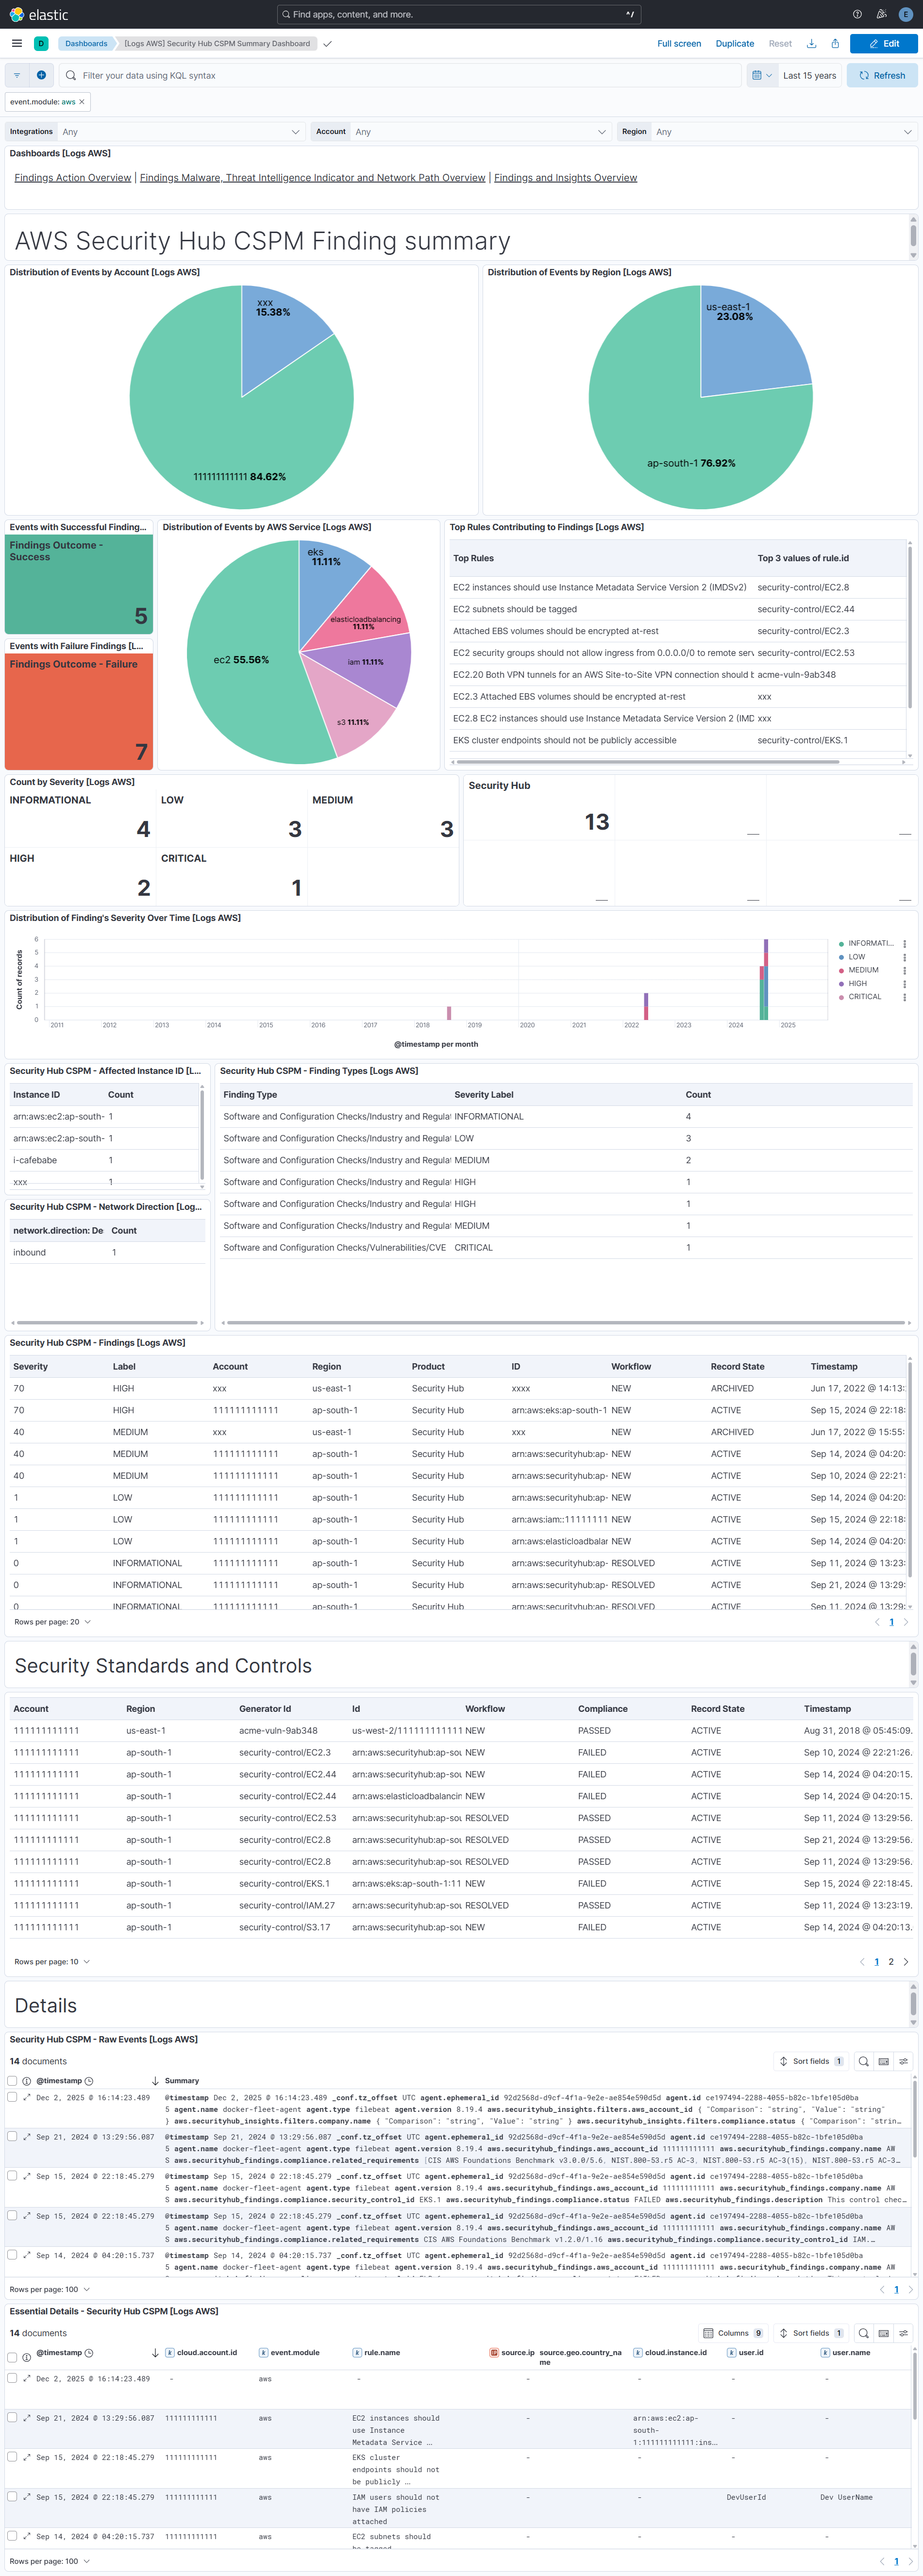
Changelog
| Version | Details | Minimum Kibana version |
|---|---|---|
| 7.1.5 | Enhancement (View pull request) The changes below apply to the Security Hub CSPM data streams ( securityhub_findings, securityhub_findings_full_posture and securityhub_insights) only.Sign requests with the native auth.aws configuration instead of a hand-rolled SigV4 template. This adds support for session tokens, shared credentials files, credential profiles and assume-role (including external_id).Migrate the Findings and Findings Full Posture data streams from the httpjson input to CEL via run_as_cel. The persisted Findings collection cursor is carried over, so collection resumes from where it stopped.Bug fix (View pull request) The fixes below apply to the Security Hub CSPM data streams only. Fix intermittent SignatureDoesNotMatch (HTTP 403) errors in the Findings, Findings Full Posture and Insights data streams caused by the hand-rolled SigV4 template evaluating now separately for the X-Amz-Date header and the Authorization signature.Fix Invalid NextToken errors (HTTP 400/403) when paginating large GetFindings result sets in the Findings data stream. The UpdatedAt window start is now pinned once per collection interval, so it cannot change between pages and invalidate the NextToken. |
9.4.0 |
| 7.1.4 | Bug fix (View pull request) Wrap the www.amazon.com:app_id and www.amazon.com:user_id examples in the user_identity.session_context.web_id_federation_data.attributes field description in backticks so they render as inline code instead of being autolinked into invalid URLs when docs are generated. |
9.4.0 |
| 7.1.3 | Enhancement (View pull request) The changes below apply to the CloudTrail data stream only. Replace every ignore_failure: true with an ignore_missing flag, a condition guard, or an explicit on_failure handler reporting to error.message, so real faults surface instead of being silently swallowed.Add support for CloudTrail fields that were previously dropped. Populate the cloud.provider, cloud.service.name and related.* ECS fields.Bug fix (View pull request) The fixes below apply to the CloudTrail data stream only. Stop populating file.hash.sha256 on digest records, where it held the hash of the previous digest file while file.path pointed at the current one. The value is still available as aws.cloudtrail.digest.previous_hash_value and in related.hash.Fix DeleteObject using event.type: delete, which is not a valid ECS value. It is now deletion.Fix Publish, SendCommand and Converse producing no event.type. They now use info, start and info respectively.Fix retain: none behaving like retain: all. It now drops both the keyword and the flattened copies as documented.Fix retain: keyword and retain: minimal discarding digest and Insights records. The setting governs API call payloads and no longer affects either record type.Fix aws.cloudtrail.service_event_details surviving retain: flattened and retain: none. It is now governed like the other payload fields. |
9.4.0 |
| 7.1.2 | Bug fix (View pull request) Add an Instance or Pod IAM Role option to the Setup Access selector so Elastic Agent can authenticate with the AWS SDK default credential chain (EC2 instance profile, EKS Pod Identity or IRSA) without entering access keys or a Role ARN. Since 7.0.0 every option required at least one credential field, which made this documented path impossible to save. |
9.4.0 |
| 7.1.1 | Bug fix (View pull request) Add data_stream.namespace to the Amazon Inspector vulnerability latest transform's unique key so findings are tracked per namespace, preventing findings ingested into non-default namespaces from being dropped or conflated in the latest index. Bump transform's destination suffix to -v2. |
9.4.0 |
| 7.1.0 | Enhancement (View pull request) Stop storing the assumed-role ARN session name in user.changes.*. The session name is now added to related.user for cross-source correlation; when it is an email, both the full email and the local-part prefix are added. user.name continues to hold the IAM role name for detection rules. |
9.4.0 |
| 7.0.0 | Enhancement (View pull request) Hide the CloudWatch, EBS, EC2, ECS, and S3 metric/log inputs when the Identity Federation setup access option is selected, since only the GuardDuty API input supports identity federation. Enhancement (View pull request) Reorganize AWS credentials configuration into a Setup Access selector with Identity Federation, Direct Access Keys, Temporary Access Keys, Assume Role, Assume Role with External ID, and Shared Credentials options. Existing access keys, role ARN, and shared credential settings continue to function and are auto-mapped to the corresponding option.Enhancement (View pull request) Switch the GuardDuty httpjson stream from manual SigV4 HMAC signing to the native auth.aws block.Breaking change (View pull request) Store the external_id variable as a secret.Enhancement (View pull request) Add assume_role_duration, assume_role_expiry_window, and supports_identity_federation variables.Breaking change (View pull request) Require Kibana and Elastic Agent ^9.4.0 (drop support for Kibana 8.x, Kibana 9.x below 9.4.0, and Elastic Agent below 9.4.0). The var_groups manifest feature and auth.aws runtime require this minimum. |
9.4.0 |
| 6.21.0 | Bug fix (View pull request) Poll Amazon Inspector findings on updatedAt instead of lastObservedAt so that findings AWS marks CLOSED or SUPPRESSED are collected and no longer remain stale in Elastic.Enhancement (View pull request) Include all Inspector finding statuses in the vulnerability latest transform and map aws.inspector.status to the vulnerability.status field (CLOSED as fixed), so remediated findings can be filtered out on the Vulnerability Findings page.Enhancement (View pull request) Add a lag_time variable to the Amazon Inspector data stream that offsets the poll cursor to tolerate delay between when a finding's updatedAt is set and when it becomes available from the API, preventing missed findings. |
9.2.1 8.19.4 |
| 6.20.4 | Bug fix (View pull request) Add security category to the Transit Gateway data stream to match its policy template categories. |
9.2.1 8.19.4 |
| 6.20.3 | Enhancement (View pull request) Add processor tags to all ingest pipeline processors to satisfy elastic-package linter requirements for format_version 3.6.0 and above. |
— |
| 6.20.2 | Bug fix (View pull request) Skip AWS service-linked Config rules when collecting compliance details so the AWS Config data stream no longer degrades on AccessDeniedException, and treat per-rule compliance errors as non-fatal so a single failing rule does not stop ingestion of the rest. |
9.2.1 8.19.4 |
| 6.20.1 | Bug fix (View pull request) Revert addition of assignment of host.id from CloudTrail target hosts. |
9.2.1 8.19.4 |
| 6.20.0 | Enhancement (View pull request) Enable agentless deployment mode for CloudWatch, EBS, EC2, ECS, and S3 policy templates. Bug fix (View pull request) Disable TSDB on the S3 daily storage data stream to avoid rejection of late-arriving daily CloudWatch metrics. |
9.2.1 8.19.4 |
| 6.19.2 | Bug fix (View pull request) Restore a stable endInclusive bound to Inspector findings filter to prevent potential nextToken invalidation. |
9.2.1 8.19.4 |
| 6.19.1 | Bug fix (View pull request) Fix aws.lambda.message flattened field handling. |
9.2.1 8.19.4 |
| 6.19.0 | Enhancement (View pull request) Use new release field for agentless deployment mode to establish as beta. |
9.2.1 8.19.4 |
| 6.18.1 | Enhancement (View pull request) Add documentation for authenticating the CloudTrail integration using AWS IAM Roles Anywhere for agents running outside AWS. |
9.2.1 8.19.4 |
| 6.18.0 | Enhancement (View pull request) Set event.kind to alert for AWS GuardDuty findings. |
9.2.1 8.19.4 |
| 6.17.1 | Bug fix (View pull request) Fix Security Hub findings collection by restoring a stable UpdatedAt end bound. |
9.2.1 8.19.4 |
| 6.17.0 | Enhancement (View pull request) Add ingest timestamp to AWS CloudWatch logs if timestamp is not present in the event. |
9.2.1 8.19.4 |
| 6.16.0 | Enhancement (View pull request) Add fail guard for unsupported VPC Flow Log formats so unrecognised records surface as pipeline errors instead of indexing silently unparsed. |
9.2.1 8.19.4 |
| 6.15.0 | Enhancement (View pull request) Add S3 polling mode performance recommendations to CloudTrail docs |
9.2.1 8.19.4 |
| 6.14.2 | Bug fix (View pull request) Fix NextToken invalidation in Security Hub, GuardDuty, and Inspector by removing the upper time bound from paginated queries. |
9.2.1 8.19.4 |
| 6.14.1 | Bug fix (View pull request) Handle null EvaluationResults in AWS Config GetComplianceDetailsByConfigRule response. |
9.2.1 8.19.4 |
| 6.14.0 | Enhancement (View pull request) Enable agentless deployment for AWS RDS metrics. |
9.2.1 8.19.4 |
| 6.13.0 | Enhancement (View pull request) Enable agentless deployment for AWS DynamoDB metrics. |
9.2.1 8.19.4 |
| 6.12.0 | Enhancement (View pull request) Enable agentless deployment for AWS SNS metrics. |
9.2.1 8.19.4 |
| 6.11.0 | Enhancement (View pull request) Enable agentless deployment for AWS Transitgateway metrics. |
9.2.1 8.19.4 |
| 6.10.0 | Enhancement (View pull request) Enable agentless deployment for AWS Billing metrics. |
9.2.1 8.19.4 |
| 6.9.0 | Enhancement (View pull request) Enable agentless deployment for AWS Health metrics. |
9.2.1 8.19.4 |
| 6.8.0 | Enhancement (View pull request) Enable agentless deployment for AWS SQS metrics. |
9.2.1 8.19.4 |
| 6.7.0 | Enhancement (View pull request) Enable agentless deployment for AWS ELB metrics. |
9.2.1 8.19.4 |
| 6.6.0 | Enhancement (View pull request) Enable agentless deployment for AWS Lambda metrics. |
9.2.1 8.19.4 |
| 6.5.1 | Bug fix (View pull request) Add credential validation to AWS Config CEL program to emit a clear error when access_key_id or secret_access_key are missing. Document that the AWS Config data stream requires static credentials and does not support Role ARN or other SDK-based credential methods. |
9.2.1 8.19.4 |
| 6.5.0 | Enhancement (View pull request) Add timestamp range filter and storage tier exclusion to latest transform source queries to reduce scan scope and improve performance. |
9.2.1 8.19.4 |
| 6.4.3 | Bug fix (View pull request) Align event.kind with ECS in securityhub_findings_full_posture data stream to avoid conflicts with ingest pipeline values. |
9.2.1 8.19.4 |
| 6.4.2 | Bug fix (View pull request) Revert event.kind from alert to event on AWS WAF. |
9.2.1 8.19.4 |
| 6.4.1 | Bug fix (View pull request) Ignore uri_parts failures on S3 access log request paths that the URI parser cannot handle. |
9.2.1 8.19.4 |
| 6.4.0 | Enhancement (View pull request) Set host.id alongside host.target.entity.id in CloudTrail pipeline for entity store host entity resolution. |
9.2.1 8.19.4 |
| 6.3.2 | Bug fix (View pull request) Fix s3access ingest pipeline to handle host headers with ports and Source region field parsing. |
9.2.1 8.19.4 |
| 6.3.1 | Bug fix (View pull request) Fix CloudTrail pipeline errors causing transient json and _conf fields to leak into indexed documents by cleaning them up in the on_failure handler, preventing dynamic mapping conflicts. |
9.2.1 8.19.4 |
| 6.3.0 | Enhancement (View pull request) Removed ECS field definitions from CDR transform destinations, now covered by ecs@mappings component template. Renamed overridden ECS fields files to ecs-overridden.yml for awsconfig and awsinspector transforms. |
9.2.1 8.19.4 |
| 6.2.0 | Enhancement (View pull request) Add support for the aws.waf.captcha_response.*, aws.waf.challenge_response.*, aws.waf.format_version, aws.waf.ja4_fingerprint, aws.waf.labels.name, aws.waf.oversize_fields, aws.waf.request_body_size, aws.waf.request_body_size_inspected_by_waf, aws.waf.response_code_sent, aws.waf.request_headers_inserted.*, host.domain, tls.client.ja3, url.fragment and url.scheme in waf data stream.aws.waf.request_headers_inserted.*, tls.client.ja3, url.registered_domain, url.fragment and url.scheme in waf data stream. |
9.2.1 8.19.4 |
| 6.1.1 | Bug fix (View pull request) Remove duplicate security-solution-default tag references |
9.2.1 8.19.4 |
| 6.1.0 | Bug fix (View pull request) Remove fixed value event.dataset mapping for lambda_logs data stream. |
9.2.1 8.19.4 |
| 6.0.0 | Breaking change (View pull request) Remove third-party pipeline for previously removed 'third-party REST API' input from 'AWS Cloudtrail'. |
9.2.1 8.19.4 |
| 5.6.1 | Bug fix (View pull request) Fix Cloudtrail's Lambda event parsing of vpcConfig.securityGroupIds and vpcConfig.subnetIds fields. |
9.2.1 8.19.4 |
| 5.6.0 | Enhancement (View pull request) Update AWS ALB Grok patterns to support the conn_trace_id field and parse malformed requests missing HTTP versions. |
9.2.1 8.19.4 |
| 5.5.1 | Bug fix (View pull request) Added support for extracting user name from AWS GovCloud STS ARNs and fixed management_event field type conversion. |
9.2.1 8.19.4 |
| 5.5.0 | Enhancement (View pull request) Add dashboards for AWS Web Application Firewall data stream. |
9.2.1 8.19.4 |
| 5.4.1 | Enhancement (View pull request) S3 Access logs, improve S3KEY regex to handle special characters. |
9.2.1 8.19.4 |
| 5.4.0 | Enhancement (View pull request) Add ec2_metrics, lambda, sqs and sns alert rule templates. |
9.2.1 8.19.4 |
| 5.3.1 | Bug fix (View pull request) Add cookies field in cloudfront logs datastream. |
9.1.4 8.19.4 |
| 5.3.0 | Enhancement (View pull request) Added rate limiting and retry configuration for AWS Config data stream. |
9.1.4 8.19.4 |
| 5.2.0 | Enhancement (View pull request) Normalize user fields for AWS CloudTrail events. |
9.1.4 8.19.4 |
| 5.1.0 | Enhancement (View pull request) Set event.kind to alert on AWS WAF events. |
9.1.4 8.19.4 |
| 5.0.0 | Breaking change (View pull request) Rebrand AWS Security Hub as AWS Security Hub CSPM to align with the vendor's current branding. This change involves updating the observer.vendor value to AWS Security Hub CSPM. |
9.1.4 8.19.4 |
| 4.7.0 | Enhancement (View pull request) Add type-specific entity fields to data stream. This enables better entity classification while maintaining backward compatibility with existing actor.entity.id and target.entity.id fields. |
9.1.4 8.19.4 |
| 4.6.0 | Enhancement (View pull request) Retain CloudTrail sessionCredentialFromConsole field as aws.cloudtrail.session_credential_from_console. |
9.1.4 8.19.4 |
| 4.5.0 | Enhancement (View pull request) Prevent updating fleet health status to degraded when the HTTPJSON template value evaluation is empty. |
9.1.4 8.19.4 |
| 4.4.0 | Enhancement (View pull request) Prefer set with copy_from. |
9.1.0 8.19.0 |
| 4.3.2 | Bug fix (View pull request) Update transform to filter out document containing an error.message from AWS Config, AWS Inspector, and AWS Security Hub latest indexes. |
9.1.0 8.19.0 |
| 4.3.1 | Bug fix (View pull request) Update the AWS CloudWatch documentation. |
9.1.0 8.19.0 |
| 4.3.0 | Enhancement (View pull request) Improve documentation to align with new guidelines. |
9.1.0 8.19.0 |
| 4.2.0 | Enhancement (View pull request) Add user.name to Cloudtrail's UserAuthentication events. |
9.1.0 8.19.0 |
| 4.1.0 | Enhancement (View pull request) Add vulnerability_workflow and misconfiguration_workflow sub category labels. |
9.1.0 8.19.0 |
| 4.0.0 | Enhancement (View pull request) Add latest transform to AWS Config and AWS Inspector.This enables support for extended protections for AWS Config and AWS Inspector.Breaking change (View pull request) The latest transforms requires transform node and necessary permissions to use the transform.The transforms stores the latest copy of vulnerabilities and misconfigurations in the destination indices, which will require additional storage. Due to change in fingeprinting on source indices, duplicates occur on source indices of AWS Config and AWS Inspector. |
9.1.0 8.19.0 |
| 3.17.2 | Bug fix (View pull request) Fix Cloudtrail's Lambda event parsing of vpcConfig.securityGroupIds and vpcConfig.subnetIds fields. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.17.1 | Bug fix (View pull request) Disable lastSync start_position configuration for CloudWatch as it's incompatible with versions below 9.x. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.17.0 | Enhancement (View pull request) Enable Agentless deployment for AWS GuardDuty. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.16.0 | Enhancement (View pull request) Map recipient_account_id to cloud.account.id for AWS CloudTrail. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.15.0 | Enhancement (View pull request) Add support for VPC Flow logs versions 6, 7, and 8. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.14.2 | Bug fix (View pull request) Remove unused agent files. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.14.1 | Bug fix (View pull request) Fixed issue where empty DescribeConfigRules responses caused 'index out of bounds' errors in AWS Config integration. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.14.0 | Enhancement (View pull request) Prevent logging expected agent HTTP JSON template errors. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.13.4 | Bug fix (View pull request) Add description on lastSync start_position configuration for CloudWatch. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.13.3 | Bug fix (View pull request) Remove redundant code from config data stream agent configuration. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.13.2 | Bug fix (View pull request) Remove Include Linked Accounts config option from AWS Health. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.13.1 | Bug fix (View pull request) Avoid updating fleet health status to degraded when Guardduty has no findings. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.13.0 | Enhancement (View pull request) Reduce unnecessary work done in cloudtrail data stream when flattened fields are not required. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.12.0 | Enhancement (View pull request) Mapping changes in inspector datastream for Cloud Detection and Response (CDR) vulnerability workflow.Parse and map newly introduced fields in the inspector data stream.Enable request trace log removal and Agentless deployment in the inspector data stream. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.11.0 | Bug fix (View pull request) Fix tlsVersion parsing when not properly defined in cloudtrail event.Enhancement (View pull request) Add empty value removal script to cloudtrail data stream ingest pipeline. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.10.1 | Bug fix (View pull request) Fix configuration template typo. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.10.0 | Enhancement (View pull request) Allow user-specification of fields to retain in the cloudtrail data stream. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.9.0 | Enhancement (View pull request) Ingest managed insights from Security Hub. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.8.2 | Bug fix (View pull request) Fix null reference in securityhub_findings* data streams when extracting host.ip. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.8.1 | Bug fix (View pull request) Modify the data type of event.kind from a constant_keyword to a keyword to handle pipeline errors that send event.kind as pipeline_error. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.8.0 | Enhancement (View pull request) Standardize user fields processing across integrations. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.7.1 | Bug fix (View pull request) Add temporary processor to remove the fields added by the Agentless policy. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.7.0 | Enhancement (View pull request) Add AWS lambda logs overview dashboard. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.6.0 | Enhancement (View pull request) Add AWS lambda logs dataset. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.5.2 | Bug fix (View pull request) Add Redshift InstanceType dimension. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.5.1 | Enhancement (View pull request) Change Redshift terraform node type because dc2.large is deprecated and leads to system tests fails. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.5.0 | Enhancement (View pull request) Add the external_id field to data streams collecting data from S3. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.4.0 | Enhancement (View pull request) Add new AWS Config datastream. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.3.3 | Enhancement (View pull request) Update README - Document ingested log types of AWS Network Firewall. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.3.2 | Enhancement (View pull request) Update README - EC2 Instance IAM Role for AWS Authentication |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.3.1 | Bug fix (View pull request) Fix handling of duplicate fields in Network Firewall Logs data stream. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.3.0 | Enhancement (View pull request) Remove deprecated httpjson input for cloudtrail data stream. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.2.0 | Enhancement (View pull request) Add agentless deployment for AWS Security Hub. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.1.0 | Enhancement (View pull request) Enhancements for Guardduty dashboards. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 3.0.0 | Breaking change (View pull request) Add new Security Hub Findings Full Posture data stream. If you rely on Findings > Misconfigurations view, enable this new data stream. |
9.0.0 8.18.0 8.17.4 8.16.6 |
| 2.45.2 | Enhancement (View pull request) Update grok pattern for AWS S3 access ingest pipeline |
9.0.0 8.16.5 |
| 2.45.1 | Bug fix (View pull request) Fix handling of SQS worker count configuration. |
9.0.0 8.16.5 |
| 2.45.0 | Breaking change (View pull request) Update default data_stream.dataset to aws.cloudwatch_logs for cloudwatch_logs data stream. |
9.0.0 8.16.5 |
| 2.44.0 | Enhancement (View pull request) Add actor.entity.id and target.entity.id |
9.0.0 8.16.5 |
| 2.43.0 | Enhancement (View pull request) Set event.type and event.action fields in vpcflow logs. |
9.0.0 8.16.5 |
| 2.42.0 | Enhancement (View pull request) Add support to configure start_timestamp and ignore_older configurations for AWS S3 backed inputs. |
9.0.0 8.16.5 |
| 2.41.1 | Bug fix (View pull request) Updated SSL description to be uniform and to include links to documentation. |
9.0.0 8.16.2 |
| 2.41.0 | Enhancement (View pull request) Ignore long cloudtrail.request_parameters and cloudtrail.response_elements fields. |
9.0.0 8.16.2 |
| 2.40.0 | Enhancement (View pull request) Add support for Kibana 9.0.0. |
9.0.0 8.16.2 |
| 2.39.0 | Enhancement (View pull request) Allow the usage of deprecated log input and support for stack 9.0 |
8.16.2 |
| 2.38.2 | Bug fix (View pull request) Update links to getting started docs |
8.16.2 |
| 2.38.1 | Enhancement (View pull request) Add missing category. |
8.16.2 |
| 2.38.0 | Enhancement (View pull request) Add support for Access Point ARN when collecting logs via the AWS S3 Bucket. |
8.16.2 |
| 2.37.0 | Enhancement (View pull request) Map aws.dimensions as object instead of flattened in CloudWatch metrics. |
8.16.0 |
| 2.36.2 | Enhancement (View pull request) Include pipeline test examples to accommodate the new Cloudtrail format for the CreateGroup and UpdateGroup event types. |
8.16.0 |
| 2.36.1 | Enhancement (View pull request) Add SQS API calls documentation and required S3 permissions. |
8.16.0 |
| 2.36.0 | Enhancement (View pull request) Add ELB connection logs dashboards for application load balancers. |
8.16.0 |
| 2.35.0 | Enhancement (View pull request) Add the support for connection logs for AWS ELB dataset for Application Load Balancers. |
8.16.0 |
| 2.34.0 | Enhancement (View pull request) Add Lambda Event Source Mapping metrics and improve Lambda dashboard to display the new metrics. |
8.16.0 |
| 2.33.0 | Enhancement (View pull request) Add option to check linked accounts when using log group prefixes to derive matching log groups |
8.16.0 |
| 2.32.0 | Bug fix (View pull request) Implemented grok processor based parsing for ipv6 & ipv4 addresses in the AWS CloudFront logs. Enhancement (View pull request) Auto formatted various text descriptions and newlines across all data streams via elastic-package. |
8.16.0 |
| 2.31.4 | Bug fix (View pull request) Update documentation with required permissions for AWS Inspector. |
8.16.0 |
| 2.31.3 | Bug fix (View pull request) Removed the reducedTimeRange filter from the AWS Billing Total Estimated Charges lens to ensure value is displayed. |
8.16.0 |
| 2.31.2 | Bug fix (View pull request) Add the support for listeners with ALPN policy extension in ELB dataset for Network Load Balancers. |
8.16.0 |
| 2.31.1 | Bug fix (View pull request) Add cloud.provider, event.kind, and observer.vendor fields to _source as needed by CDR workflows. |
8.16.0 |
| 2.31.0 | Enhancement (View pull request) Improve support for Cloud Detection and Response (CDR) workflows in securityhub_findings data stream. |
8.16.0 |
| 2.30.3 | Enhancement (View pull request) Map aws.dimensions as object instead of flattened in CloudWatch metrics (backported from 2.37.0) |
8.15.2 |
| 2.30.2 | Bug fix (View pull request) Add the support for listeners with ALPN policy extension in ELB dataset for Network Load Balancers. |
8.15.2 |
| 2.30.1 | Bug fix (View pull request) Update the AWS dashboard panels. |
8.15.2 |
| 2.30.0 | Enhancement (View pull request) Support configuring the Owning Account |
8.15.2 |
| 2.29.0 | Enhancement (View pull request) Add mapping for the service.runtimeDetails fields in GuardDuty events. |
8.15.0 |
| 2.28.0 | Enhancement (View pull request) Add reference to AWS API requests and pricing information. |
8.15.0 |
| 2.27.0 | Enhancement (View pull request) Improve ingest pipeline error reporting. |
8.15.0 |
| 2.26.0 | Enhancement (View pull request) Add more data to related.entity field. |
8.15.0 |
| 2.26.0-preview01 | Enhancement (View pull request) Add related.entity field. |
— |
| 2.25.1 | Bug fix (View pull request) Add aws.metrics_names_fingerprint field and mark it as a dimension. |
8.14.0 |
| 2.25.0 | Enhancement (View pull request) Allow @custom pipeline access to event.original without setting preserve_original_event. |
8.14.0 |
| 2.24.3 | Bug fix (View pull request) Fix aws.metrics_names_fingerprint field. |
8.14.0 |
| 2.24.2 | Bug fix (View pull request) Add aws.metrics_names_fingerprint. |
8.14.0 |
| 2.24.1 | Bug fix (View pull request) Fixed and refactored AWS cloudfront log parsing. |
8.14.0 |
| 2.24.0 | Enhancement (View pull request) Add dot_expander processor into metrics ingest pipeline. |
8.14.0 |
| 2.23.0 | Enhancement (View pull request) Split the current AWS ELB dashboard into 3 separate dashboards, each focusing on a specific type of load balancer ELB, ALB, and NLB. |
8.14.0 |
| 2.22.1 | Bug fix (View pull request) Update max_number_of_messages parameter description |
8.14.0 |
| 2.22.0 | Enhancement (View pull request) Add global dataset filter for dashboards to improve performance. |
8.14.0 |
| 2.21.0 | Enhancement (View pull request) Fix route53 public logs grok pattern. |
8.14.0 |
| 2.20.0 | Enhancement (View pull request) Add S3 polling option to data streams use aws-s3 input |
8.14.0 |
| 2.19.0 | Enhancement (View pull request) Add a visualization panel to display the Inbound and Outbound traffic of Application load balancers. |
8.14.0 |
| 2.18.0 | Enhancement (View pull request) Add AWS Health integration. |
8.14.0 |
| 2.17.0 | Enhancement (View pull request) ECS version updated to 8.11.0. Update the kibana constraint to ^8.13.0. Modified the field definitions to remove ECS fields made redundant by the ecs@mappings component template. |
8.13.0 |
| 2.16.0 | Enhancement (View pull request) Add TargetResponseTime metric to ELB Application metrics. |
8.12.0 |
| 2.15.4 | Bug fix (View pull request) Fix AWS Network Firewall title and description. |
8.12.0 |
| 2.15.3 | Enhancement (View pull request) Add endpoint + region variables to all SQS based AWS integrations. |
8.12.0 |
| 2.15.2 | Bug fix (View pull request) Fix AWS Cloudtrail resources field processing. |
8.12.0 |
| 2.15.1 | Bug fix (View pull request) Don't index empty AWS Security Hub responses. |
8.12.0 |
| 2.15.0 | Enhancement (View pull request) Adds async event age and drops metrics, and implements sum aggregation for existing lambda metrics. |
8.12.0 |
| 2.14.2 | Bug fix (View pull request) Update aggregation function for AWS lambda invocation metric. |
8.12.0 |
| 2.14.1 | Enhancement (View pull request) Document billing data stream limitations. |
8.12.0 |
| 2.14.0 | Enhancement (View pull request) Add ability to set processors and leader election on AWS Billing. |
8.12.0 |
| 2.13.1 | Enhancement (View pull request) Update latency parameter description |
8.12.0 |
| 2.13.0 | Enhancement (View pull request) Add Amazon MSK integration |
8.12.0 |
| 2.12.2 | Bug fix (View pull request) Fix an issue were the "_id" field was being used to aggregate data in Severity Over Time dashboard. |
8.12.0 |
| 2.12.1 | Enhancement (View pull request) Add cloudsecurity_cdr sub category label. |
8.12.0 |
| 2.12.0 | Enhancement (View pull request) Enable 'secret' for the sensitive fields. |
8.12.0 |
| 2.11.3 | Bug fix (View pull request) Fix query range calculation for GuardDuty datastream. |
8.10.2 |
| 2.11.2 | Bug fix (View pull request) Remove hardcoded event.dataset field and use ecs instead. |
8.10.2 |
| 2.11.1 | Enhancement (View pull request) Improve wording on milliseconds. |
8.10.2 |
| 2.11.0 | Enhancement (View pull request) Convert Total Estimated Charges panel to new metric visualization. |
8.10.2 |
| 2.10.2 | Bug fix (View pull request) Fix dimensions fingerprint field |
8.10.2 |
| 2.10.1 | Bug fix (View pull request) Fix exclude_files pattern. |
8.10.2 |
| 2.10.0 | Enhancement (View pull request) Convert "AWS Redshift metrics overview" visualizations to new metric. |
8.10.2 |
| 2.9.1 | Bug fix (View pull request) Change SQS metrics statistic method, which includes changing ApproximateAgeOfOldestMessage from average to max, changing NumberOfMessagesDeleted, NumberOfEmptyReceives, NumberOfMessagesReceived and NumberOfMessagesSent from average to sum. |
8.9.0 |
| 2.9.0 | Enhancement (View pull request) Limit request tracer log count to five. |
8.9.0 |
| 2.8.6 | Bug fix (View pull request) Add missing fields from beats input |
8.9.0 |
| 2.8.5 | Enhancement (View pull request) Update donut charts with pie for better representation |
8.9.0 |
| 2.8.4 | Bug fix (View pull request) Remove unused aws..metrics..* and aws.s3.bucket.name |
8.9.0 |
| 2.8.3 | Bug fix (View pull request) Include documentation and mappings for subfields of dns.answers Bug fix (View pull request) Fix mapping for tags and dynamic metric fields |
8.9.0 |
| 2.8.2 | Bug fix (View pull request) Add null checks and ignore_missing checks to the rename processor |
8.9.0 |
| 2.8.1 | Bug fix (View pull request) Fix incorrect billing metrics displayed under AWS Billing overview dashboard. |
8.9.0 |
| 2.8.0 | Enhancement (View pull request) Allow configuration of TLD for guardduty, inspector, and security hub datastreams. |
8.9.0 |
| 2.7.0 | Enhancement (View pull request) Add tags.yml file so that integration's dashboards and saved searches are tagged with "Security Solution" and displayed in the Security Solution UI. Enhancement (View pull request) Upgrade package spec to 3.0.0. Bug fix (View pull request) Fix duplicated and invalid field definitions. Bug fix (View pull request) Add missing dashboard filters. |
8.9.0 |
| 2.6.1 | Bug fix (View pull request) Fix AWS API Gateway logs dashboard lens |
8.9.0 |
| 2.6.0 | Enhancement (View pull request) ECS version updated to 8.10.0. |
8.9.0 |
| 2.5.0 | Enhancement (View pull request) Update Cloudtrail datastream to support tlsDetails field |
8.9.0 |
| 2.4.1 | Bug fix (View pull request) Fix Security Hub Findings to abide by ECS allowed values. |
8.9.0 |
| 2.4.0 | Bug fix (View pull request) Add AWS API Gateway metrics dashboards for each API type and additional filters which ensure data consistency |
8.9.0 |
| 2.3.0 | Enhancement (View pull request) Change include_linked_accounts default to true |
8.9.0 |
| 2.2.1 | Bug fix (View pull request) Fix GuardDuty API call parameter. |
8.9.0 |
| 2.2.0 | Enhancement (View pull request) Add AWS API Gateway metrics dashboard Stage filter, control groups and clean up |
8.9.0 |
| 2.1.2 | Bug fix (View pull request) Fix AWS API Gateway metrics dashboard |
8.9.0 |
| 2.1.1 | Enhancement (View pull request) Improve AWS API Gateway dashboard |
8.9.0 |
| 2.1.0 | Enhancement (View pull request) Enable TSDB by default for EC2 metrics data stream. This improves storage usage and query performance. For more details, see https://www.elastic.co/guide/en/elasticsearch/reference/current/tsds.html. |
8.9.0 |
| 2.0.0 | Enhancement (View pull request) Remove deprecated option for "Cloudwatch via S3"from the AWS CloudWatch integration. If you are using it take note that logs WON'T BE ingested via this route anymore once you update. |
8.9.0 |
| 1.53.5 | Enhancement (View pull request) Set metric type in EC2 data stream fields. |
8.9.0 |
| 1.53.4 | Enhancement (View pull request) Add dimension fields to EC2 data stream. |
8.9.0 |
| 1.53.3 | Enhancement (View pull request) Add missing fields definition for ec2 |
8.9.0 |
| 1.53.2 | Bug fix (View pull request) Remove the remove processor since rename processor removes old field already. |
8.9.0 |
| 1.53.1 | Enhancement (View pull request) Disable TSDB on AWS Billing. |
8.9.0 |
| 1.53.0 | Enhancement (View pull request) Add AWS API Gateway custom acccess logging fields. |
8.9.0 |
| 1.52.1 | Enhancement (View pull request) Use default color for AWS dashboards metric charts. |
8.9.0 |
| 1.52.0 | Enhancement (View pull request) Enable TSDB by default for cloudwatch metrics data stream. This improves storage usage and query performance. For more details, see https://www.elastic.co/guide/en/elasticsearch/reference/current/tsds.html. |
8.9.0 |
| 1.51.3 | Bug fix (View pull request) Remove hardcoded event.dataset field and use ecs instead. |
8.8.1 |
| 1.51.2 | Enhancement (View pull request) Disable TSDB on AWS Billing. |
8.8.1 |
| 1.51.1 | Enhancement (View pull request) Use object metric type for the cloudwatch metrics |
8.8.1 |
| 1.51.0 | Enhancement (View pull request) Add standalone S3 option for vpcflow |
8.8.1 |
| 1.50.6 | Enhancement (View pull request) Add metric_type metadata to the cloudwatch data_stream |
8.8.1 |
| 1.50.5 | Enhancement (View pull request) Migrate AWS Security Hub dashboards to lens. |
8.8.1 |
| 1.50.4 | Enhancement (View pull request) Migrate AWS VPC dashboard visualizations to lens. |
8.8.1 |
| 1.50.3 | Enhancement (View pull request) Add EMR logs dashboard. |
8.8.1 |
| 1.50.2 | Enhancement (View pull request) Migrate AWS Billing dashboard visualizations to lens. |
8.8.1 |
| 1.50.1 | Enhancement (View pull request) Add AWS API Gateway logs dashboard. |
8.8.1 |
| 1.50.0 | Enhancement (View pull request) Add EMR logs data stream. |
8.8.1 |
| 1.49.0 | Enhancement (View pull request) Add API Gateway logs datastream |
8.8.1 |
| 1.48.0 | Enhancement (View pull request) Adding missing fields for the CloudTrail datastream - add option for standalone S3 bucket |
8.8.1 |
| 1.47.1 | Enhancement (View pull request) Migrate AWS Redshift dashboard input controls. |
8.8.1 |
| 1.47.0 | Enhancement (View pull request) Migrate AWS S3 Server Access Log Overview dashboard visualizations to lens. |
8.8.1 |
| 1.46.9 | Enhancement (View pull request) Migrate AWS Network Firewall dashboard input controls. |
8.8.1 |
| 1.46.8 | Enhancement (View pull request) Add dimensions metadata to the cloudwatch data_stream |
8.8.1 |
| 1.46.7 | Enhancement (View pull request) Enable time series data streams for the API Gateway and EMR data streams. This improves storage usage and query performance. For more details, see https://www.elastic.co/guide/en/elasticsearch/reference/current/tsds.html. |
8.8.1 |
| 1.46.6 | Enhancement (View pull request) Update metric type and set dimension fields for AWS EMR data stream. |
8.8.1 |
| 1.46.5 | Enhancement (View pull request) Fix metric type for API Gateway metric fields. |
8.8.1 |
| 1.46.4 | Enhancement (View pull request) Set dimensions fields for API Gateway data stream. |
— |
| 1.46.3 | Enhancement (View pull request) Add missing S3 fields for vpcflow |
8.8.1 |
| 1.46.2 | Enhancement (View pull request) Enable time series data streams for the S3 daily storage and S3 request datasets. This improves storage usage and query performance. For more details, see https://www.elastic.co/guide/en/elasticsearch/reference/current/tsds.html. |
8.8.1 |
| 1.46.1 | Enhancement (View pull request) Enable time series data streams for the Usage dataset. This improves storage usage and query performance. For more details, see https://www.elastic.co/guide/en/elasticsearch/reference/current/tsds.html. |
8.8.1 |
| 1.46.0 | Enhancement (View pull request) Enable time series data streams for the metrics datasets Billing, DynamoDB, EBS, ECS, ELB, Firewall, Kinesis, Lambda, NAT gateway, RDS, Redshift, S3 Storage Lens, SNS, SQS, Transit Gateway and VPN. This improves storage usage and query performance. For more details, see https://www.elastic.co/guide/en/elasticsearch/reference/current/tsds.html. |
8.8.1 |
| 1.45.9 | Enhancement (View pull request) Add new fingerprint dimension to AWS Billing. |
8.8.1 |
| 1.45.8 | Enhancement (View pull request) Add metric_type metadata to s3_daily_storage and s3_request data streams. |
8.8.1 |
| 1.45.7 | Enhancement (View pull request) Add dimension fields metadata to s3_request and s3_data_storage data streams to support TSDB |
8.8.1 |
| 1.45.6 | Enhancement (View pull request) Add metric type to S3 Storage Lens. |
8.8.1 |
| 1.45.4 | Enhancement (View pull request) Set dimension fields for S3 Storage Lens. |
8.8.1 |
| 1.45.3 | Bug fix (View pull request) Remove aws.dimensions.* from package-fields.yml |
8.8.1 |
| 1.45.2 | Enhancement (View pull request) Add AWS EMR metrics dashboard. |
8.8.1 |
| 1.45.1 | Enhancement (View pull request) Add AWS API Gateway dashboard. |
8.8.1 |
| 1.45.0 | Enhancement (View pull request) Add AWS EMR metrics data stream. |
8.8.1 |
| 1.44.4 | Enhancement (View pull request) Migrate AWS Metric Overview dashboard visualizations to lens. |
8.8.1 |
| 1.44.3 | Enhancement (View pull request) Migrate AWS ELB Access Log dashboard visualizations to lens. |
8.8.1 |
| 1.44.2 | Bug fix (View pull request) Fix image link in readme |
8.8.1 |
| 1.44.1 | Enhancement (View pull request) Migrate AWS TransitGateway metrics dashboard to lenses. |
8.8.1 |
| 1.44.0 | Enhancement (View pull request) Add permissions to reroute events to logs-- for cloudwatch_logs and ec2_logs datastream. |
8.8.1 |
| 1.43.2 | Enhancement (View pull request) Add documentation for latency parameter |
8.8.1 |
| 1.43.1 | Enhancement (View pull request) Add tags_filter and include_linked_accounts config parameter in missing metric data streams. |
8.8.1 |
| 1.43.0 | Enhancement (View pull request) Add include_linked_accounts config parameter for metrics data streams. |
8.8.1 |
| 1.42.0 | Enhancement (View pull request) Add field agent.id to be set as dimension for TSDB migration. |
8.7.1 |
| 1.41.0 | Enhancement (View pull request) Migrate AWS NATGateway metrics dashboard visualizations to lenses. |
8.7.1 |
| 1.40.9 | Enhancement (View pull request) Migrate AWS ELB metrics dashboard visualizations to lenses. |
8.7.1 |
| 1.40.8 | Enhancement (View pull request) Migrate EC2 metrics dashboard visualizations to lenses. |
8.7.1 |
| 1.40.7 | Enhancement (View pull request) Add AWS Firewall metrics dashboard input control groups. |
8.7.1 |
| 1.40.6 | Enhancement (View pull request) Migrate AWS S3 Storage Lens dashboard visualizations to lens. |
8.7.1 |
| 1.40.5 | Enhancement (View pull request) Migrate Usage Overview dashboard to lenses. |
8.7.1 |
| 1.40.4 | Enhancement (View pull request) Migrate AWS CloudTrail dashboard visualizations to lenses. |
8.7.1 |
| 1.40.3 | Enhancement (View pull request) Add fields metric type to usage, dynamoDB and ELB data streams. |
8.7.1 |
| 1.40.2 | Enhancement (View pull request) Replace aws.rds.db_instance.identifier with aws.dimensions.DBInstanceIdentifier in RDS dashboard. |
8.7.1 |
| 1.40.1 | Enhancement (View pull request) Add link to main AWS requirements in all integrations page. |
8.7.1 |
| 1.40.0 | Enhancement (View pull request) Add metric type to SNS, SQS and Billing data streams. |
8.7.1 |
| 1.39.0 | Enhancement (View pull request) Add AWS API Gateway data stream. |
8.7.1 |
| 1.38.4 | Enhancement (View pull request) Add dimension fields to billing, sns and sqs data streams. |
8.7.1 |
| 1.38.3 | Enhancement (View pull request) Add dimension fields to firewall, transit gateway and vpn data streams. |
8.7.1 |
| 1.38.2 | Enhancement (View pull request) Add metric type to vpn, firewall and transit gateway data streams. |
8.7.1 |
| 1.38.1 | Enhancement (View pull request) Add metric type to RDS data stream. |
8.7.1 |
| 1.38.0 | Enhancement (View pull request) Add dimensions to RDS data stream. |
8.7.1 |
| 1.37.3 | Bug fix (View pull request) Fix incorrect fields on multiple visualizations. |
8.7.1 |
| 1.37.2 | Enhancement (View pull request) Migrate AWS RDS metrics dashboard to lenses. |
8.7.1 |
| 1.37.1 | Enhancement (View pull request) Migrate AWS SNS dashboard visualizations to lenses. |
8.7.1 |
| 1.37.0 | Enhancement (View pull request) Migrate AWS SQS metrics dashboard visualizations to lenses. |
8.7.1 |
| 1.36.9 | Enhancement (View pull request) Migrate AWS VPN metrics dashboard to lenses. |
8.7.1 |
| 1.36.8 | Enhancement (View pull request) Add dimension fields to usage, dynamoDB and ELB data streams. |
8.7.1 |
| 1.36.7 | Enhancement (View pull request) Add dimension fields to Lambda data stream for TSDB support. |
8.7.1 |
| 1.36.6 | Enhancement (View pull request) Add metric type to natgateway data stream fields. |
8.7.1 |
| 1.36.5 | Enhancement (View pull request) Add metric type to EBS fields. |
8.7.1 |
| 1.36.4 | Enhancement (View pull request) Add support for TSDB on kinesis data stream (metric type). |
8.7.1 |
| 1.36.3 | Enhancement (View pull request) Add dimensions to Redshift data stream. |
8.7.1 |
| 1.36.2 | Enhancement (View pull request) Add metric type mapping to Redshift data stream. |
8.7.1 |
| 1.36.1 | Enhancement (View pull request) Add dimension fields to natgateway data stream. |
8.7.1 |
| 1.36.0 | Enhancement (View pull request) Add metric type to Lambda fields. |
8.7.1 |
| 1.35.1 | Bug fix (View pull request) Fix typo in field name causing erroneous timestamp detection on the s3access data stream. |
8.7.1 |
| 1.35.0 | Enhancement (View pull request) Add a new flag to enable request tracing on httpjson based input |
8.7.1 |
| 1.34.5 | Enhancement (View pull request) Migrate AWS Lambda metrics dashboard visualizations to lenses. |
8.6.0 |
| 1.34.4 | Enhancement (View pull request) Migrate AWS DynamoDB metrics dashboard visualizations to lenses. |
8.6.0 |
| 1.34.3 | Enhancement (View pull request) Add field metric type to ECS data stream. |
8.6.0 |
| 1.34.2 | Enhancement (View pull request) Add dimension fields to Kinesis datastream. |
8.6.0 |
| 1.34.1 | Enhancement (View pull request) Add dimension fields to ECS datastream for TSDB support. |
8.6.0 |
| 1.34.0 | Enhancement (View pull request) Add dimensions to EBS data stream. |
8.6.0 |
| 1.33.3 | Enhancement (View pull request) Add number_of_workers and latency to all CloudWatch Logs based integrations. |
8.6.0 |
| 1.33.2 | Bug fix (View pull request) Add missing permissions in the AWS Billing integration documentation. |
8.6.0 |
| 1.33.1 | Bug fix (View pull request) Add missing permissions in the AWS CloudWatch Logs integration documentation. |
8.6.0 |
| 1.33.0 | Enhancement (View pull request) Add latency configuration option on the CloudWatch Logs integration. |
8.6.0 |
| 1.32.2 | Bug fix (View pull request) Fix a minor documentation format issue. |
8.6.0 |
| 1.32.1 | Enhancement (View pull request) Added categories and/or subcategories. |
8.6.0 |
| 1.32.0 | Enhancement (View pull request) Migrate AWS EBS dashboard visualizations to lenses. |
8.6.0 |
| 1.31.0 | Enhancement (View pull request) Add a data stream for Amazon GuardDuty. |
8.6.0 |
| 1.30.0 | Enhancement (View pull request) Add dashboards data streams filters. |
8.6.0 |
| 1.29.1 | Bug fix (View pull request) Drop comments from CloudFront loglines |
8.6.0 |
| 1.29.0 | Enhancement (View pull request) Add data_granularity parameter and rename period title to Collection Period. |
8.6.0 |
| 1.28.3 | Bug fix (View pull request) Remove quotes from VPC flow log message field and move dot_expander processor to top |
8.4.0 |
| 1.28.2 | Bug fix (View pull request) Add dot_expander processor to expand all fields with dot into object fields Bug fix (View pull request) Support VPC flow log with message field |
8.4.0 |
| 1.28.1 | Enhancement (View pull request) Adjust kinesis integration to kinesis data stream |
8.4.0 |
| 1.28.0 | Enhancement (View pull request) Enhance S3 integration dashboard |
8.4.0 |
| 1.27.3 | Bug fix (View pull request) Support multiple forwarded IPs in cloudfront integration |
8.4.0 |
| 1.27.2 | Enhancement (View pull request) Update the pagination termination condition. |
8.4.0 |
| 1.27.1 | Enhancement (View pull request) Added a Summary Dashboard for AWS Security Hub. |
8.4.0 |
| 1.27.0 | Enhancement (View pull request) Add Inspector data stream. |
8.4.0 |
| 1.25.3 | Bug fix (View pull request) Remove duplicate fields from agent.yml and use ecs.yml for ECS fields |
8.3.0 |
| 1.25.2 | Bug fix (View pull request) Update ec2 fields.yml doc |
8.3.0 |
| 1.25.1 | Bug fix (View pull request) Remove duplicate 'content_type' config that causes errors while configurating the integration. |
8.3.0 |
| 1.25.0 | Enhancement (View pull request) Force content type where json content is expected |
8.3.0 |
| 1.24.6 | Bug fix (View pull request) Enhance Kinesis integration dashboard |
8.3.0 |
| 1.24.5 | Bug fix (View pull request) Allow adding multiple processors in cloudfront logs. |
8.3.0 |
| 1.24.4 | Bug fix (View pull request) Do not rely on dynamodb lightweight module metricset. |
8.3.0 |
| 1.24.3 | Bug fix (View pull request) Fix adding processors in cloudfront logs. |
8.3.0 |
| 1.24.2 | Bug fix (View pull request) Fix billing datastream agent template. |
8.3.0 |
| 1.24.1 | Bug fix (View pull request) Fix aws.cloudtrail.request_id parsing |
8.3.0 |
| 1.24.0 | Bug fix (View pull request) Expose Default Region setting to UI |
8.3.0 |
| 1.23.4 | Bug fix (View pull request) Set default endpoint to empty string |
8.3.0 |
| 1.23.3 | Bug fix (View pull request) Fix Billing Dashboard |
8.3.0 |
| 1.23.2 | Bug fix (View pull request) Fix EC2 dashboard |
8.3.0 |
| 1.23.1 | Enhancement (View pull request) Update all AWS documentation. |
8.1.0 |
| 1.23.0 | Bug fix (View pull request) Fix file.path field in cloudtrail data stream to use json.digestS3Object |
8.1.0 |
| 1.22.0 | Enhancement (View pull request) Update cloud.region parsing |
8.1.0 |
| 1.21.0 | Enhancement (View pull request) Add Security Hub Findings and Insights data streams |
8.1.0 |
| 1.20.0 | Enhancement (View pull request) Improve dashboards by removing individual visualizations from library |
8.1.0 |
| 1.19.5 | Enhancement (View pull request) Move ebs metrics config from beats to integrations |
8.0.0 7.15.0 |
| 1.19.4 | Bug fix (View pull request) Fix proxy URL documentation rendering. |
8.0.0 7.15.0 |
| 1.19.3 | Bug fix (View pull request) Update sample_event.json in kinesis data stream |
8.0.0 7.15.0 |
| 1.19.2 | Enhancement (View pull request) Move NATGateway metrics config from beats to integrations |
8.0.0 7.15.0 |
| 1.19.1 | Enhancement (View pull request) Move Transit Gateway metrics config from beats to integrations |
8.0.0 7.15.0 |
| 1.19.0 | Enhancement (View pull request) Add Kinesis metrics datastream |
8.0.0 7.15.0 |
| 1.18.2 | Enhancement (View pull request) Move s3_request metrics config from beats to integrations Enhancement (View pull request) Move s3_daily_storage metrics config from beats to integrations Enhancement (View pull request) Move SQS metrics config from beats to integrations Enhancement (View pull request) Move SNS metrics config from beats to integrations Enhancement (View pull request) Move lambda metrics config from beats to integrations |
8.0.0 7.15.0 |
| 1.18.1 | Enhancement (View pull request) Release AWS billing integration as GA |
8.0.0 7.15.0 |
| 1.18.0 | Enhancement (View pull request) Add ECS metricset Bug fix (View pull request) Fix incorrect fields on multiple visualizations |
8.0.0 7.15.0 |
| 1.17.5 | Enhancement (View pull request) Release Amazon Redshift integration as GA |
8.0.0 7.15.0 |
| 1.17.4 | Bug fix (View pull request) Fix data_stream.dataset indentation on cloudwatch_logs integration |
8.0.0 7.15.0 |
| 1.17.3 | Bug fix (View pull request) Add missing endpoint config to metrics datasets. Enhancement (View pull request) Move usage metrics config from beats to integrations Enhancement (View pull request) Move dynamodb metrics config from beats to integrations |
8.0.0 7.15.0 |
| 1.17.2 | Bug fix (View pull request) Improve support for event.original field from upstream forwarders. |
8.0.0 7.15.0 |
| 1.17.1 | Bug fix (View pull request) Fix misspelling of Log Stream Prefix variable in manifest for aws-cloudwatch input |
8.0.0 7.15.0 |
| 1.17.0 | Enhancement (View pull request) Added Redshift integration |
8.0.0 7.15.0 |
| 1.16.6 | Enhancement (View pull request) Update documentation with additional context for new users. |
8.0.0 7.15.0 |
| 1.16.5 | Enhancement (View pull request) Move ELB metrics config from beats to integrations |
— |
| 1.16.4 | Bug fix (View pull request) Fix ELB dataset to parse URLs with spaces Enhancement (View pull request) Upgrade ECS to 8.2.0 |
8.0.0 7.15.0 |
| 1.16.3 | Enhancement (View pull request) Move RDS metrics config from beats to integrations |
— |
| 1.16.2 | Enhancement (View pull request) Move EC2 metrics config from beats to integrations |
— |
| 1.16.1 | Bug fix (View pull request) Fix invalid values for ECS fields in vpcflow |
— |
| 1.16.0 | Enhancement (View pull request) Move VPN configuration file into integrations and add tag collection |
8.0.0 7.15.0 |
| 1.15.0 | Enhancement (View pull request) Deprecate s3 input in cloudwatch integration Enhancement (View pull request) Improve description for cloudwatch integration |
— |
| 1.14.8 | Bug fix (View pull request) Fix http.response.status_code to accept 000 |
8.0.0 7.15.0 |
| 1.14.7 | Bug fix (View pull request) Fix aws.dimensions.* for rds data stream Bug fix (View pull request) Fix aws.dimensions.* for sns data stream Bug fix (View pull request) Add aws.dimensions.* for dynamodb data stream |
8.0.0 7.15.0 |
| 1.14.6 | Enhancement (View pull request) Improve s3 integration tile title and description |
— |
| 1.14.5 | Bug fix (View pull request) Fix duplicate titles for integrations |
8.0.0 7.15.0 |
| 1.14.4 | Bug fix (View pull request) Fix cloudfront integration grok pattern |
— |
| 1.14.3 | Enhancement (View pull request) Add new pattern to VPC Flow logs including all 29 v5 fields |
— |
| 1.14.2 | Bug fix (View pull request) Fix billing dashboard. |
— |
| 1.14.1 | Enhancement (View pull request) Add documentation for multi-fields |
— |
| 1.14.0 | Enhancement (View pull request) Add configuration for max_number_of_messages to the aws.firewall_logs S3 input. |
8.0.0 7.15.0 |
| 1.13.1 | Bug fix (View pull request) Fix metricbeat- reference in dashboard |
8.0.0 7.15.0 |
| 1.13.0 | Enhancement (View pull request) Compress dashboard screenshots. |
8.0.0 7.15.0 |
| 1.12.1 | Bug fix (View pull request) Fix field mapping conflicts in the elb_logs data stream relating to ECS fields ( trace.id, source.port, and a few others). |
8.0.0 7.15.0 |
| 1.12.0 | Enhancement (View pull request) Add CloudFront Logs Datastream |
— |
| 1.11.4 | Bug fix (View pull request) Add Ingest Pipeline script to map IANA Protocol Numbers |
— |
| 1.11.3 | Bug fix (View pull request) Changing missing ecs versions to 8.0.0 |
— |
| 1.11.2 | Bug fix (View pull request) Add data_stream.dataset option for custom aws-cloudwatch log input |
— |
| 1.11.1 | Bug fix (View pull request) Update permission list |
— |
| 1.11.0 | Enhancement (View pull request) Update to ECS 8.0 |
8.0.0 7.15.0 |
| 1.10.2 | Enhancement (View pull request) Change cloudwatch metrics and logs default to false |
8.0.0 7.15.0 |
| 1.10.1 | Enhancement (View pull request) Add description of supported vpcflow formats |
— |
| 1.10.0 | Enhancement (View pull request) Add cloudwatch input into AWS package for log collection |
— |
| 1.9.0 | Enhancement (View pull request) Add Route 53 Resolver Logs Datastream |
8.0.0 7.15.0 |
| 1.8.0 | Enhancement (View pull request) Add Route 53 Public Zone Logs Datastream |
— |
| 1.7.1 | Bug fix (View pull request) Regenerate test files using the new GeoIP database |
— |
| 1.7.0 | Enhancement (View pull request) Add integration for AWS Network Firewall |
— |
| 1.6.2 | Bug fix (View pull request) Change test public IPs to the supported subset |
— |
| 1.6.1 | Enhancement (View pull request) Fix the value of event.created in CloudTrail data stream. |
8.0.0 7.15.0 |
| 1.6.0 | Enhancement (View pull request) Add max_number_of_messages config option to AWS S3 input config. |
— |
| 1.5.1 | Enhancement (View pull request) Add missing sample events |
8.0.0 7.15.0 |
| 1.5.0 | Enhancement (View pull request) Support Kibana 8.0 |
8.0.0 7.15.0 |
| 1.4.1 | Enhancement (View pull request) Add Overview dashboard for AWS S3 Storage Lens |
7.15.0 |
| 1.4.0 | Enhancement (View pull request) Add integration for AWS S3 Storage Lens |
— |
| 1.3.2 | Enhancement (View pull request) Uniform with guidelines |
— |
| 1.3.1 | Enhancement (View pull request) Add config parameter descriptions |
— |
| 1.3.0 | Enhancement (View pull request) Add WAF datastream |
— |
| 1.2.2 | Bug fix (View pull request) Prevent pipeline script error |
— |
| 1.2.1 | Bug fix (View pull request) Fix logic that checks for the 'forwarded' tag |
— |
| 1.2.0 | Enhancement (View pull request) Update to ECS 1.12.0 |
— |
| 1.1.0 | Enhancement (View pull request) vpcflow sync with filebeat fileset |
7.14.0 |
| 1.0.0 | Enhancement (View pull request) Release AWS as GA |
7.14.0 |
| 0.10.7 | Enhancement (View pull request) Add proxy config |
7.14.0 |
| 0.10.6 | Bug fix (View pull request) Fix aws.billing.EstimatedCharges field name |
— |
| 0.10.5 | Bug fix (View pull request) Add event.created field |
— |
| 0.10.4 | Enhancement (View pull request) Improve RDS dashboard |
7.14.0 |
| 0.10.3 | Enhancement (View pull request) Convert to generated ECS fields |
— |
| 0.10.2 | Enhancement (View pull request) update to ECS 1.11.0 |
— |
| 0.10.1 | Enhancement (View pull request) Escape special characters in docs |
— |
| 0.10.0 | Enhancement (View pull request) Update integration description |
— |
| 0.9.3 | Bug fix (View pull request) Fix categories for each policy template |
— |
| 0.9.2 | Enhancement (View pull request) Add linked account information into billing metricset |
— |
| 0.9.1 | Bug fix (View pull request) Fix aws.s3access pipeline when remote IP is a - |
— |
| 0.9.0 | Enhancement (View pull request) Change default credential options to access keys |
— |
| 0.8.0 | Enhancement (View pull request) Set "event.module" and "event.dataset" |
7.14.0 |
| 0.7.0 | Enhancement (View pull request) Introduce granularity using input_groups |
— |
| 0.6.4 | Enhancement (View pull request) Add support for Splunk authorization tokens |
— |
| 0.6.3 | Bug fix (View pull request) Fix bug in Third Party ingest pipeline |
— |
| 0.6.2 | Bug fix (View pull request) Removed incorrect http.request.referrer field from elb logs |
— |
| 0.6.1 | Enhancement (View pull request) Add support for CloudTrail Digest & Insight logs |
7.13.0 |
| 0.6.0 | Enhancement (View pull request) Update ECS version, add event.original and preparing for package GA |
— |
| 0.5.6 | Bug fix (View pull request) Fix stack compatability |
7.13.0 |
| 0.5.5 | Enhancement (View pull request) Allow role_arn work with access keys for AWS |
— |
| 0.5.4 | Enhancement (View pull request) Rename s3 input to aws-s3. |
— |
| 0.5.3 | Enhancement (View pull request) Add missing "geo" fields |
— |
| 0.5.2 | Enhancement (View pull request) update to ECS 1.9.0 |
— |
| 0.5.1 | Bug fix (View pull request) Ignore missing "json" field in ingest pipeline |
— |
| 0.5.0 | Enhancement (View pull request) Moving edge processors to ingest pipeline |
7.12.0 |
| 0.4.2 | Enhancement (View pull request) Updating package owner |
— |
| 0.4.1 | Bug fix (View pull request) Correct sample event file. |
— |
| 0.4.0 | Enhancement (View pull request) Add changes to use ECS 1.8 fields. |
— |
| 0.0.3 | Enhancement (View pull request) initial release |
— |