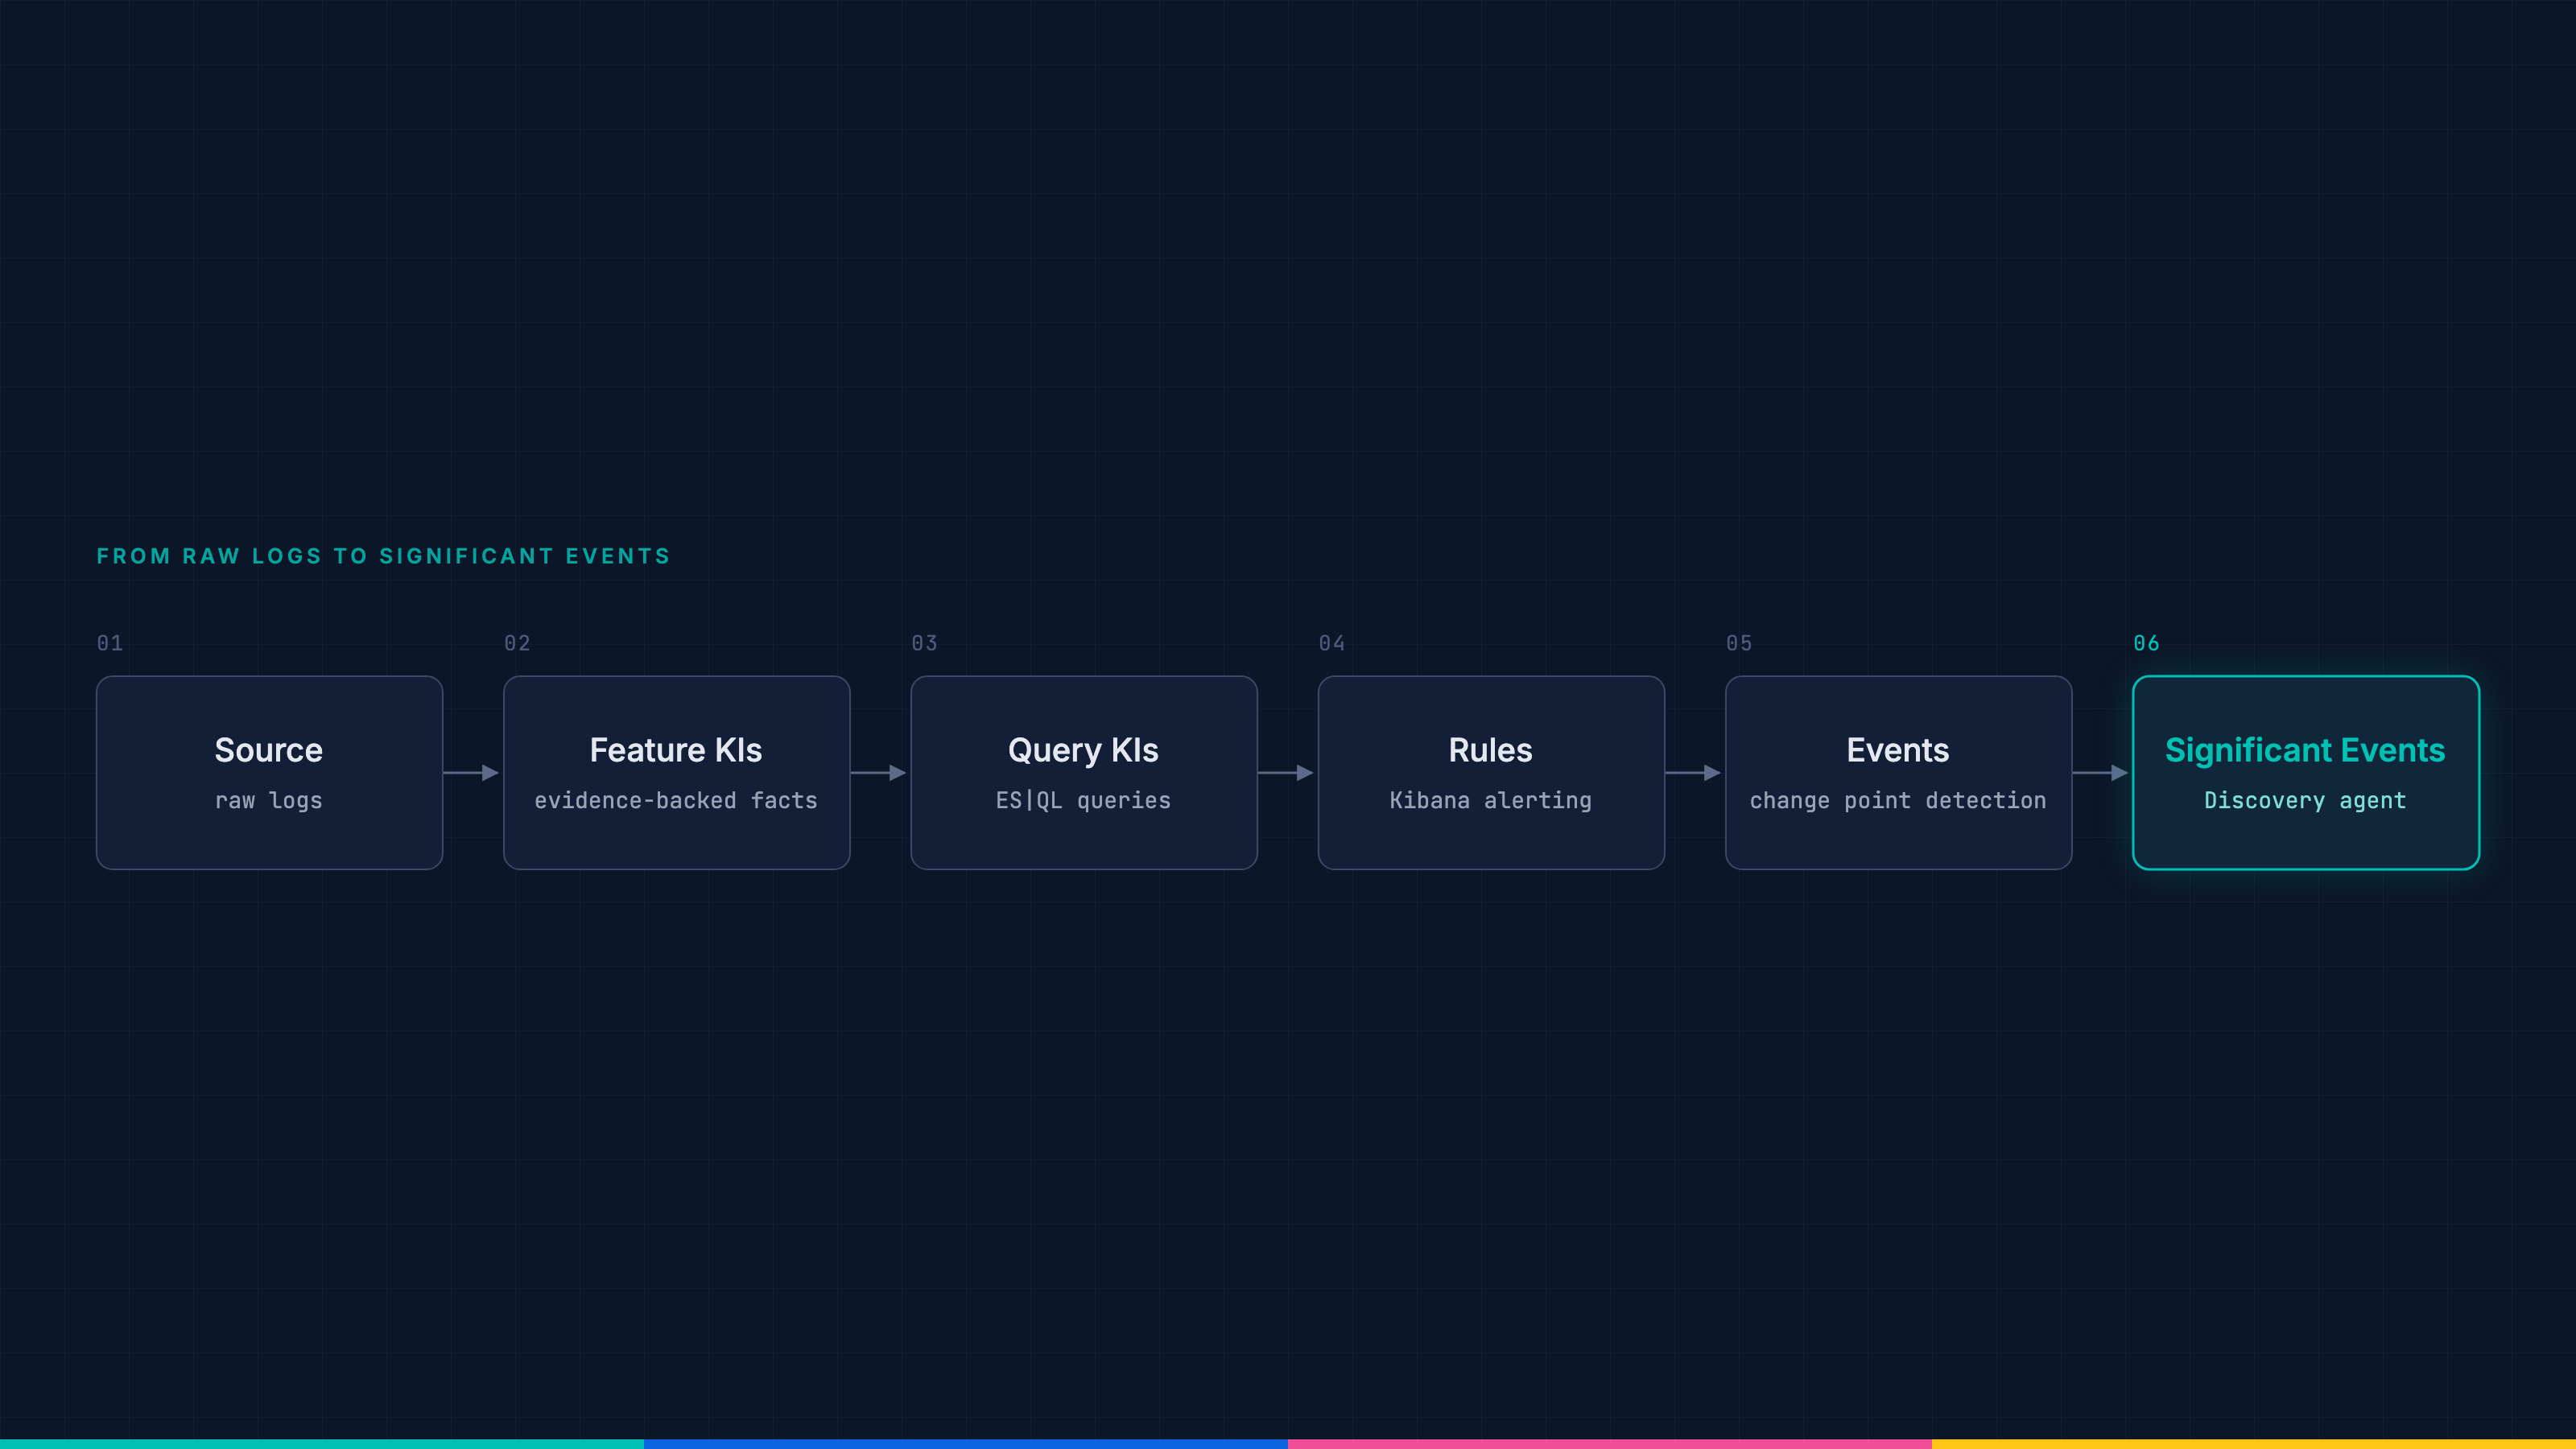
Two rules, one outage, one alert: How change point detection cuts alert noise
The discovery agent re-runs each firing rule’s own ES|QL query against the logs unchanged, so the alert names the unreachable service with the query that proves it.
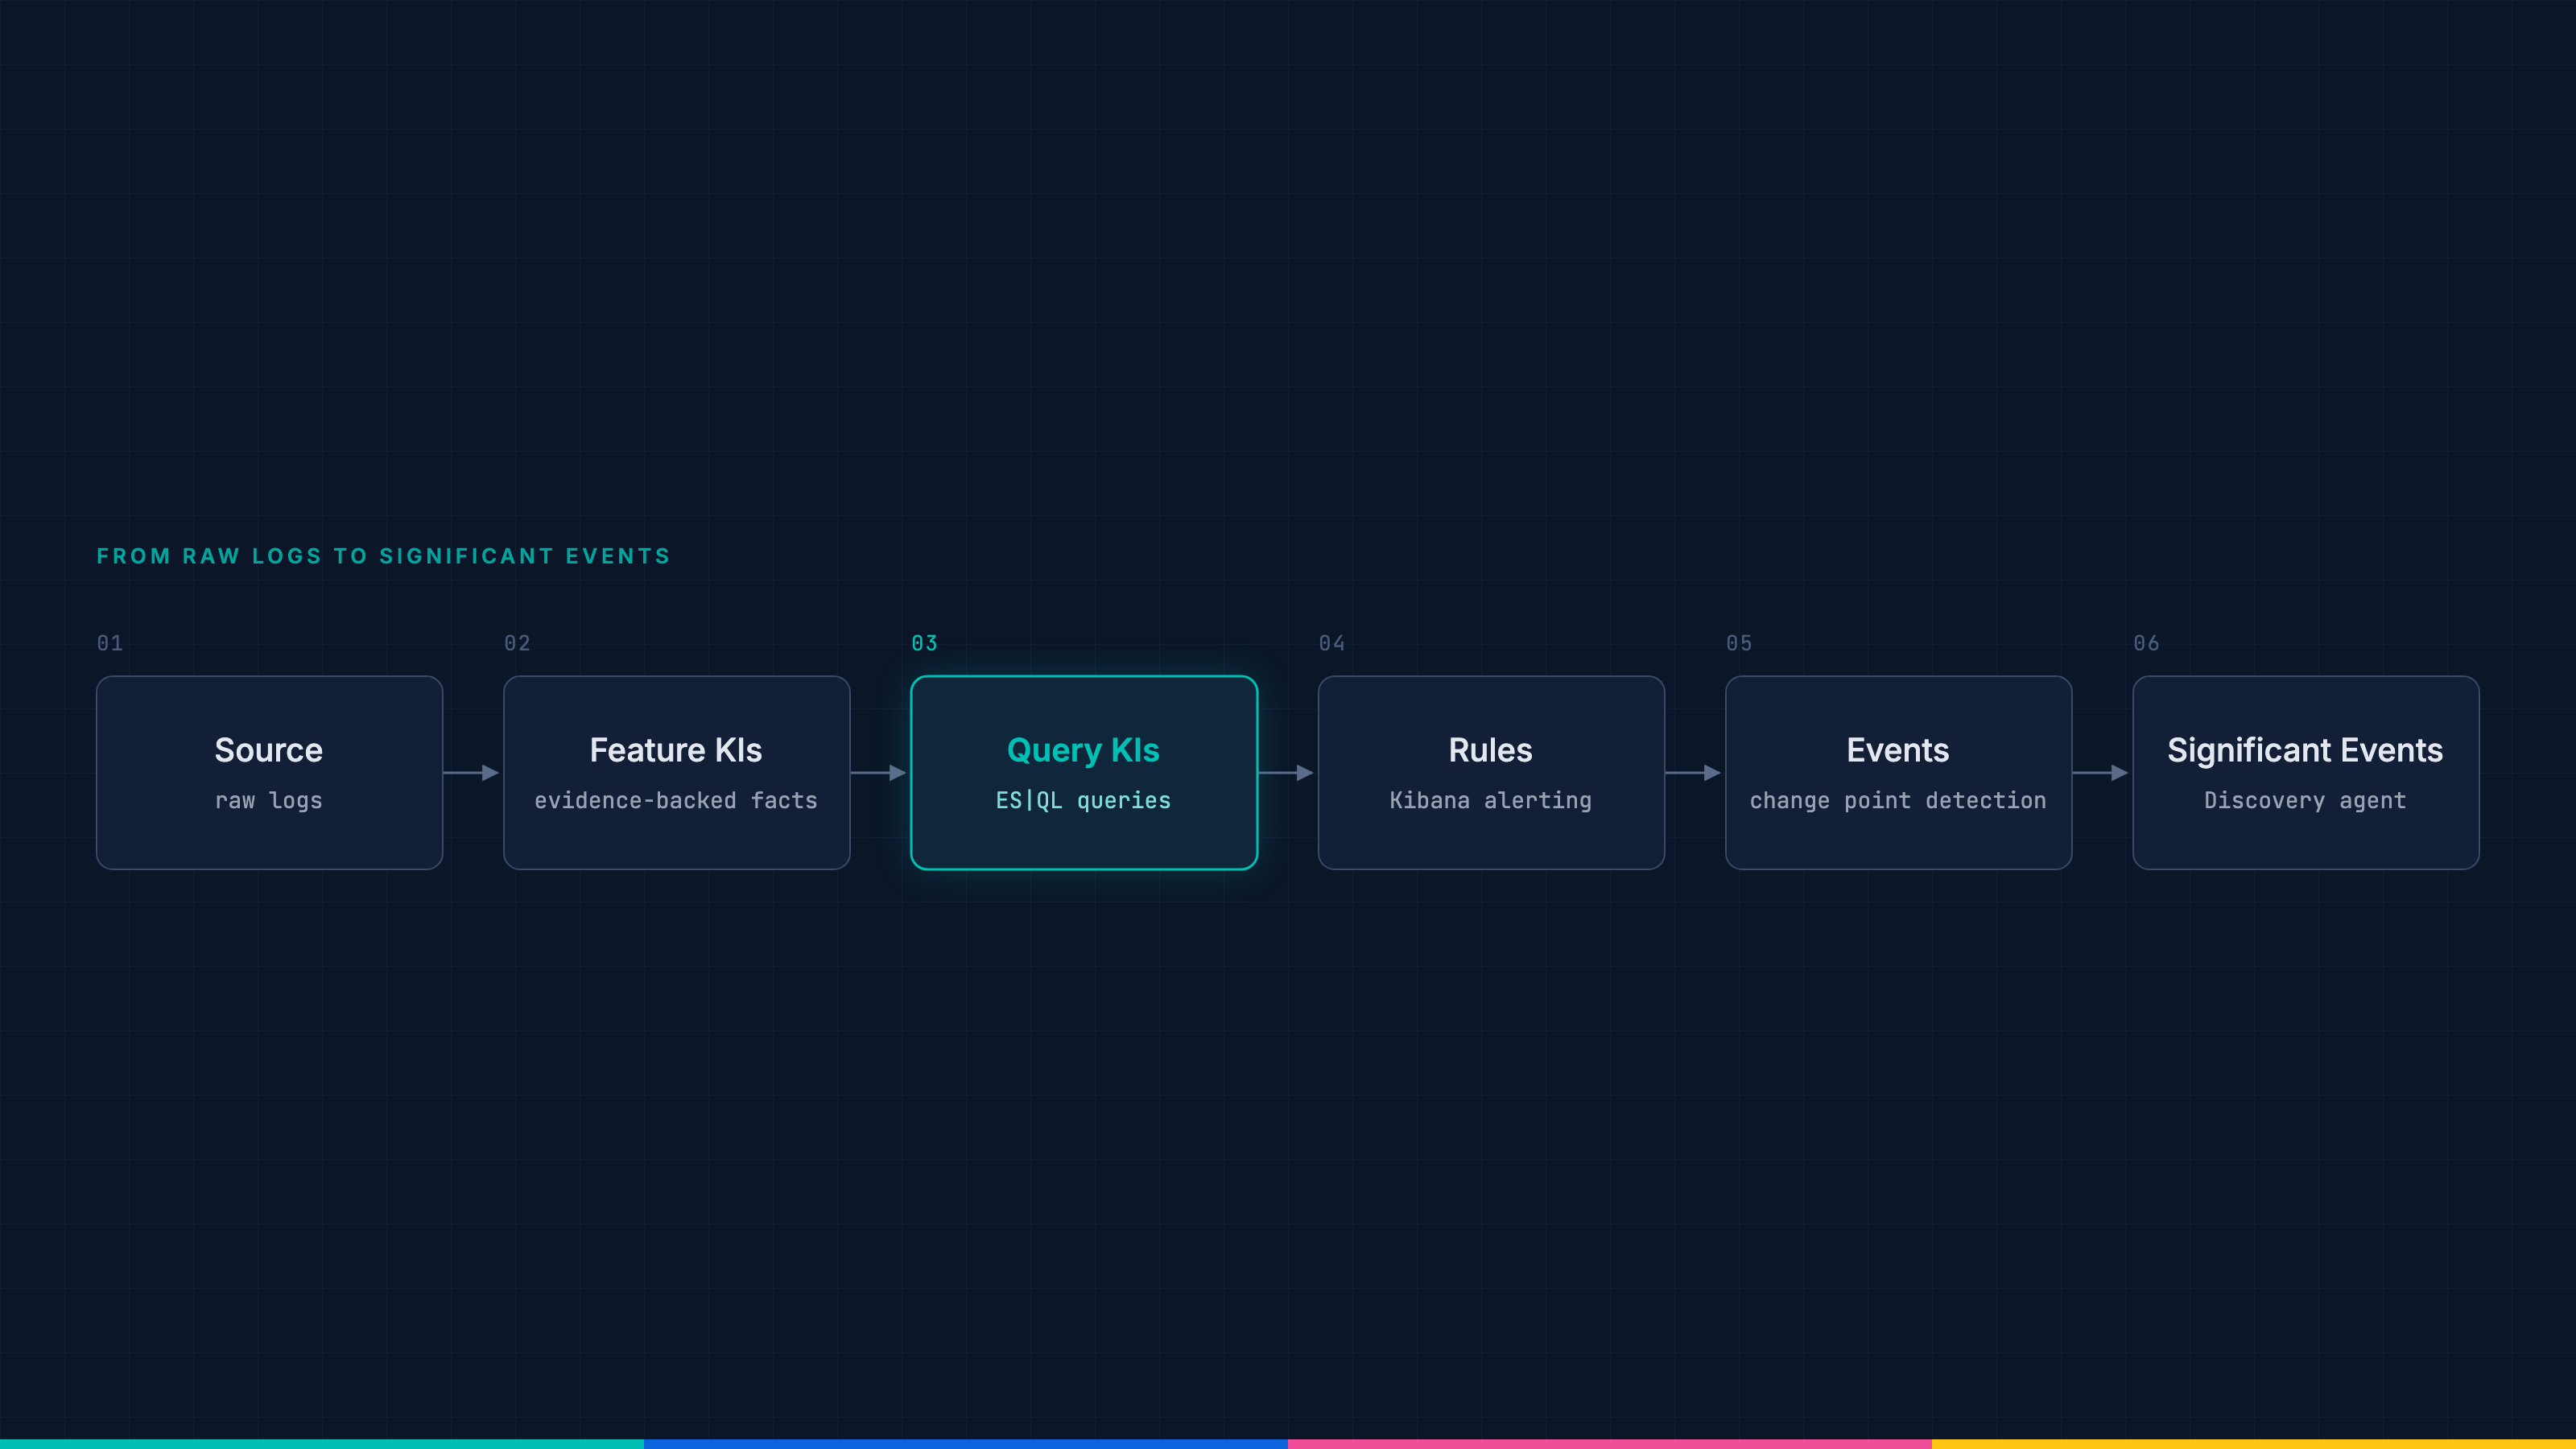
Your logs already wrote the alert: Generating ES|QL detection queries in Elasticsearch
On the OpenTelemetry demo, the top generated ES|QL detection query matches 0 documents while the shop is healthy and 676 during a payment outage.
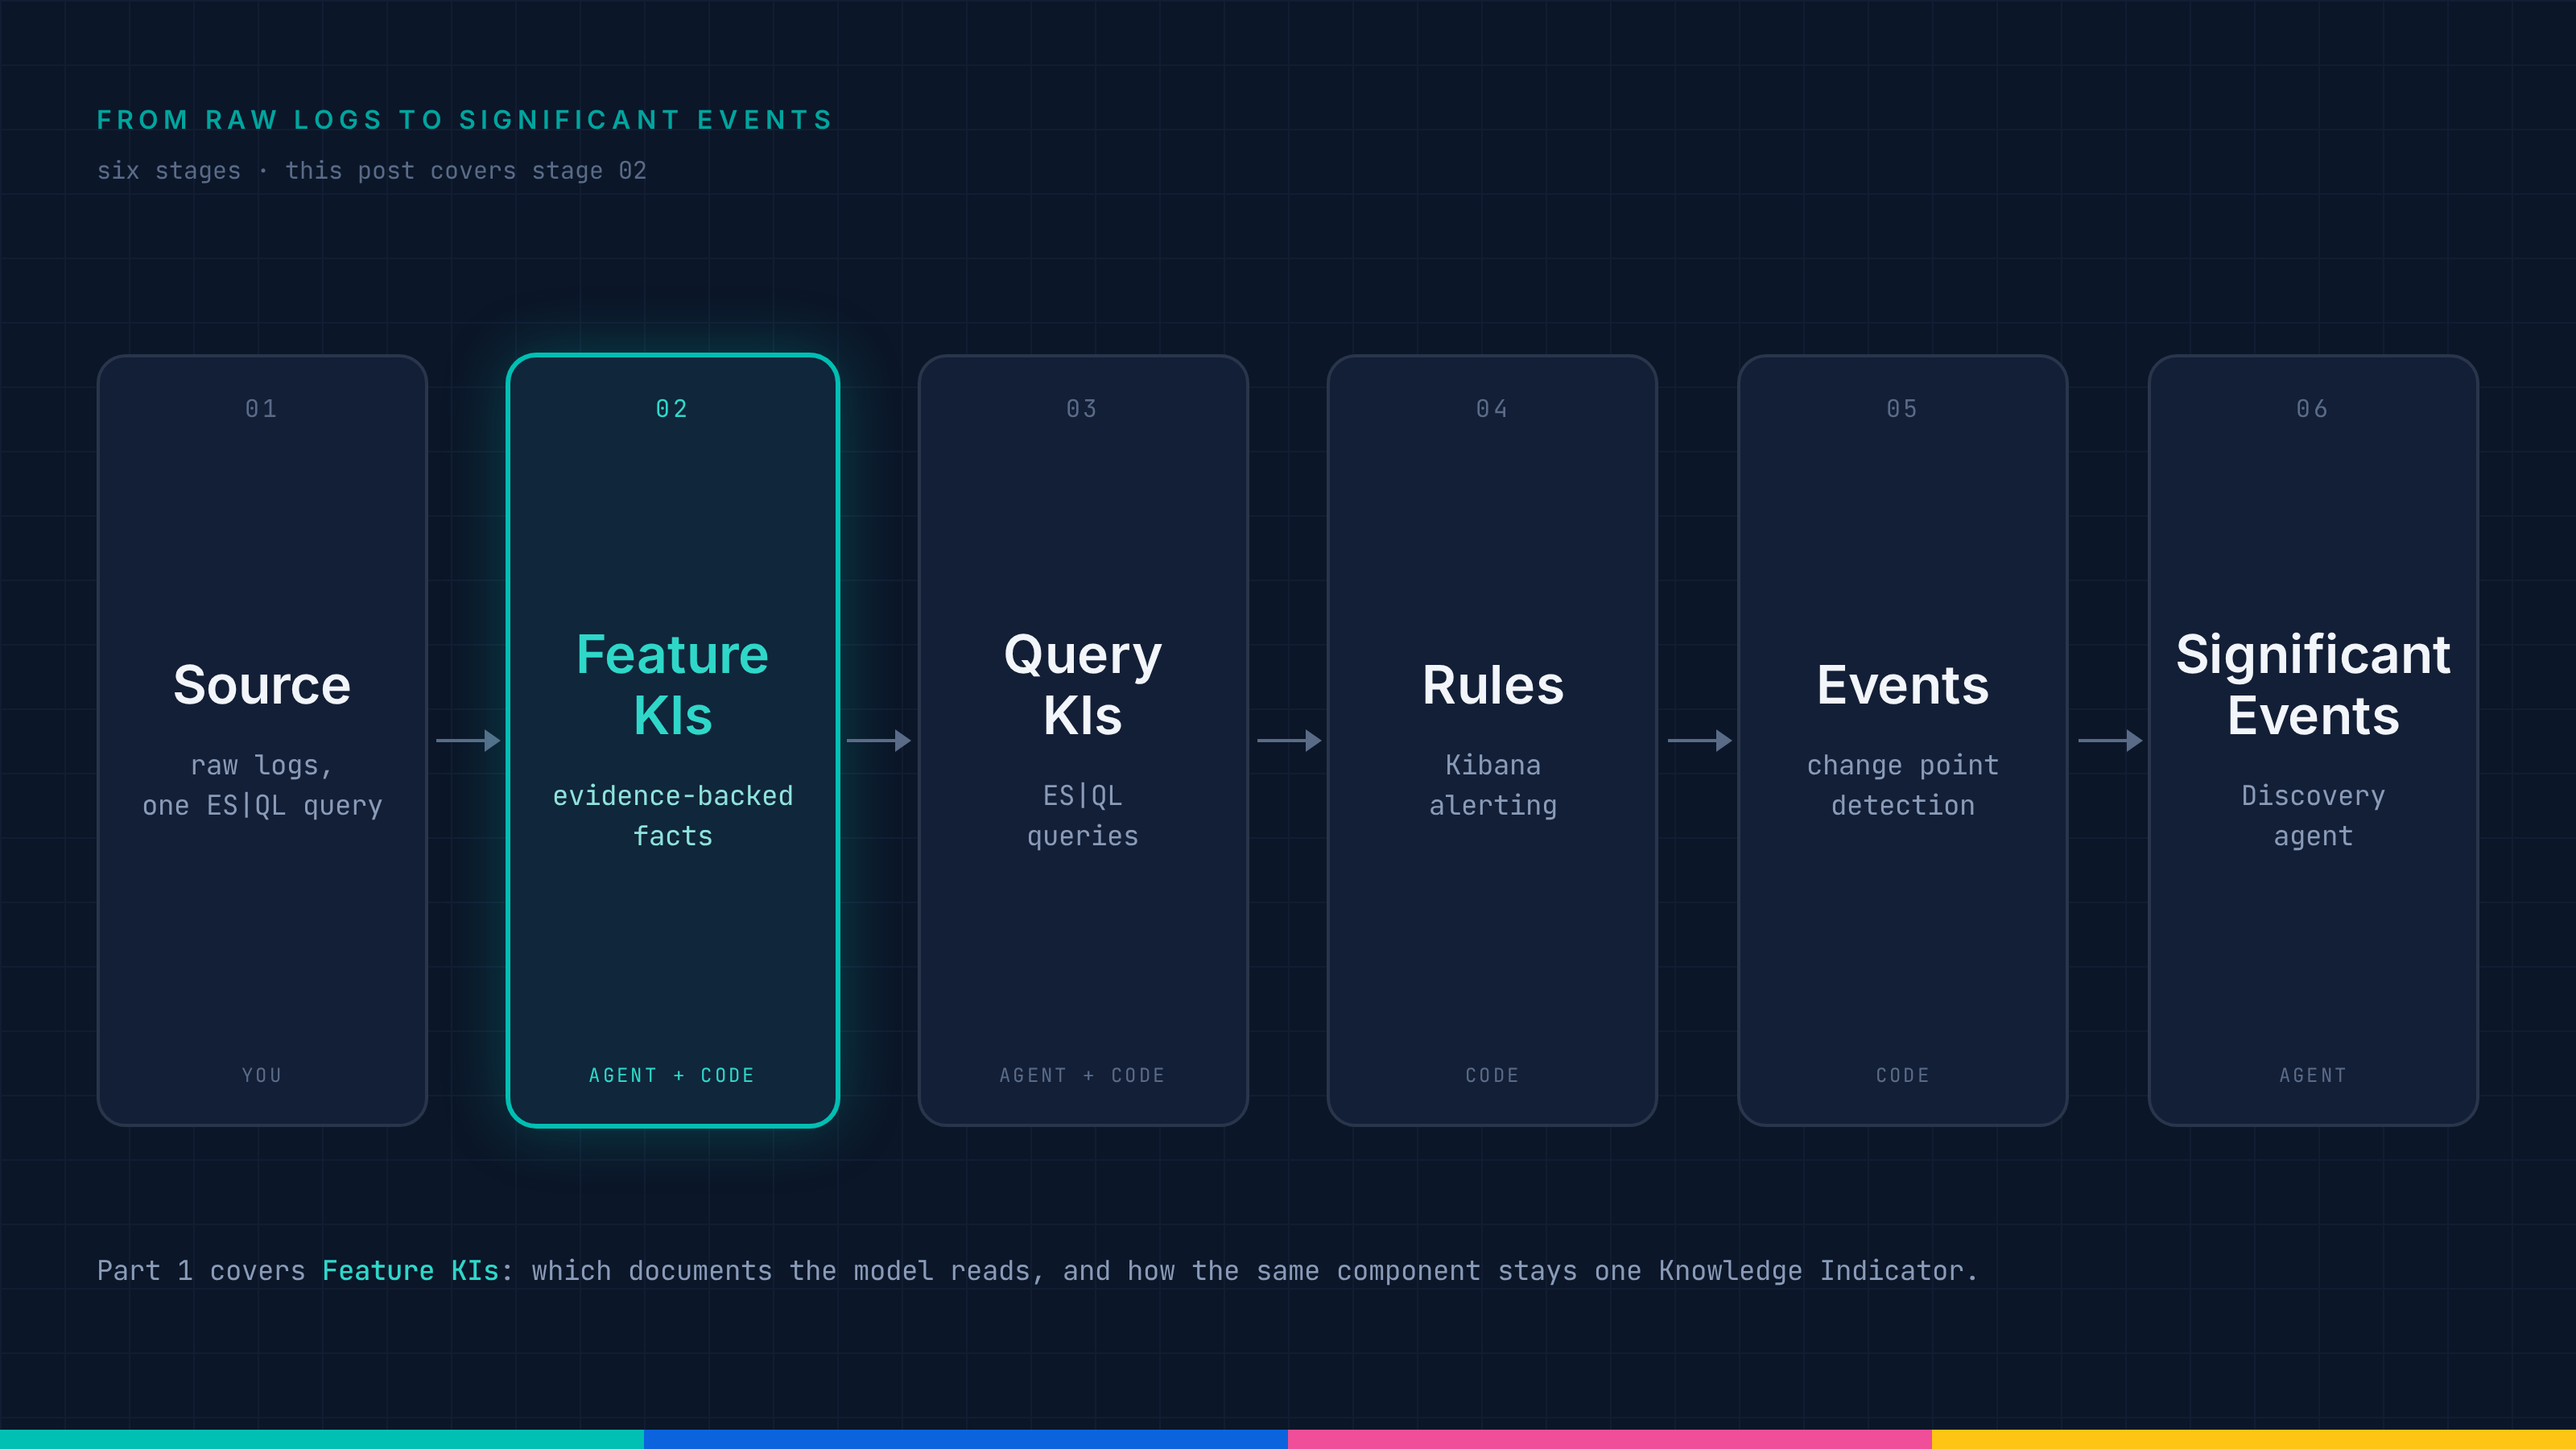
How Elastic Significant Events turns 100 log samples into detection rules
Pick the wrong 100 and you get `log.level: error`, a rule that fires on every request or finds nothing at all, and log sampling is what decides between them.
The Great Cat Escape: A hands-on guide to OpenTelemetry, Elastic APM, and Kibana alerting
Six cats are plotting their escape and you get one alert to stop them. Instrument a Python game with OpenTelemetry, ship it to Elastic APM, and the ES|QL rule you write decides whether you catch the worst offender before it hits ten attempts.
One ES|QL query, 365 days of audit logs: Same search on hot data and searchable snapshots
Collect audit logs with the EDOT Collector, then confirm the 365-day retention policy actually applied before an auditor asks you to.
The service with the most errors was healthy: root cause analysis from logs with ES|QL
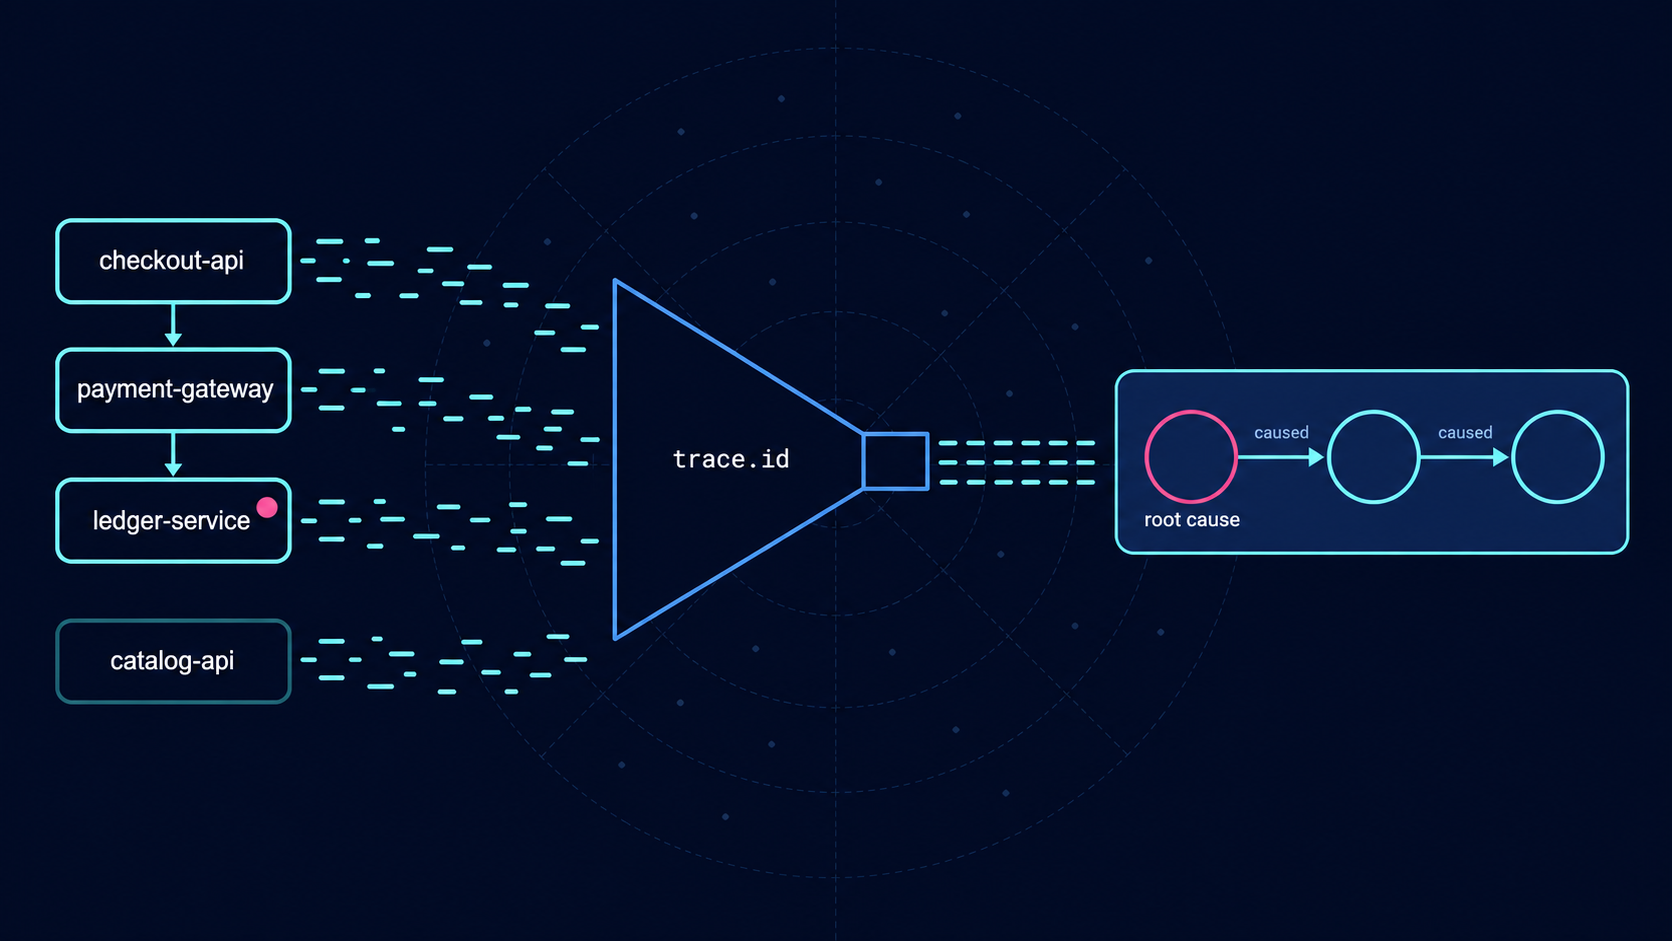
Metrics ranked three services identically at 19.1%. Four ES|QL queries over the same 4,688 OpenTelemetry log records traced 955 of 956 failure chains back to one of them, and needed no service dependency model to do it.
14 alerts, 1 incident: Measuring alerting rule noise with ES|QL in Elasticsearch
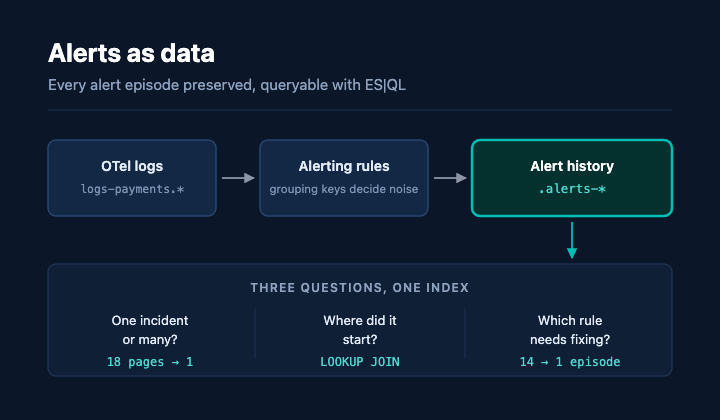
Grouping keys decide how many alerts one incident produces, and because Kibana stamps every alert document with a rule revision, you can measure your alert noise reduction against the same incident that caused the alerts in the first place.
Cut log storage costs with two Elasticsearch data tiers instead of four
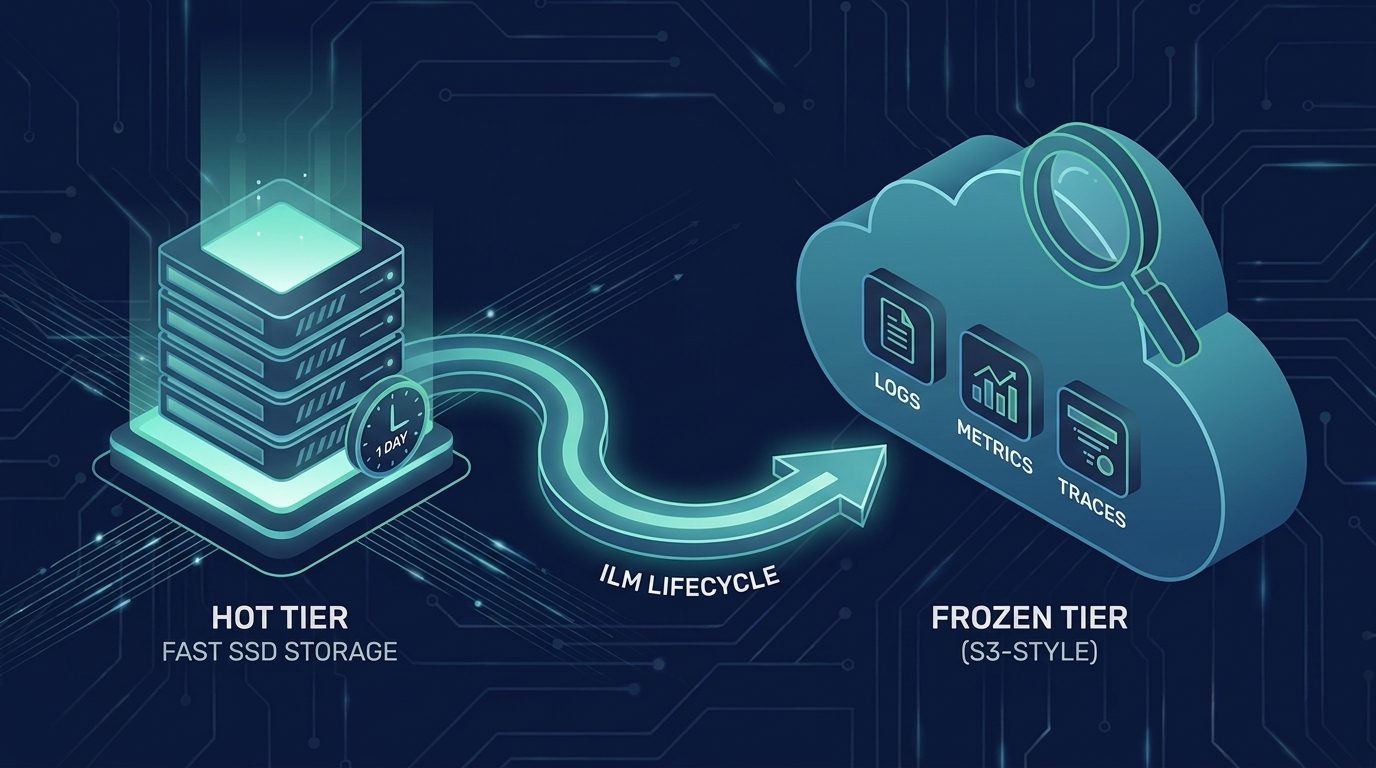
Elastic benchmarked one day of logs on SSD with everything older moved to frozen searchable snapshots, and it came out 16x cheaper than keeping all of it hot. The ILM policy and the cost model are both in the post.
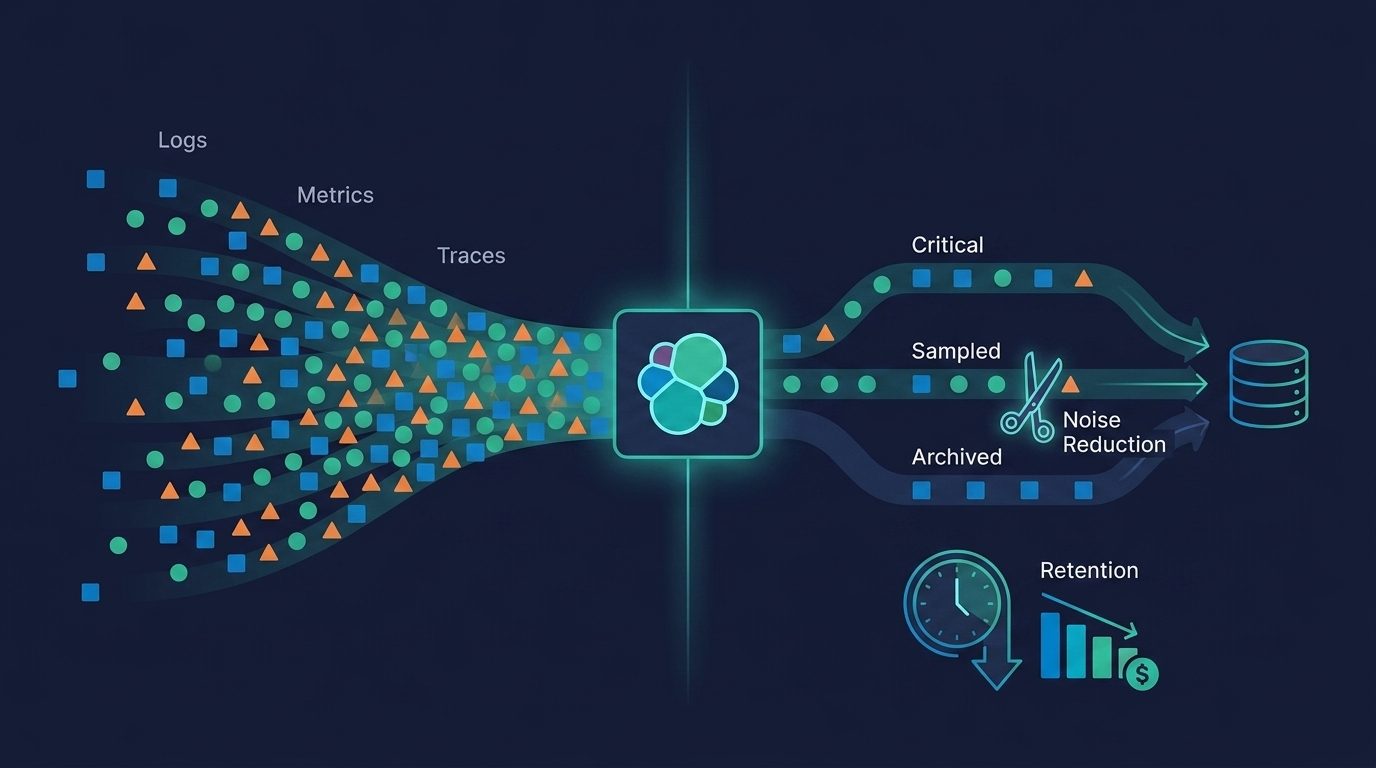
Not every log deserves 90 days: per-stream retention in Elastic Streams
AI Partitioning reads your data and proposes child streams. Retention, drops and downsampling then become per-stream settings, so the noisy ones expire on their own schedule.
Cross-project search for Elastic Observability: one query across every linked project
Keep your observability data where it lives, and still search, alert, and monitor across every linked Serverless project, easily!
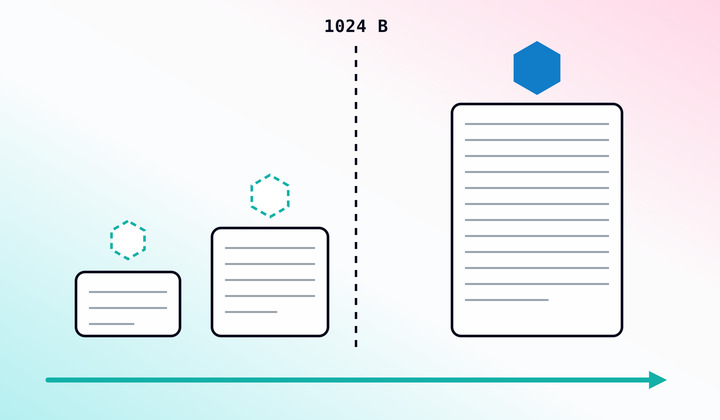
No log file too small: How Elastic Agent tracks files below the 1 KiB threshold
Elastic Agent 9.5 builds a small log file's identity out of the bytes it already has, then re-links it as it grows and crosses 1024 bytes, so it is never re-ingested.
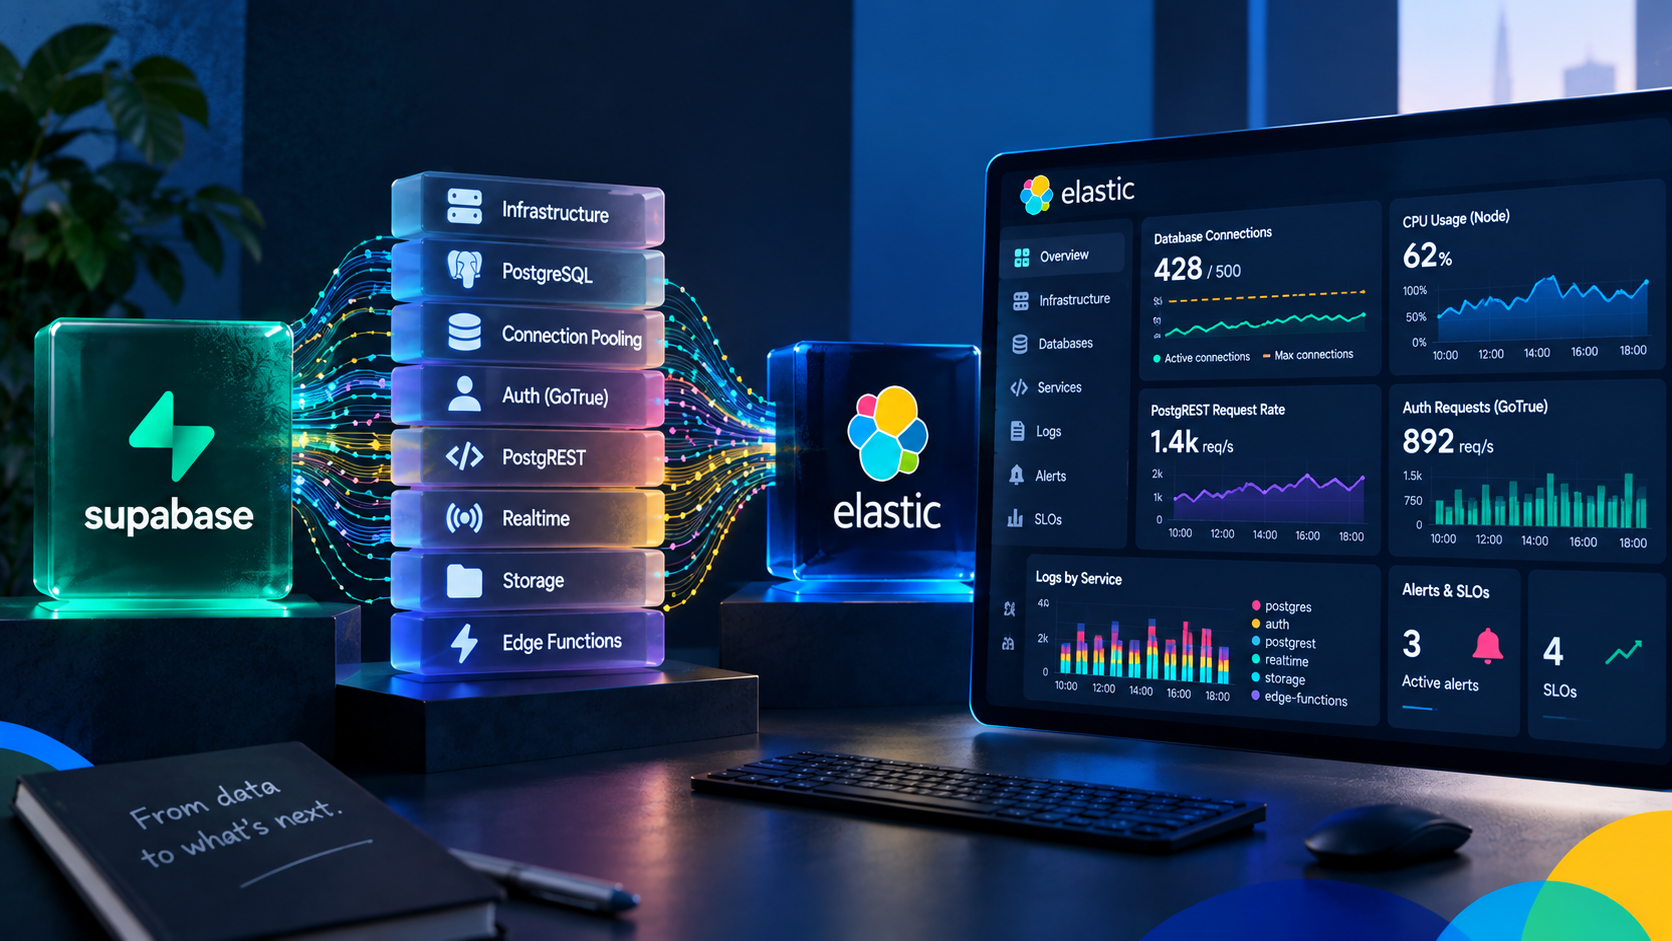
Monitor Supabase in Elastic: dashboards, alert templates, SLO templates, and zero agents
When your Supabase API goes slow, it could be the node, Postgres, the pooler or PostgREST. Elastic tells you which one and shows you the logs from whichever it was.