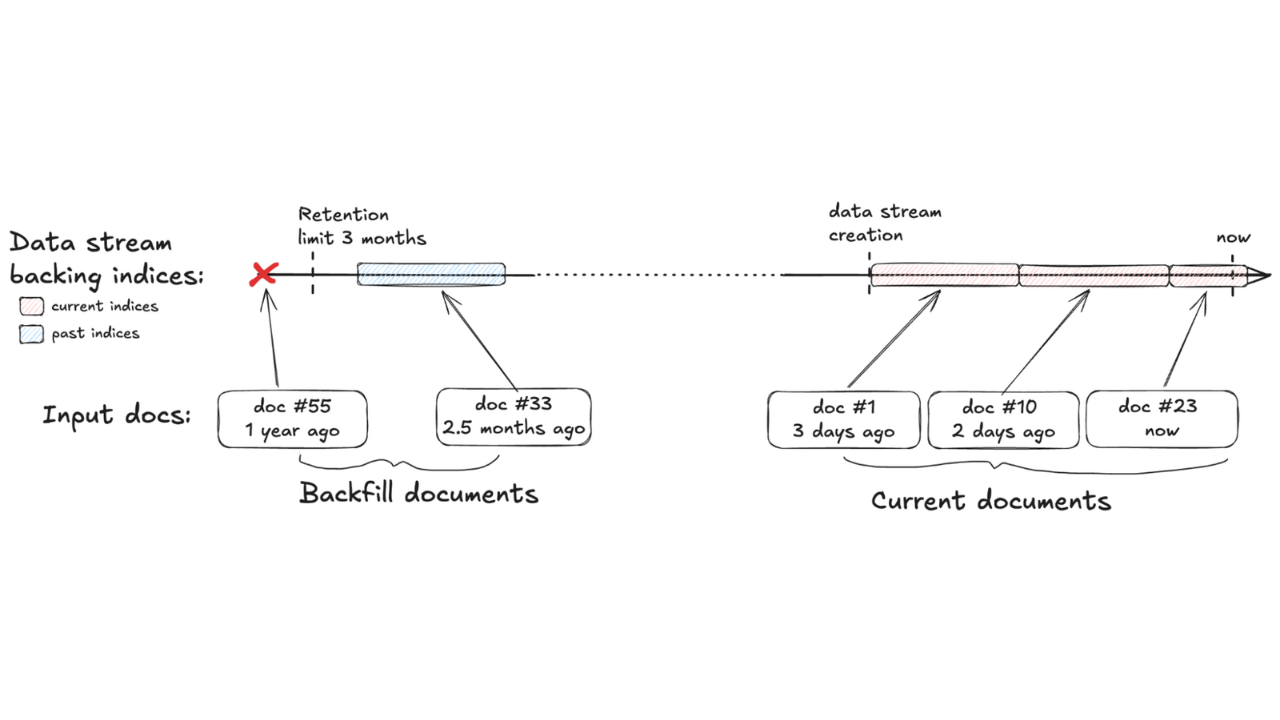
Backfill time series data in Elasticsearch: Load months of historical metrics through the bulk API
Elasticsearch works out the time boundaries and creates the past backing indices as the documents land, so a historical data migration runs on your normal ingest path.
No more allocation delays: Decoupling snapshots from shard relocation in stateless Elasticsearch
Clusters scale out under load without waiting for a snapshot to finish, because snapshots now read straight from the object store and no longer pin shards in place.
Dashboard activity logs: Find out which Kibana dashboards get used
Kibana now logs who viewed, edited or deleted each dashboard, how long it took and what failed, so you can catch a broken dashboard before anyone reports it.
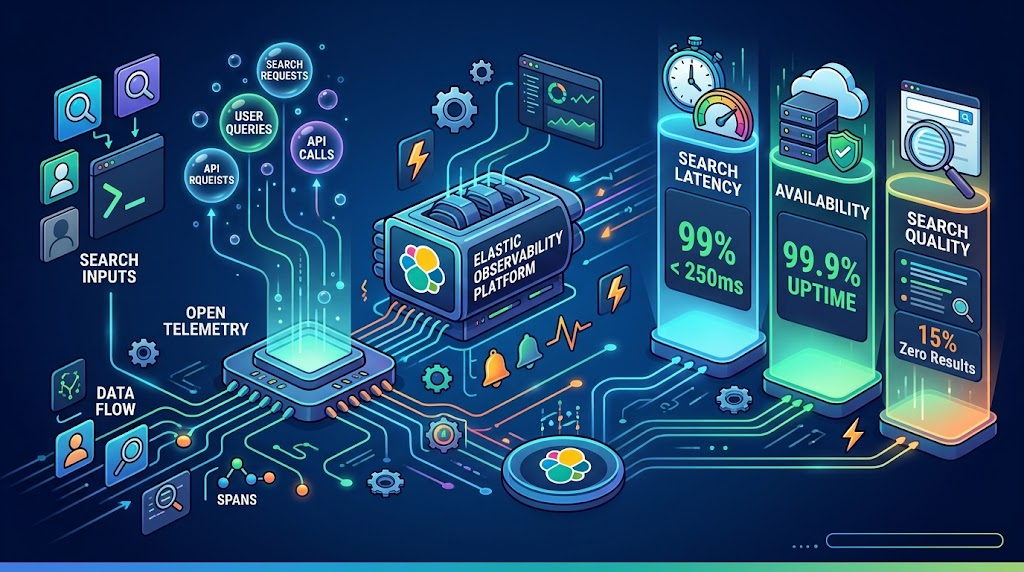
Three SLOs every search team needs: monitoring search latency, availability and quality with OpenTelemetry
Your OpenTelemetry search spans already carry the signals for SLOs, burn rate alerts, anomaly detection and incident response, and this post shows how to build all four in Elastic Observability.
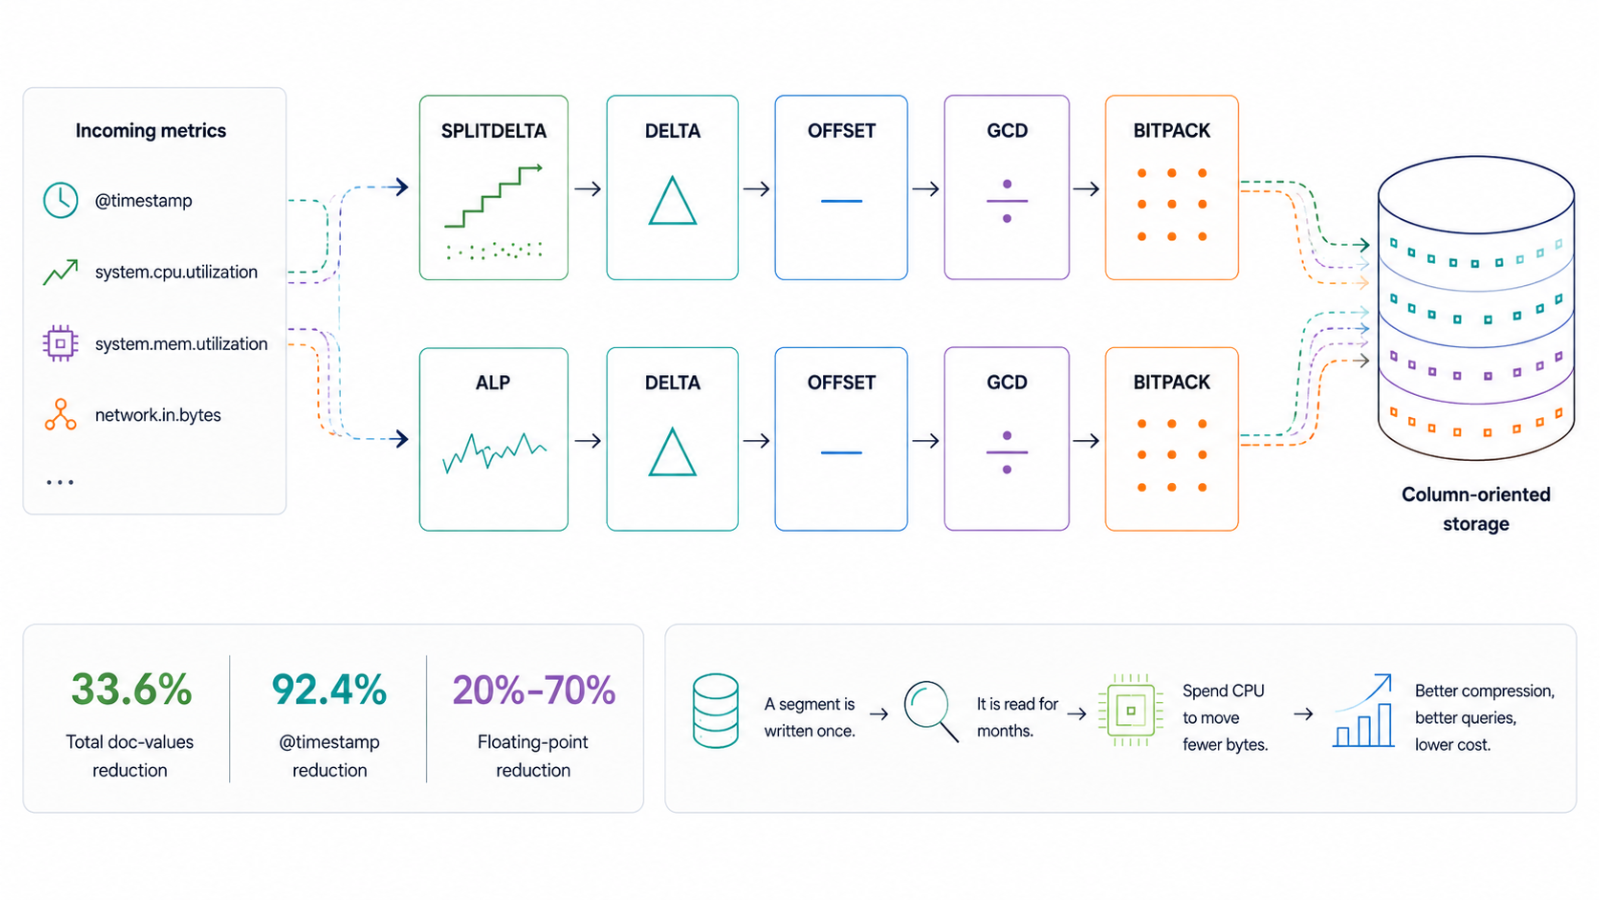
ES95: Adaptive Compression for Elasticsearch Time-Series Metrics
ES95 is Elasticsearch 9.5's new adaptive time series codec that cuts @timestamp storage by 92% and floating point fields by up to 74%, with zero configuration.

Two lines of JSON to replace your ILM policy: data stream lifecycle adds frozen tier support
In Elasticsearch 9.5, frozen_after in data stream lifecycle moves indices to searchable snapshots on object storage on their own, keeping them queryable alongside downsampling and retention.
The mystery stress your heap chart can't see: AutoOps now watches vector off-heap memory
Dense vectors use off-heap memory your heap chart never shows. AutoOps detects memory pressure before vector RAM stress causes OOM.
Your agents have been keeping receipts: turning Elastic Agent Builder's built-in OTel traces into token cost dashboards in Kibana
Your Agent Builder agents already log every LLM call as an OTel trace, and that agent tracing data can power token cost dashboards and budget alerts before one runaway conversation quietly wrecks your month.
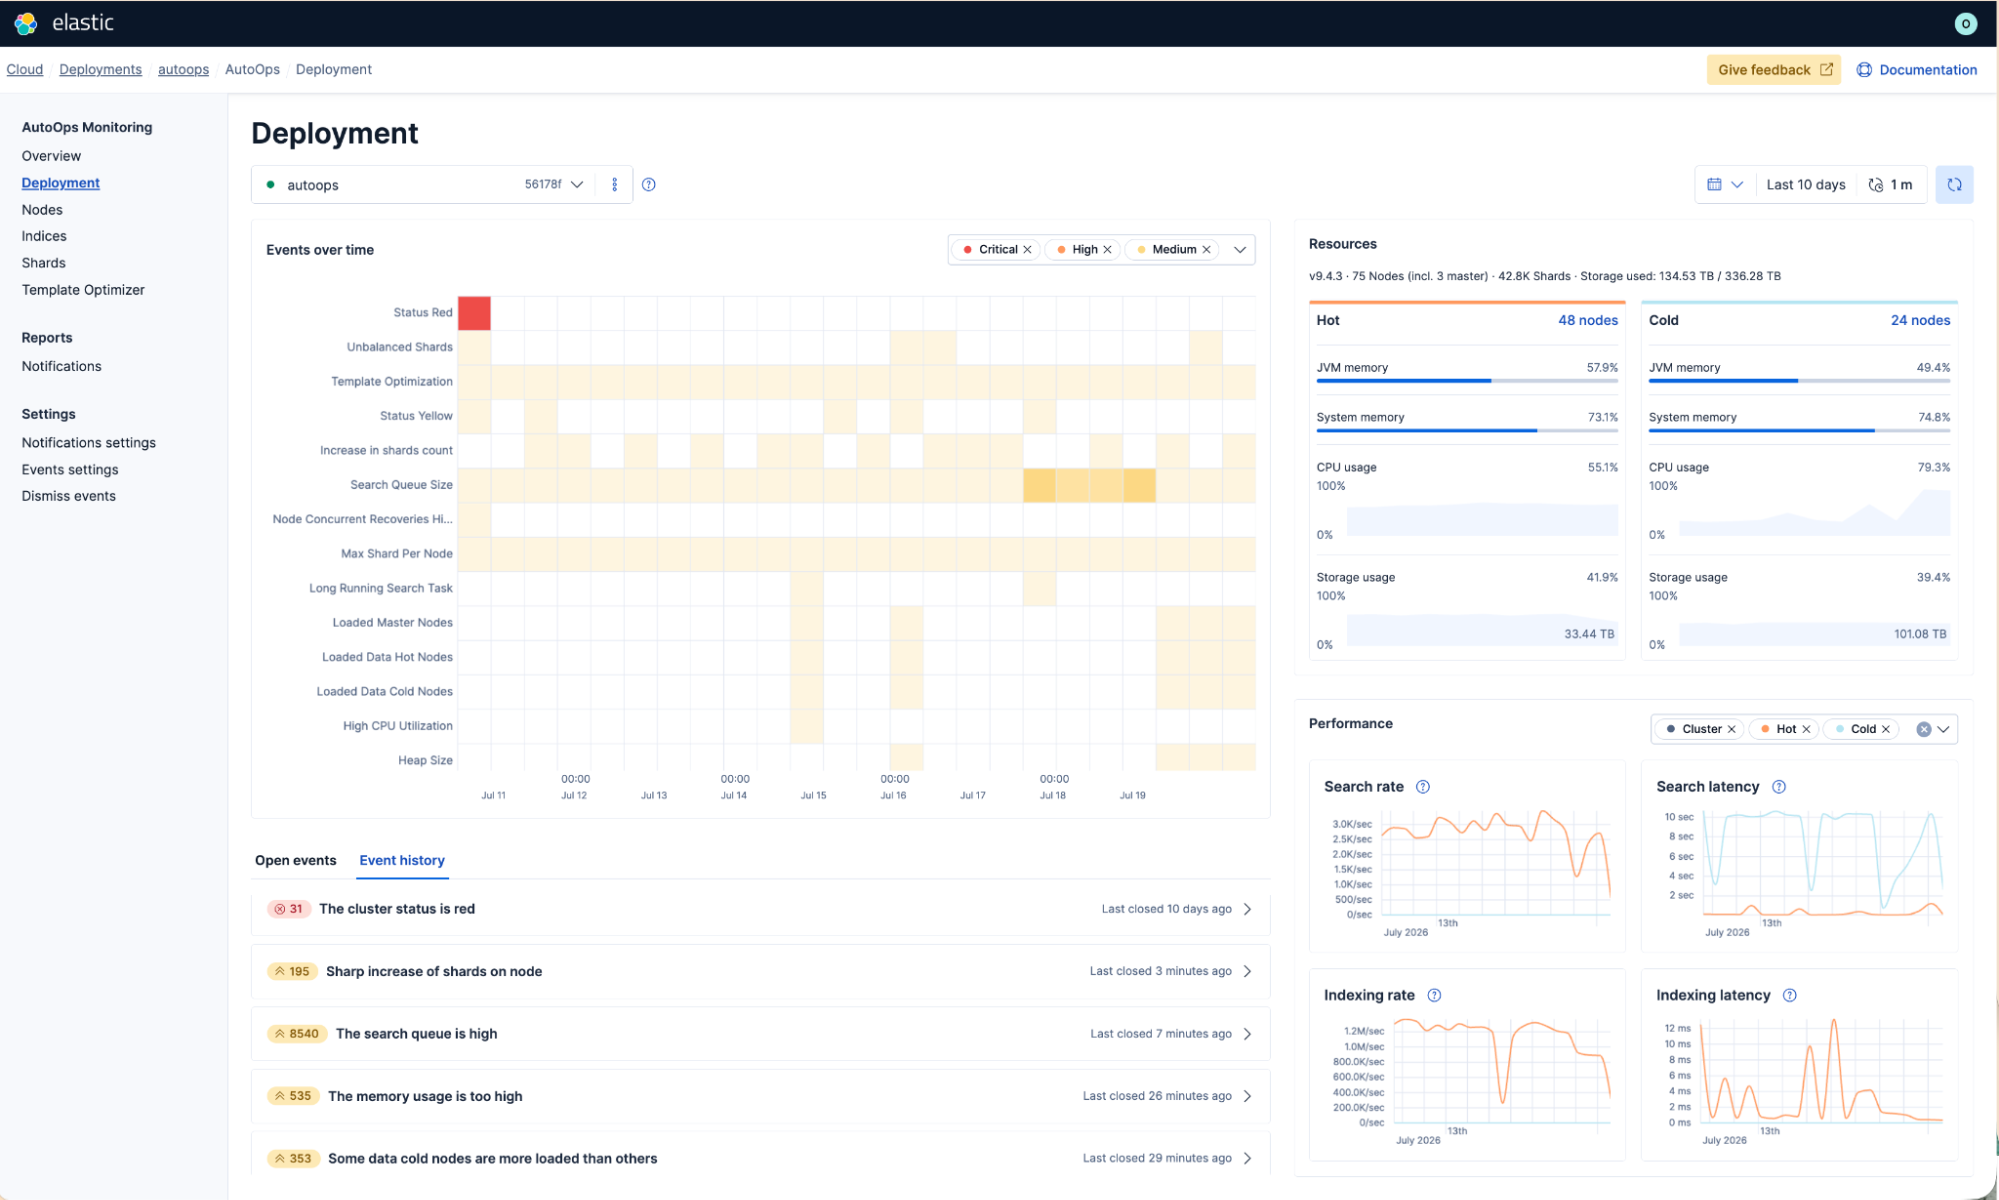
Faster Elasticsearch issue triage with redesigned AutoOps
AutoOps introduces clearer severity, updated page layouts, and simpler issue triage for Elastic Cloud Hosted deployments and Cloud Connect clusters.

98.9% faster queries, 4x more indexing throughput: a systematic Elasticsearch performance diagnosis
Use AutoOps, the Profile API and ES Rally together to find cluster hotspots, slow queries and index bottlenecks, with real benchmarks showing a 98.9% latency cut and 4x indexing gain.

Your compliance posture just got an upgrade: Elasticsearch now supports FIPS 140-3
Elastic 9.4 brings FIPS 140-3 support for Elasticsearch and Kibana to GA. Here's what changes for federal, defense and regulated deployments, and how to migrate from 140-2.
Why your Elasticsearch cluster is hitting disk watermarks: 14 real-world causes explained
Learn how Elasticsearch disk watermarks work, why they trigger, and how to diagnose 14 of the most common scenarios Support encounters, from index bloat to ILM stalls.