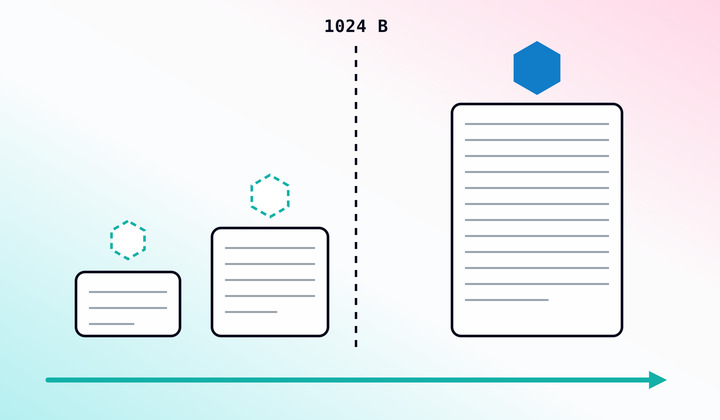
No log file too small: How Elastic Agent tracks files below the 1 KiB threshold
Elastic Agent 9.5 builds a small log file's identity out of the bytes it already has, then re-links it as it grows and crosses 1024 bytes, so it is never re-ingested.
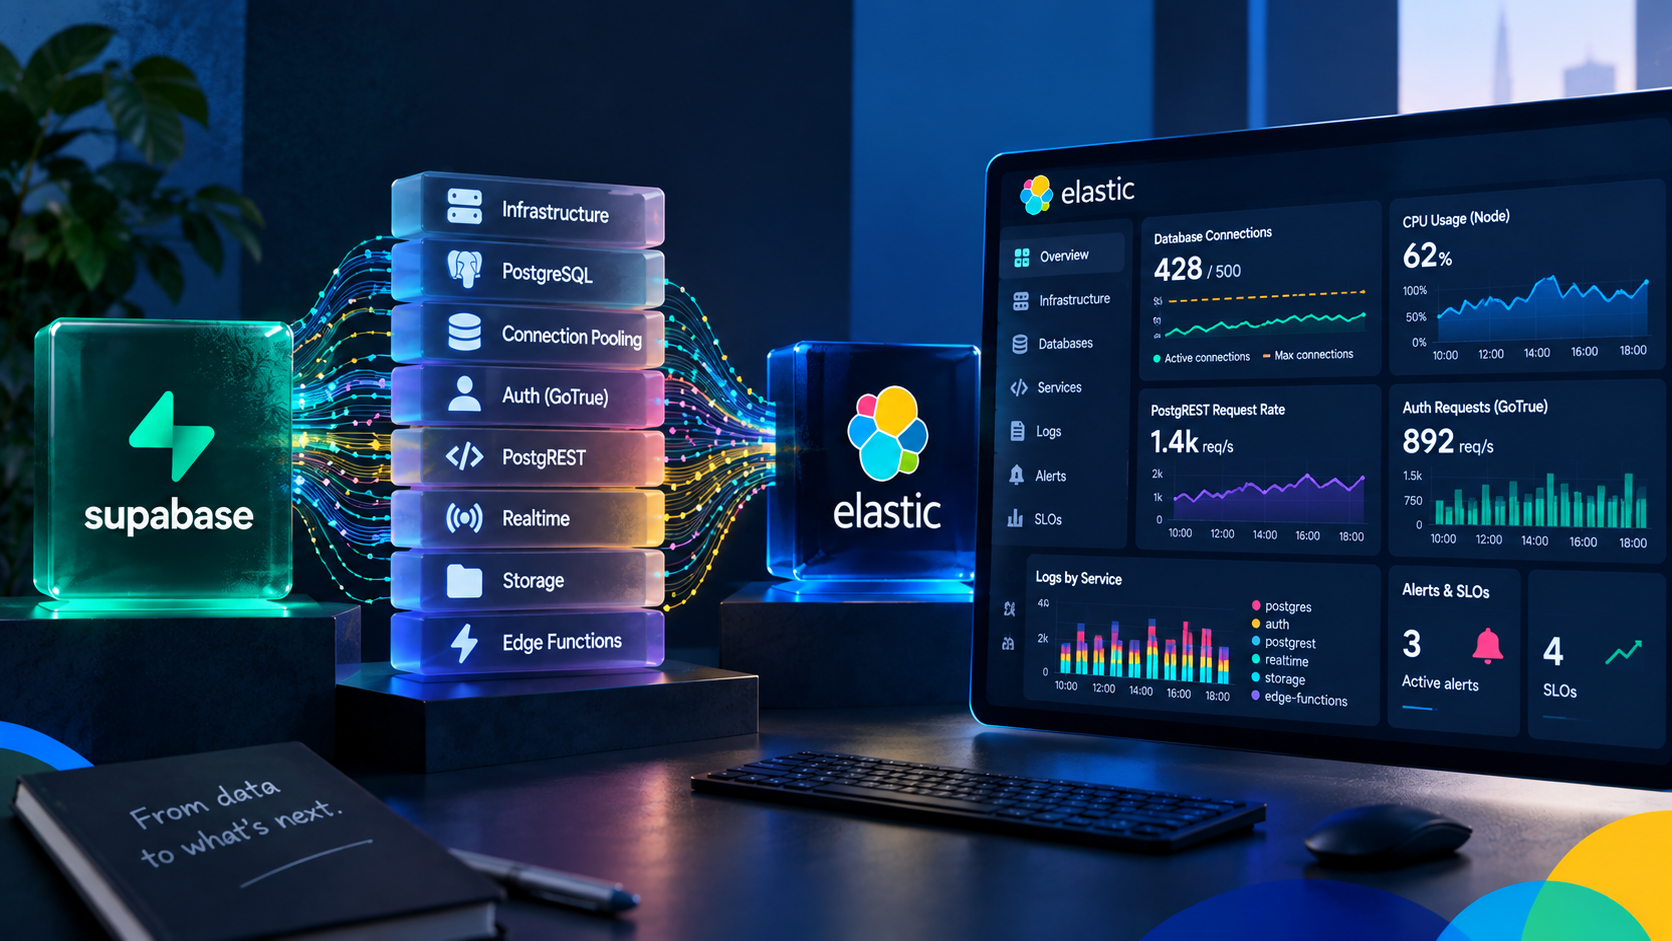
Monitor Supabase in Elastic: dashboards, alert templates, SLO templates, and zero agents
When your Supabase API goes slow, it could be the node, Postgres, the pooler or PostgREST. Elastic tells you which one and shows you the logs from whichever it was.
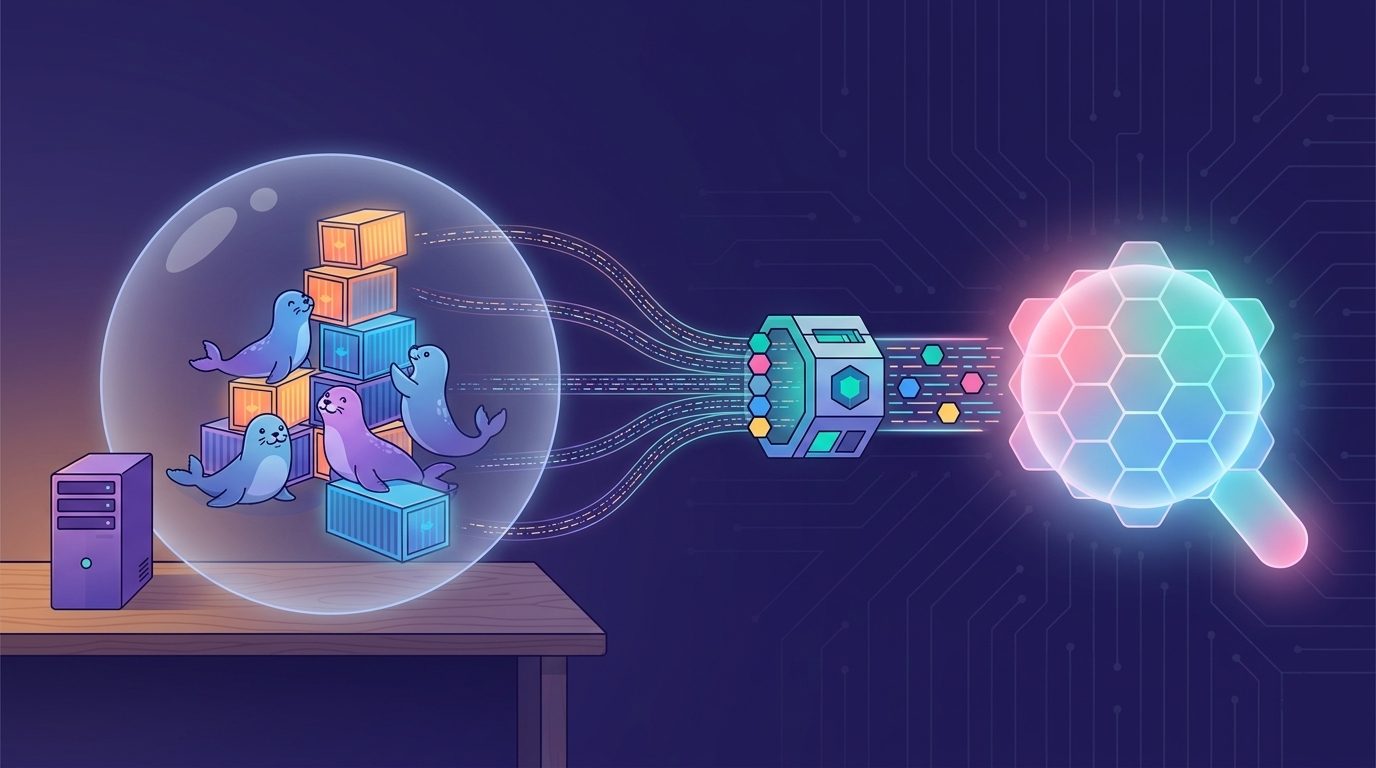
Collecting rootless Podman logs with Elastic Agent: the CRI parser, user-scoped paths, and the Podman socket
Rootless Podman containers write their logs in CRI format. This Fleet policy reads them and attaches container.* fields, with the match_source_index value that rootless paths need.
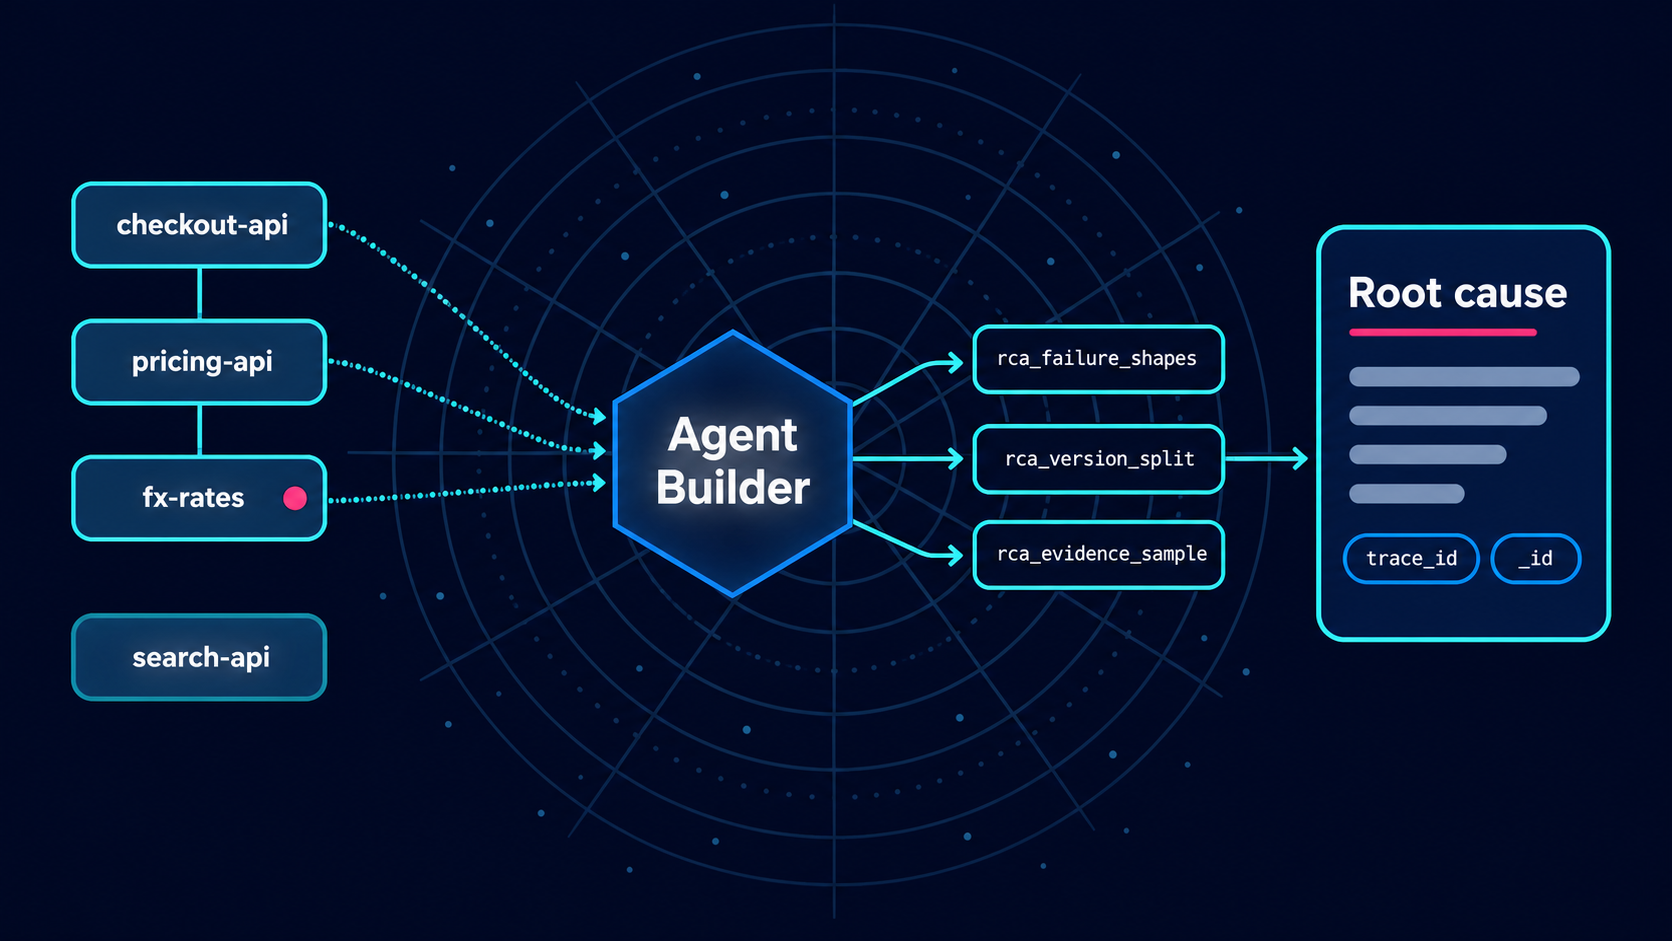
AI root cause analysis in Elastic Agent Builder that cites its evidence
The new release failed at 27.2%, the old one at 28.2%, so the deploy was never the cause; the agent worked that out in 72 seconds and handed back a trace ID for the failure that was.
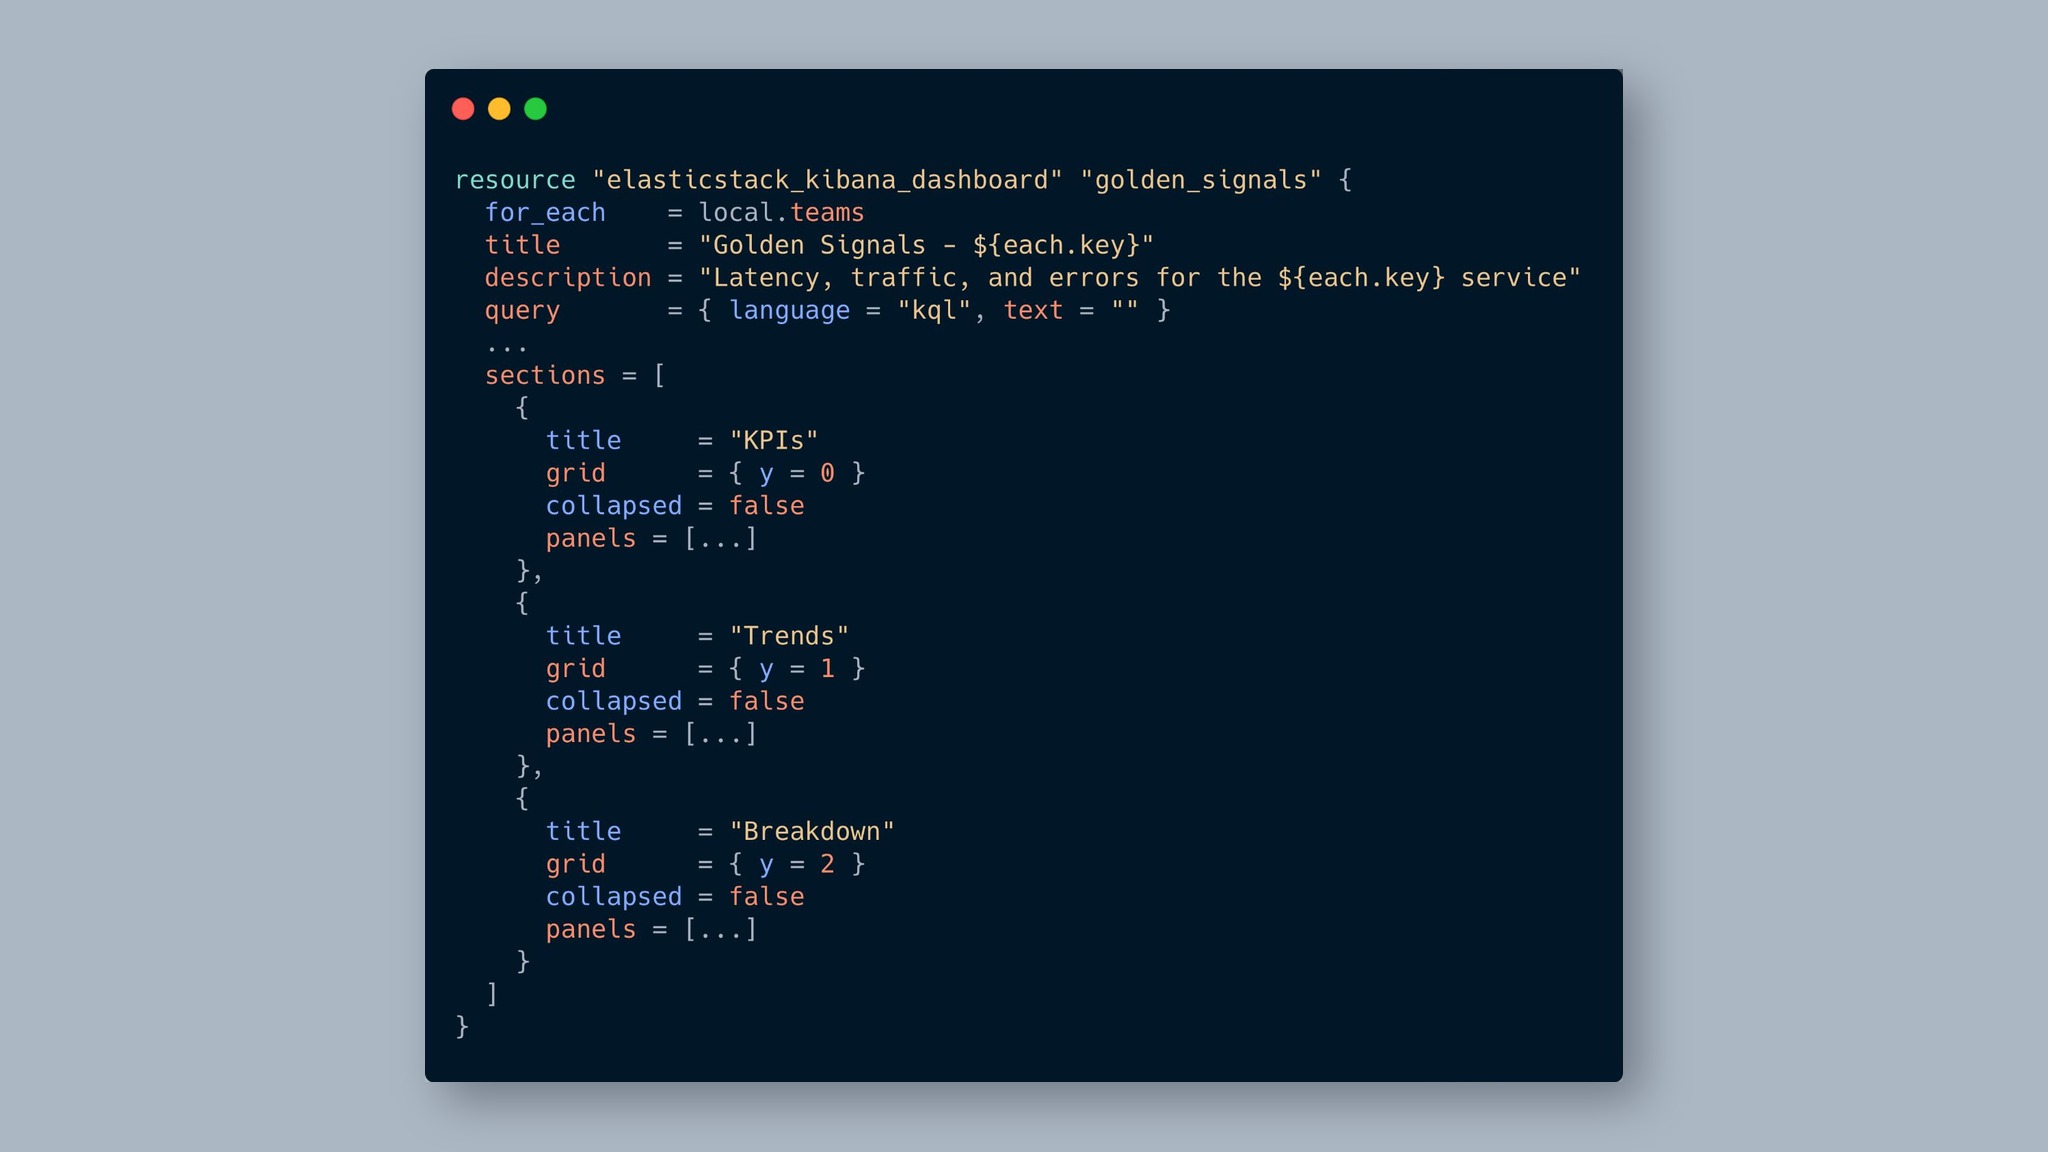
One edit, every dashboard updated: managing Kibana observability at scale with Terraform
Define your golden-signals panels once in a shared HCL library and use for_each to generate every team's dashboard, with drift detection and git rollback built in.
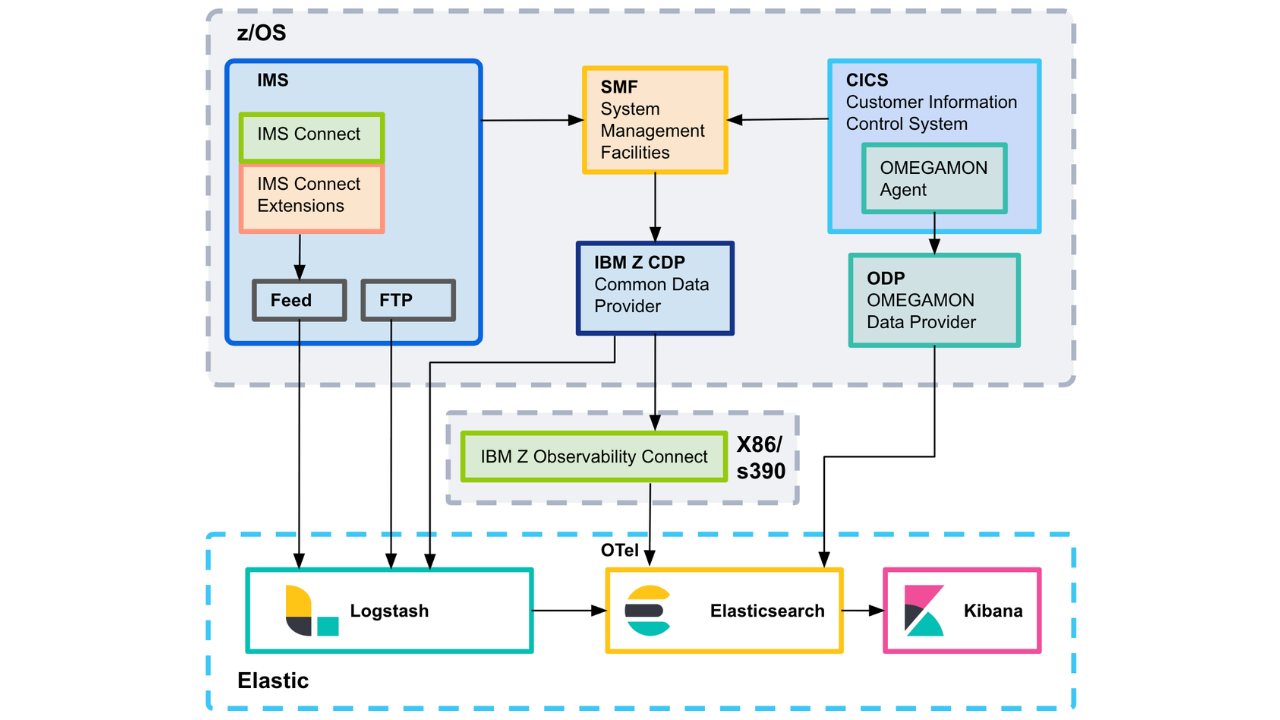
Elastic z/OS ingest: five architectures for mainframe data
This field guide walks through the ingest architectures I've seen work in production, the data quality checks that decide whether your dashboards actually work, and the ECS mapping that makes mainframe data usable to the platform.
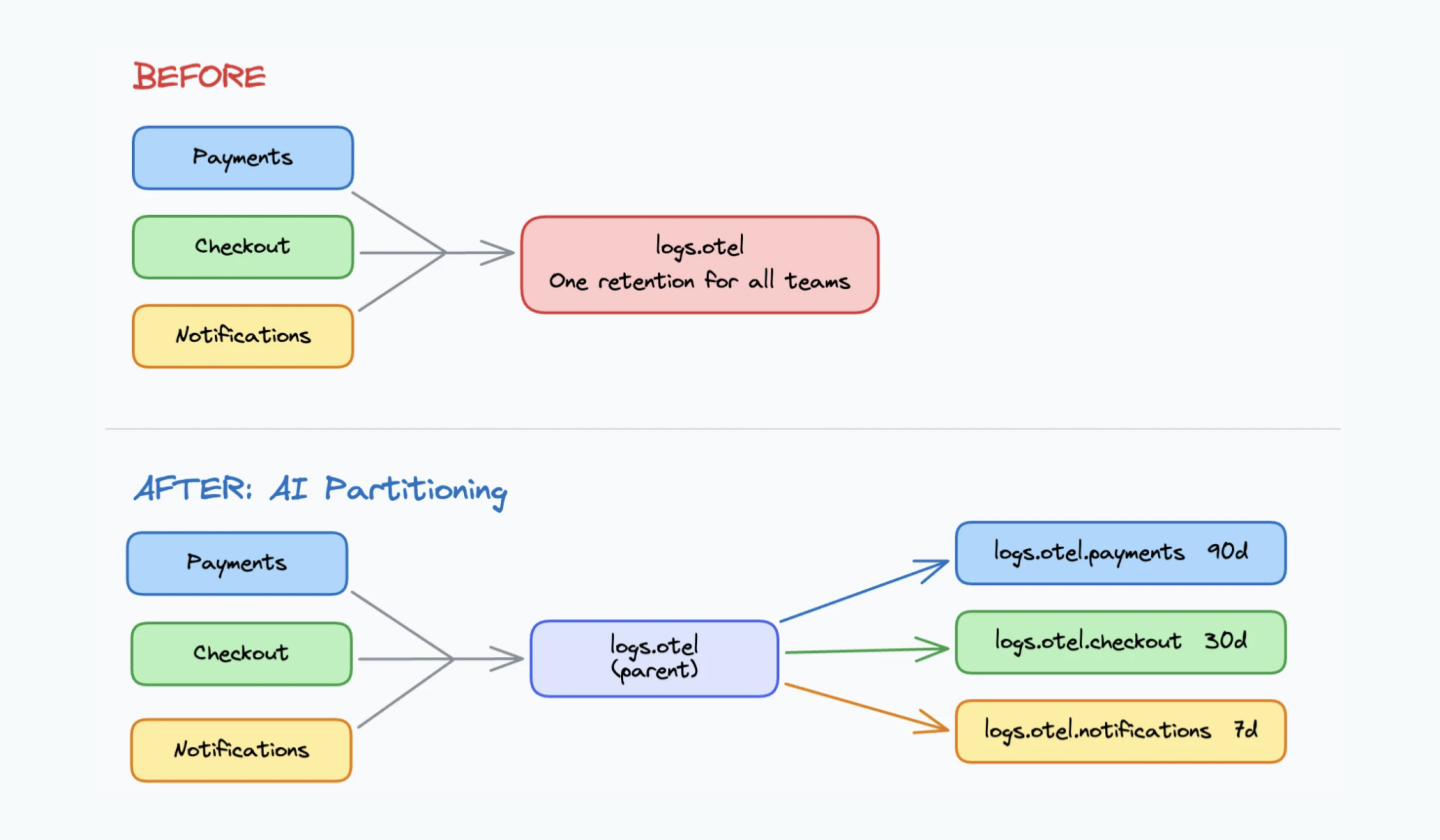
One OTLP endpoint, three teams, zero routing rules: Elasticsearch Streams AI Partitioning
Stop writing log routing rules upfront. See how Streams AI Partitioning reads your data, proposes child streams, and lets you set per-team retention in minutes.
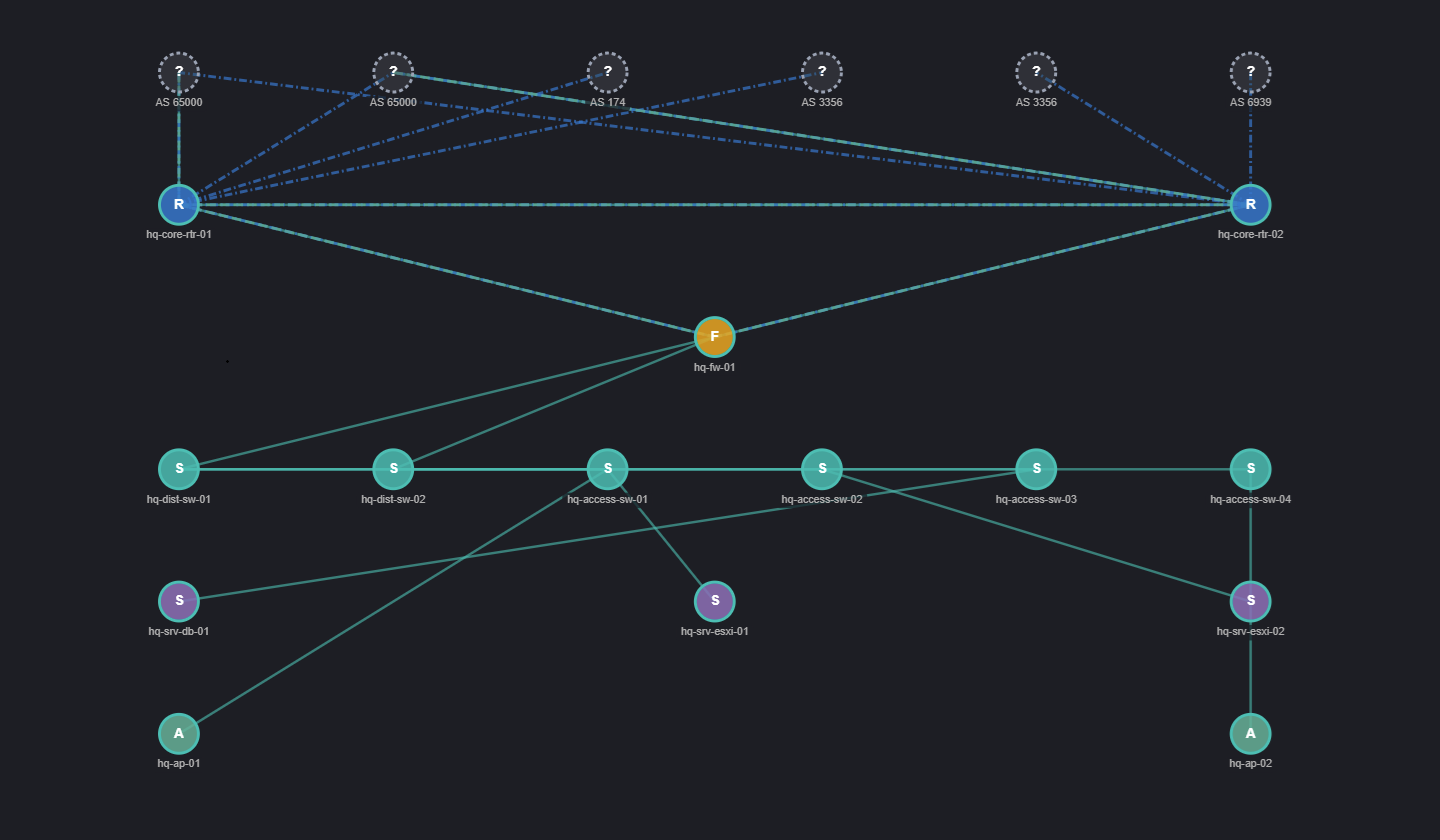
SNMP Topology Data in Kibana: Collection to Canvas
The Network Topology plugin for Kibana provides a ready-to-deploy Logstash pipeline, a structured schema, and a topology view that shows what's connected to what.
Configure downsampling directly in Elastic Streams, no more JSON editing needed
Configure downsampling in Elastic Streams alongside retention and tiers, with a live preview and validation. No more editing ILM or lifecycle JSON.
Migrate Logstash Pipelines from Azure Event Hubs to OTel Collector Kafka Receiver
Step-by-step guide to migrating Logstash pipelines from the Azure Event Hubs plugin to the OpenTelemetry Collector Kafka receiver.
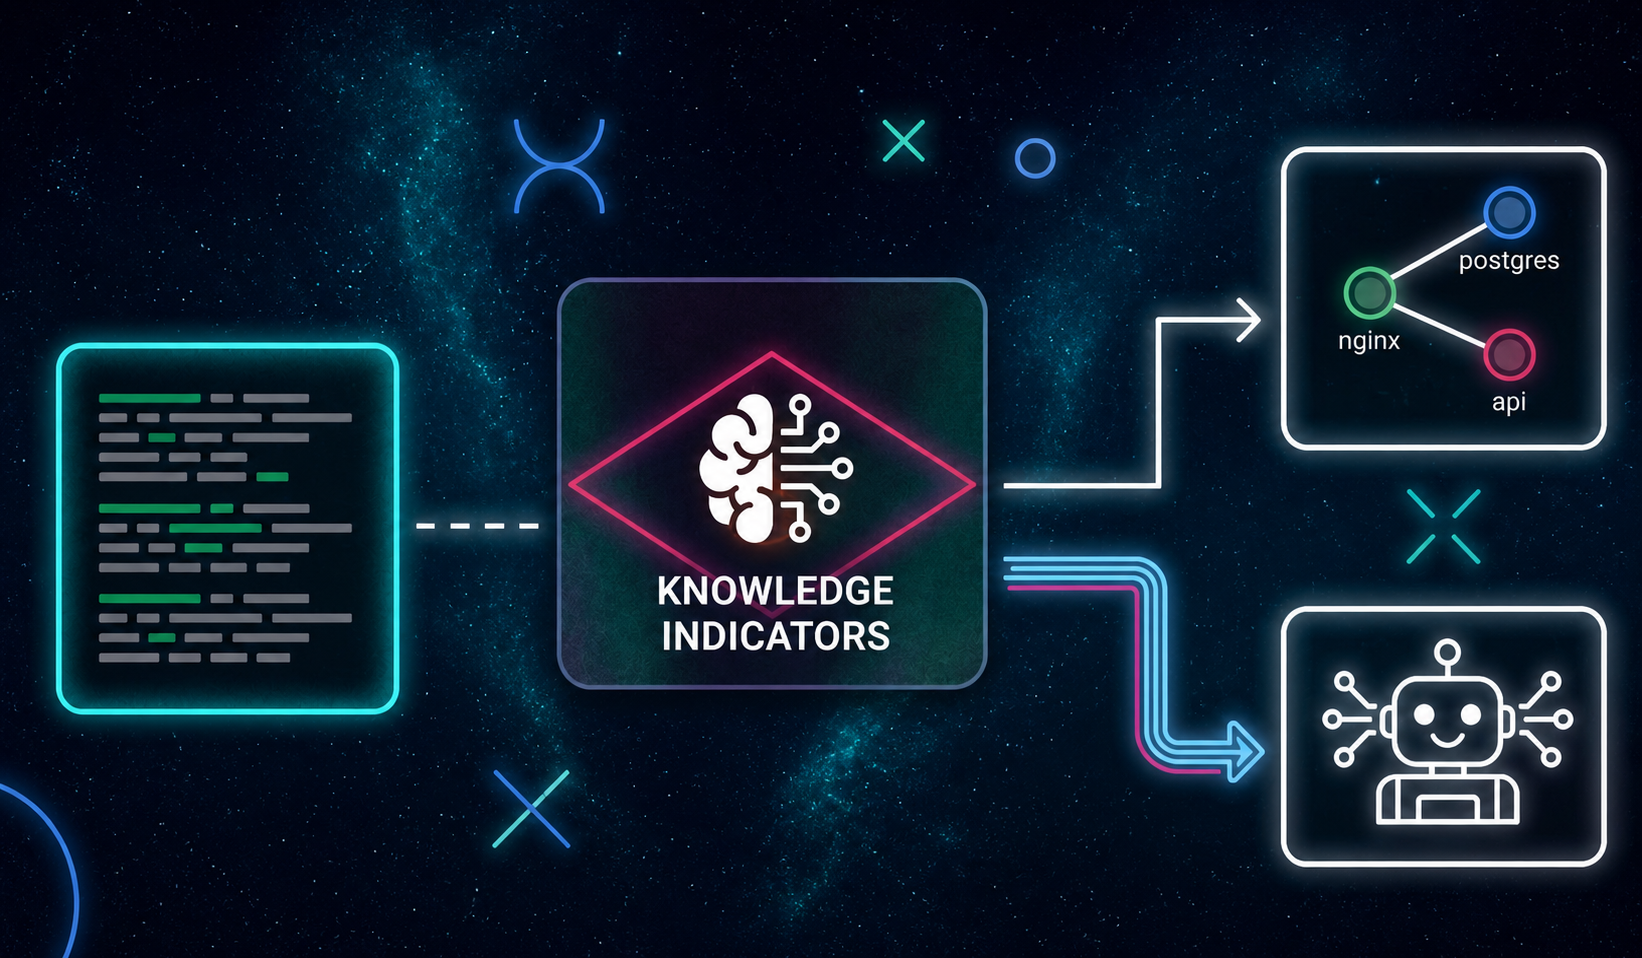
From raw logs to system knowledge: the AI context layer observability is missing
A self-updating knowledge base built from your logs: services, dependencies, and failure modes, so your AI agents always know what they are looking at.
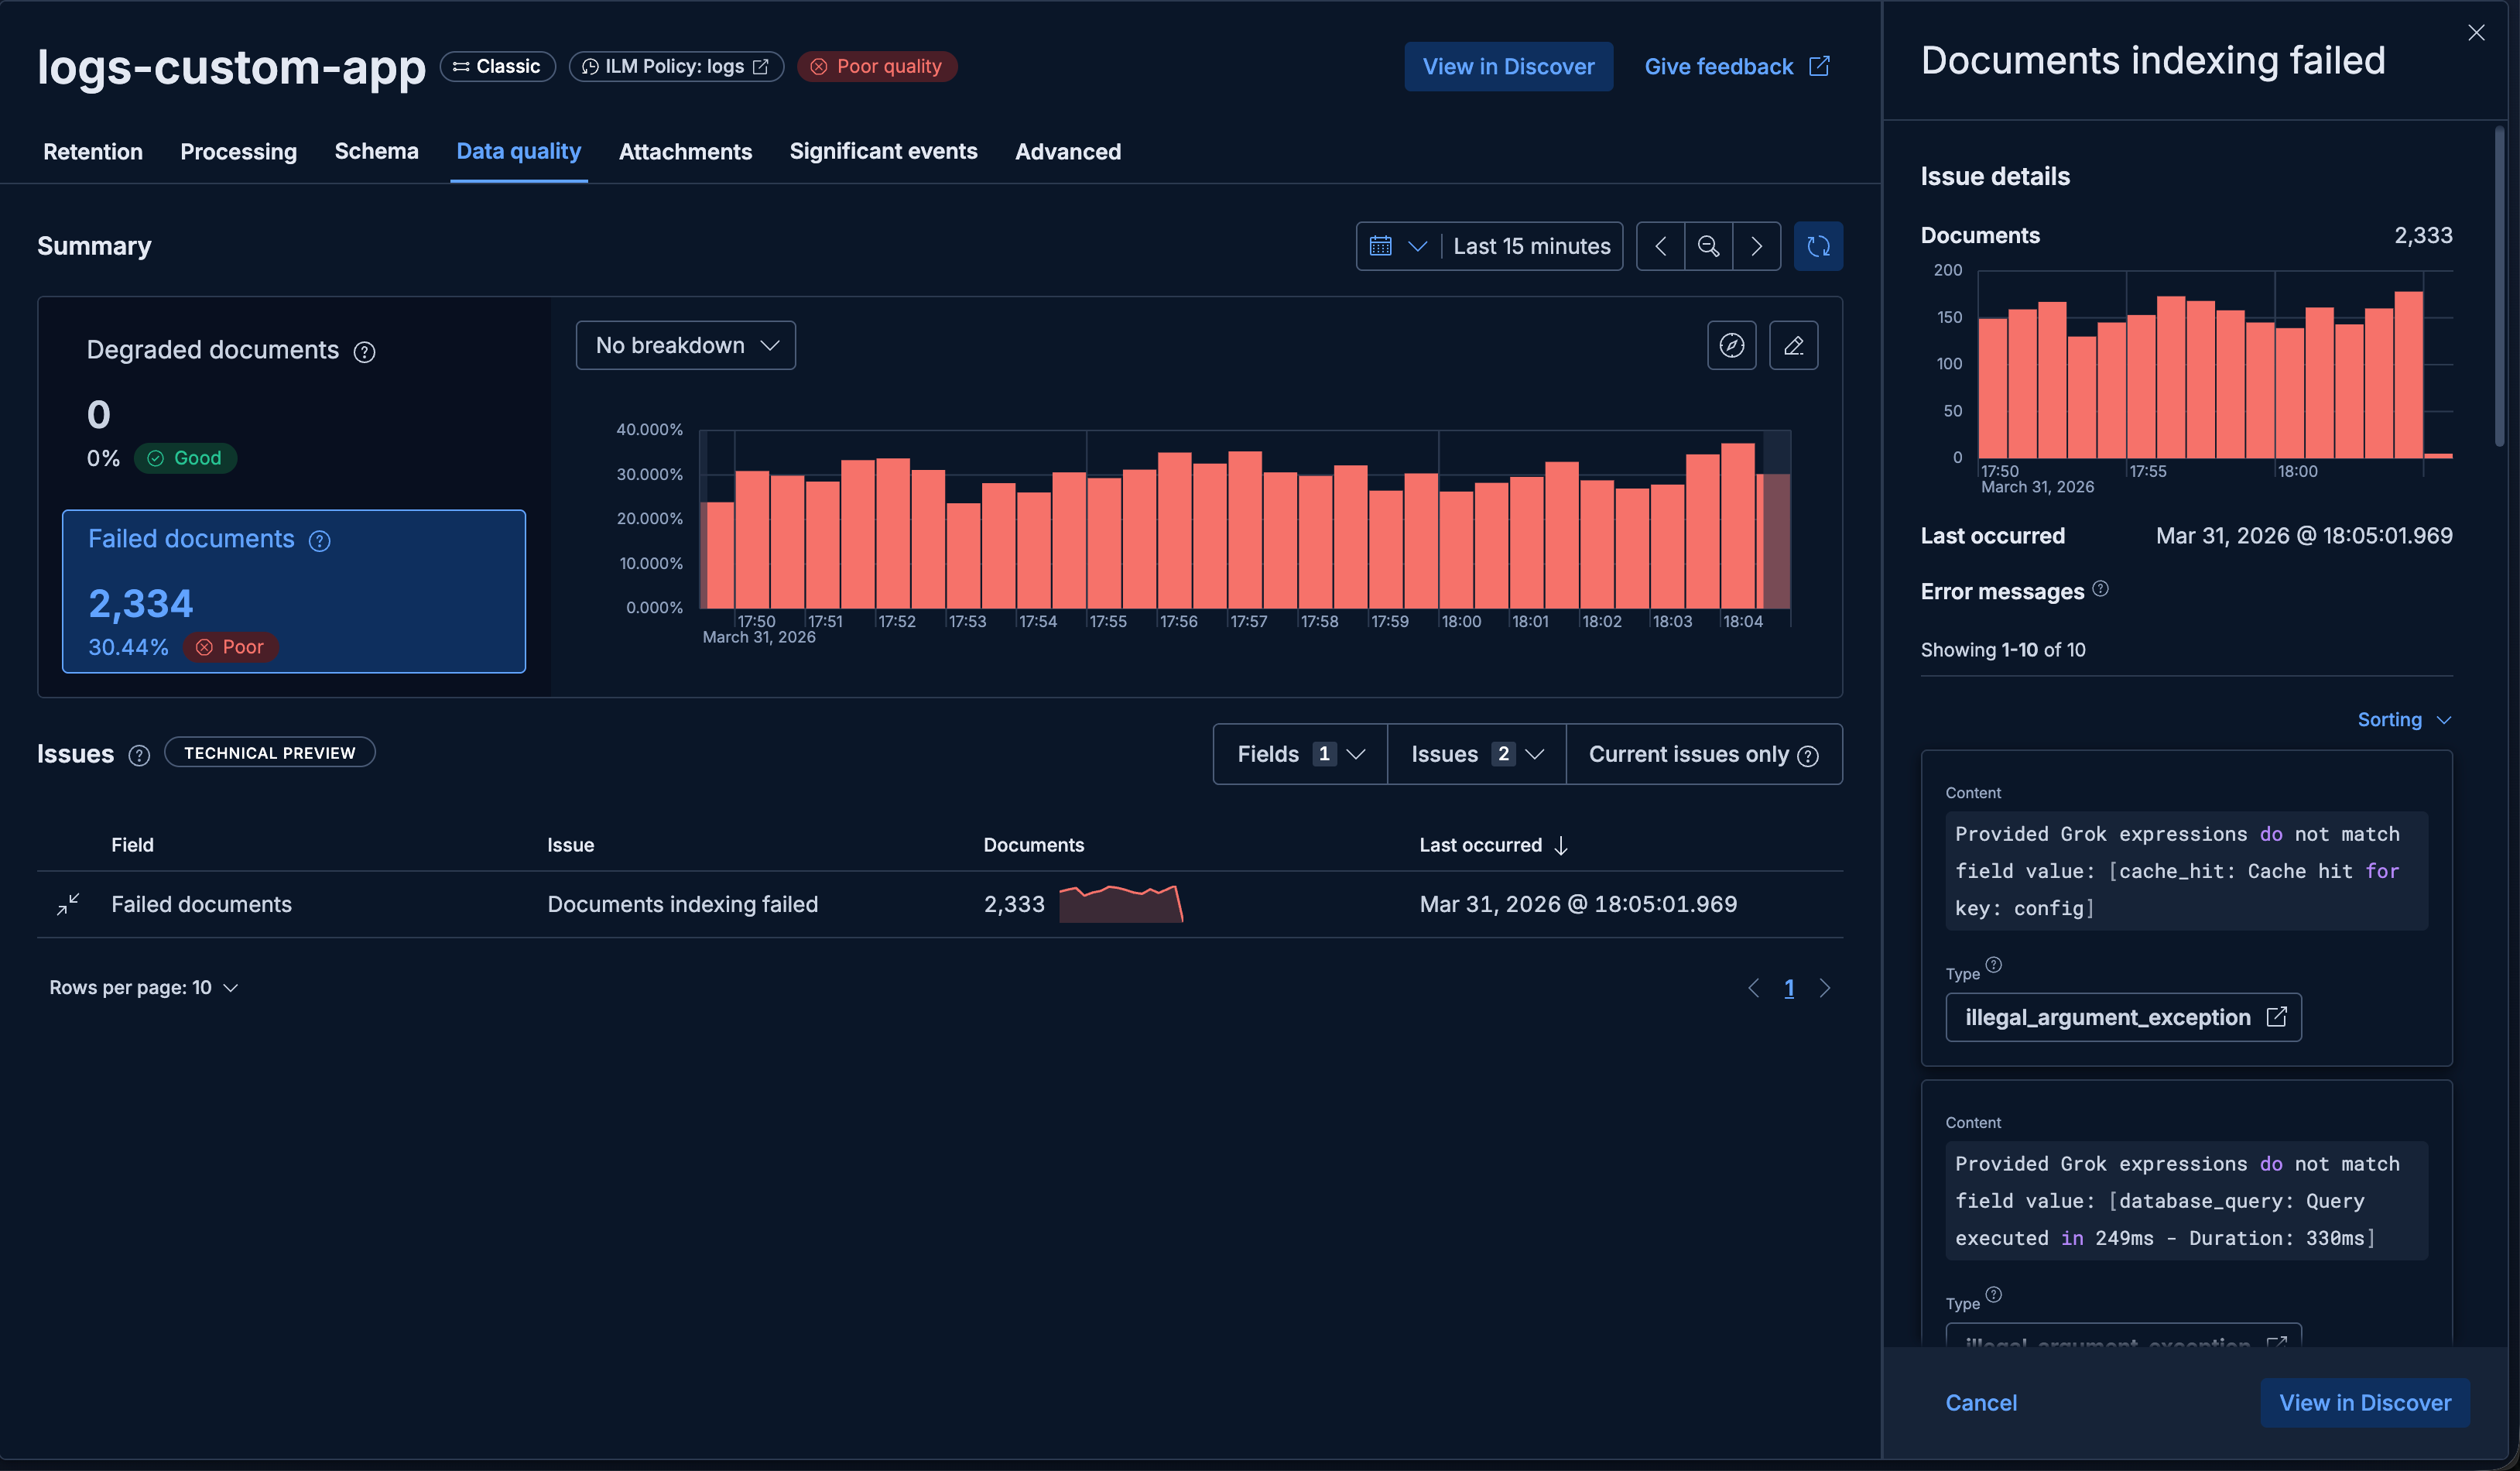
Fixing Elastic Streams processing failures without dropping data
When your Streams ingest pipeline breaks, failed documents land in the failure store, not the floor. Here's how to use those exact failures to fix your pipeline without re-ingesting from the source.