Blogs
Elastic Security Labs empowers security teams across the globe with novel security intelligence research and free to use tools.
Elastic on Defence Cyber Marvel 2026: A Technical overview from the Exercise Floor
An overview of the Elastic Security and AI infrastructure deployed to support the UK Ministry of Defence's flagship cyber exercise, Defence Cyber Marvel 2026.
Elastic Security Integrations Roundup: Q1 2026
Elastic Security Labs announces nine new integrations for Elastic Security spanning cloud security, endpoint visibility, email threat detection, identity and SIEM.
Prioritizing Alerts Triage with Higher-Order Detection Rules
Scaling SOC efficiency through multi-signal correlation and higher-order detection patterns.
Elastic releases detections for the Axios supply chain compromise
Hunting and detection rules for the Elastic-discovered Axios supply chain compromise.
Supercharge Your SOC
Detection Engineering in the Era of AI Agents - The New Frontier.
Streamlining the Security Analyst Experience
Alert Triage, Investigation, and Response with Elastic's Agentic Security Operations Platform.
Security Automation with Elastic Workflows: From Alert to Response
A practical guide to building intelligent, automated security playbooks with Elastic Workflows.
Investigating from the Endpoint Across Your Environment with Elastic Security XDR
This article highlights how Elastic Security XDR unifies endpoint protection with multi-domain security analytics to help analysts trace and contain multi-stage attacks across hybrid and cloud environments.
Linux & Cloud Detection Engineering - TeamPCP Container Attack Scenario
This publication provides a real-world walkthrough of TeamPCP's multi-stage container compromise, demonstrating how Elastic's D4C surfaces runtime signals across each stage of the attack chain.
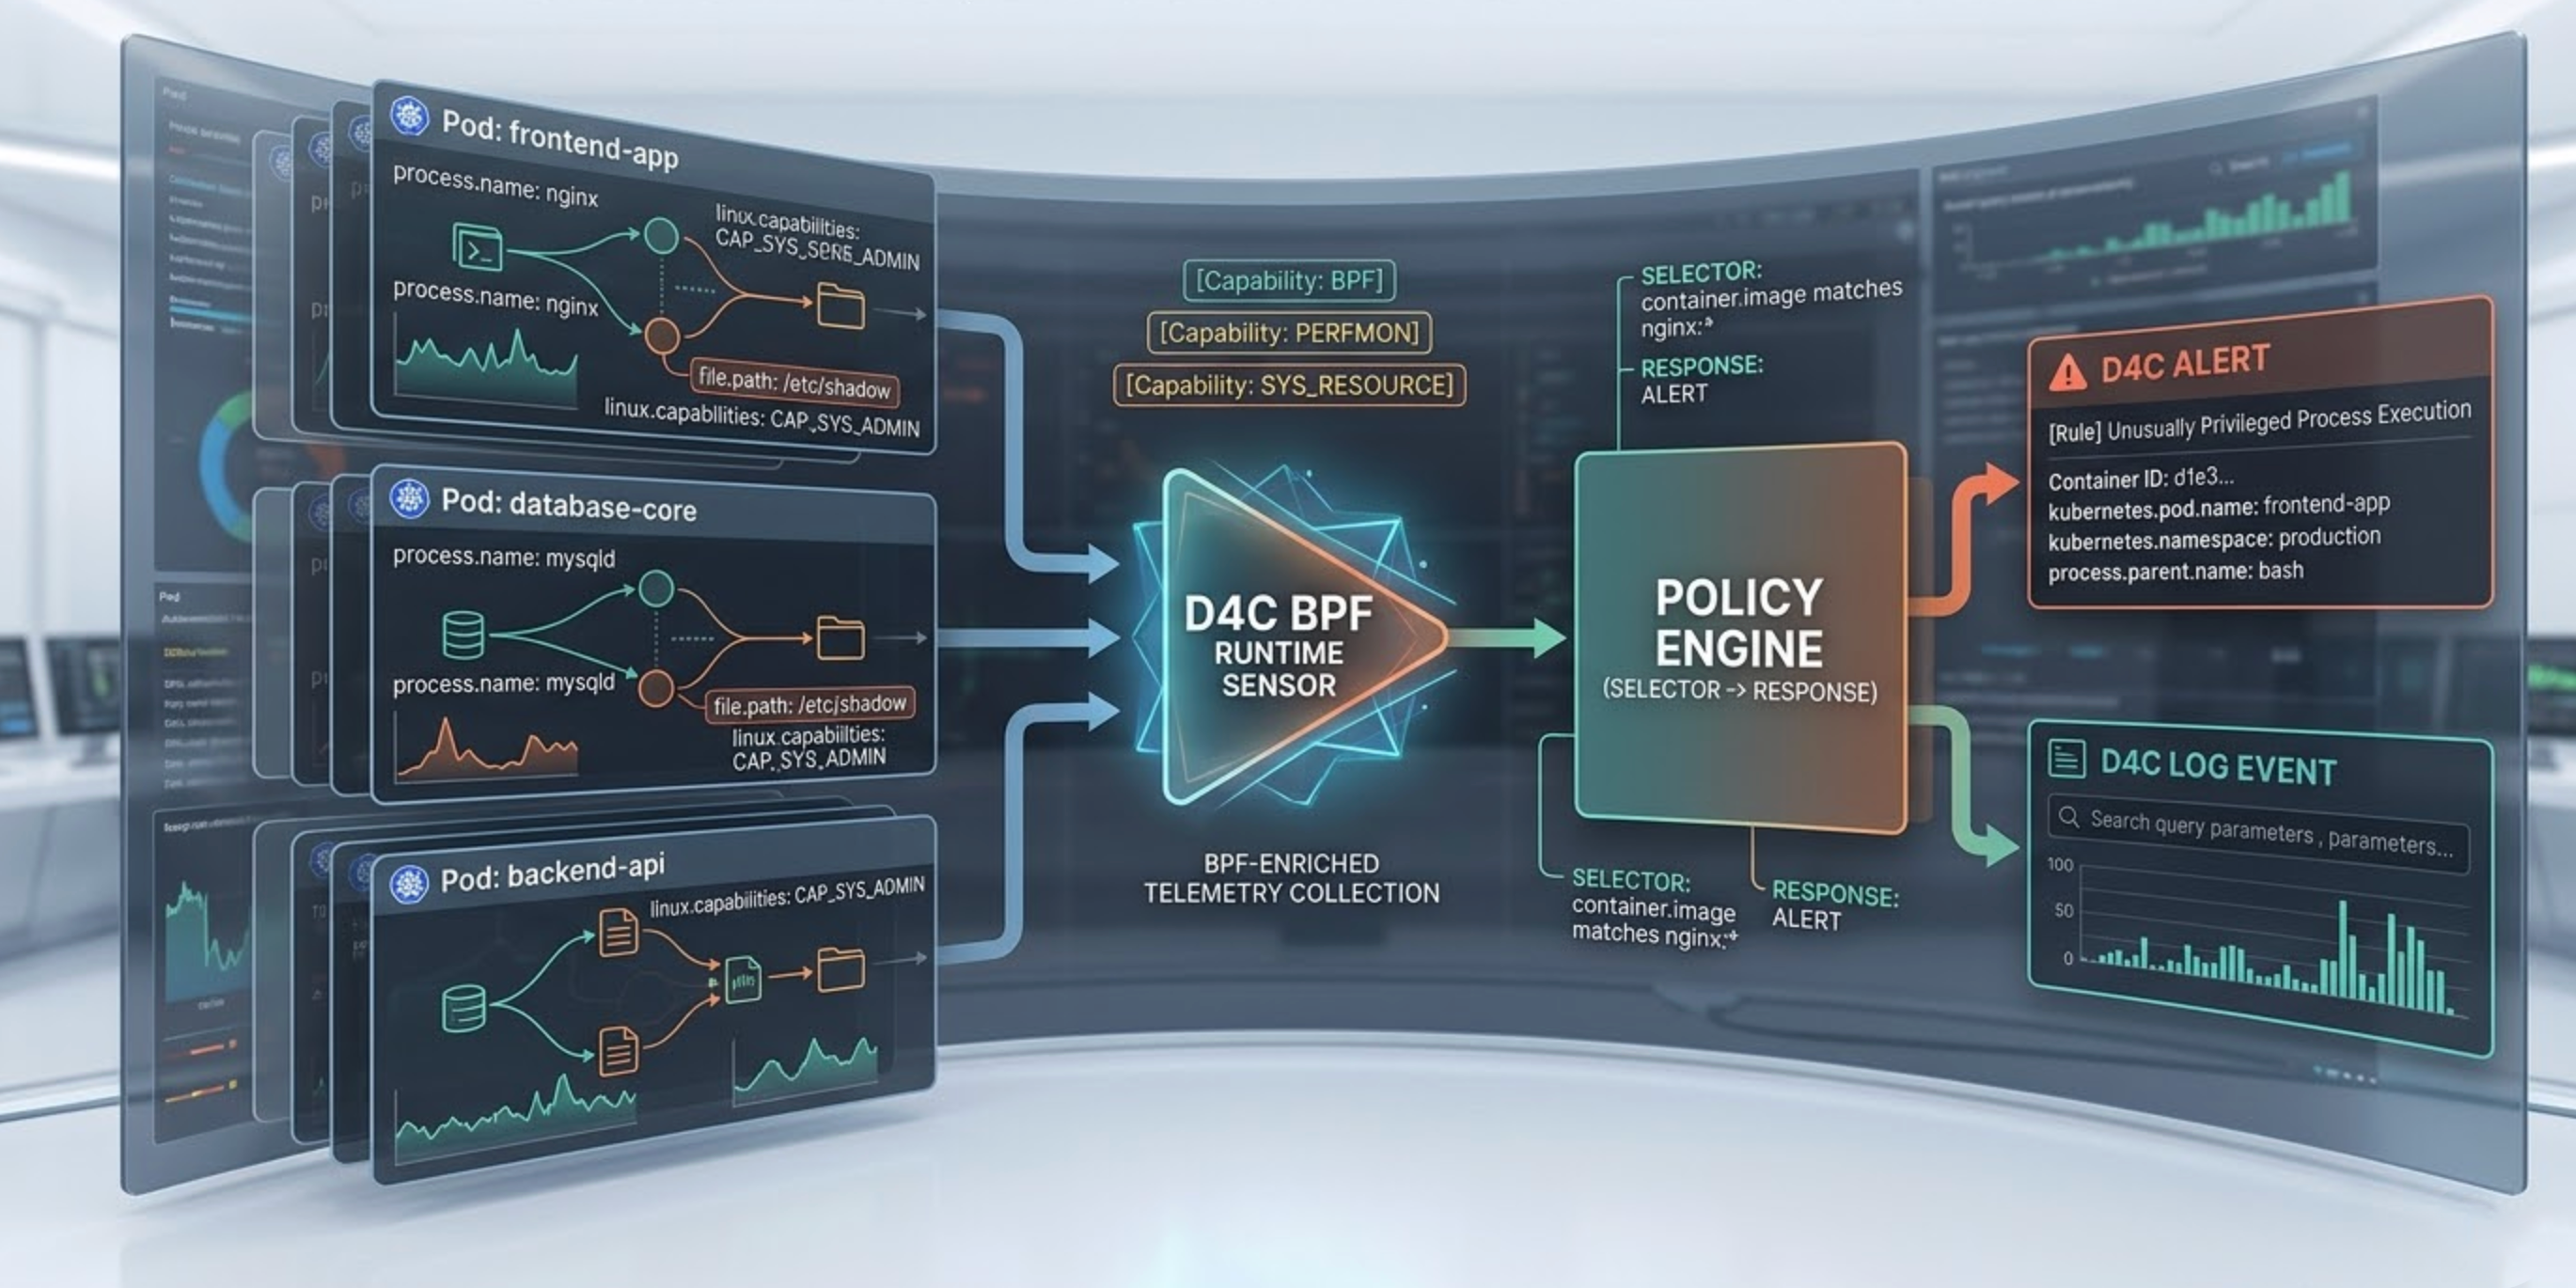
Linux & Cloud Detection Engineering - Getting Started with Defend for Containers (D4C)
This technical resource provides a comprehensive walkthrough of Elastic’s Defend for Containers (D4C) integration, covering Kubernetes-based deployment, the analysis of BPF-enriched runtime telemetry, and the practical application of policy-driven security controls to monitor and alert on activities within containerized Linux environments.
Get started with Elastic Security from your AI agent
Go from zero to a fully populated Elastic Security environment without leaving your IDE, using open source Agent Skills.
Managing Elastic Security Detection Rules with Terraform
Learn to define and deploy Elastic Security detection rules and exceptions using the Elastic Stack Terraform Provider vs detection-rules repository DaC capabilities.