Blogs
Elastic Security Labs empowers security teams across the globe with novel security intelligence research and free to use tools.
From API key to live threat detections in minutes: how Elastic Security ingests Google Threat Intelligence
Find out how Elastic Security ingests Google Threat Intelligence for continuous detection and uses AI-driven workflows to enrich alerts in real time, from API key to live detections in minutes.
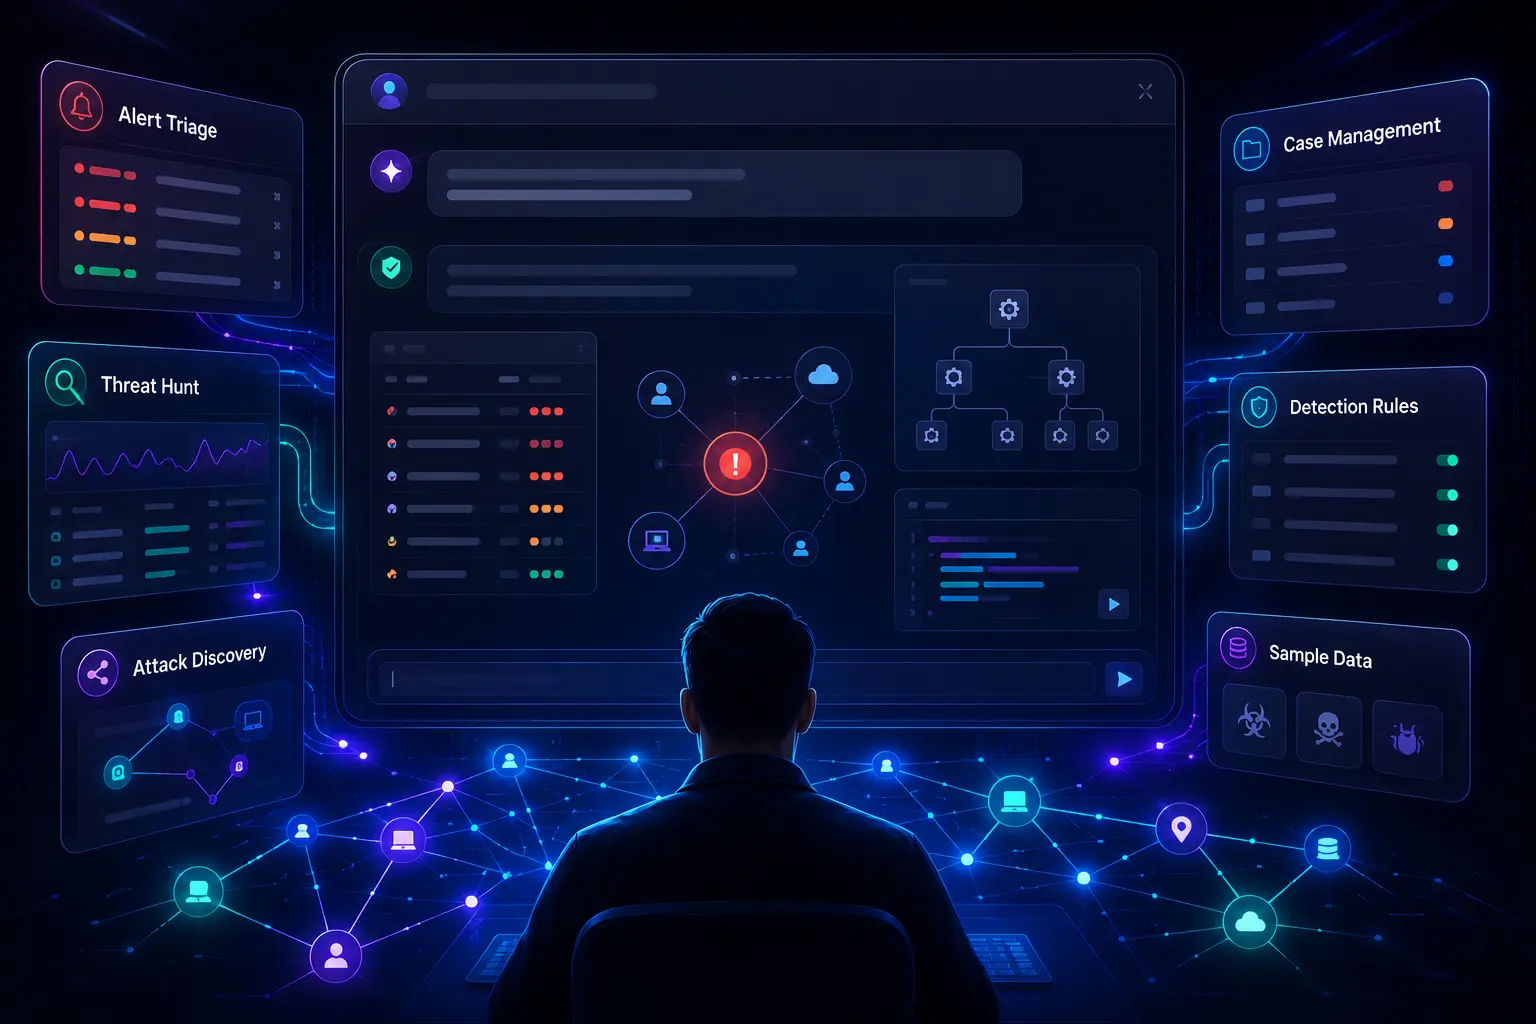
Elastic Security MCP App: Interactive security operations inside your AI Tools
Elastic Security is the first security vendor to ship an interactive UI in AI tools. Triage alerts, hunt threats, correlate attack chains, and open cases, all from inside your AI conversation.
Detecting Web Server Probing & Fuzzing in Traefik with Automated Cloudflare Response
This article shows how a customized Elastic Security ES|QL detection rule can identify web server probing and fuzzing activity in Traefik logs and automatically block the attacking IP via Cloudflare.
Your UEBA is lying to you: Why entity record quality decides everything
Most entity analytics systems are confidently wrong. They track users who do not exist, generate risk scores built on noise, and call it behavioral analytics. Learn why the entities records you don't create matter as much as the ones you do and how a confidence-tiered model changes the game.
AI-generated hunting leads: The hunt starts before you ask the question
Introducing AI-generated hunting leads, proactive, environment-aware threat hypotheses powered by Elastic Entity analytics and integrated AI reasoning.
Know who to watch before the incident finds you
Elastic Security v9.4 introduces Entity Analytics Watchlists, a way to codify what your team already knows about high-risk entities and feed that context directly into risk scoring, without custom pipelines or detection engineering overhead
Elastic Workflows GA: automation where your security data already lives
Elastic Workflows is generally available in 9.4, bringing production-ready security automation with deeper case management integration, human-in-the-loop support, natural language authoring, and more.
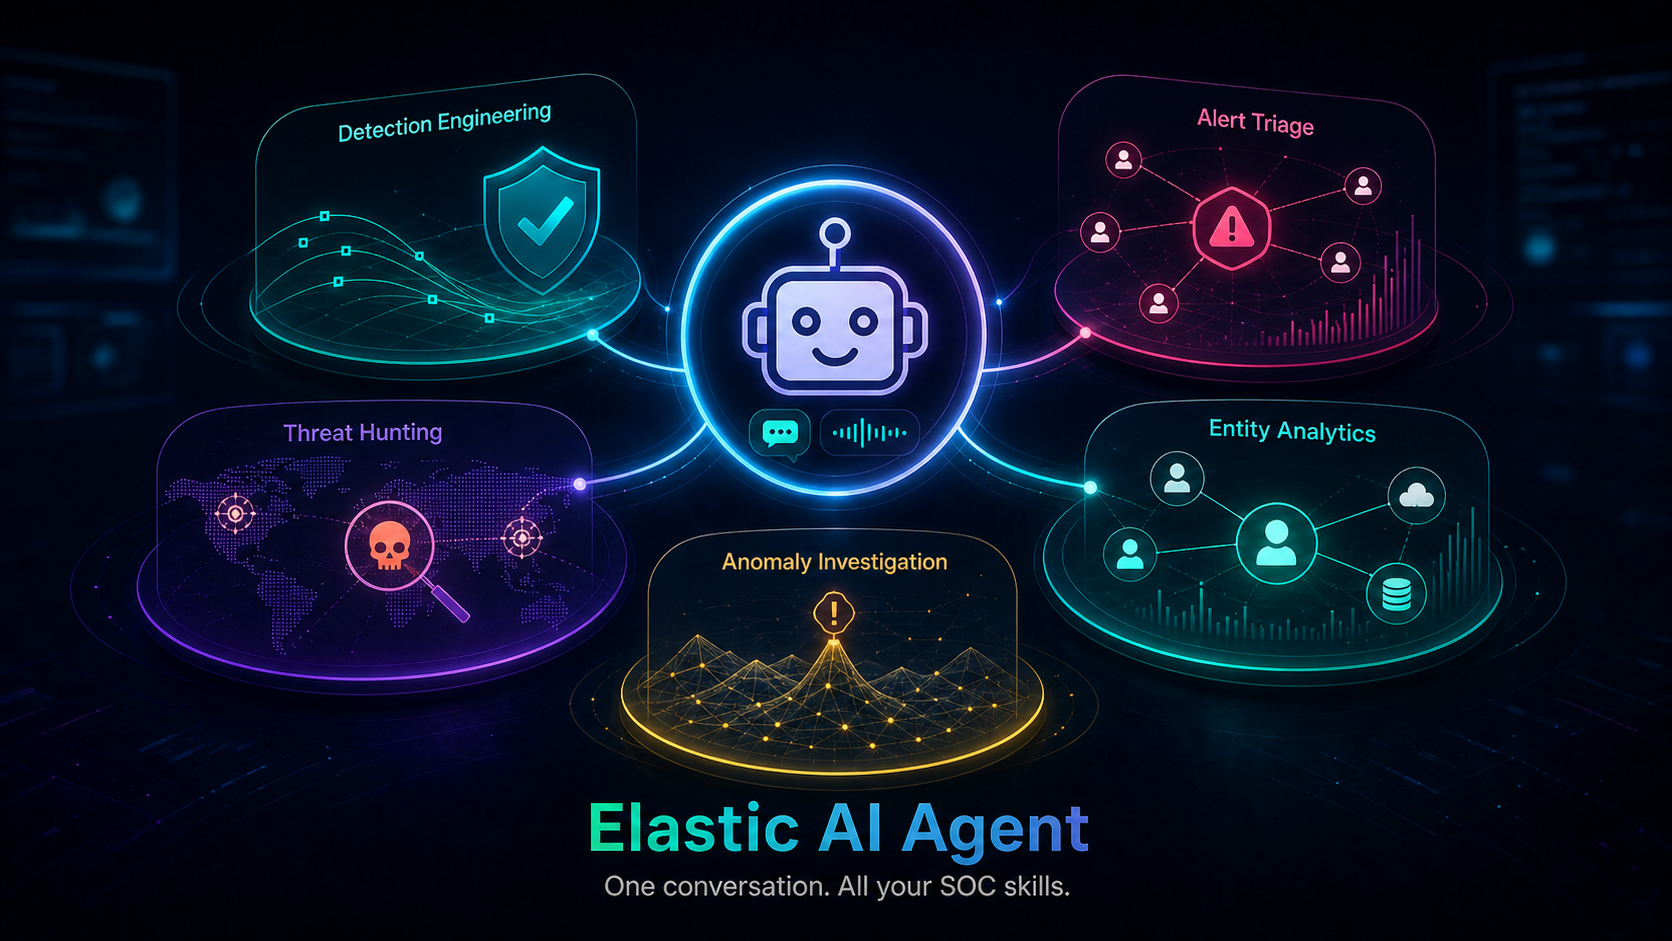
One agent, the right skills: Elastic Security 9.4 brings domain expertise on demand to every SOC workflow
Elastic Security 9.4 introduces skills, modular AI capabilities that teach the Elastic AI Agent how to detect, investigate, and hunt like a specialist. This is how they work, and why they matter for the SOC.
Elastic Conversational Entity Analytics: threat hunting in a single conversation
Conversational Entity Analytics delivers Entity Analytics features as rich inline attachments and Canvas previews into Agent Builder, so you don’t have to leave the conversation.
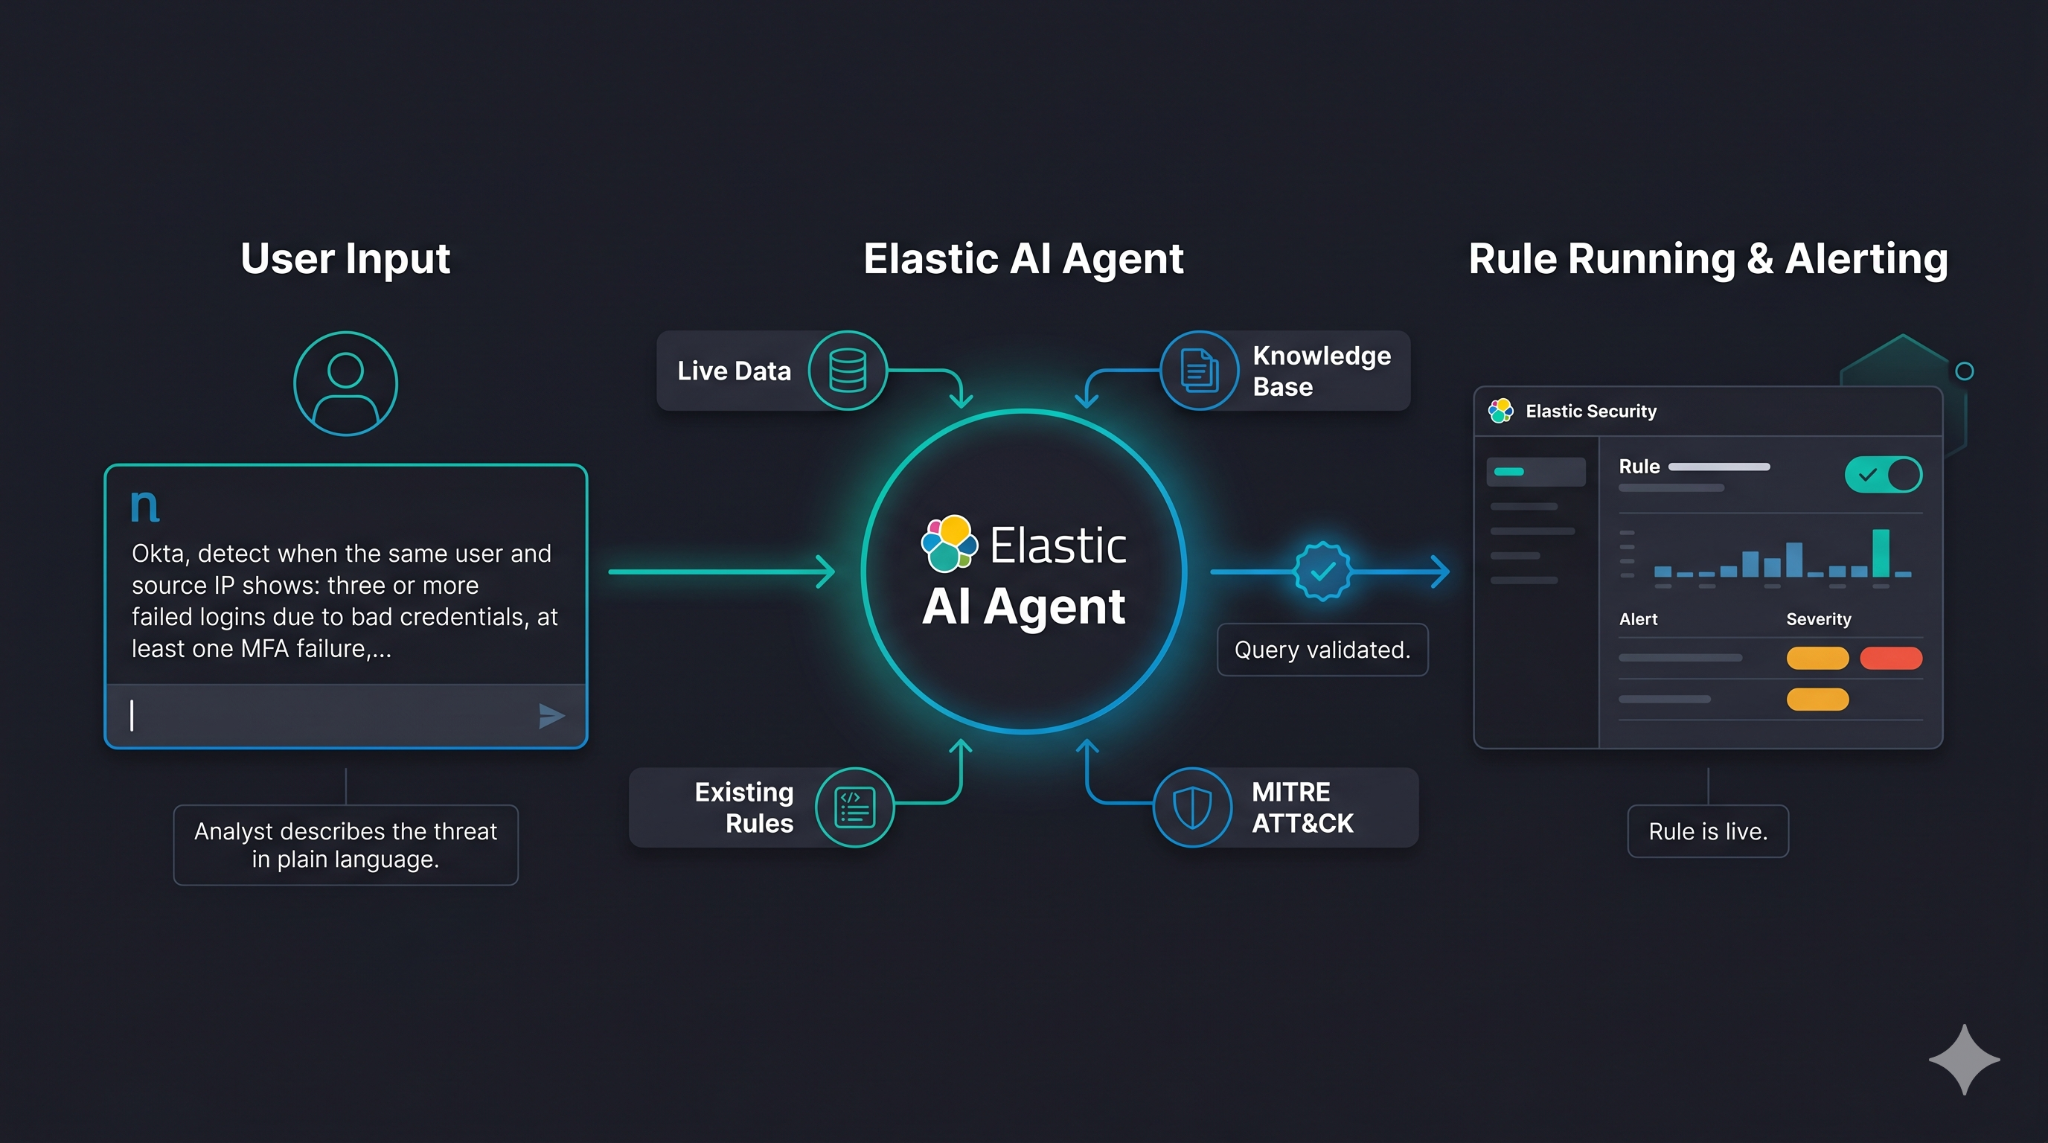
From plain English to production rule: AI-native Elasticsearch ES|QL detection in Elastic Security
Elastic Security now lets analysts describe a threat behavior in plain language and receive a complete, validated Elasticsearch ES|QL detection rule in return, no query expertise required.
DFIR: From alert to root cause using Osquery without leaving Elastic Security
Learn how to perform distributed, real-time Digital Forensics and Incident Response (DFIR) using Osquery and Elastic to investigate threats at scale without relying on disk imaging.
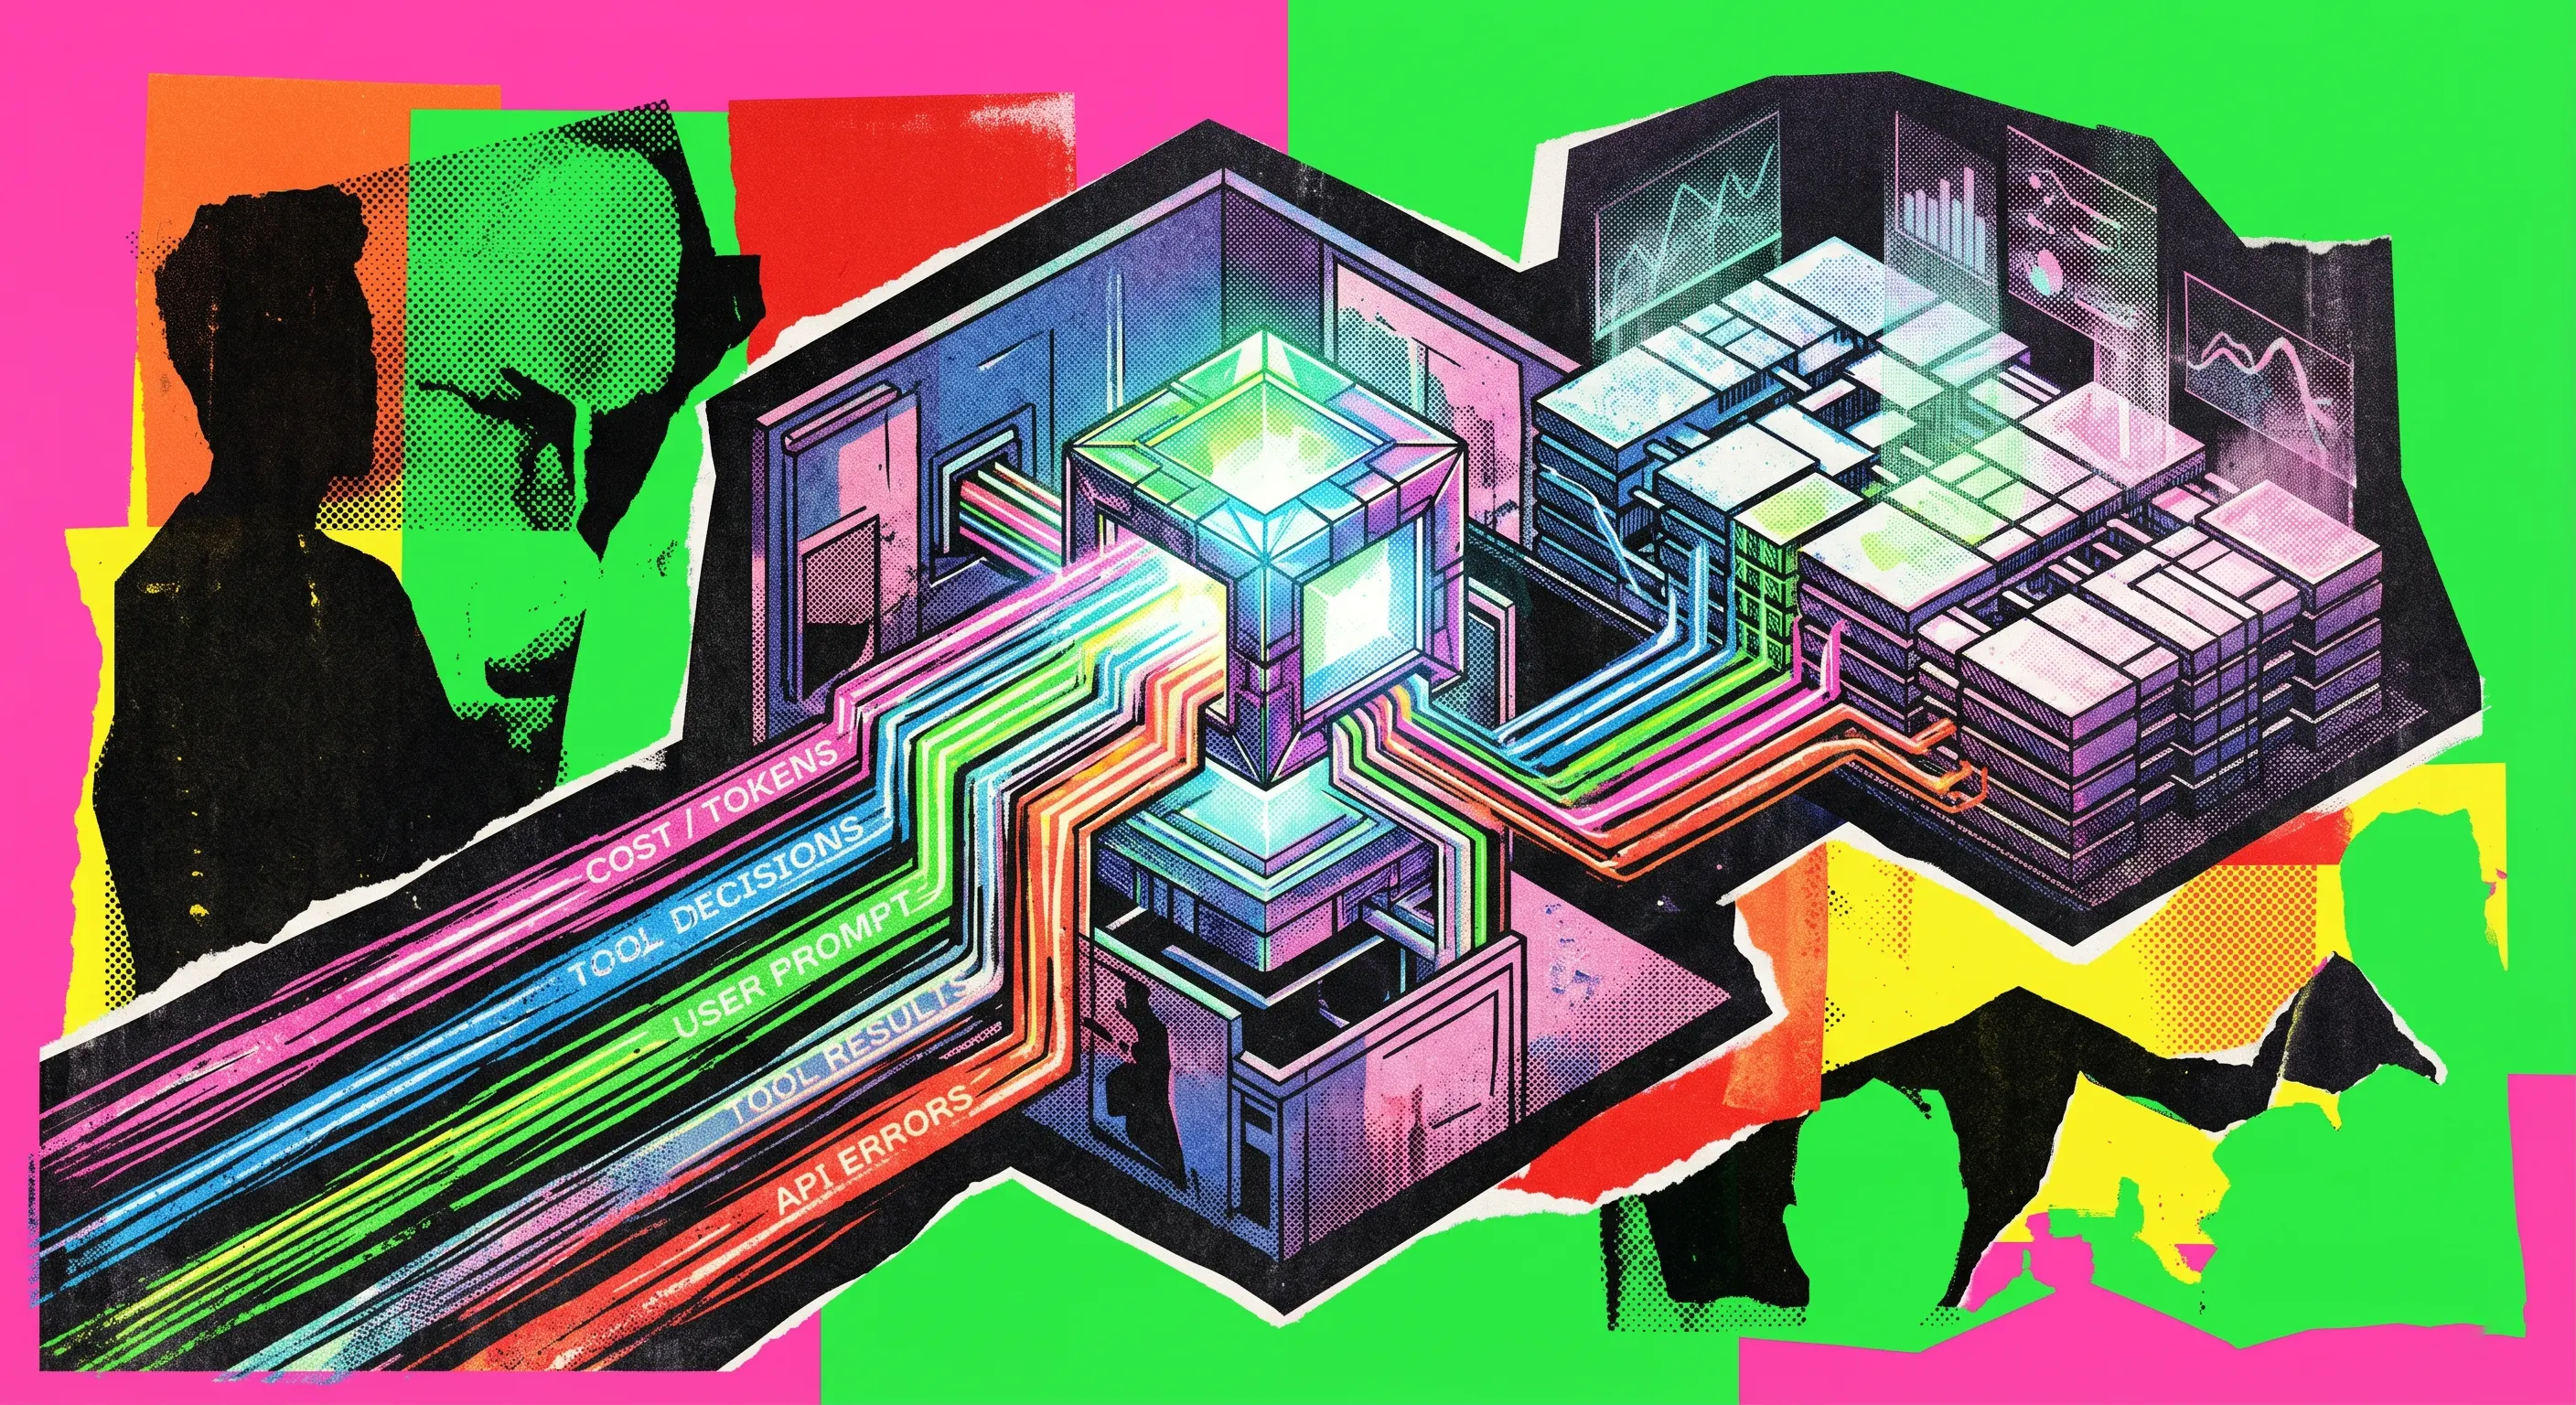
Monitoring Claude Code/Cowork at scale with OTel in Elastic
How Elastic's InfoSec team built a monitoring pipeline for Claude Code and Claude Cowork using their native OTel export capabilities and Elastic's OTel ingestion infrastructure.