
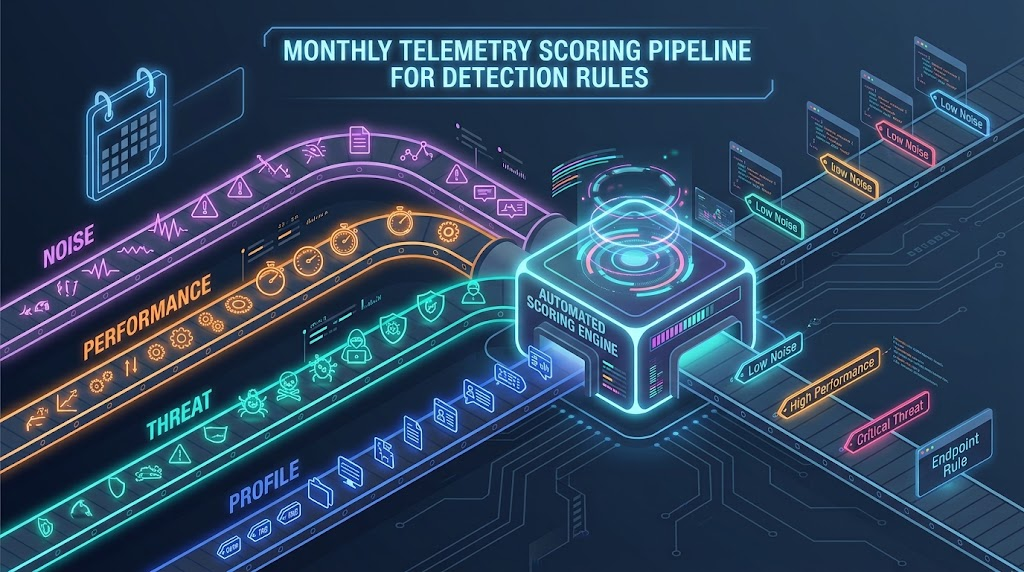
Behind the tags: How Elastic SIEM grades 1,781 detection rules on noise, speed, and threat coverage
This article explains how Elastic SIEM uses a monthly automated telemetry pipeline to score prebuilt detection rules across noise, performance, threat, and profile dimensions, helping security teams decide which rules to enable first.
SOC case management and detection rule history in Elastic Security
Elastic Security now tracks every detection rule change with one-click rollback and makes case data queryable out of the box, so SOC teams get audit trails and reporting without configuring anything.
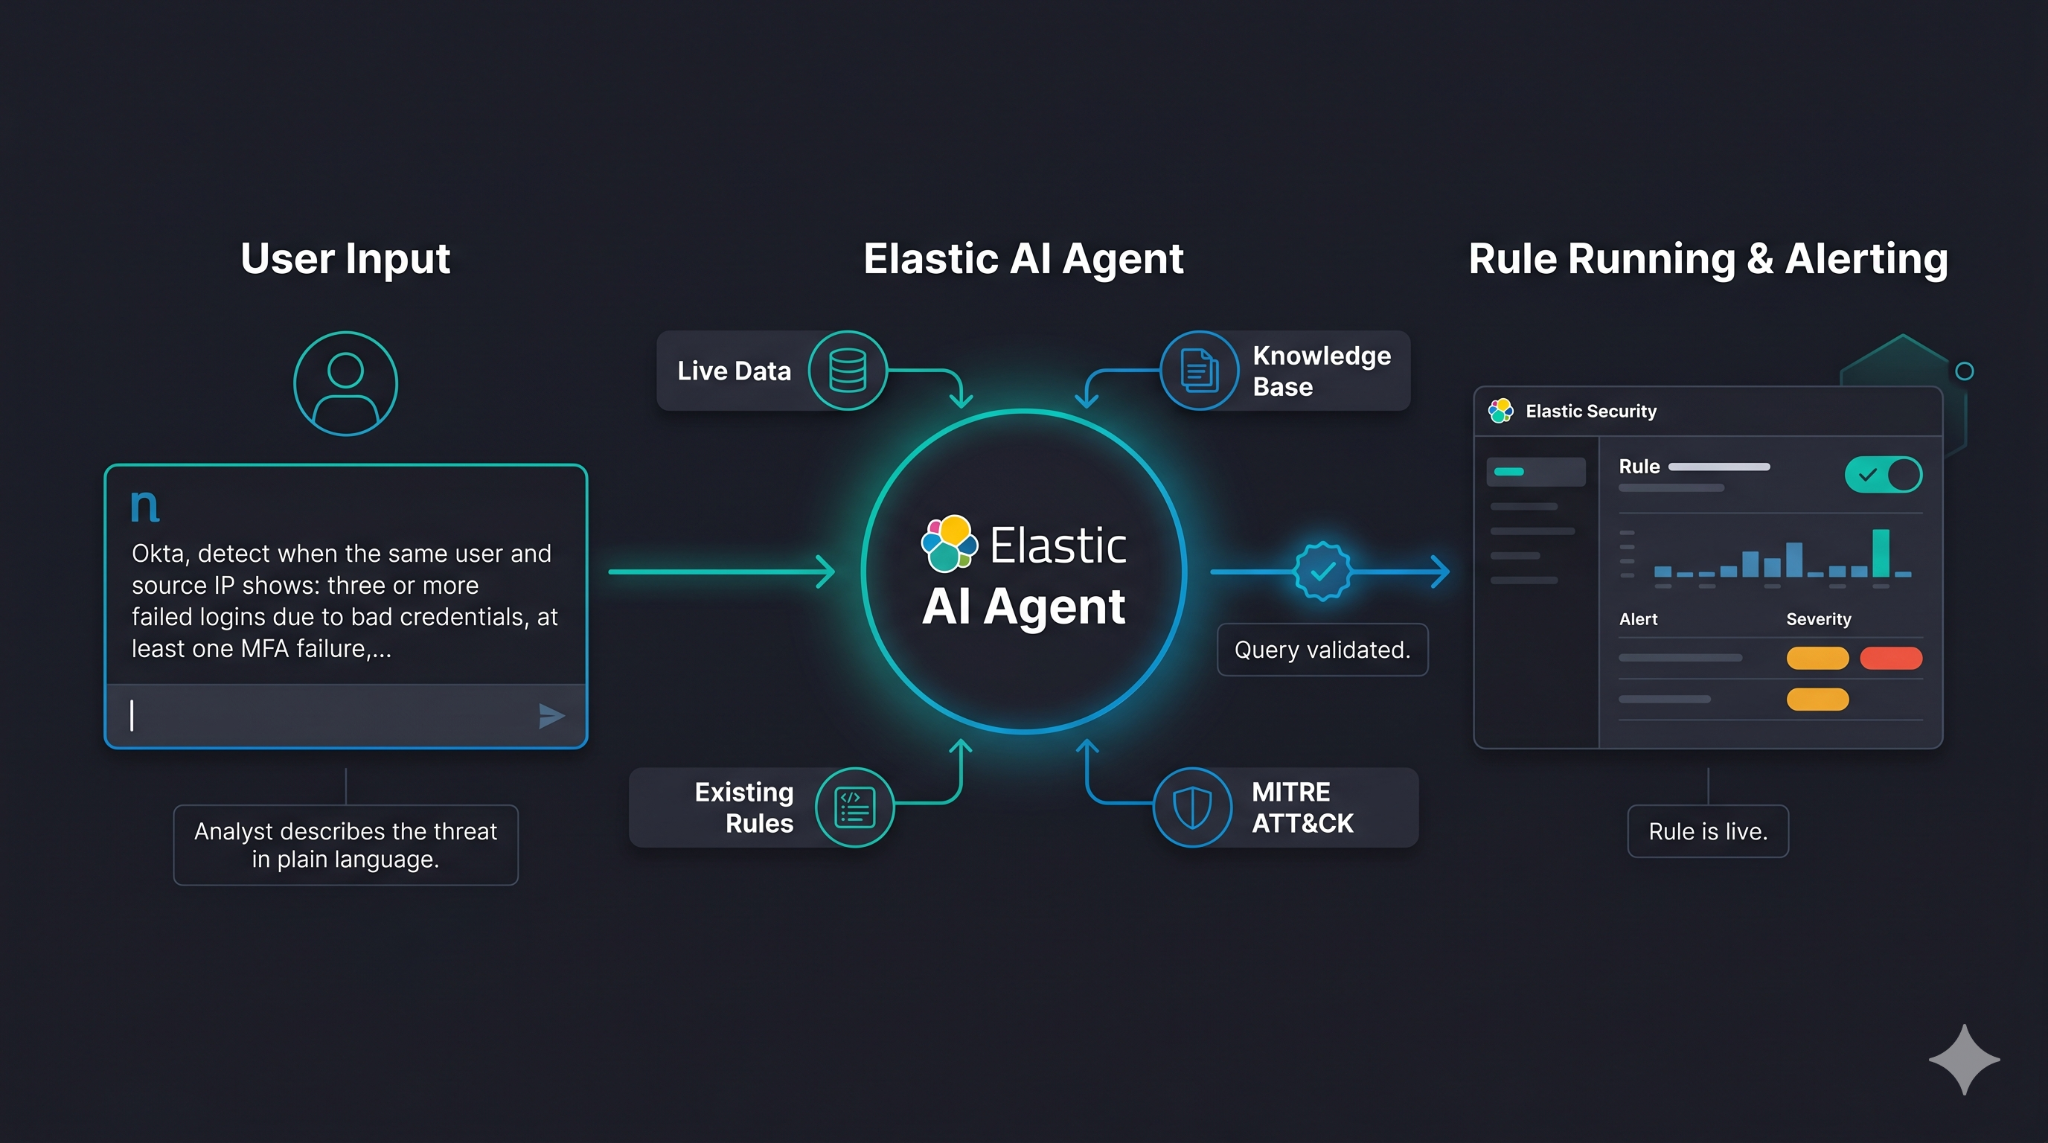
From plain English to production rule: AI-native Elasticsearch ES|QL detection in Elastic Security
Elastic Security now lets analysts describe a threat behavior in plain language and receive a complete, validated Elasticsearch ES|QL detection rule in return, no query expertise required.
Managing Elastic Security Detection Rules with Terraform
Learn to define and deploy Elastic Security detection rules and exceptions using the Elastic Stack Terraform Provider vs detection-rules repository DaC capabilities.
The Engineer's Guide to Elastic Detections as Code
This post details the latest evolution of Elastic Security's Detections as Code (DaC) framework, including its development timeline, current feature highlights, and tailored implementation examples.