Data access: the hidden cost of security vendor lock-in
Getting data into a security platform is always easy; getting it back out is where vendors add cost, extra tooling, and latency, and it is the part of the evaluation most teams overlook.
Not another Log4Shell: inside the Log4j 2 deserialization allowlist bypass
We reproduced this java deserialization vulnerability against official Log4j 2.26.1 JARs. Getting to command execution took two more things that Log4j itself does not ship. Here is how the bypass works, which versions carry it, and what to hunt for.
SOC case management and detection rule history in Elastic Security
Elastic Security now tracks every detection rule change with one-click rollback and makes case data queryable out of the box, so SOC teams get audit trails and reporting without configuring anything.
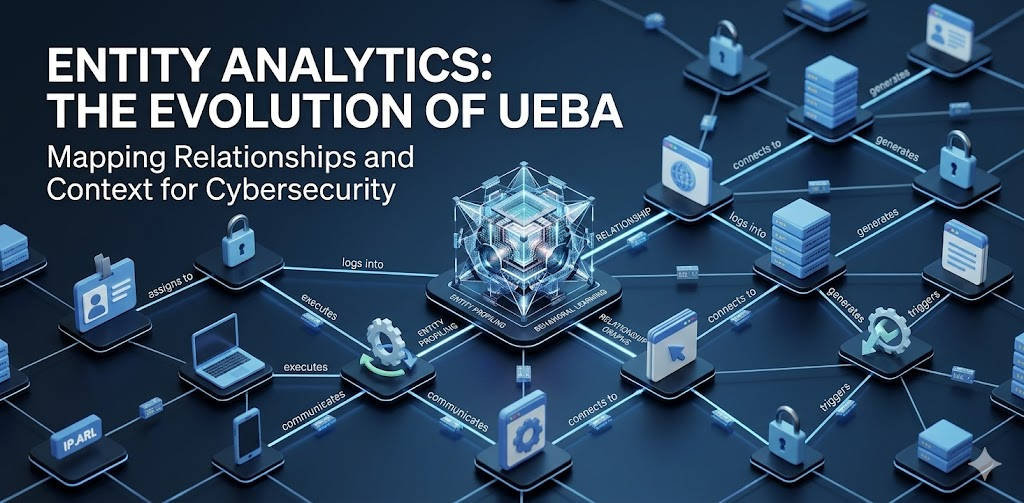
Your UEBA is lying to you: Why entity record quality decides everything
Most entity analytics systems are confidently wrong. They track users who do not exist, generate risk scores built on noise, and call it behavioral analytics. Learn why the entities records you don't create matter as much as the ones you do and how a confidence-tiered model changes the game.
Know who to watch before the incident finds you
Elastic Security v9.4 introduces Entity Analytics Watchlists, a way to codify what your team already knows about high-risk entities and feed that context directly into risk scoring, without custom pipelines or detection engineering overhead
Streamlining the Security Analyst Experience
Alert Triage, Investigation, and Response with Elastic's Agentic Security Operations Platform.
Automating detection tuning requests with Kibana cases
Learn how to automate detection rule tuning requests in Elastic Security. This guide shows how to add custom fields to Cases, create a rule to detect tuning needs, and use a webhook to create a frictionless feedback loop between analysts and detection engineers.
TOR Exit Node Monitoring Overview
Learn how to monitor your enterprise for TOR exit node activity.
Elastic Security opens public detection rules repo
Elastic Security has opened its detection rules repository to the world. We will develop rules in the open alongside the community, and we’re welcoming your community-driven detections. This is an opportunity to share collective security knowledge.