Not another Log4Shell: inside the Log4j 2 deserialization allowlist bypass
We reproduced this java deserialization vulnerability against official Log4j 2.26.1 JARs. Getting to command execution took two more things that Log4j itself does not ship. Here is how the bypass works, which versions carry it, and what to hunt for.
Detecting Web Server Probing & Fuzzing in Traefik with Automated Cloudflare Response
This article shows how a customized Elastic Security ES|QL detection rule can identify web server probing and fuzzing activity in Traefik logs and automatically block the attacking IP via Cloudflare.
Prioritizing Alerts Triage with Higher-Order Detection Rules
Scaling SOC efficiency through multi-signal correlation and higher-order detection patterns.
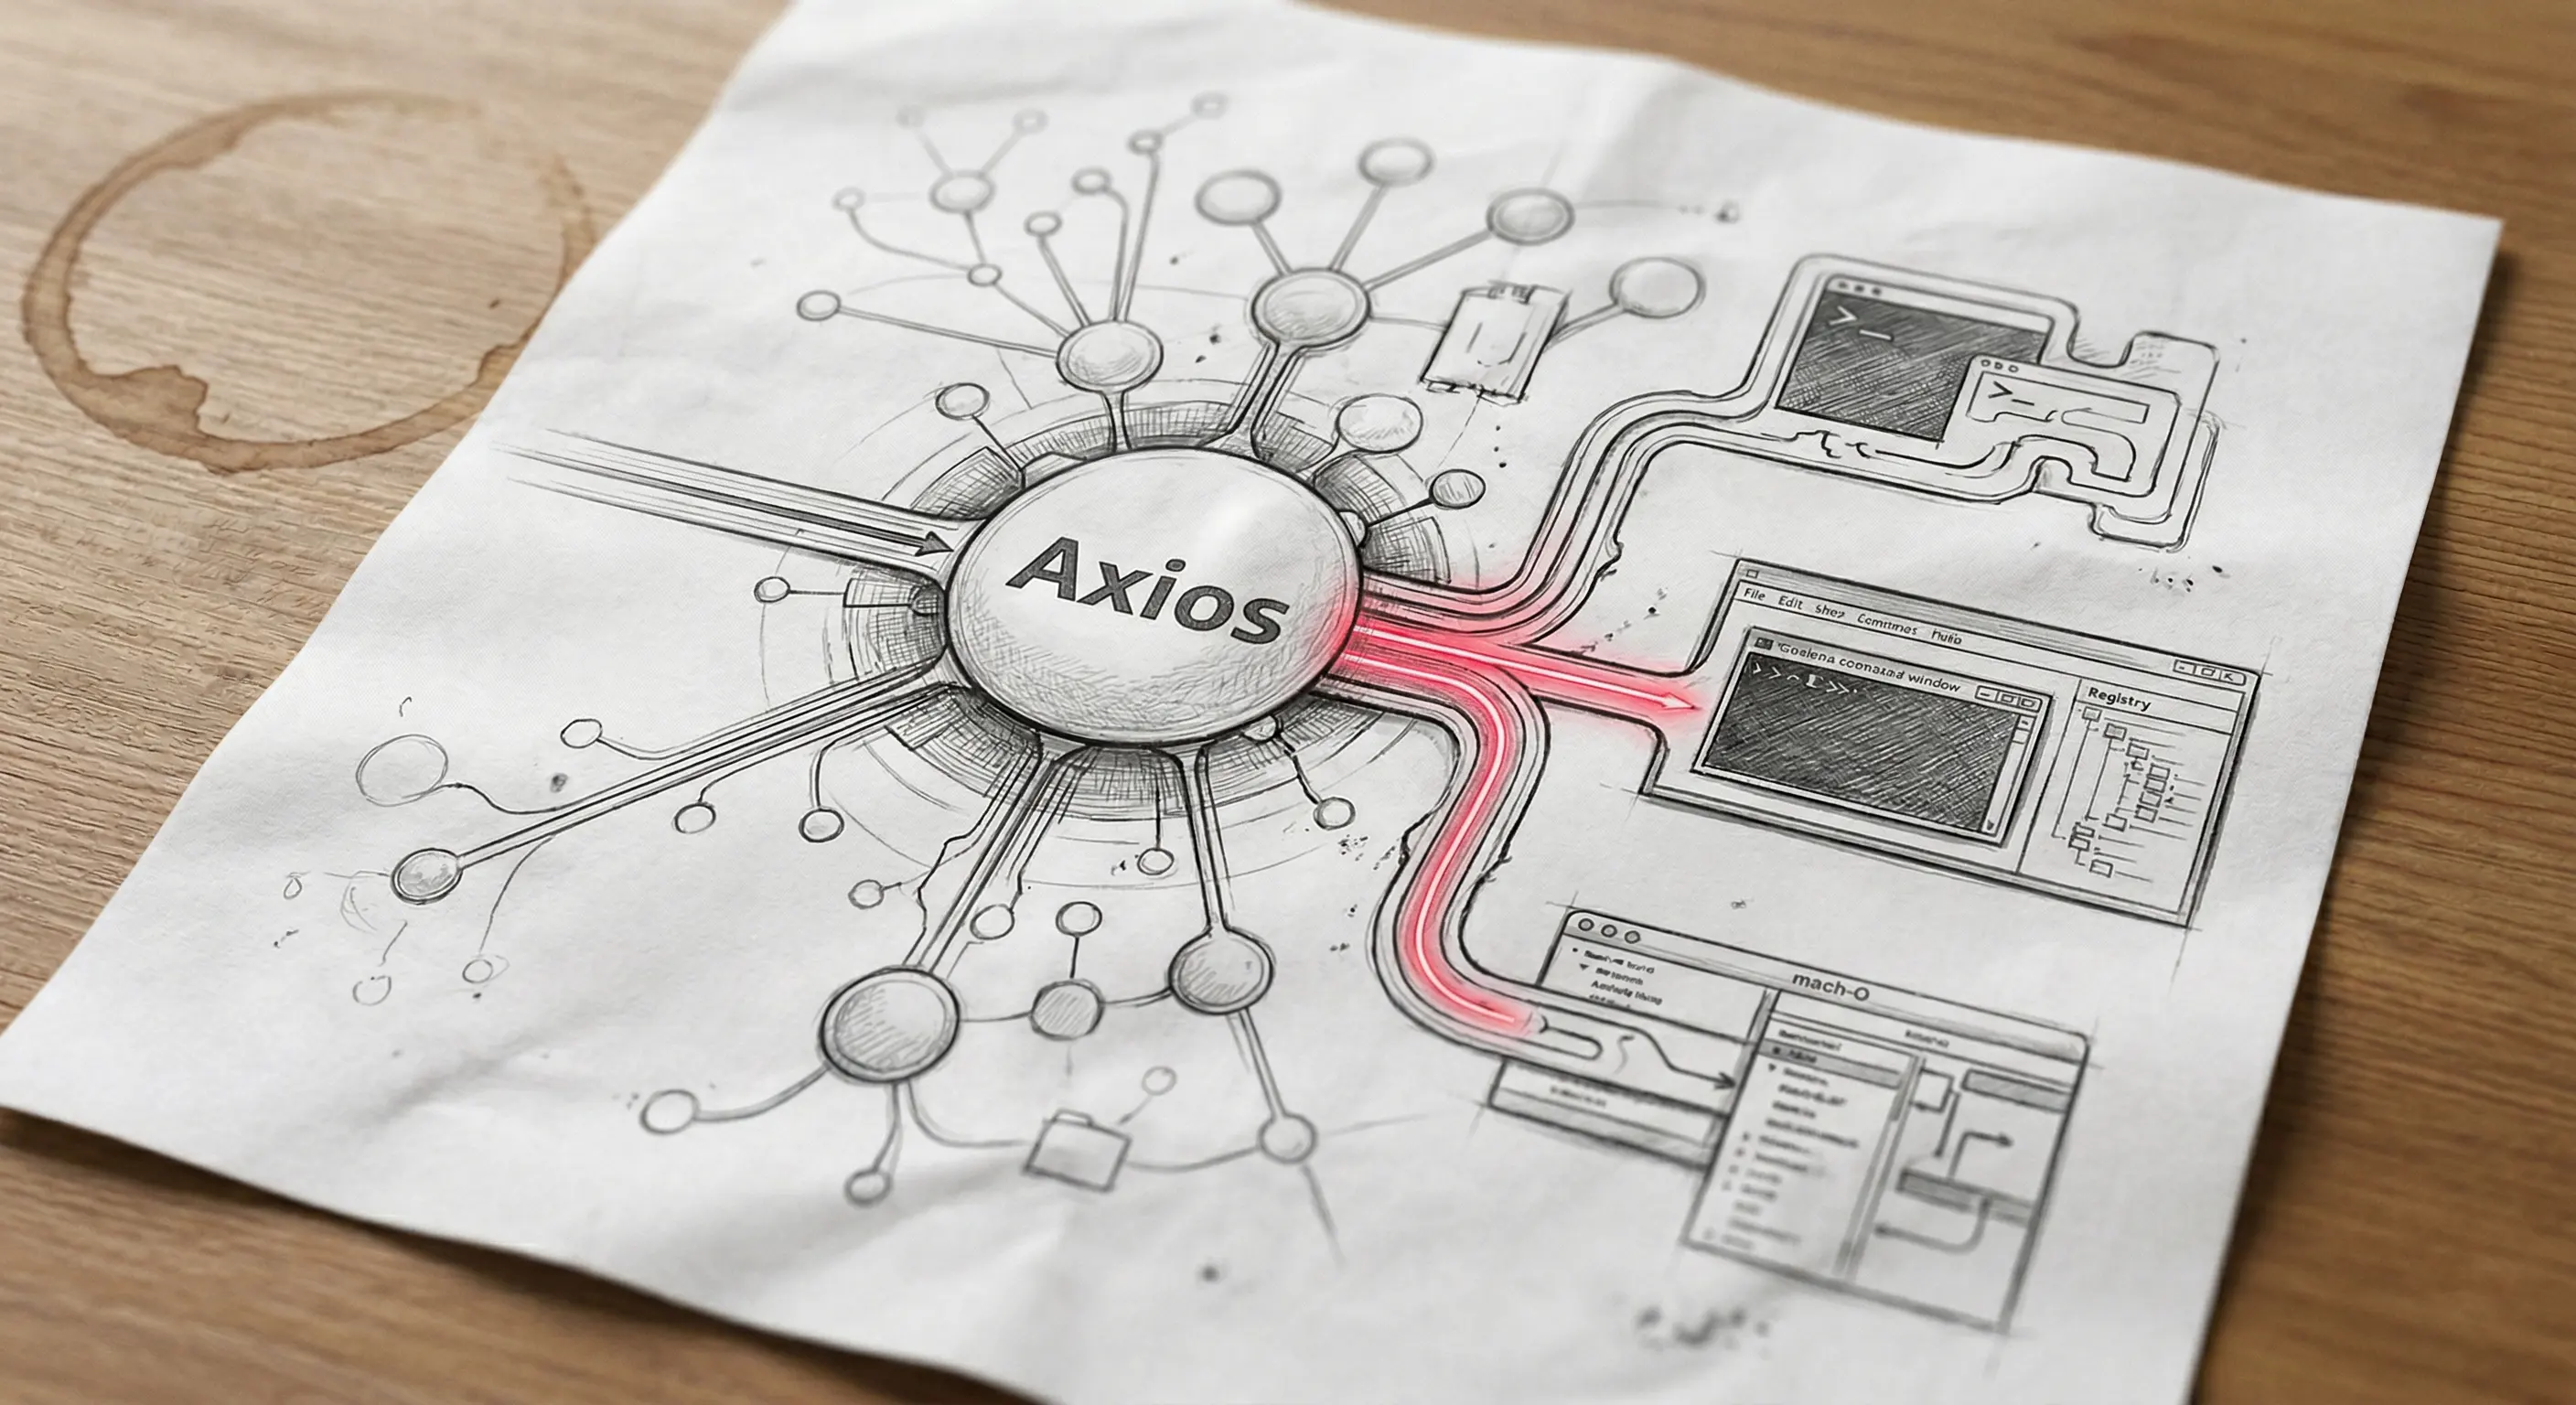
Elastic releases detections for the Axios supply chain compromise
Hunting and detection rules for the Elastic-discovered Axios supply chain compromise.
SolarWinds Web Help Desk Exploitation - February 2026
Elastic Security detection and prevention capabilities for the recently-disclosed SolarWinds Web Help Desk vulnerabilities.
From Hypothesis to Action: Proactive Threat Hunting with Elastic Security
Elastic Security is designed to enable hypothesis-driven threat hunting at speed and scale. By unifying security telemetry and enabling analytics across clusters, threat hunters can ask complex questions across all their data, correlate signals, and validate hypotheses quickly without manual data stitching.
Elevate Your Threat Hunting with Elastic
Elastic is releasing a threat hunting package designed to aid defenders with proactive detection queries to identify actor-agnostic intrusions.
Storm on the Horizon: Inside the AJCloud IoT Ecosystem
Wi-Fi cameras are popular due to their affordability and convenience but often have security vulnerabilities that can be exploited.
Linux detection engineering with Auditd
In this article, learn more about using Auditd and Auditd Manager for detection engineering.
Exploring the Future of Security with ChatGPT
Recently, OpenAI announced APIs for engineers to integrate ChatGPT and Whisper models into their apps and products. For some time, engineers could use the REST API calls for older models and otherwise use the ChatGPT interface through their website.
Identifying beaconing malware using Elastic
In this blog, we walk users through identifying beaconing malware in their environment using our beaconing identification framework.
Hunting for Lateral Movement using Event Query Language
Elastic Event Query Language (EQL) correlation capabilities enable practitioners to capture complex behavior for adversary Lateral Movement techniques. Learn how to detect a variety of such techniques in this blog post.