Blogs
Elastic Security Labs empowers security teams across the globe with novel security intelligence research and free to use tools.
Patch diff to SYSTEM
Leveraging LLMs and patch diffing, this research details a Use-After-Free vulnerability in Windows DWM, demonstrating a reliable exploit that achieves escalation from low-privileged user permissions to SYSTEM.
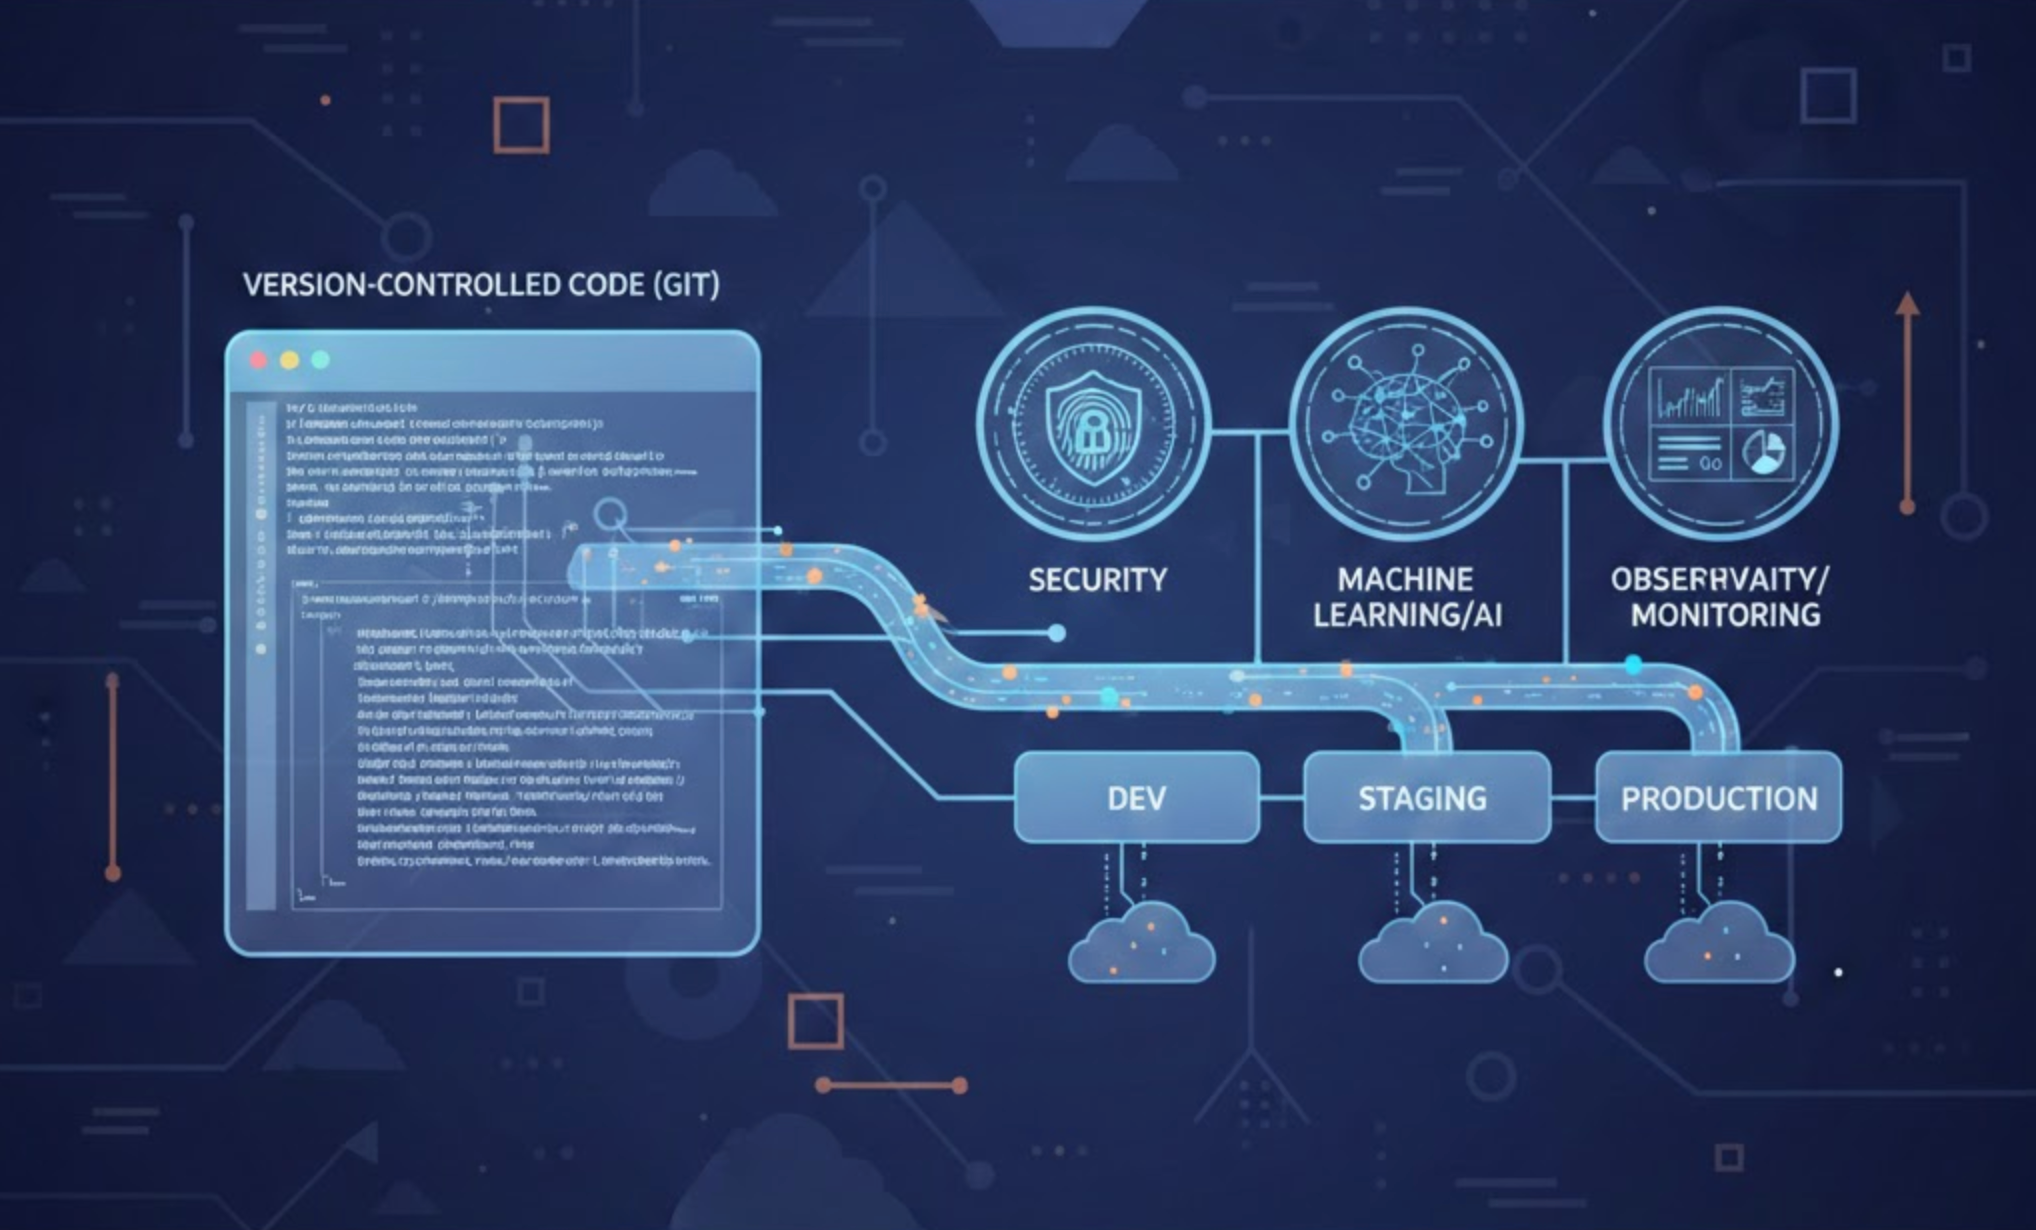
Manage your Elastic security stack as code with the Elastic Stack Terraform provider
From detection rules to AI connectors - the latest Terraform provider releases bring security, observability, and ML capabilities to your infrastructure-as-code workflows.
Make The Most of Network Firewall Logs with Elastic Security
Make the most of your firewall logs. In Part 1 of our series, learn how to ingest and parse logs from any firewall with Elastic Agent and use the Network Page to visually explore your network traffic for instant insights.
Speeding APT Attack Confirmation with Attack Discovery, Workflows, and Agent Builder
This article walks through how Elastic Security's Attack Discovery, combined with Workflows and Agent Builder, can automatically detect, correlate, and confirm APT-level attacks like Chrysalis while reducing analyst response time from hours to minutes.
SolarWinds Web Help Desk Exploitation - February 2026
Elastic Security detection and prevention capabilities for the recently-disclosed SolarWinds Web Help Desk vulnerabilities.
DYNOWIPER: Destructive Malware Targeting Poland's Energy Sector
Learn how Elastic Defend's ransomware protection successfully detects and prevents DYNOWIPER execution using canary file monitoring.
Automating GOAD and Live Malware Labs
Stop building labs by hand. Automate the deployment of a fully instrumented Purple Team range using Ludus and Elastic Security. Spin up infrastructure, execute attacks, and validate detection rules in a single, repeatable workflow.
The Engineer's Guide to Elastic Detections as Code
This post details the latest evolution of Elastic Security's Detections as Code (DaC) framework, including its development timeline, current feature highlights, and tailored implementation examples.
From Alert Fatigue to Agentic Response: How Workflows and Agent Builder Close the Loop
Attempting to chase individual alerts is a losing strategy. To succeed, we have to move beyond simple automation scripts and into the era of Agentic AI.
From Qradar to Elastic: Automate your Detection Rule Migration
Today, we are excited to announce a major expansion to our Automatic Migration feature that changes that narrative. In Elastic Security 9.3, we are introducing Automatic Migration support for QRadar detection rules (now in Tech Preview), joining our existing Splunk translation capabilities to further expedite your journey to Elastic Security. Let's take a closer look at what's supported.
How Elastic Infosec Optimizes Defend for Cost and Performance
This article details the internal Elastic Infosec team's process to optimize our endpoint data collection using Event Filtering and Advanced Policy Settings in Elastic Defend.
From Hypothesis to Action: Proactive Threat Hunting with Elastic Security
Elastic Security is designed to enable hypothesis-driven threat hunting at speed and scale. By unifying security telemetry and enabling analytics across clusters, threat hunters can ask complex questions across all their data, correlate signals, and validate hypotheses quickly without manual data stitching.