Blogs
Elastic Security Labs empowers security teams across the globe with novel security intelligence research and free to use tools.
SOC case management and detection rule history in Elastic Security
Elastic Security now tracks every detection rule change with one-click rollback and makes case data queryable out of the box, so SOC teams get audit trails and reporting without configuring anything.
Elastic goes all-in on Hacker Summer Camp at Black Hat and DEF CON in Las Vegas
Attack Discovery turns raw alerts into validated threats and Elastic Defend closes vulnerable driver gaps as fast as they're disclosed. Watch it all run against real attacks at the booth.
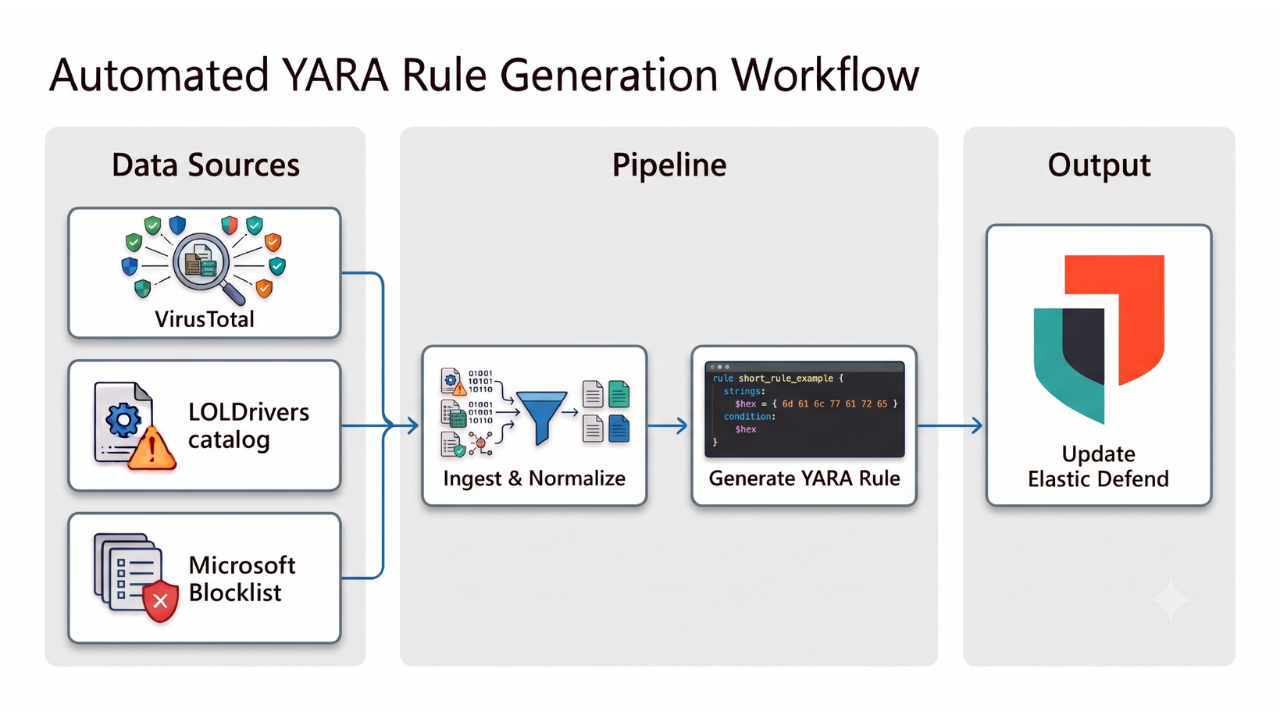
What's new in Elastic Defend: 800+ vulnerable driver rules, automated troubleshooting, and ARM support
Elastic Defend automatically generates and instantly deploys vulnerable driver YARA rules from VirusTotal, LOLDrivers and Microsoft's blocklist, closing the gap BYOVD attacks depend on. Plus a new troubleshooting skill and ARM endpoint protection.
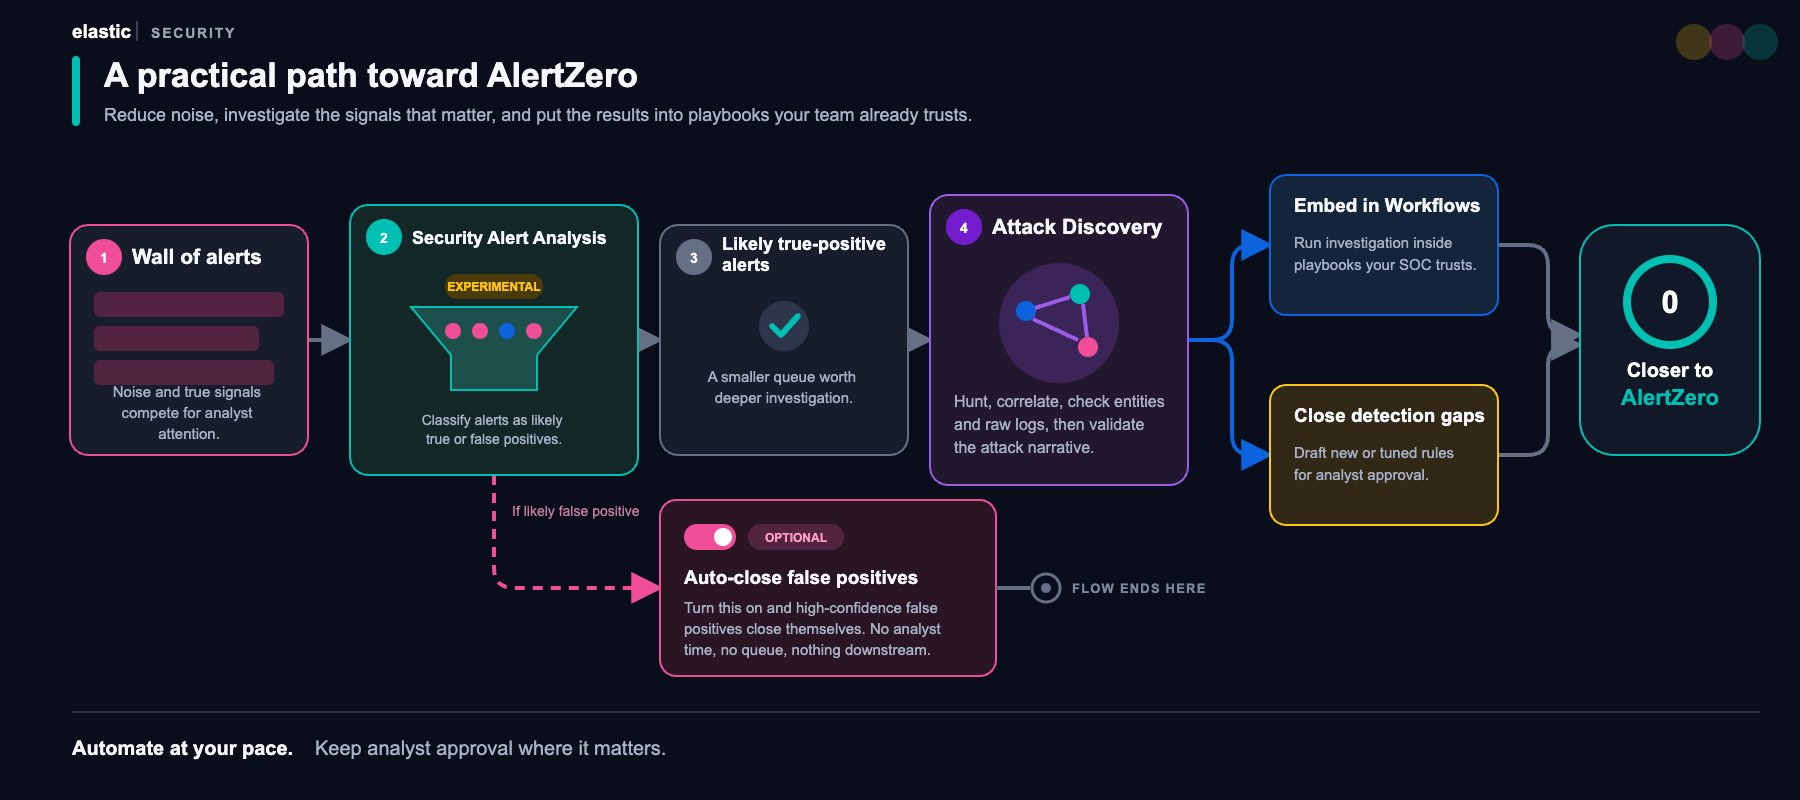
Journey to AlertZero: AI-driven alert triage and attack investigation for the agentic SOC
Elastic Security 9.5 gives SOC teams AI that handles first-pass alert triage and investigation, so analysts can get back to threat hunting and detection engineering instead of working through queue noise.
Stop rewriting detection rules by hand: automatic Sentinel-to-Elastic migration is here
Elastic's first automatic migration from a modern SIEM. Translate your Sentinel detection rules into Elastic Security without rebuilding them.
Inside Elastic InfoSec's agentic SOC: How we cut AI agent LLM calls by 60%
We run fourteen AI agents that triage Elastic InfoSec alerts. They were taking 19 LLM calls to do work that needed 8. Here's the five-step optimization loop we run across the fleet, plus the prompt template you can use with any AI assistant.
Inside Elastic InfoSec's agentic SOC: When to inline your agent's skills for a 5× cost reduction
We tested two agentic SOC architectures in parallel across 36,822 real Agent Builder conversations. One won by 5.7x: a specialized workflow triaging alerts for $0.69 each, against $3.42 for a single agent juggling 14 Skills. The data and the decision framework are both below.
wp2shell hits WordPress: detecting pre-auth RCE from plugin drop to command execution
We ran the wp2shell WordPress RCE chain end-to-end with Elastic Defend. Detection rule walkthrough, IOCs, and hunt guidance.
How Elasticsearch ES|QL COMPLETION turns noisy curl and wget rules into high-fidelity cloud security alerts
Elastic InfoSec tested this detection rule pattern on their own cloud fleet, filtering noisy curl and wget events with deterministic logic and LLM triage so only genuine threats reach an analyst.
Inside Elastic InfoSec's agentic SOC: cutting alert triage from 30 minutes to under 3
Elastic's InfoSec team built AI agents on Elastic Workflows that investigate every alert and assemble the case before an analyst ever opens it.
From vulnerability report to CVE draft in minutes: how Elastic automated security advisories with AI
How Elastic's security team built an AI agent with RAG against MITRE's CWE and CAPEC catalogues to draft CVE advisories from raw vulnerability reports, including the full prompt and crawler configs.
Azure AD Graph Activity Logs: Ingestion and threat detection to close the visibility gap
Azure AD Graph Activity Logs land in Elastic with full ECS parsing. Detect ROADrecon and AADInternals enumeration with ready-to-use detection rules.