Threat Command
Primary threat research from Elastic Security Labs Threat Command.
TELEPUZ: a modular MaaS malware spreading via CLICKFIX-VIDAR chains
TELEPUZ is a modular malware that emerged through CLICKFIX-VIDAR attacks in April. We reverse-engineered it to show you the infrastructure and evasion techniques that matter.
ClickFix to Cash-Out: Anatomy of a Mexican Banking-Fraud Toolkit
Elastic Security Labs tracks REF6045, an active operator-assisted banking fraud operation targeting customers of Mexican banks, fintech, payment processors, and cryptocurrency exchanges.
Lost in relocation: analysis of a new loader distributing CASTLESTEALER
Find out how a new obfuscated loader evades static detection using .reloc section abuse, five anti-VM/language checks and MBA obfuscation to deliver infostealer malware via Google Ads.
Detecting Tycoon 2FA AiTM attacks across Entra ID and Google Workspace
Tycoon 2FA bypasses MFA on Entra ID and Google Workspace. We map telemetry fingerprints across both platforms, ship detection rules for both tiers, and contain incidents in under 10 seconds with Elastic Workflows.
PHANTOMPULSE: anatomy of a hijackable blockchain-C2 RAT
Elastic Security Labs presents a detailed reverse-engineering analysis of PHANTOMPULSE, the long-lived RAT delivered to crypto-sector victims through the REF6598 intrusion set.
Copy Fail and DirtyFrag: Linux Page Cache Bugs in the Wild
This research analyzes the Linux kernel privilege escalation vulnerabilities Copy Fail and DirtyFrag, which exploit subtle page cache corruption bugs to create reliable paths to root access. Additionally, Elastic Security Labs is releasing detection logic for these vulnerabilities.
TCLBANKER: Brazilian Banking Trojan Spreading via WhatsApp and Outlook
REF3076 uses a trojanized Logitech installer to deploy TCLBANKER, a Brazilian banking trojan with environment-gated payloads, WPF fraud overlays, and self-propagating WhatsApp and Outlook worm modules.
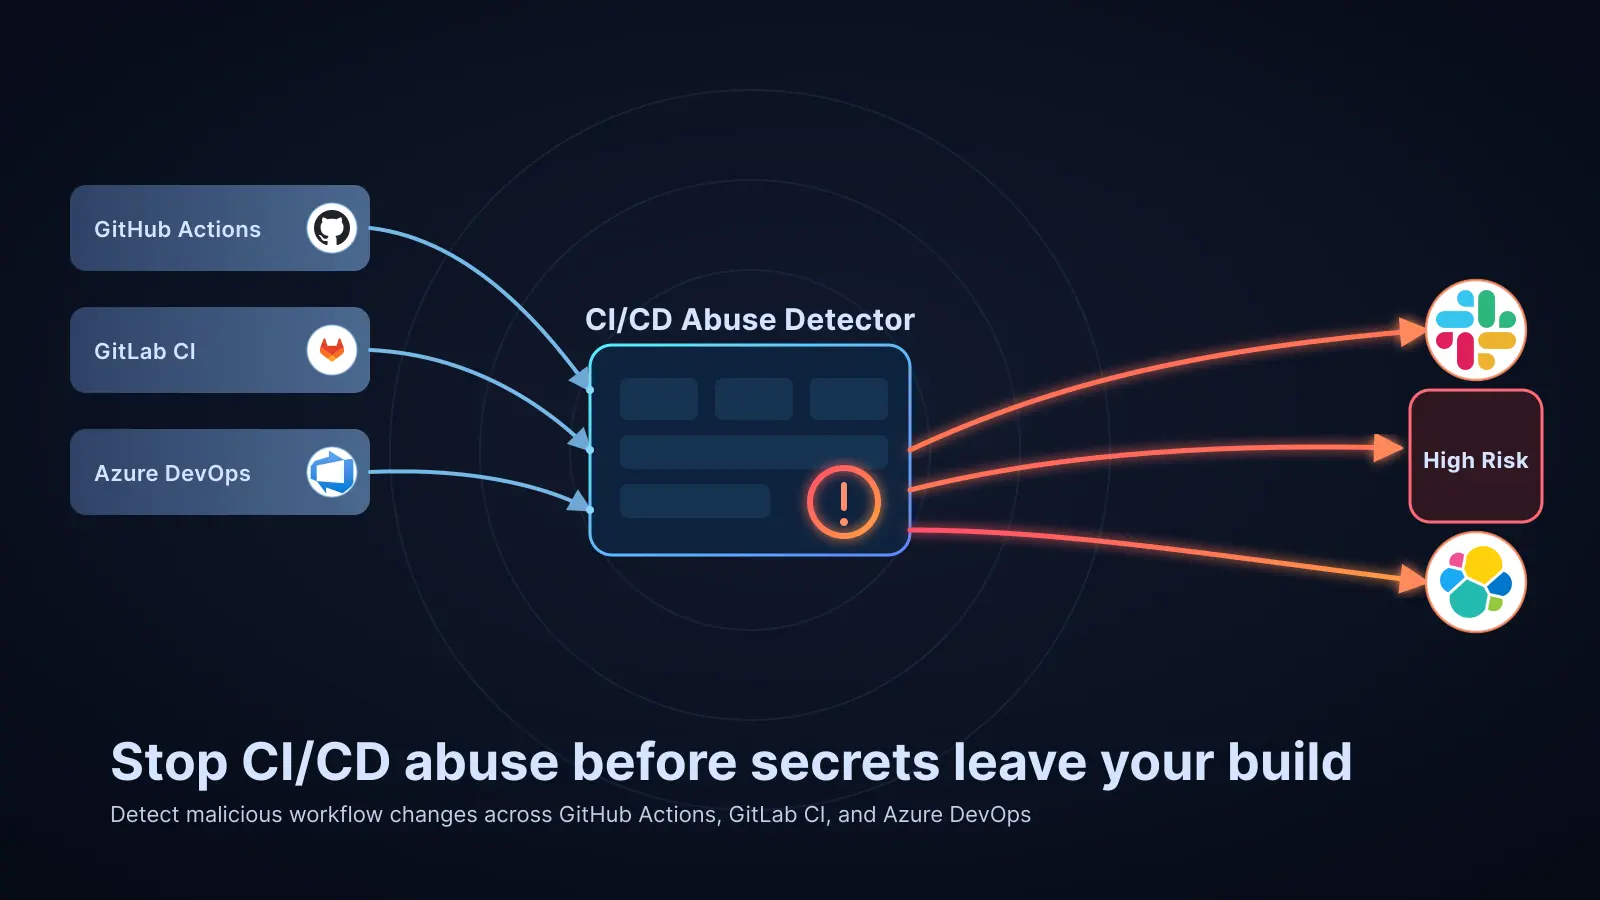
CI/CD pipeline abuse: the problem no one is watching
How we built an open-source, drop-in CI template that uses signal extraction and LLM reasoning to catch CI/CD abuse in GitHub Actions, GitLab CI, and Azure DevOps pipelines.
The Cost of Understanding: LLM-Driven Reverse Engineering vs Iterative LLM Obfuscation
Elastic Security Labs explores the ongoing arms race between LLM-driven reverse engineering and obfuscation.
Phantom in the vault: Obsidian abused to deliver PhantomPulse RAT
Elastic Security Labs uncovers a novel social engineering campaign that abuses the popular note-taking application, Obsidian's legitimate community plugin ecosystem. The campaign, which we track as REF6598, targets individuals in the financial and cryptocurrency sectors through elaborate social engineering on LinkedIn and Telegram.
Hooked on Linux: Rootkit Detection Engineering
In this second part of a two-part series, we explore Linux rootkit detection engineering, focusing on the limitations of static detection reliance, and the importance of rootkit behavioral detection.
How we caught the Axios supply chain attack
Joe Desimone shares the story of how he caught the Axios supply chain attack with a proof of concept tool built in an afternoon.