Category: Detection Engineering
Articles tagged Detection Engineering
Inside the loop: Five AI attack frameworks that never ask permission
Five agentic offensive frameworks act in bursts of two to 25 seconds, and none enforces authorization in code. What ARTEX, CyberStrikeAI, Cairn, PentAGI, and HexStrike leave in your telemetry, and the ES|QL hunt that catches them.
56 AWS API calls in 141 milliseconds: Inside an AI-run intrusion
A CyberStrikeAI server spent 16 days in four AWS accounts using eight identities, and the CloudTrail record shows why six detection rules each caught only part of it.
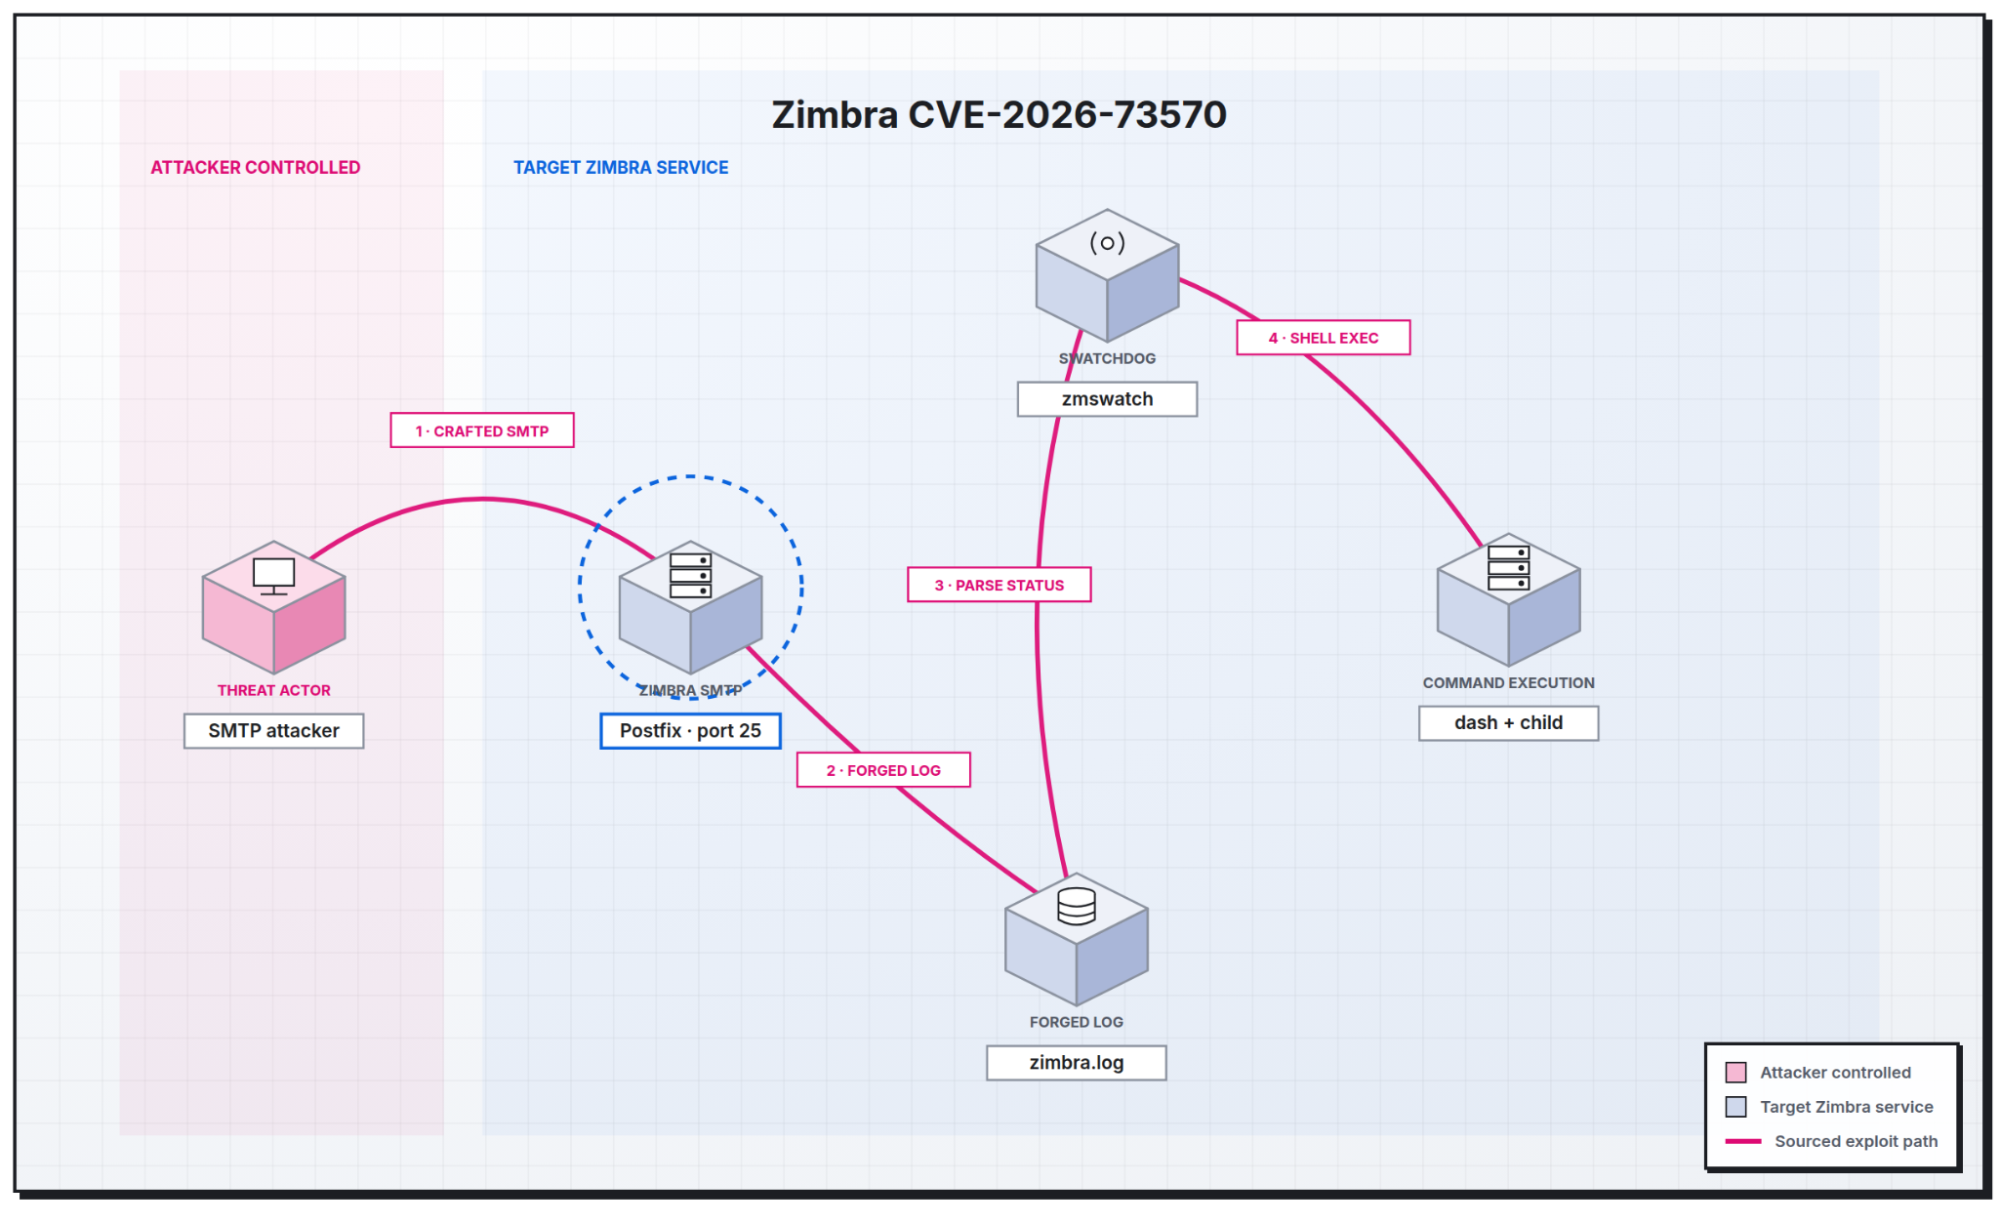
How CVE-2026-73570 turns a Zimbra log file into remote code execution
We reproduced the Zimbra command injection vulnerability and found that several public PoCs write a payload Swatchdog never matches, so a failed test looks like a patched server.
php2shell: Assessing Elastic detection coverage relevant to CVE-2026-109618 and CVE-2026-109619
CVE-2026-109618 and CVE-2026-109619 are critical PHP core RCE flaws that leaked ahead of disclosure. We cover what is verified, why exploitation converges on a web server spawning a shell, and the Elastic detections developed to catch this behavior.
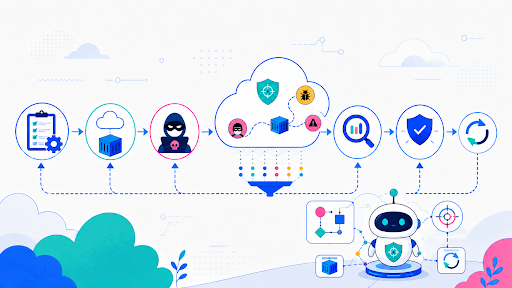
Cloud Threat Emulation on Autopilot: Context is Everything
Cloud threat emulation is more than detonation. A plan-first methodology for cloud detection engineering: scope, victim model, telemetry, coverage, cleanup. Learn how to properly leverage AI to automate your emulations.

Linux Detection Engineering - Local Privilege Escalation
Seven of the thirteen Linux privilege escalation CVEs we tracked in 2026 turned out to be the same copy-on-write bug pointed at different kernel interfaces. We ran the public proof-of-concept for eleven exploits and two misconfigurations, and noted which rules fired.
How to correlate Kubernetes audit logs with container runtime data
Two fields join the Kubernetes API to what ran inside the pod, and one turns up a container escape your process events never recorded.
REVSTEALER ramps up: analysis of up-and-coming infostealer
Elastic Security Labs deep dives into REVSTEALER, an emerging infostealer targeting browsers, wallets, and gaming accounts.
Linux Detection Engineering - Fileless Execution
We reproduced five Linux fileless execution patterns with FENIX, including memfd_create staging, interpreter one-liners, deleted binaries, and in-memory kernel module loads, then mapped each to the Elastic Defend rules that catch it.
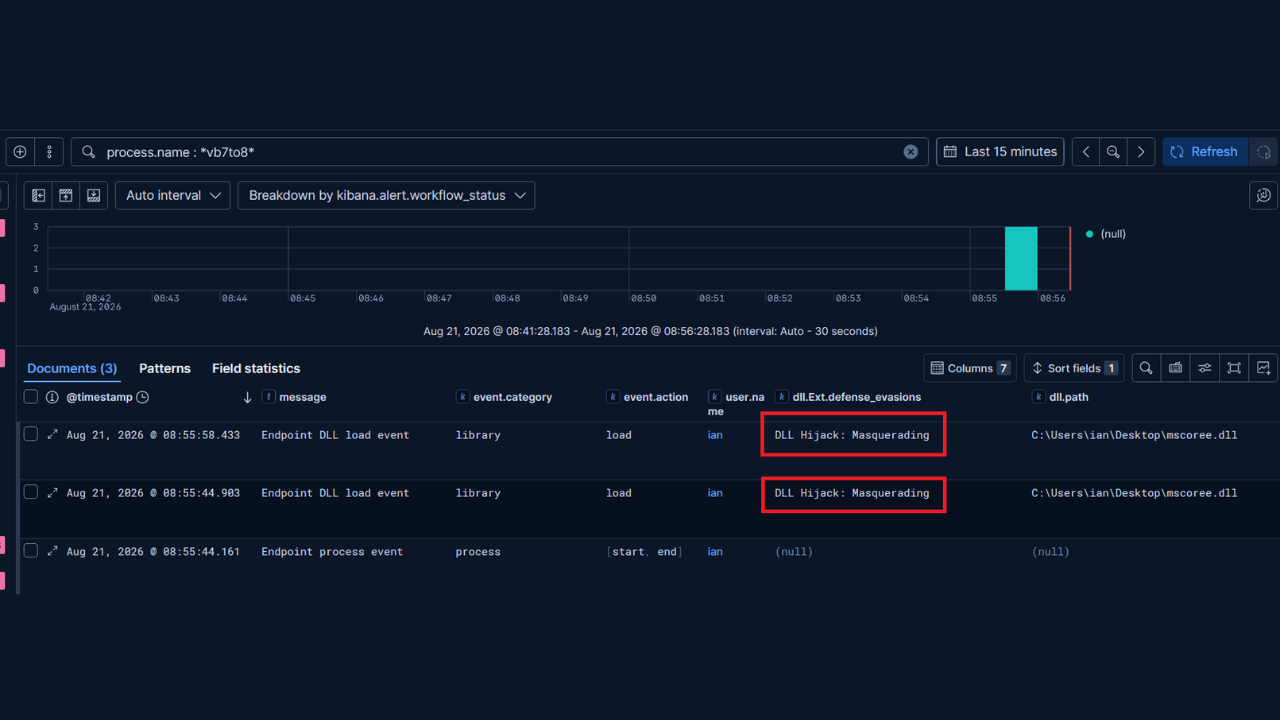
From 88 lines to 1: Detecting DLL hijacking with Elastic Defend
The ClickFix campaign that sideloads a malicious mscoree.dll also ships a driver to kill Elastic Endpoint. We rebuilt that DLL as a NativeAOT library, dropped it beside a signed Microsoft binary, and Elastic Defend 9.5.0 flagged the load.
Exploring the Hugging Face Breach: mapping AI agent tactics to Elastic Defend
Every stage of the Hugging Face breach maps to Elastic Defend and SIEM rules already shipping, from worker RCE and credential harvest to self-migrating C2 and GenAI detection.
Detecting Tycoon 2FA AiTM attacks across Entra ID and Google Workspace
Tycoon 2FA bypasses MFA on Entra ID and Google Workspace. We map telemetry fingerprints across both platforms, ship detection rules for both tiers, and contain incidents in under 10 seconds with Elastic Workflows.