Threat Command
Primary threat research from Elastic Security Labs Threat Command.
Inside the Axios supply chain compromise - one RAT to rule them all
Elastic Security Labs analyzes a supply chain compromise of the axios npm package delivering a unified cross-platform RAT
Fake Installers to Monero: A Multi-Tool Mining Operation
Elastic Security Labs dissects a long-running operation deploying RATs, cryptominers, and CPA fraud through fake installer lures, tracking its evolution across campaigns and Monero payouts.
Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER
Elastic Security Labs observed two custom malware components targeting a South Asian financial institution: a modular backdoor with USB-based spreading and a DLL-side-loaded keylogger.
Illuminating VoidLink: Technical analysis of the VoidLink rootkit framework
Elastic Security Labs analyzes VoidLink, a sophisticated Linux malware framework that combines traditional Loadable Kernel Modules with eBPF to maintain persistence.
From Invitation to Infection: How SILENTCONNECT Delivers ScreenConnect
SILENTCONNECT is a multi-stage loader that leverages VBScript, in-memory PowerShell execution, and PEB masquerading to silently deploy the ScreenConnect RMM tool.
Hooked on Linux: Rootkit Taxonomy, Hooking Techniques and Tradecraft
In this first part of a two-part series, we explore Linux rootkit taxonomy, trace their evolution from userland shared object hijacking and kernel-space loadable kernel module hooking to modern eBPF- and io_uring-powered techniques.
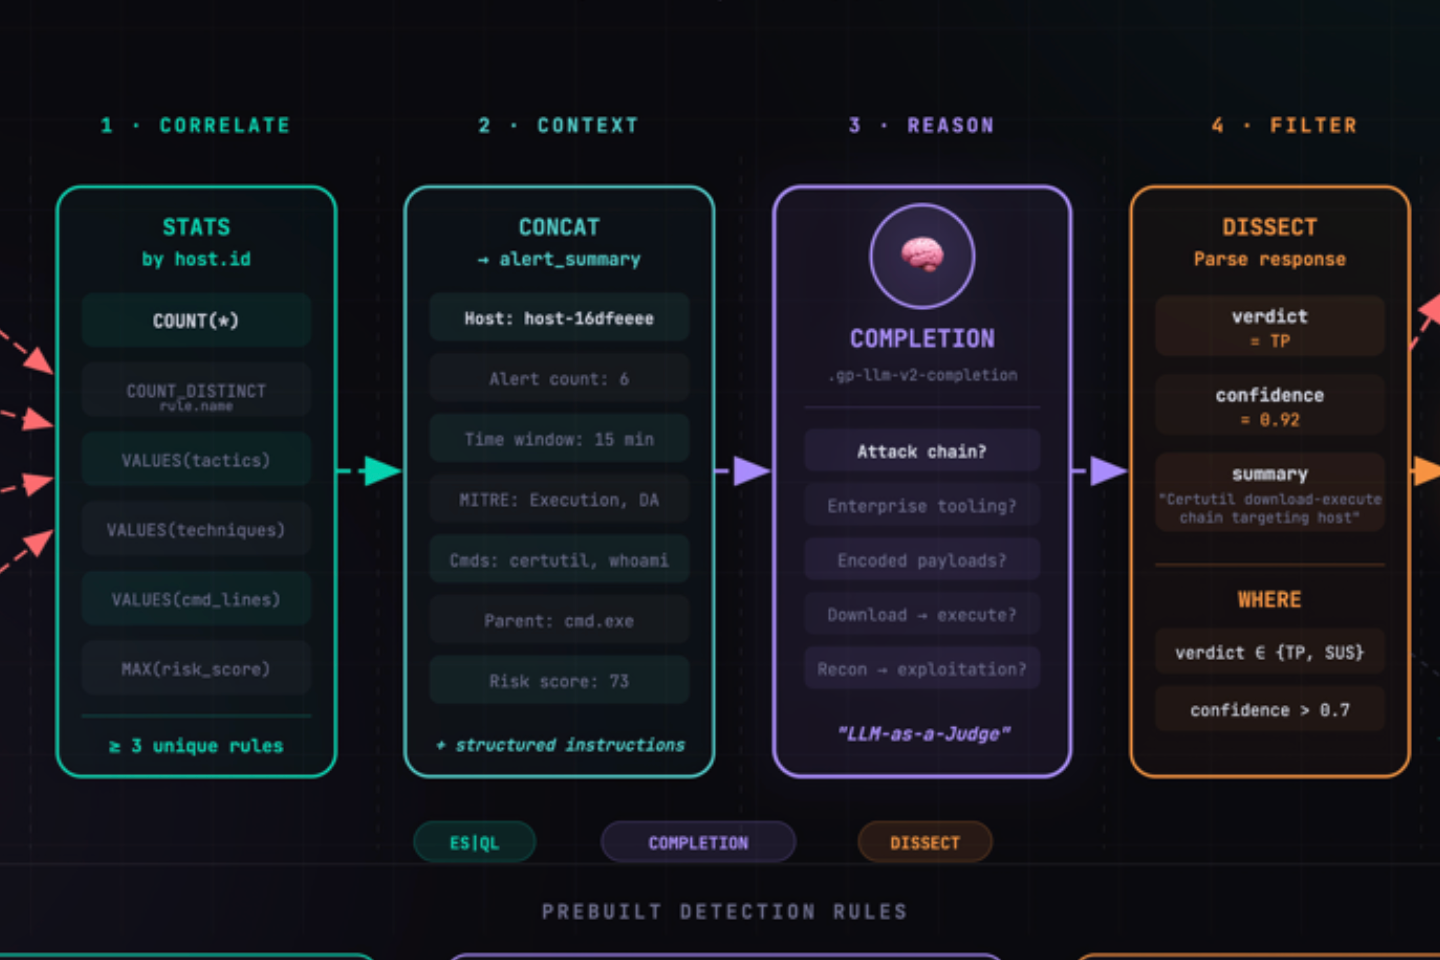
Beyond Behaviors: AI-Augmented Detection Engineering with ES|QL COMPLETION
Learn how Elastic's ES|QL COMPLETION command brings LLM reasoning directly into detection rules, enabling detection engineers to build intelligent alert triage without external orchestration.
MIMICRAT: ClickFix Campaign Delivers Custom RAT via Compromised Legitimate Websites
Elastic Security Labs uncovered a ClickFix campaign using compromised legitimate sites to deliver a five-stage chain ending in MIMICRAT, a custom native C RAT with malleable C2, token theft, and SOCKS5 tunneling.
The Immutable Illusion: Pwning Your Kernel with Cloud Files
Threat actors can abuse a class of vulnerabilities to bypass security restrictions and break trust chains.
BADIIS to the Bone: New Insights to a Global SEO Poisoning Campaign
In November 2025, Elastic Security Labs observed an intrusion affecting a multinational organization based in Southeast Asia. During the analysis of this activity, our team observed various post-compromise techniques and tooling used to deploy BADIIS malware onto a Windows web server consistent with other industry publications.
NANOREMOTE, cousin of FINALDRAFT
The fully-featured backdoor we call NANOREMOTE shares characteristics with malware described in REF7707 and is similar to the FINALDRAFT implant.
RONINGLOADER: DragonBreath’s New Path to PPL Abuse
Elastic Security Labs uncovers RONINGLOADER, a multi-stage loader deploying DragonBreath’s updated gh0st RAT variant. The campaign weaponizes signed drivers, thread-pool injection, and PPL abuse to disable Defender and evade Chinese EDR tools.