Category: Threat Intelligence
Articles tagged Threat Intelligence
Inside the loop: Five AI attack frameworks that never ask permission
Five agentic offensive frameworks act in bursts of two to 25 seconds, and none enforces authorization in code. What ARTEX, CyberStrikeAI, Cairn, PentAGI, and HexStrike leave in your telemetry, and the ES|QL hunt that catches them.
56 AWS API calls in 141 milliseconds: Inside an AI-run intrusion
A CyberStrikeAI server spent 16 days in four AWS accounts using eight identities, and the CloudTrail record shows why six detection rules each caught only part of it.
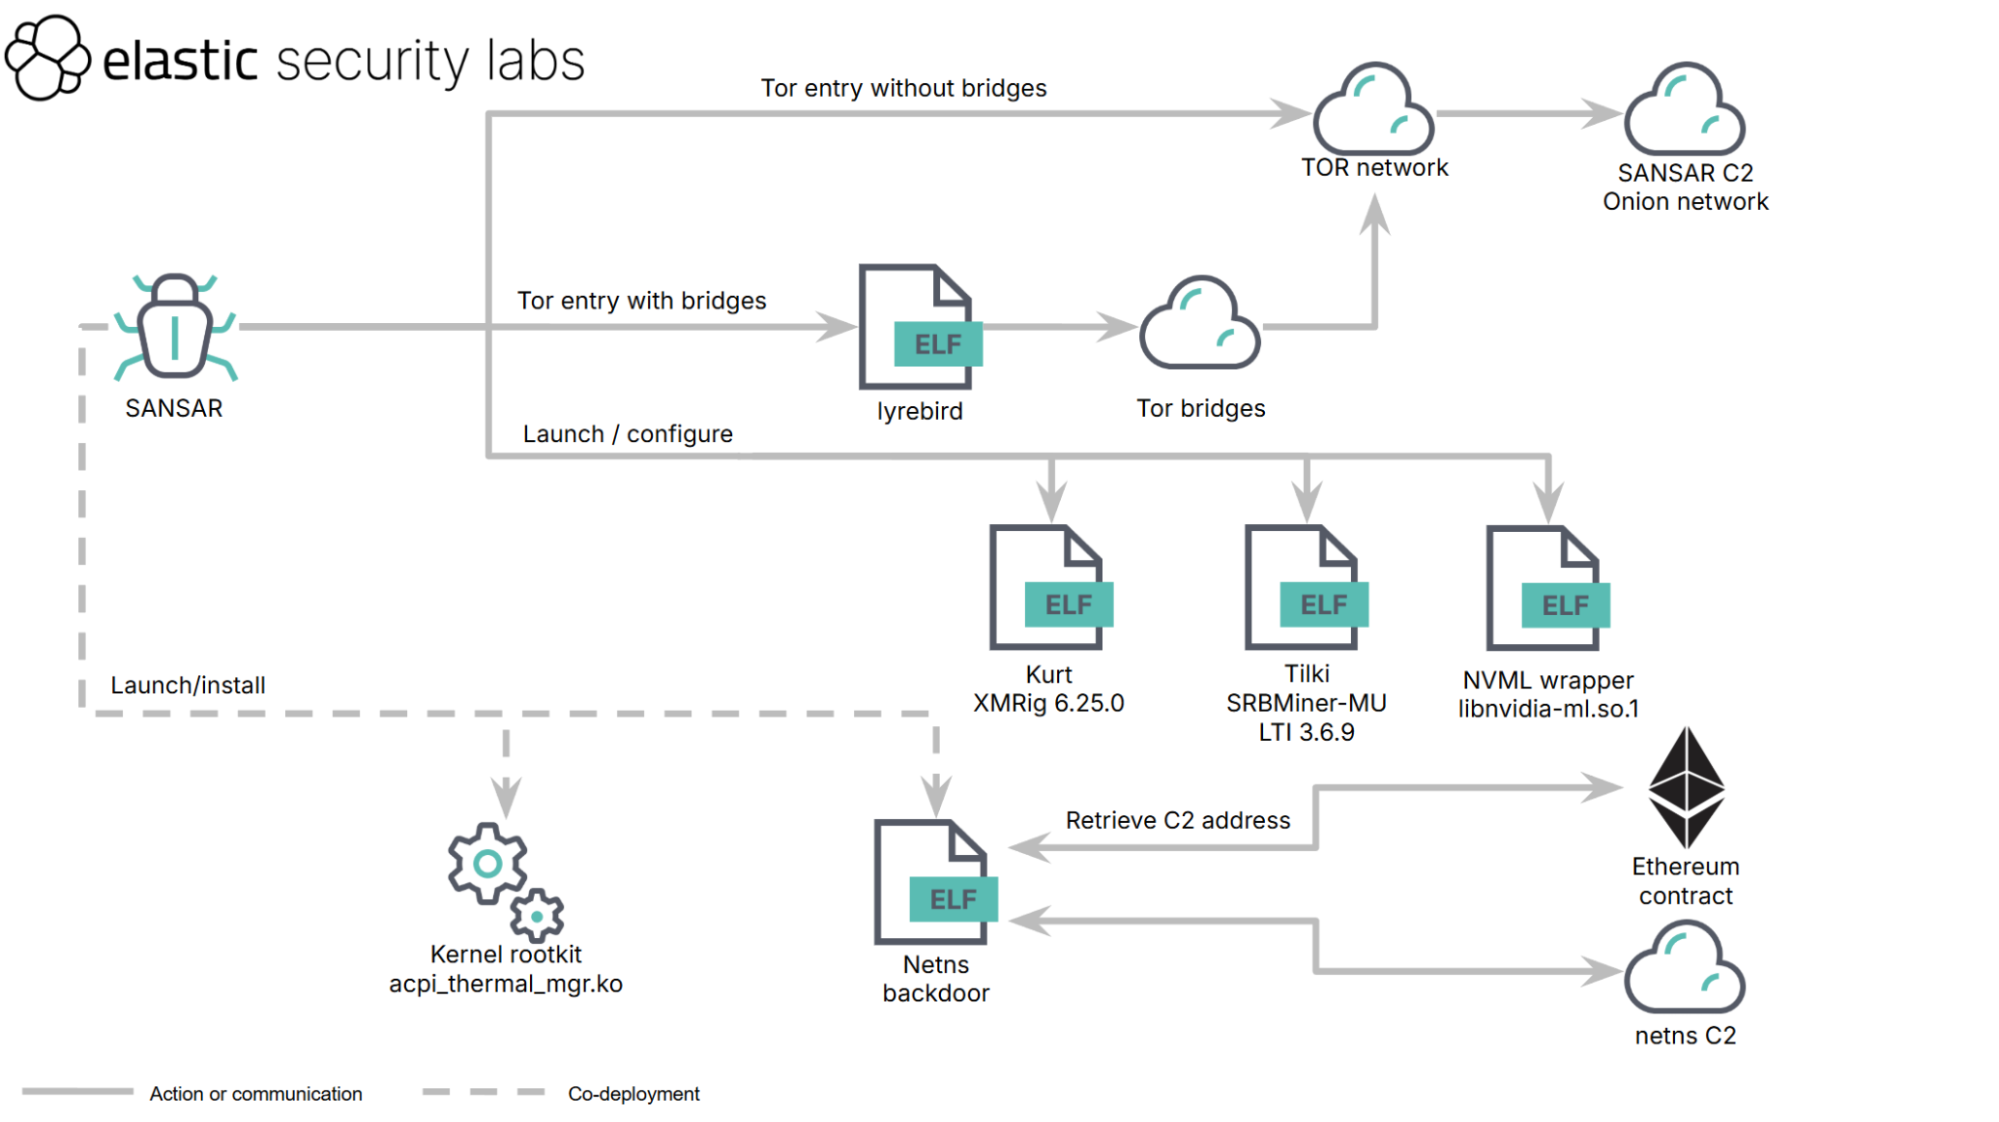
0% GPU utilization: How SANSAR hides Linux cryptomining
Elastic Security Labs analyzes SANSAR, a Linux cryptomining orchestrator that manages miners over Tor, alongside a kernel rootkit, GPU monitoring hooks and a backdoor that retrieves its C2 address from Ethereum.
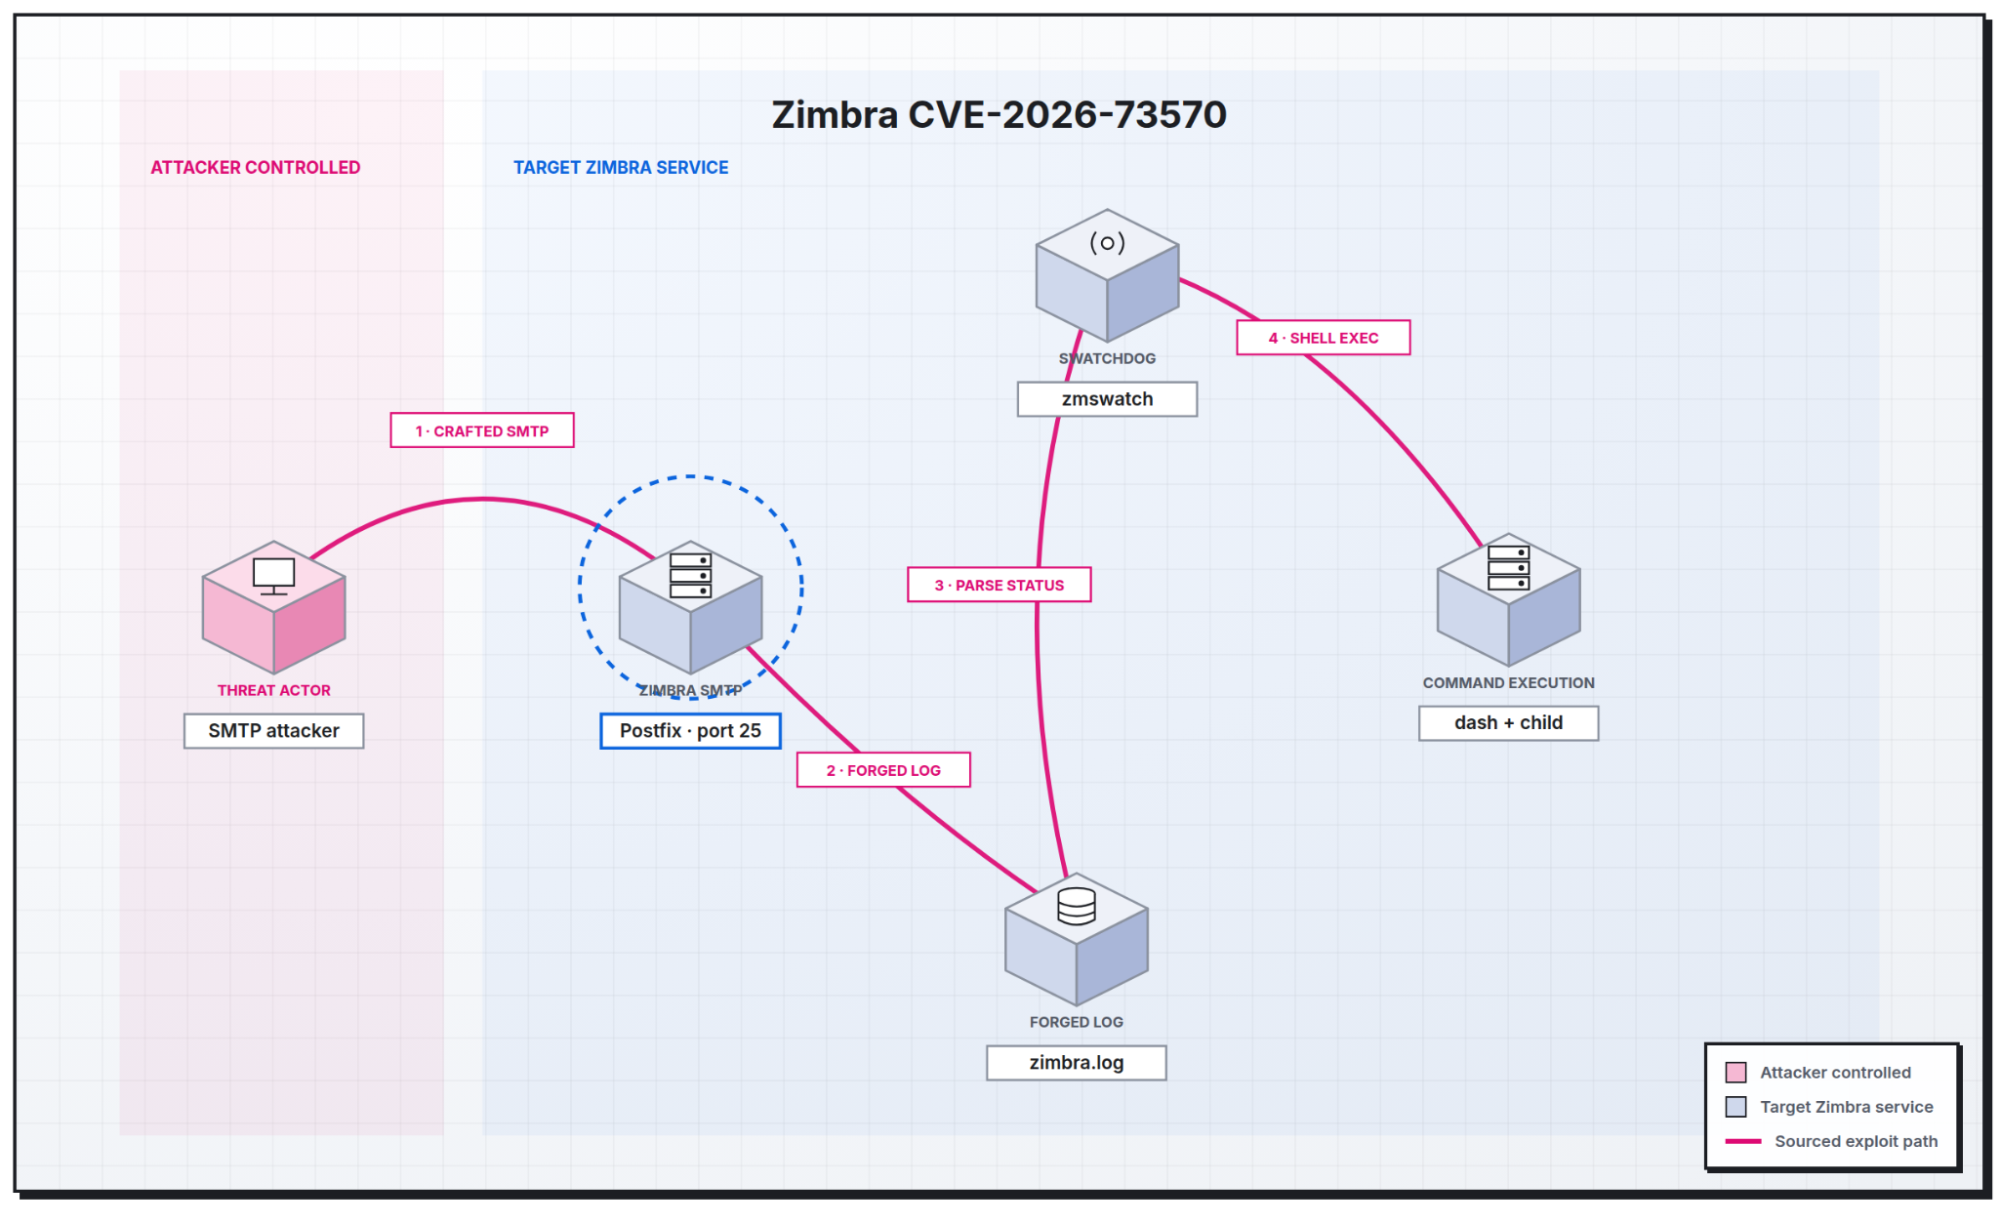
How CVE-2026-73570 turns a Zimbra log file into remote code execution
We reproduced the Zimbra command injection vulnerability and found that several public PoCs write a payload Swatchdog never matches, so a failed test looks like a patched server.
php2shell: Assessing Elastic detection coverage relevant to CVE-2026-109618 and CVE-2026-109619
CVE-2026-109618 and CVE-2026-109619 are critical PHP core RCE flaws that leaked ahead of disclosure. We cover what is verified, why exploitation converges on a web server spawning a shell, and the Elastic detections developed to catch this behavior.
Auditing the auditor: Unmasking Apex Accelerator
REF8801 exposes how Apex Accelerator combines convincing Web3 services with malicious npm packages, attacker-controlled AI infrastructure, and cross-platform malware delivery.
The extension you never installed: KREMLIN forges Chrome's own integrity checks to steal banking sessions
Elastic Security Labs tracked this malicious browser extension across seven campaigns and 15 months, through Brazilian bank lures and the Ethereum smart contracts that hold its C2 configuration.
REVSTEALER ramps up: analysis of up-and-coming infostealer
Elastic Security Labs deep dives into REVSTEALER, an emerging infostealer targeting browsers, wallets, and gaming accounts.
Shai-Hulud strikes again: CHAINDROP worm hits 400+ npm packages
Elastic Security Labs identified the return of Shai-Hulud. Attackers compromised the keyv maintainer and deployed CHAINDROP, a worm that uses stolen npm credentials to backdoor co-owned packages totaling over 1.3 billion monthly downloads.
New North Korean campaign uses fake coding interviews to steal developer credentials
DPRK-aligned hackers hid malware inside SVG flag images to backdoor developer job interview coding tests. Not one antivirus vendor caught it.
How we caught the Axios supply chain attack
Joe Desimone shares the story of how he caught the Axios supply chain attack with a proof of concept tool built in an afternoon.
Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER
Elastic Security Labs observed two custom malware components targeting a South Asian financial institution: a modular backdoor with USB-based spreading and a DLL-side-loaded keylogger.