Inside Elastic InfoSec's agentic SOC: cutting alert triage from 30 minutes to under 3
Elastic's InfoSec team built AI agents on Elastic Workflows that investigate every alert and assemble the case before an analyst ever opens it.
From vulnerability report to CVE draft in minutes: how Elastic automated security advisories with AI
How Elastic's security team built an AI agent with RAG against MITRE's CWE and CAPEC catalogues to draft CVE advisories from raw vulnerability reports, including the full prompt and crawler configs.
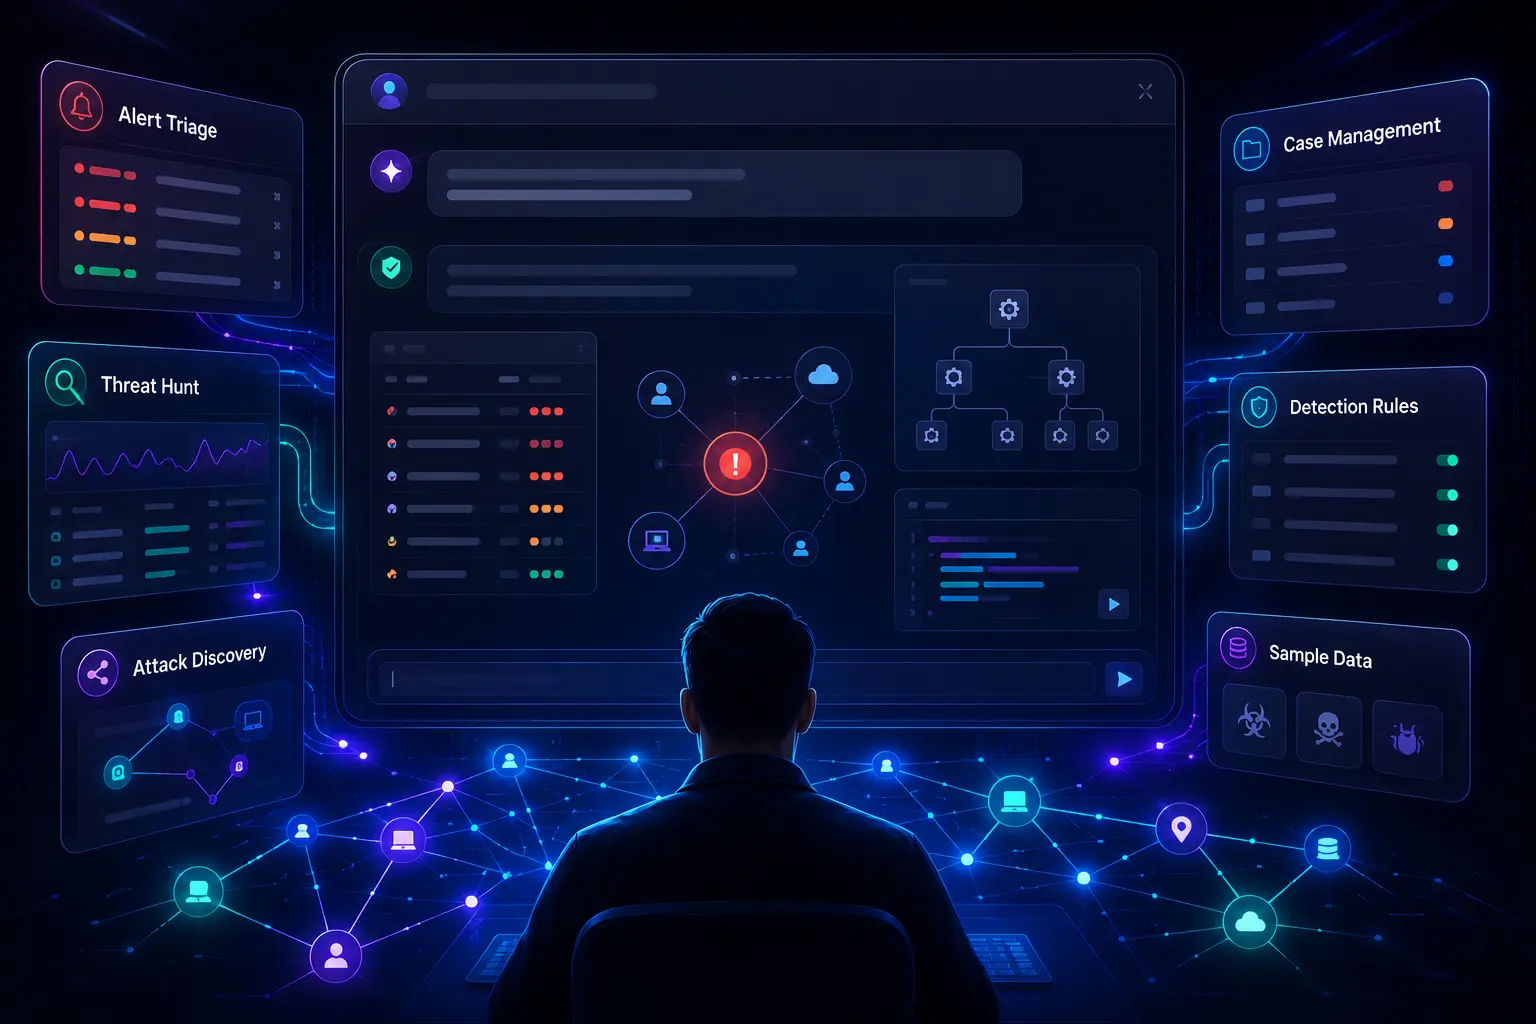
Elastic Security MCP App: Interactive security operations inside your AI Tools
Elastic Security is the first security vendor to ship an interactive UI in AI tools. Triage alerts, hunt threats, correlate attack chains, and open cases, all from inside your AI conversation.
AI-generated hunting leads: The hunt starts before you ask the question
Introducing AI-generated hunting leads, proactive, environment-aware threat hypotheses powered by Elastic Entity analytics and integrated AI reasoning.
Elastic Workflows GA: automation where your security data already lives
Elastic Workflows is generally available in 9.4, bringing production-ready security automation with deeper case management integration, human-in-the-loop support, natural language authoring, and more.
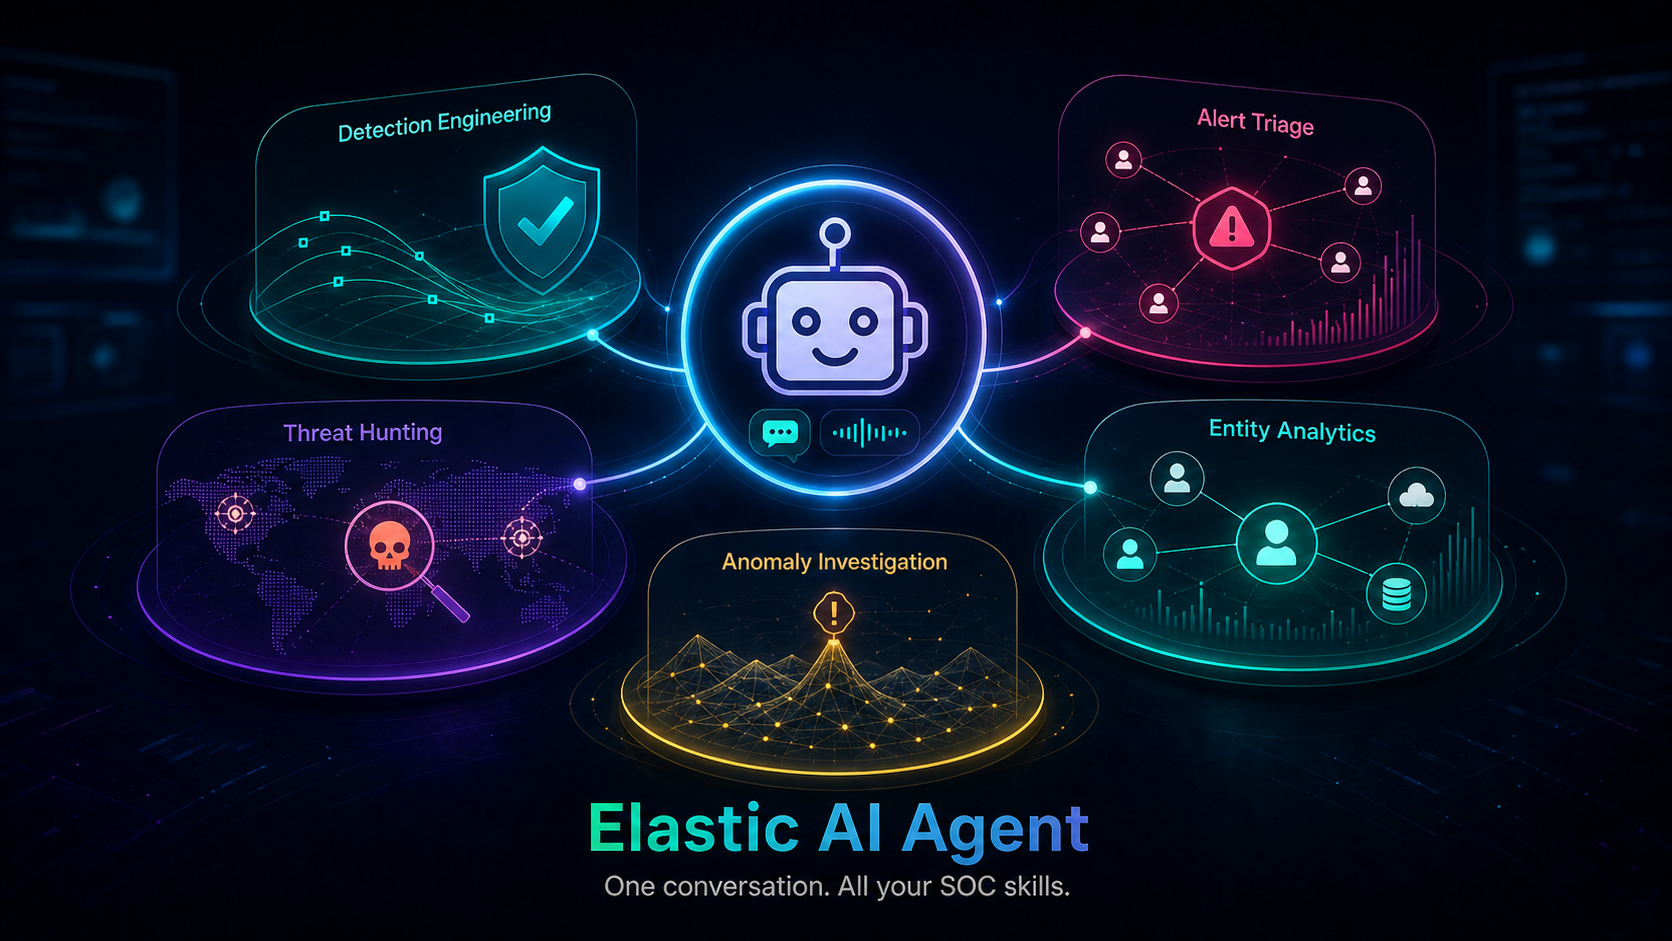
One agent, the right skills: Elastic Security 9.4 brings domain expertise on demand to every SOC workflow
Elastic Security 9.4 introduces skills, modular AI capabilities that teach the Elastic AI Agent how to detect, investigate, and hunt like a specialist. This is how they work, and why they matter for the SOC.
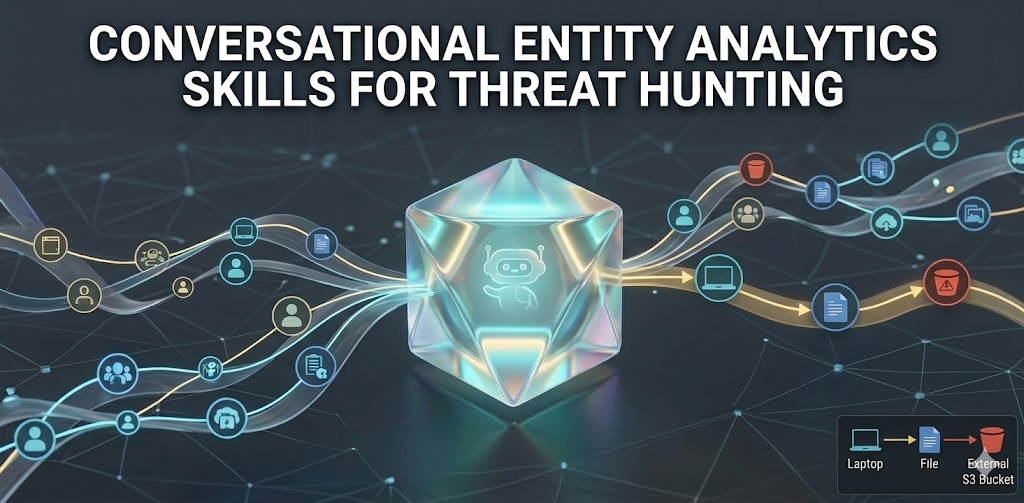
Elastic Conversational Entity Analytics: threat hunting in a single conversation
Conversational Entity Analytics delivers Entity Analytics features as rich inline attachments and Canvas previews into Agent Builder, so you don’t have to leave the conversation.
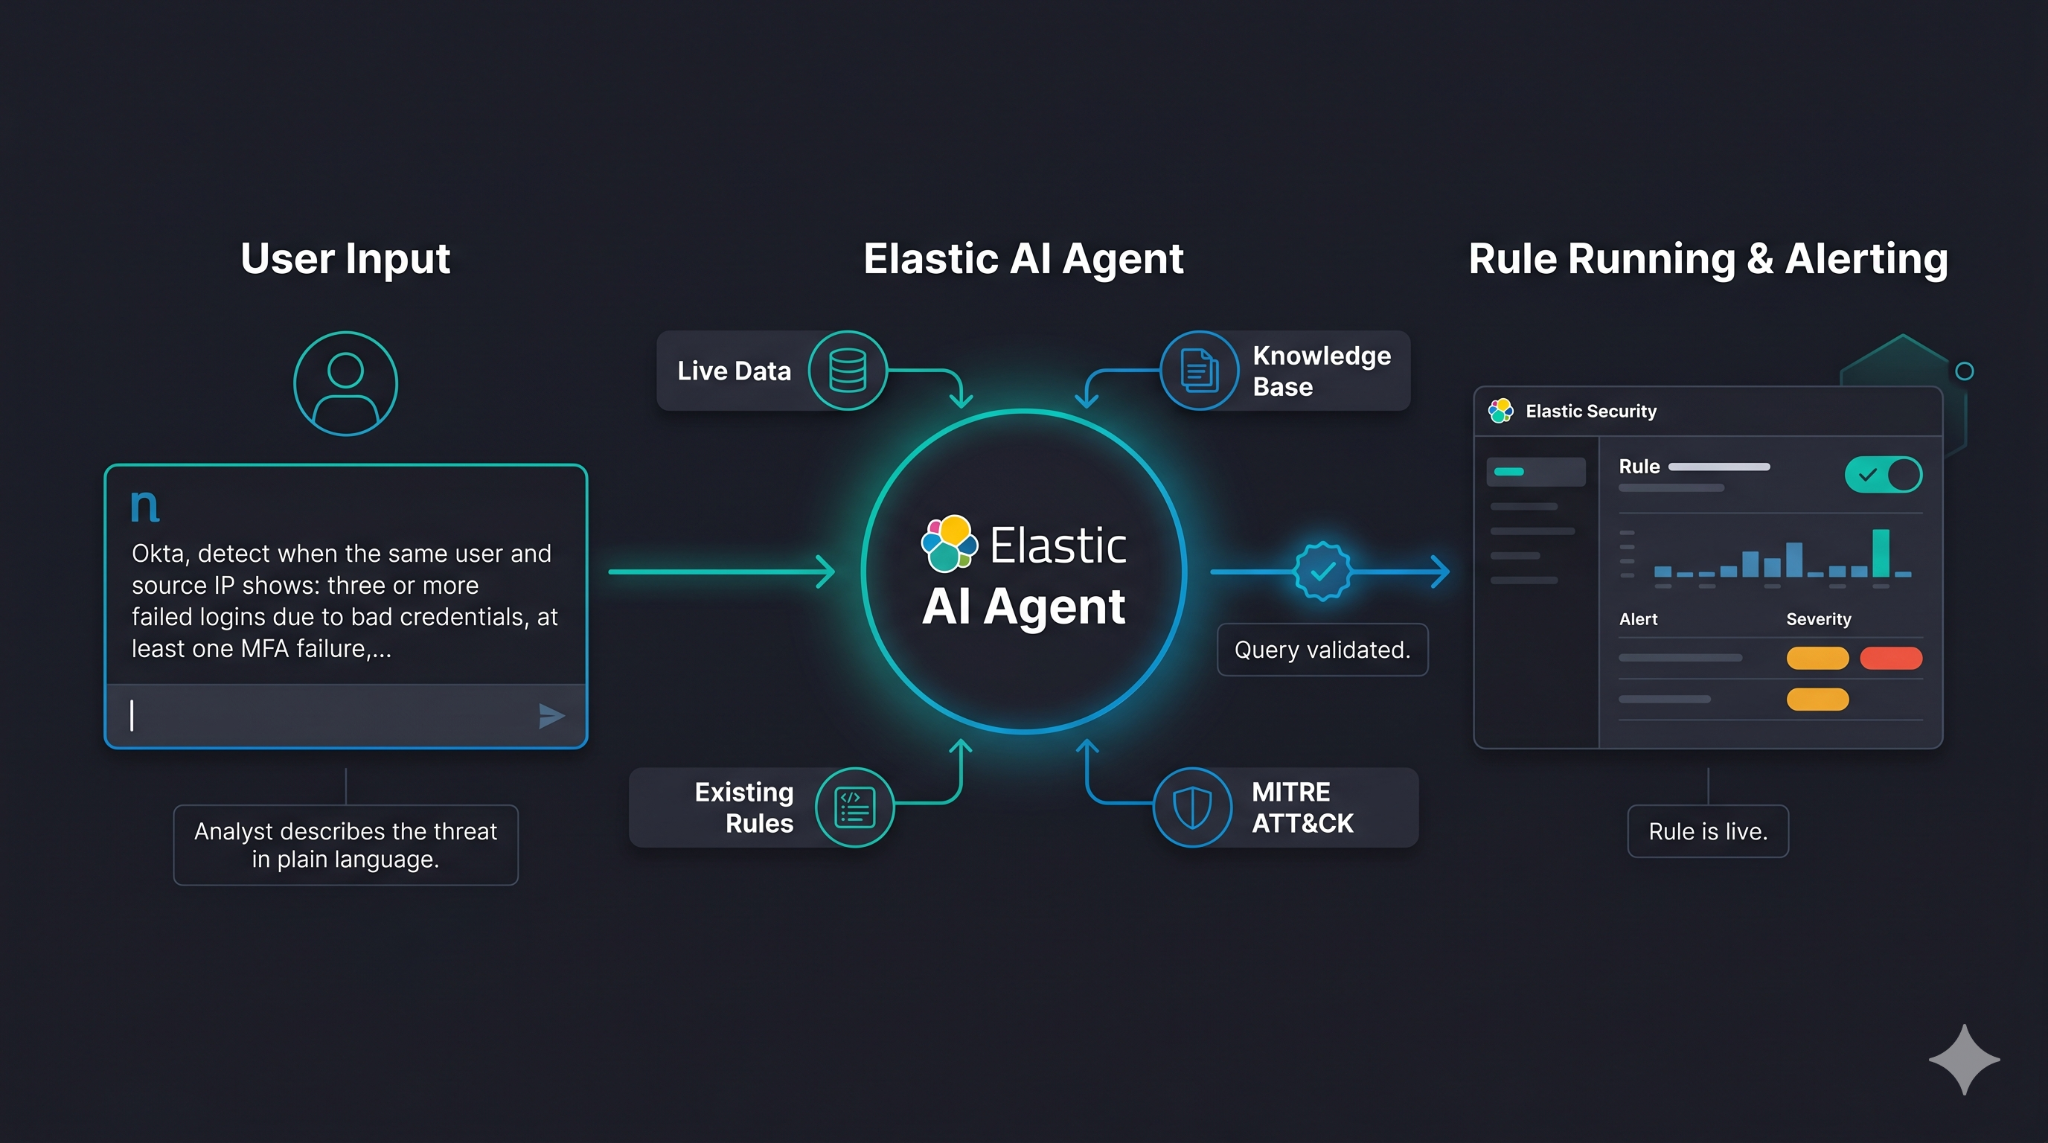
From plain English to production rule: AI-native Elasticsearch ES|QL detection in Elastic Security
Elastic Security now lets analysts describe a threat behavior in plain language and receive a complete, validated Elasticsearch ES|QL detection rule in return, no query expertise required.
Supercharge Your SOC
Detection Engineering in the Era of AI Agents - The New Frontier.
Security Automation with Elastic Workflows: From Alert to Response
A practical guide to building intelligent, automated security playbooks with Elastic Workflows.
Get started with Elastic Security from your AI agent
Go from zero to a fully populated Elastic Security environment without leaving your IDE, using open source Agent Skills.
Speeding APT Attack Confirmation with Attack Discovery, Workflows, and Agent Builder
This article walks through how Elastic Security's Attack Discovery, combined with Workflows and Agent Builder, can automatically detect, correlate, and confirm APT-level attacks like Chrysalis while reducing analyst response time from hours to minutes.