Blog
Significant Events
Significant Events reads about 100 documents from a log source and writes detection rules from them. This series follows what those rules catch during a real outage.
How Elastic Significant Events turns 100 log samples into detection rules
Observability Labs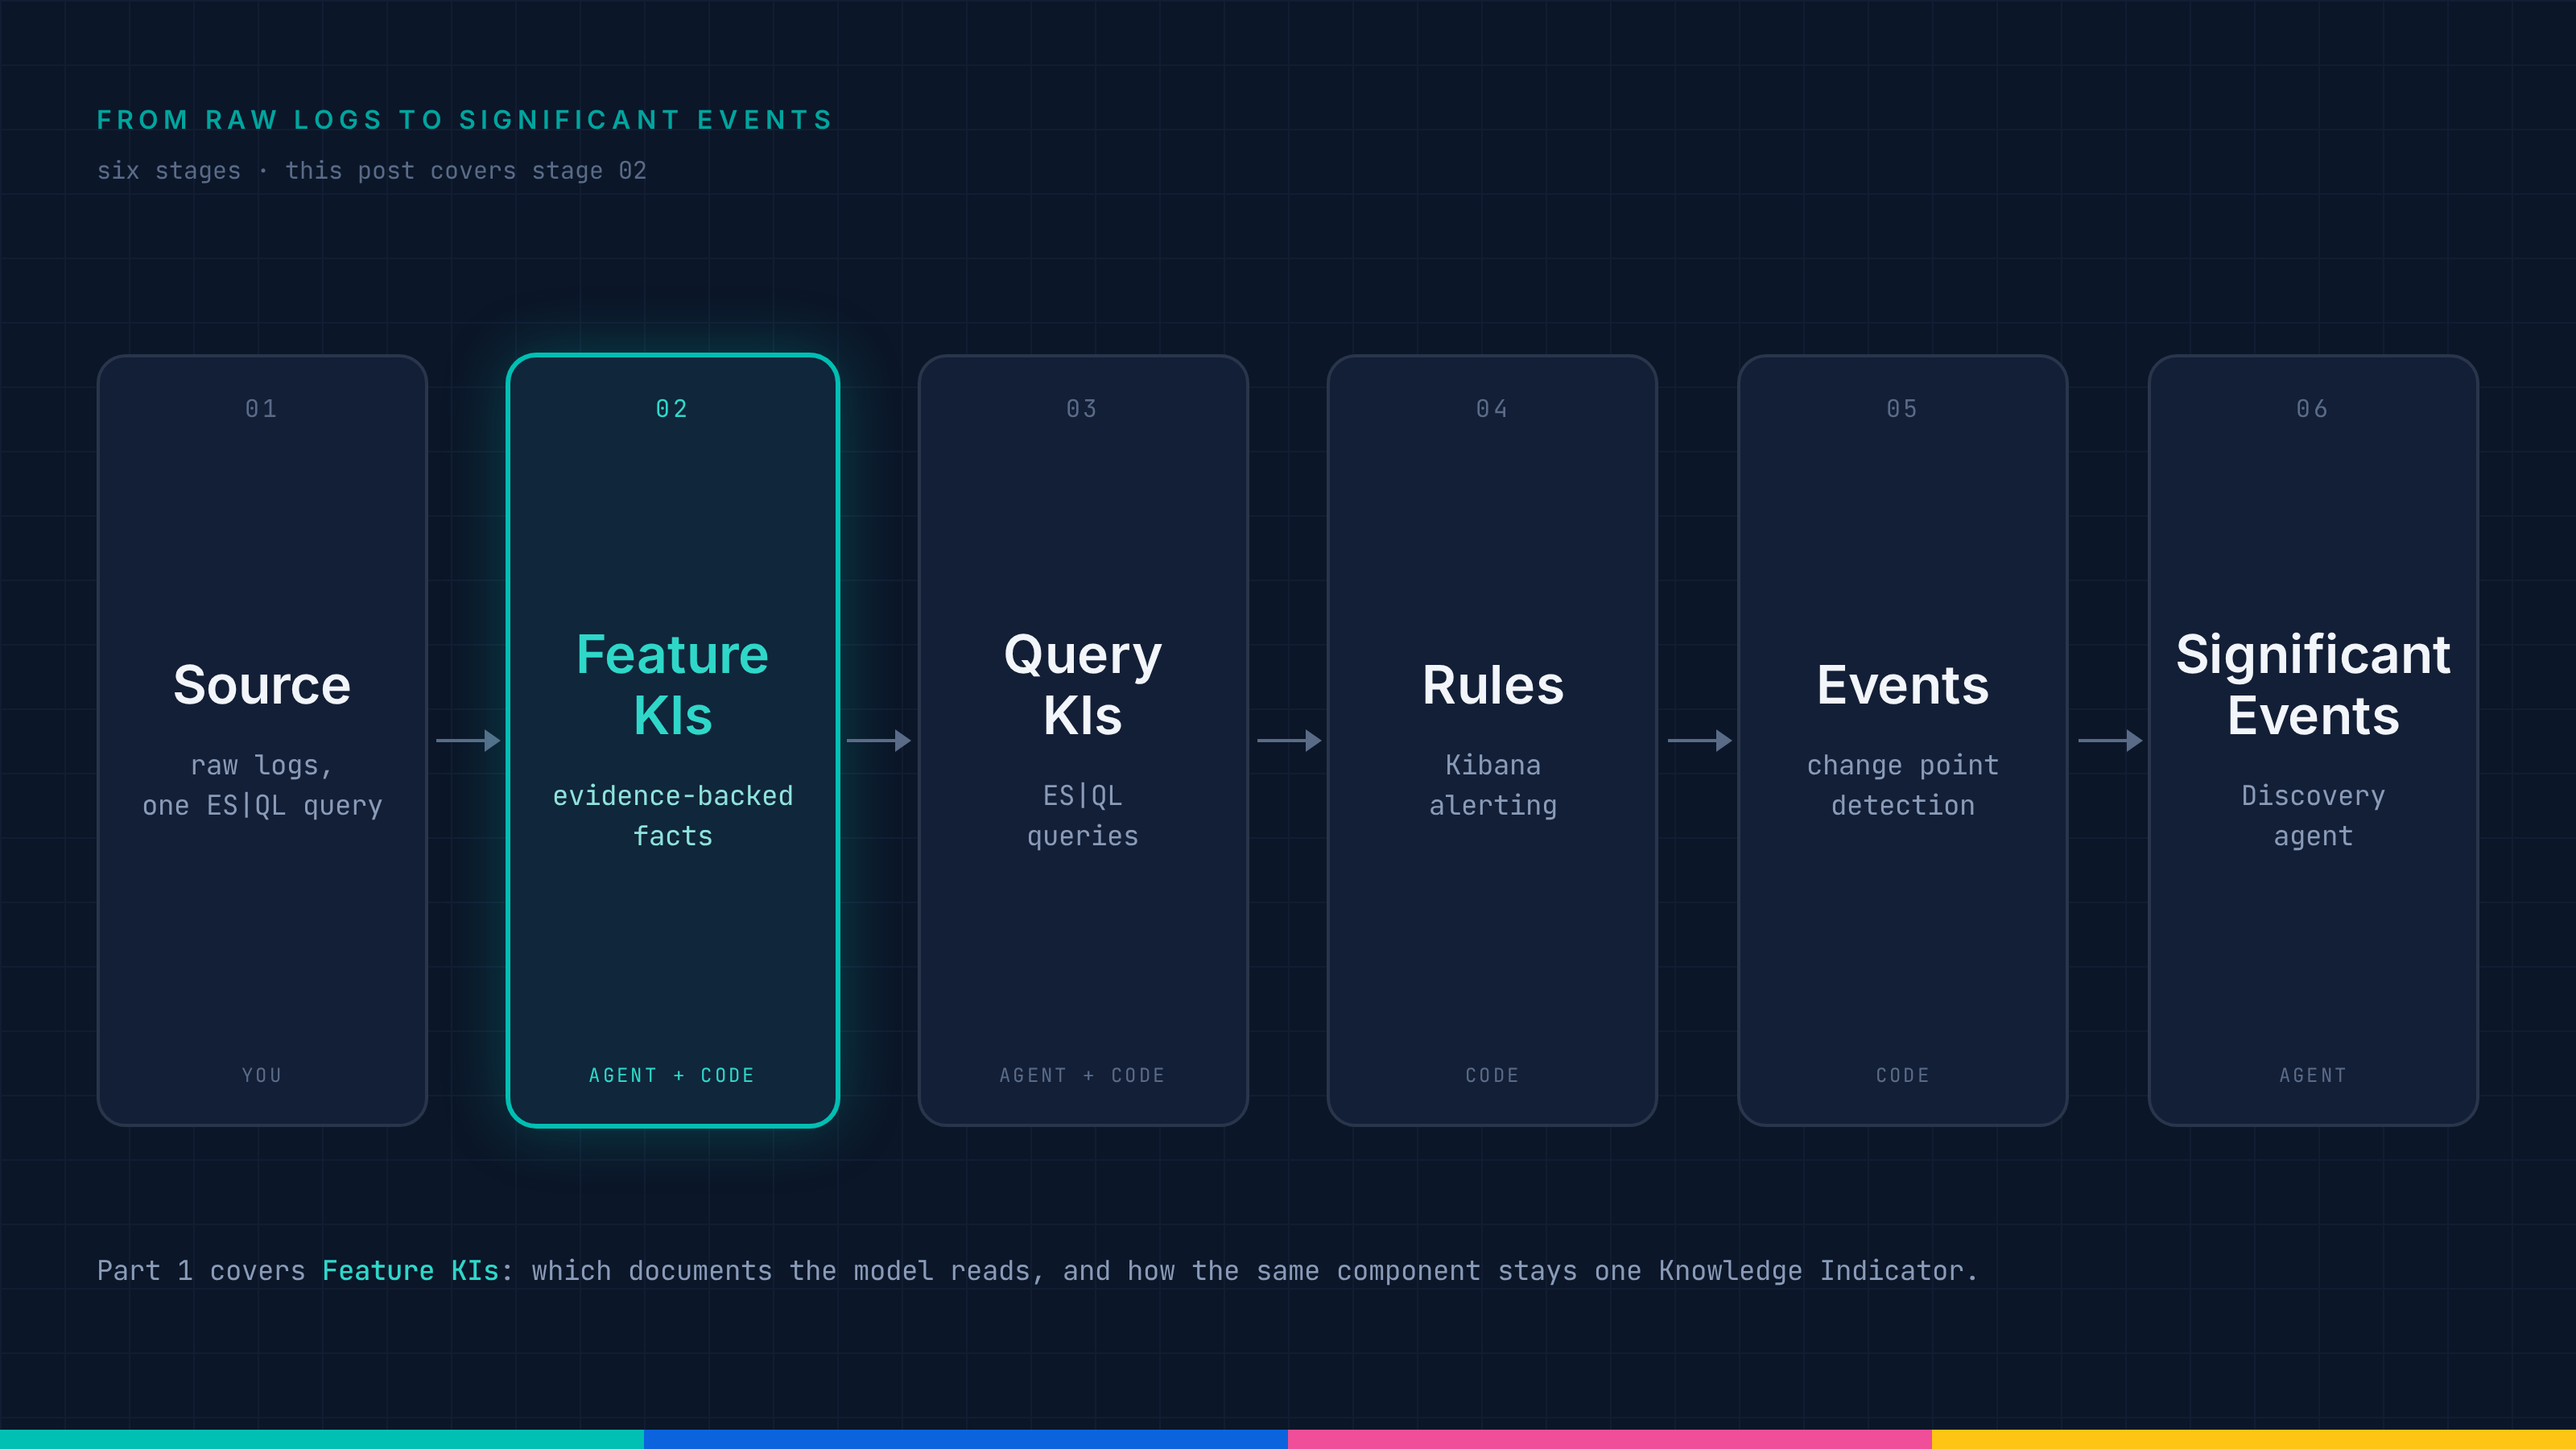
How Elastic Significant Events turns 100 log samples into detection rules
Pick the wrong 100 and you get `log.level: error`, a rule that fires on every request or finds nothing at all, and log sampling is what decides between them.
Your logs already wrote the alert: Generating ES|QL detection queries in Elasticsearch
Observability Labs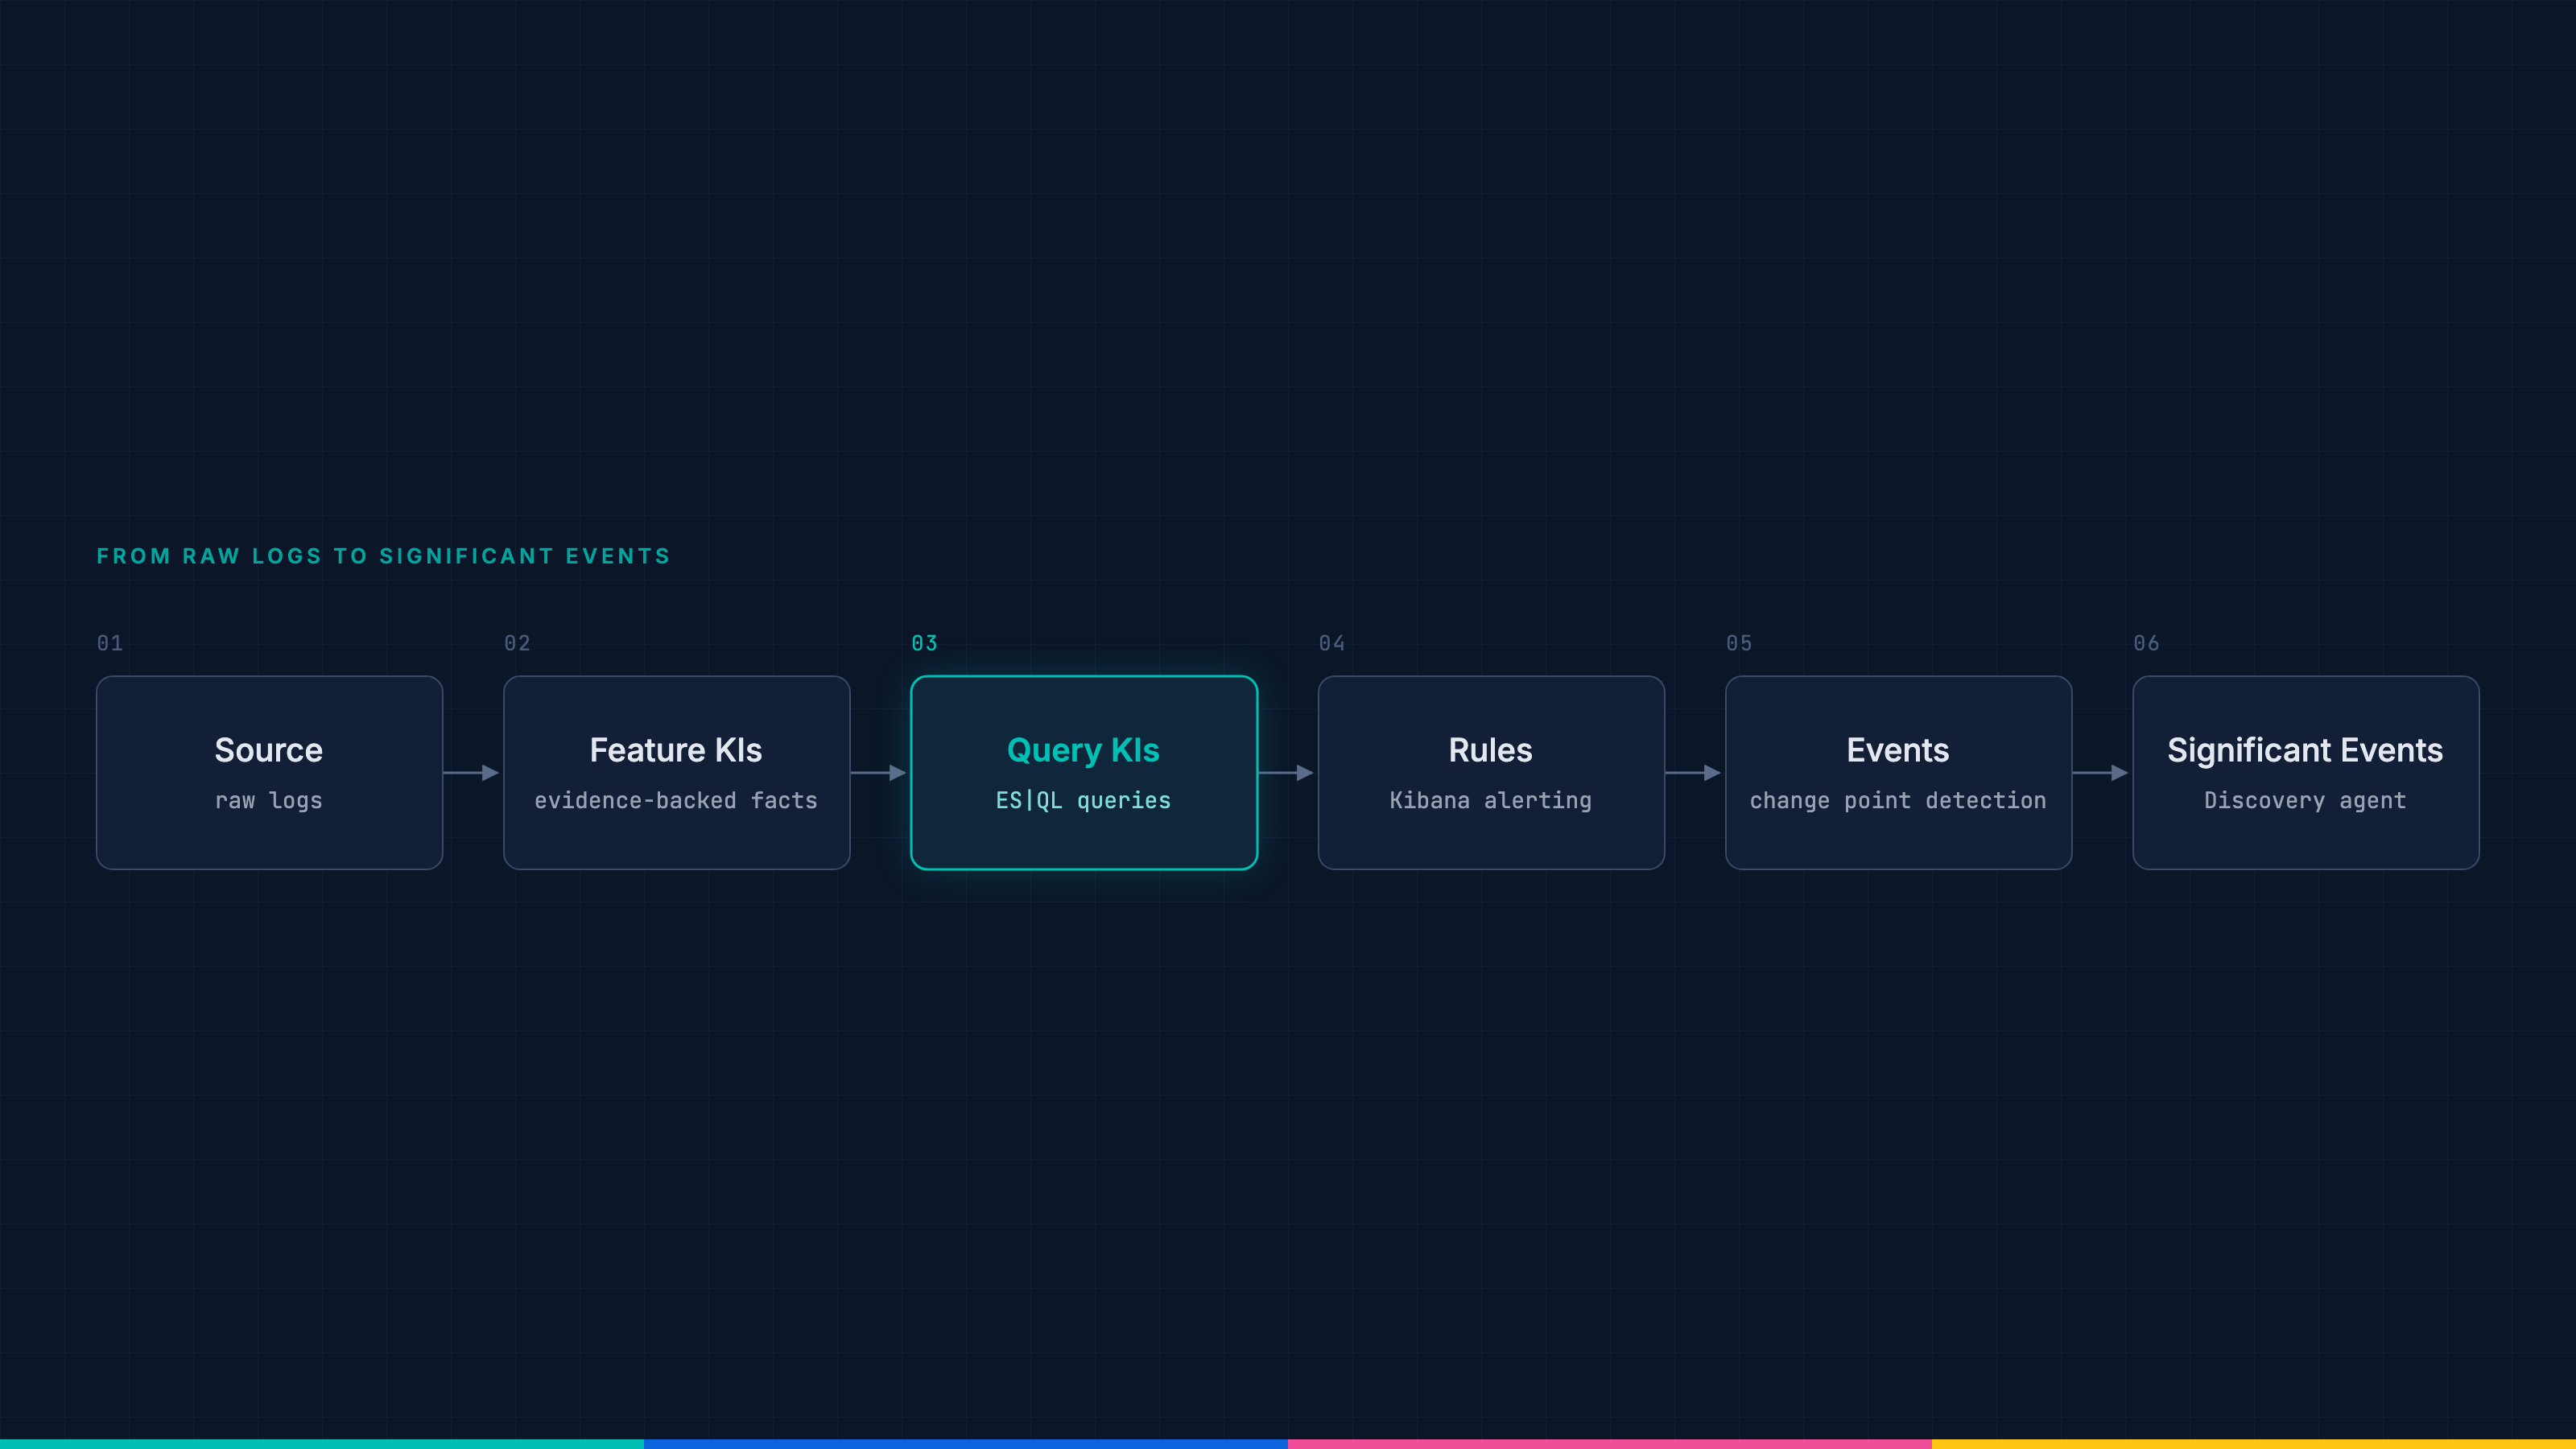
Your logs already wrote the alert: Generating ES|QL detection queries in Elasticsearch
On the OpenTelemetry demo, the top generated ES|QL detection query matches 0 documents while the shop is healthy and 676 during a payment outage.
Two rules, one outage, one alert: How change point detection cuts alert noise
Observability Labs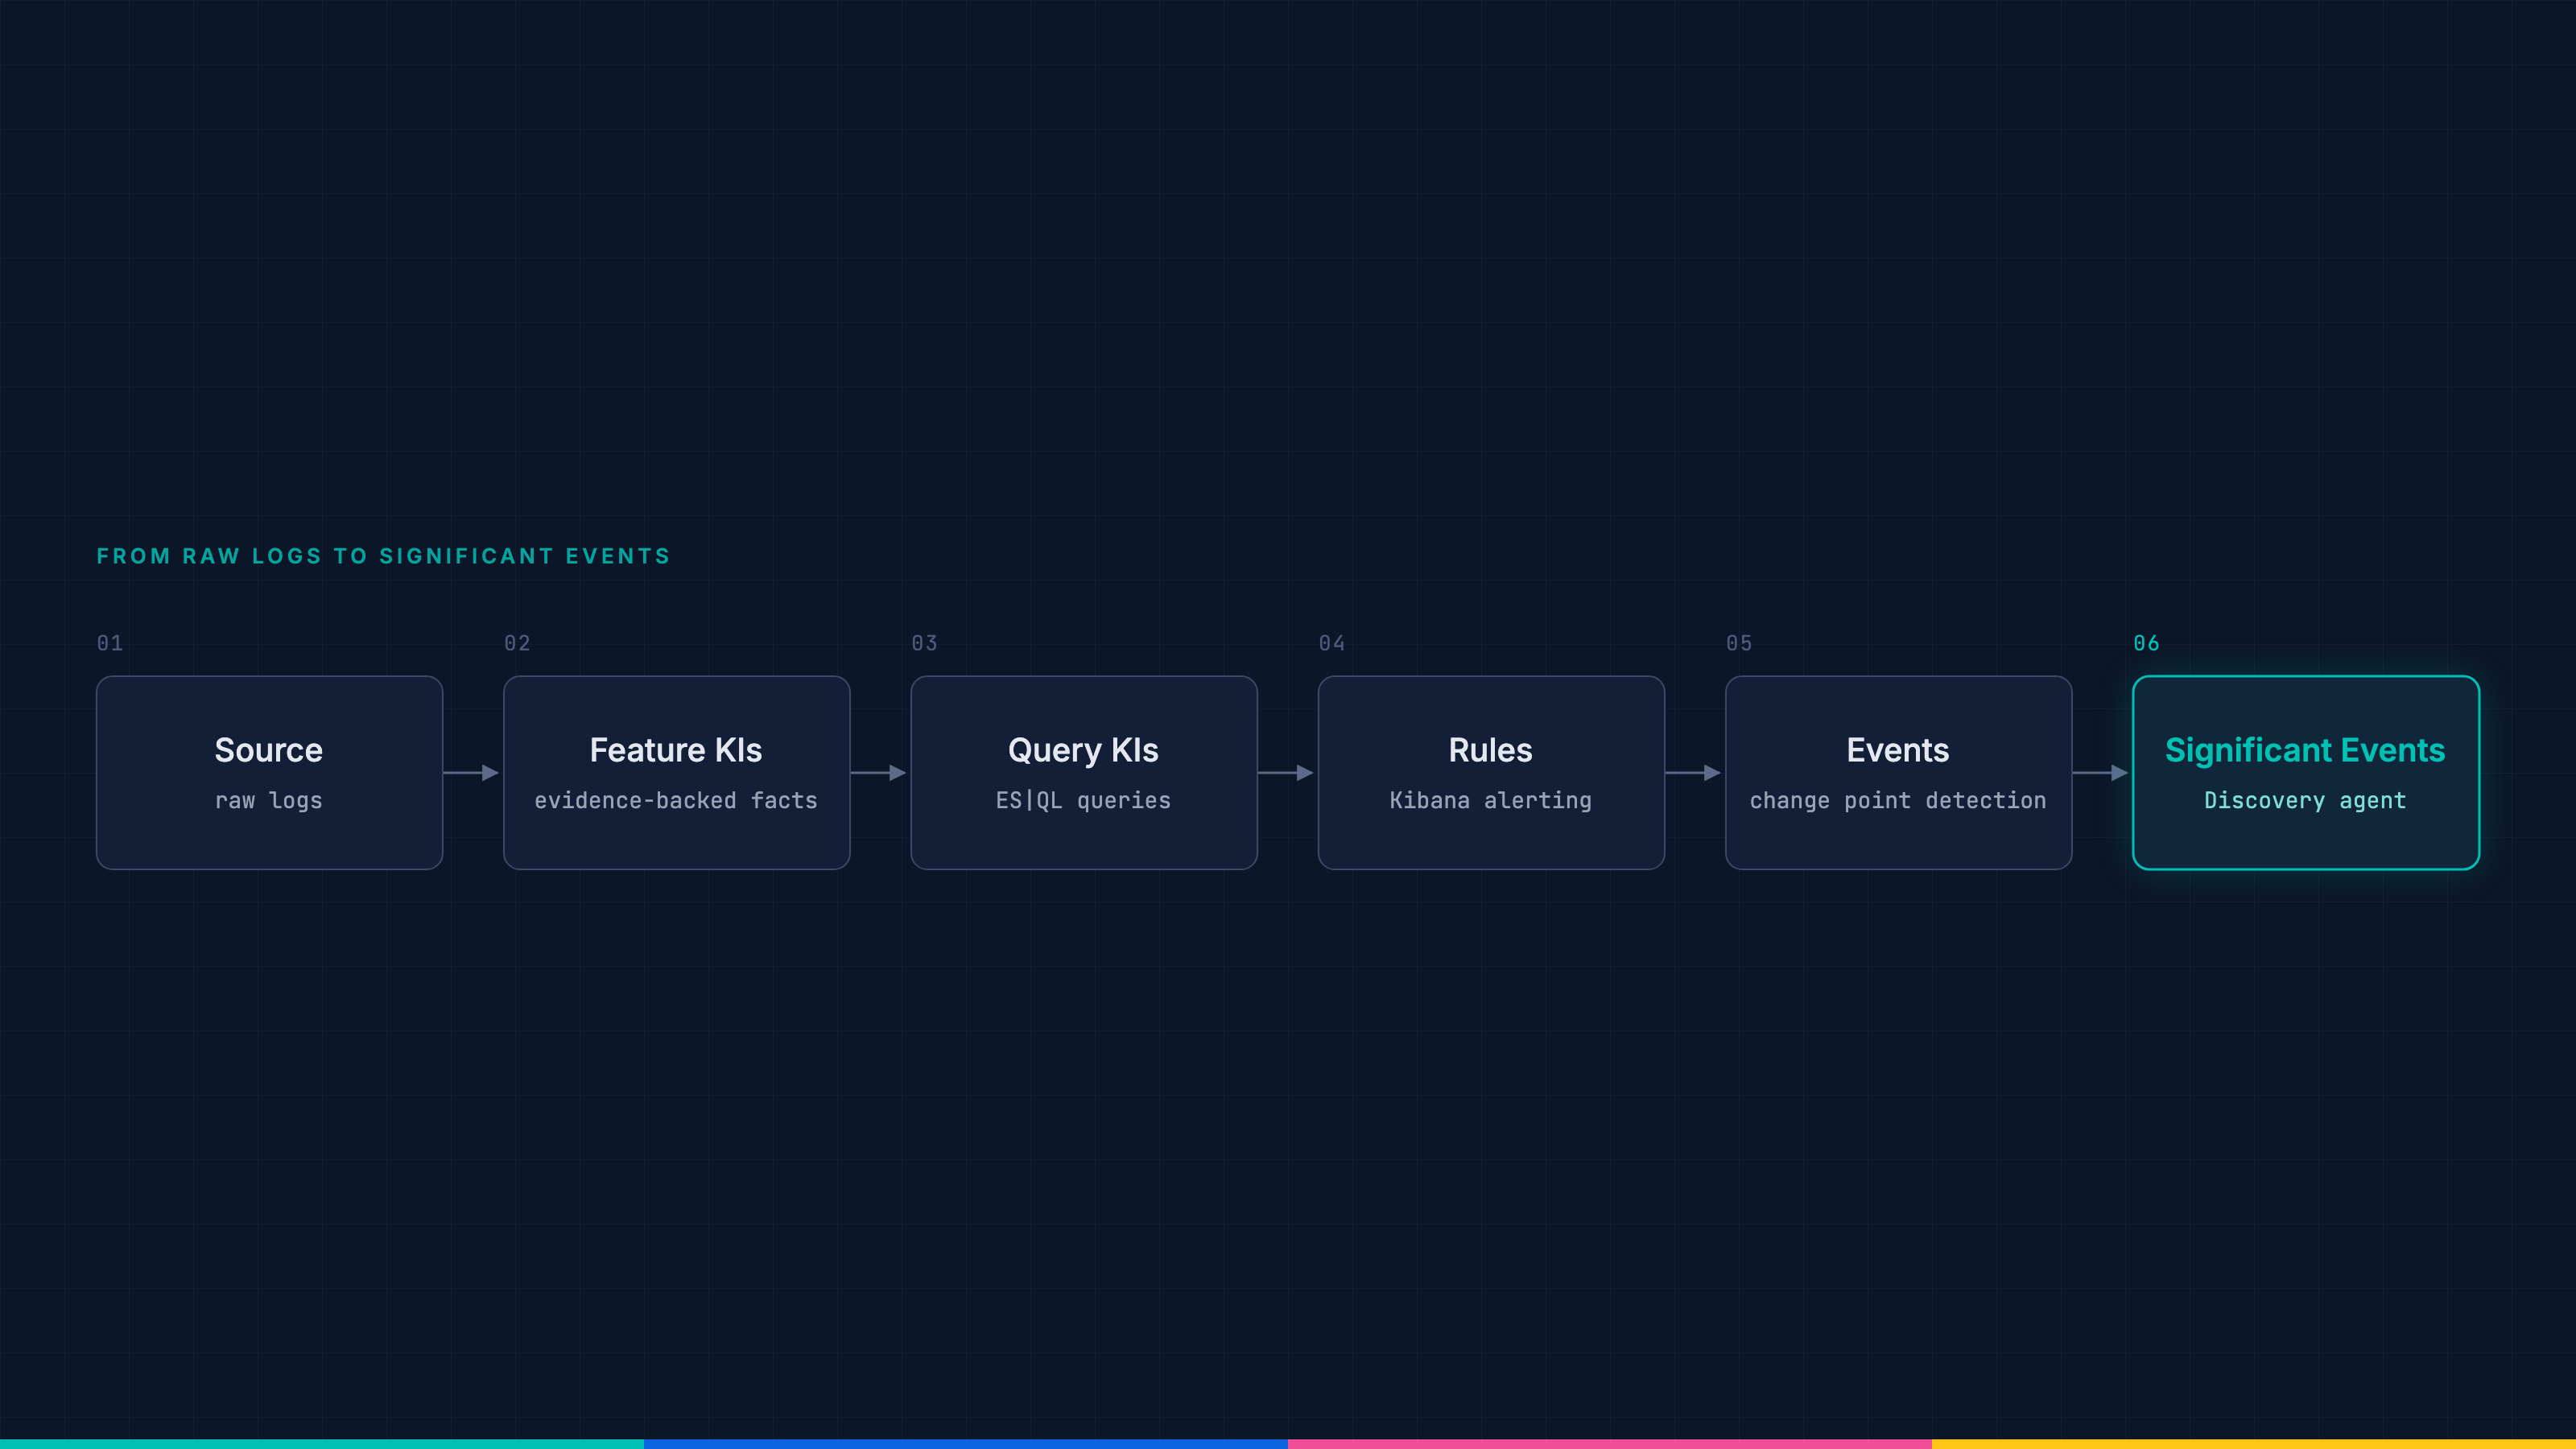
Two rules, one outage, one alert: How change point detection cuts alert noise
The discovery agent re-runs each firing rule’s own ES|QL query against the logs unchanged, so the alert names the unreachable service with the query that proves it.