Category: Threat Intelligence
Articles tagged Threat Intelligence
php2shell: Assessing Elastic detection coverage relevant to CVE-2026-109618 and CVE-2026-109619
CVE-2026-109618 and CVE-2026-109619 are critical PHP core RCE flaws that leaked ahead of disclosure. We cover what is verified, why exploitation converges on a web server spawning a shell, and the Elastic detections developed to catch this behavior.
Auditing the auditor: Unmasking Apex Accelerator
REF8801 exposes how Apex Accelerator combines convincing Web3 services with malicious npm packages, attacker-controlled AI infrastructure, and cross-platform malware delivery.
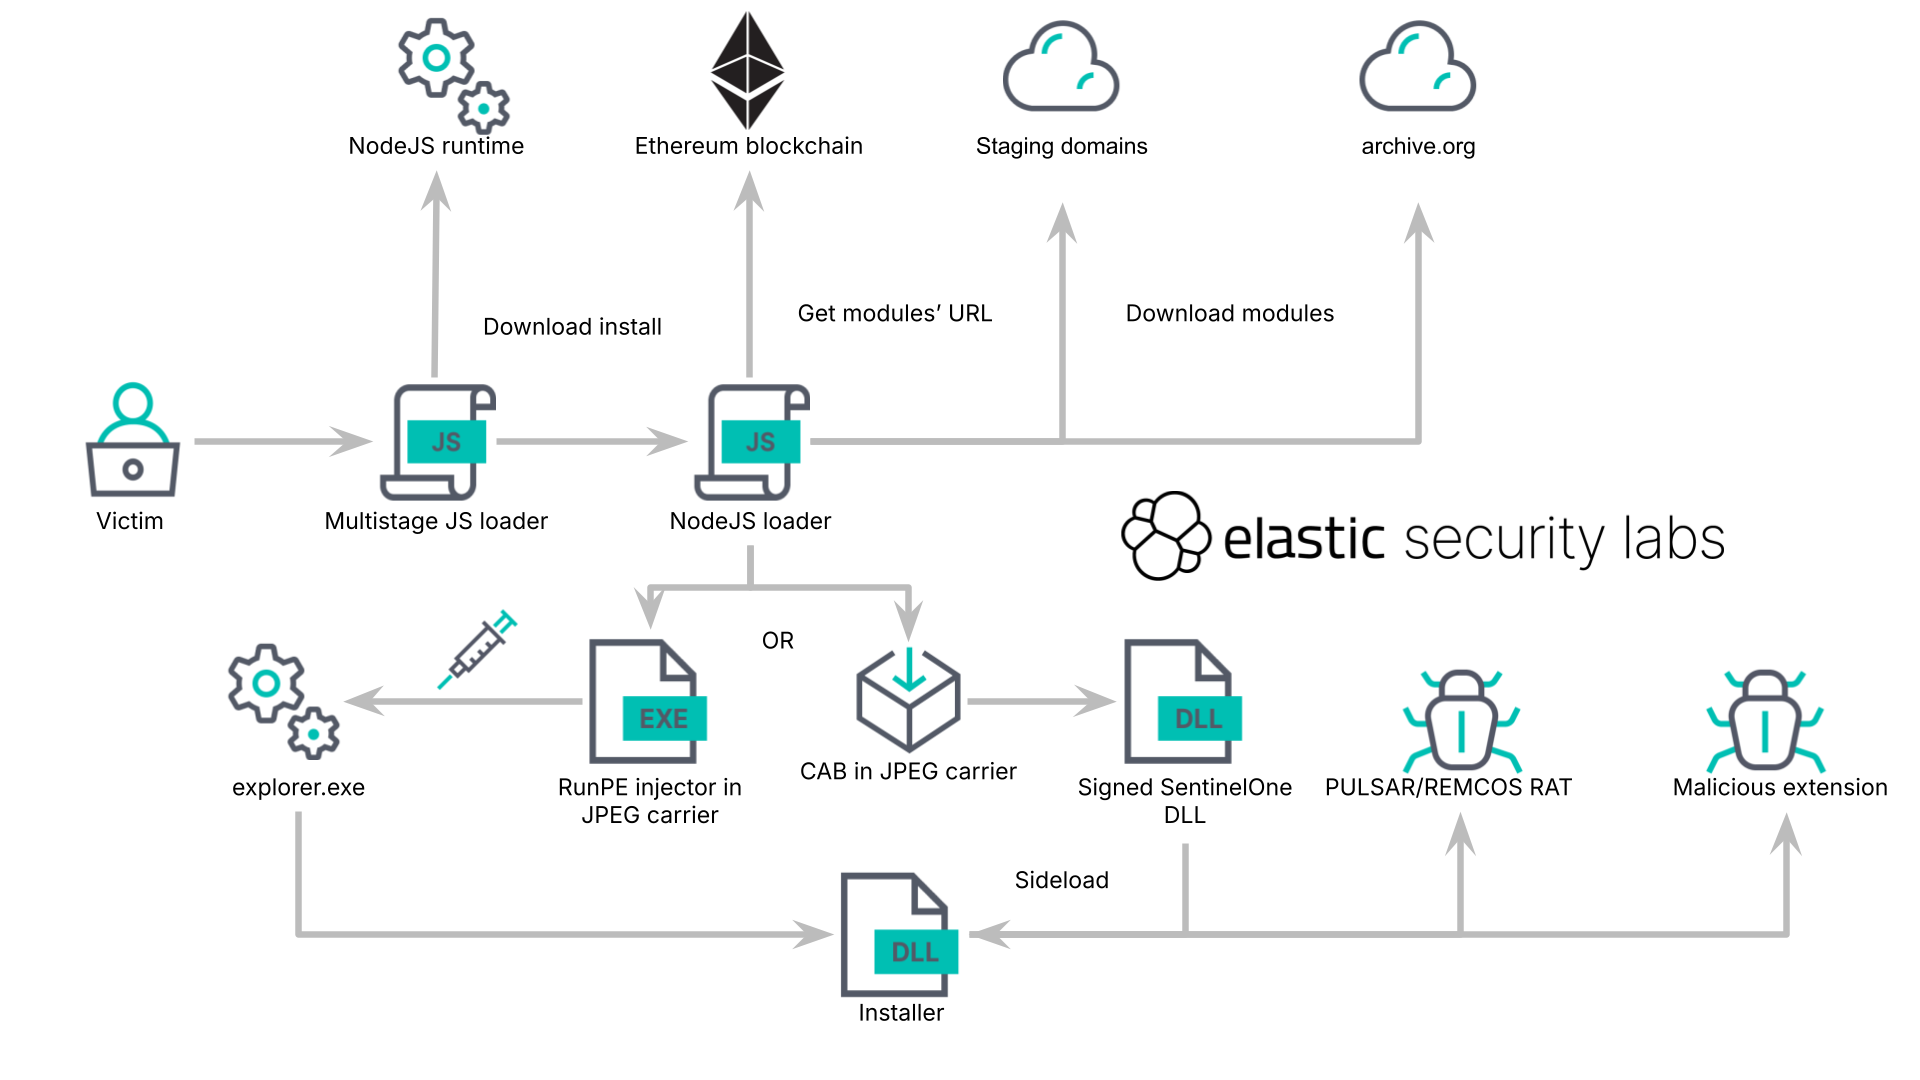
The extension you never installed: KREMLIN forges Chrome's own integrity checks to steal banking sessions
Elastic Security Labs tracked this malicious browser extension across seven campaigns and 15 months, through Brazilian bank lures and the Ethereum smart contracts that hold its C2 configuration.
REVSTEALER ramps up: analysis of up-and-coming infostealer
Elastic Security Labs deep dives into REVSTEALER, an emerging infostealer targeting browsers, wallets, and gaming accounts.
Shai-Hulud strikes again: CHAINDROP worm hits 400+ npm packages
Elastic Security Labs identified the return of Shai-Hulud. Attackers compromised the keyv maintainer and deployed CHAINDROP, a worm that uses stolen npm credentials to backdoor co-owned packages totaling over 1.3 billion monthly downloads.
New North Korean campaign uses fake coding interviews to steal developer credentials
DPRK-aligned hackers hid malware inside SVG flag images to backdoor developer job interview coding tests. Not one antivirus vendor caught it.
How we caught the Axios supply chain attack
Joe Desimone shares the story of how he caught the Axios supply chain attack with a proof of concept tool built in an afternoon.
Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER
Elastic Security Labs observed two custom malware components targeting a South Asian financial institution: a modular backdoor with USB-based spreading and a DLL-side-loaded keylogger.
Taking SHELLTER: a commercial evasion framework abused in-the-wild
Elastic Security Labs detected the recent emergence of infostealers using an illicitly acquired version of the commercial evasion framework, SHELLTER, to deploy post-exploitation payloads.
Bit ByBit - emulation of the DPRK's largest cryptocurrency heist
A high-fidelity emulation of the DPRK's largest cryptocurrency heist via a compromised macOS developer and AWS pivots.
From South America to Southeast Asia: The Fragile Web of REF7707
REF7707 targeted a South American foreign ministry using novel malware families. Inconsistent evasion tactics and operational security missteps exposed additional adversary-owned infrastructure.
GrimResource - Microsoft Management Console for initial access and evasion
Elastic researchers uncovered a new technique, GrimResource, which allows full code execution via specially crafted MSC files. It underscores a trend of well-resourced attackers favoring innovative initial access methods to evade defenses.