Category: AI Security
Articles tagged AI Security
Auditing the auditor: Unmasking Apex Accelerator
REF8801 exposes how Apex Accelerator combines convincing Web3 services with malicious npm packages, attacker-controlled AI infrastructure, and cross-platform malware delivery.
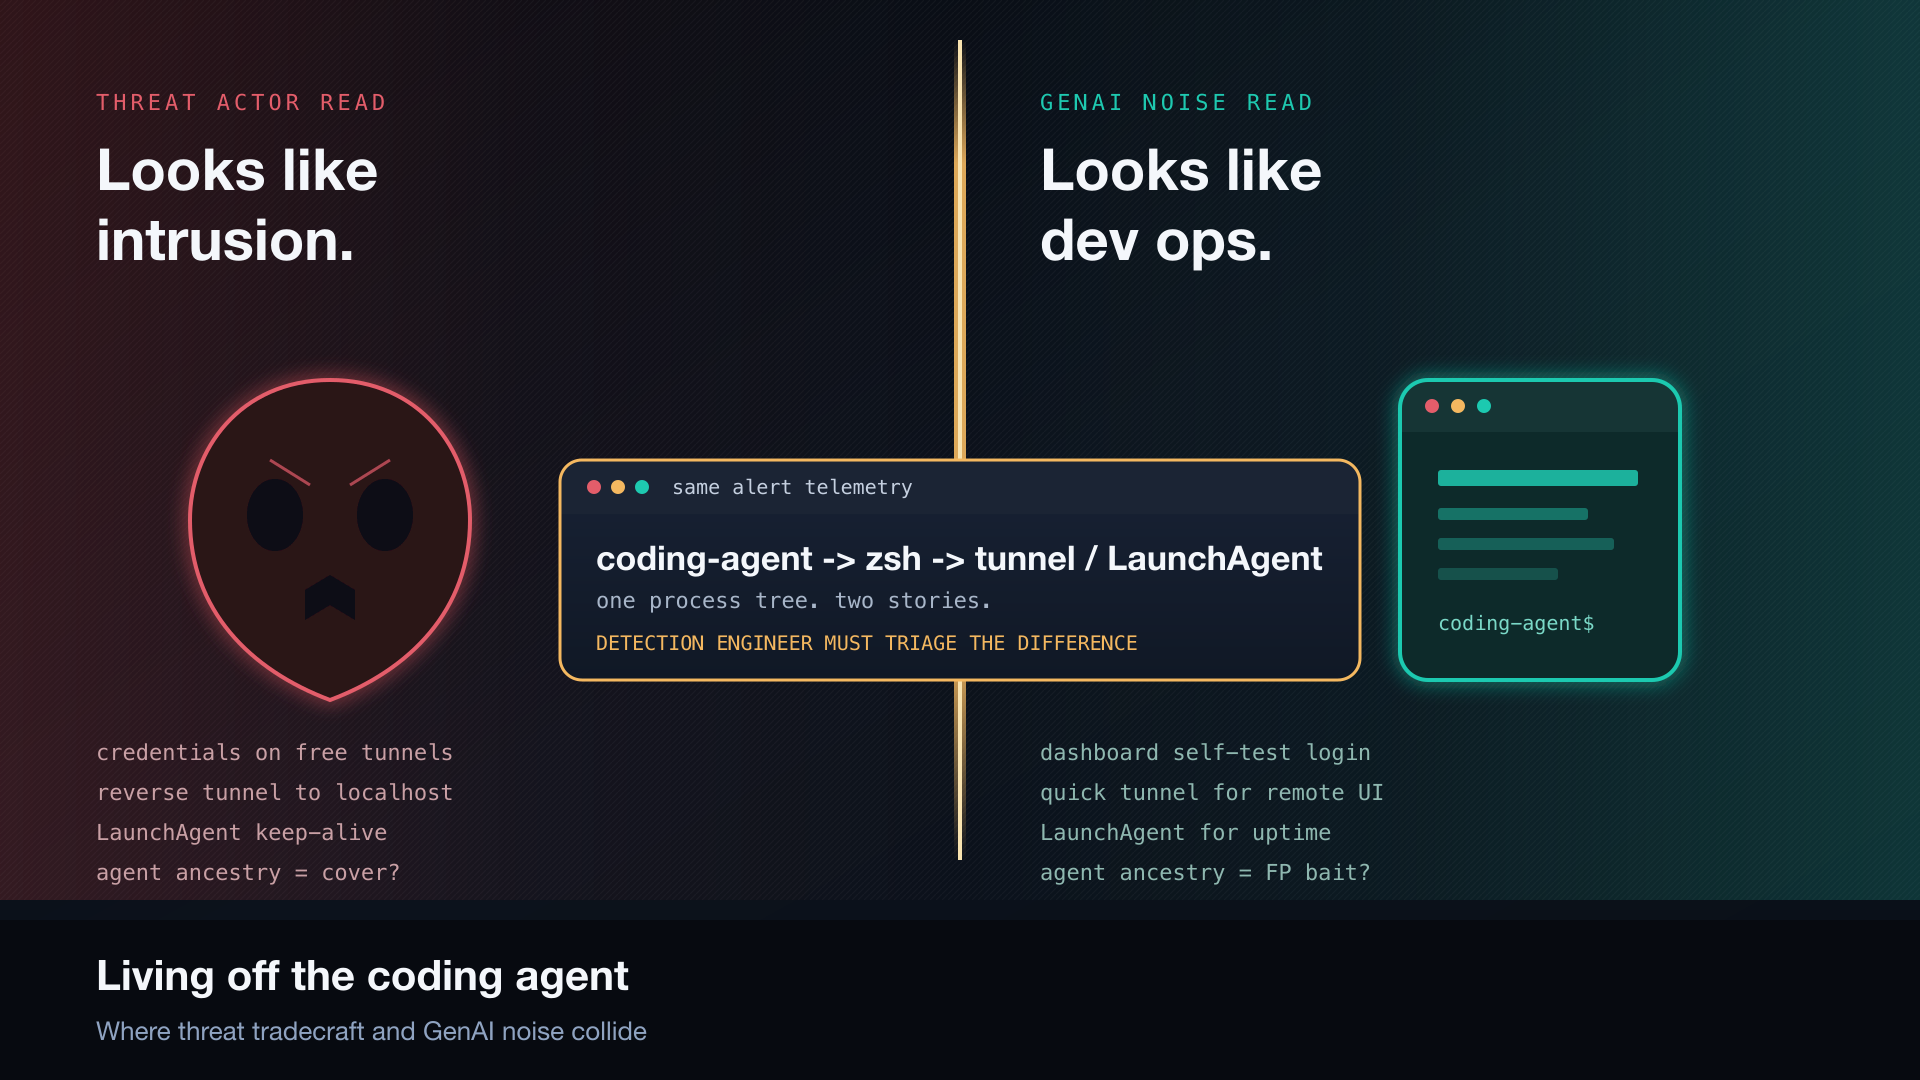
Living off the coding agent: Two tales of tunnels and LaunchAgents
Agent-parented reverse tunnels and LaunchAgents can expose a local admin app to the internet. Endpoint still needs to treat that as high severity even when the activity looks like vibe-coded ops, not confirmed malware.
The Cost of Understanding: LLM-Driven Reverse Engineering vs Iterative LLM Obfuscation
Elastic Security Labs explores the ongoing arms race between LLM-driven reverse engineering and obfuscation.
MCP Tools: Attack Vectors and Defense Recommendations for Autonomous Agents
This research examines how Model Context Protocol (MCP) tools expand the attack surface for autonomous agents, detailing exploit vectors such as tool poisoning, orchestration injection, and rug-pull redefinitions alongside practical defense strategies.
Elastic Advances LLM Security with Standardized Fields and Integrations
Discover Elastic’s latest advancements in LLM security, focusing on standardized field integrations and enhanced detection capabilities. Learn how adopting these standards can safeguard your systems.
Embedding Security in LLM Workflows: Elastic's Proactive Approach
Dive into Elastic's exploration of embedding security directly within Large Language Models (LLMs). Discover our strategies for detecting and mitigating several of the top OWASP vulnerabilities in LLM applications, ensuring safer and more secure AI-driven applications.