攻撃の発見
Attack Discoveryは、数百件ものアラートをトリアージして本当に重要な数件の攻撃に絞り込み、直感的なインターフェースで結果を返します。これにより、提示された攻撃を迅速に理解し、即座にフォローアップアクションを実行できるようになります。
Elastic Searchを14日間無料でお試しいただき、これらの機能をさらに深くテストしてください。
類似のデモを探す

Security
Accelerate data onboarding with Elastic AI Import
Elastic’s Automatic Import feature saves analysts from the lengthy process of building custom data parsers, allowing them to instead focus on threat hunting and improve their organization’s security posture. In this demo, see how Elastic AI Import feature can process both supported or unsupported log sources, normalizing and enriching them for analysts.
Security
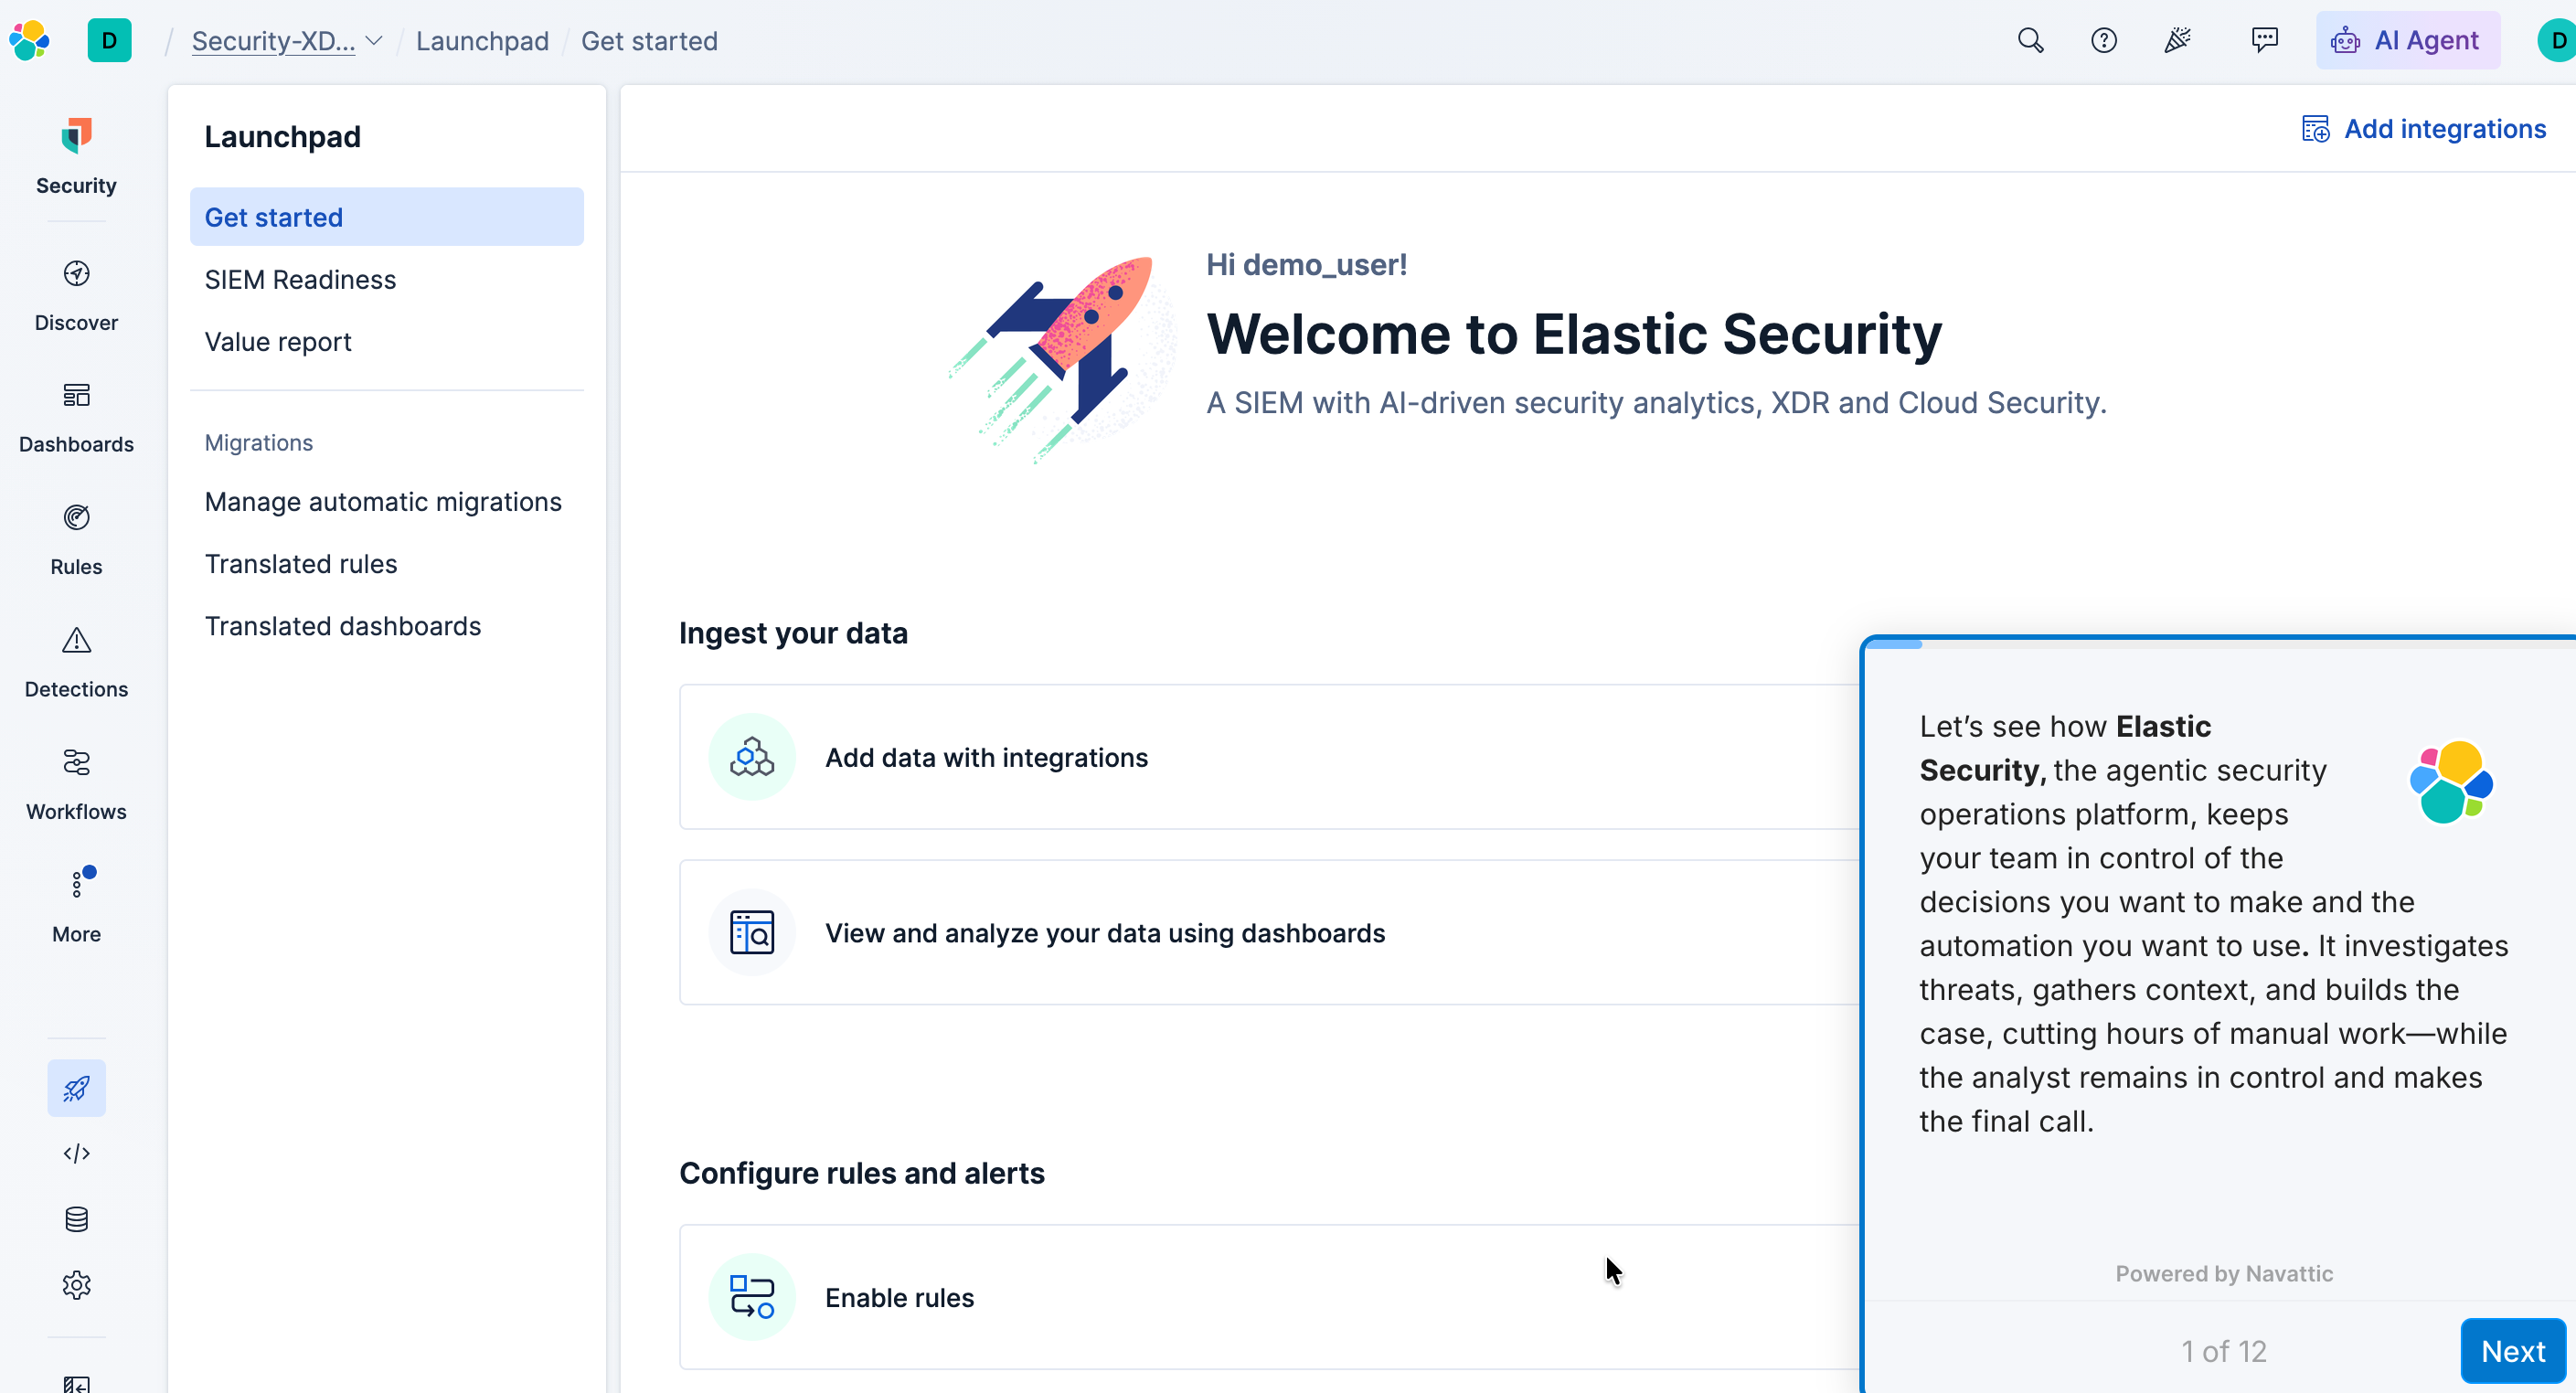
Elastic Security: Agentic Security Operations Platform
Step through Elastic’s agentic SOC live. Watch autonomous agents correlate and investigate a real alert end-to-end, then stage a response through Elastic Workflows—with deterministic playbooks and agentic reasoning working side by side. You stay in control at every gate, approving agent actions and seeing exactly how judgment and verification remain with the analyst while the busywork runs itself.
Security
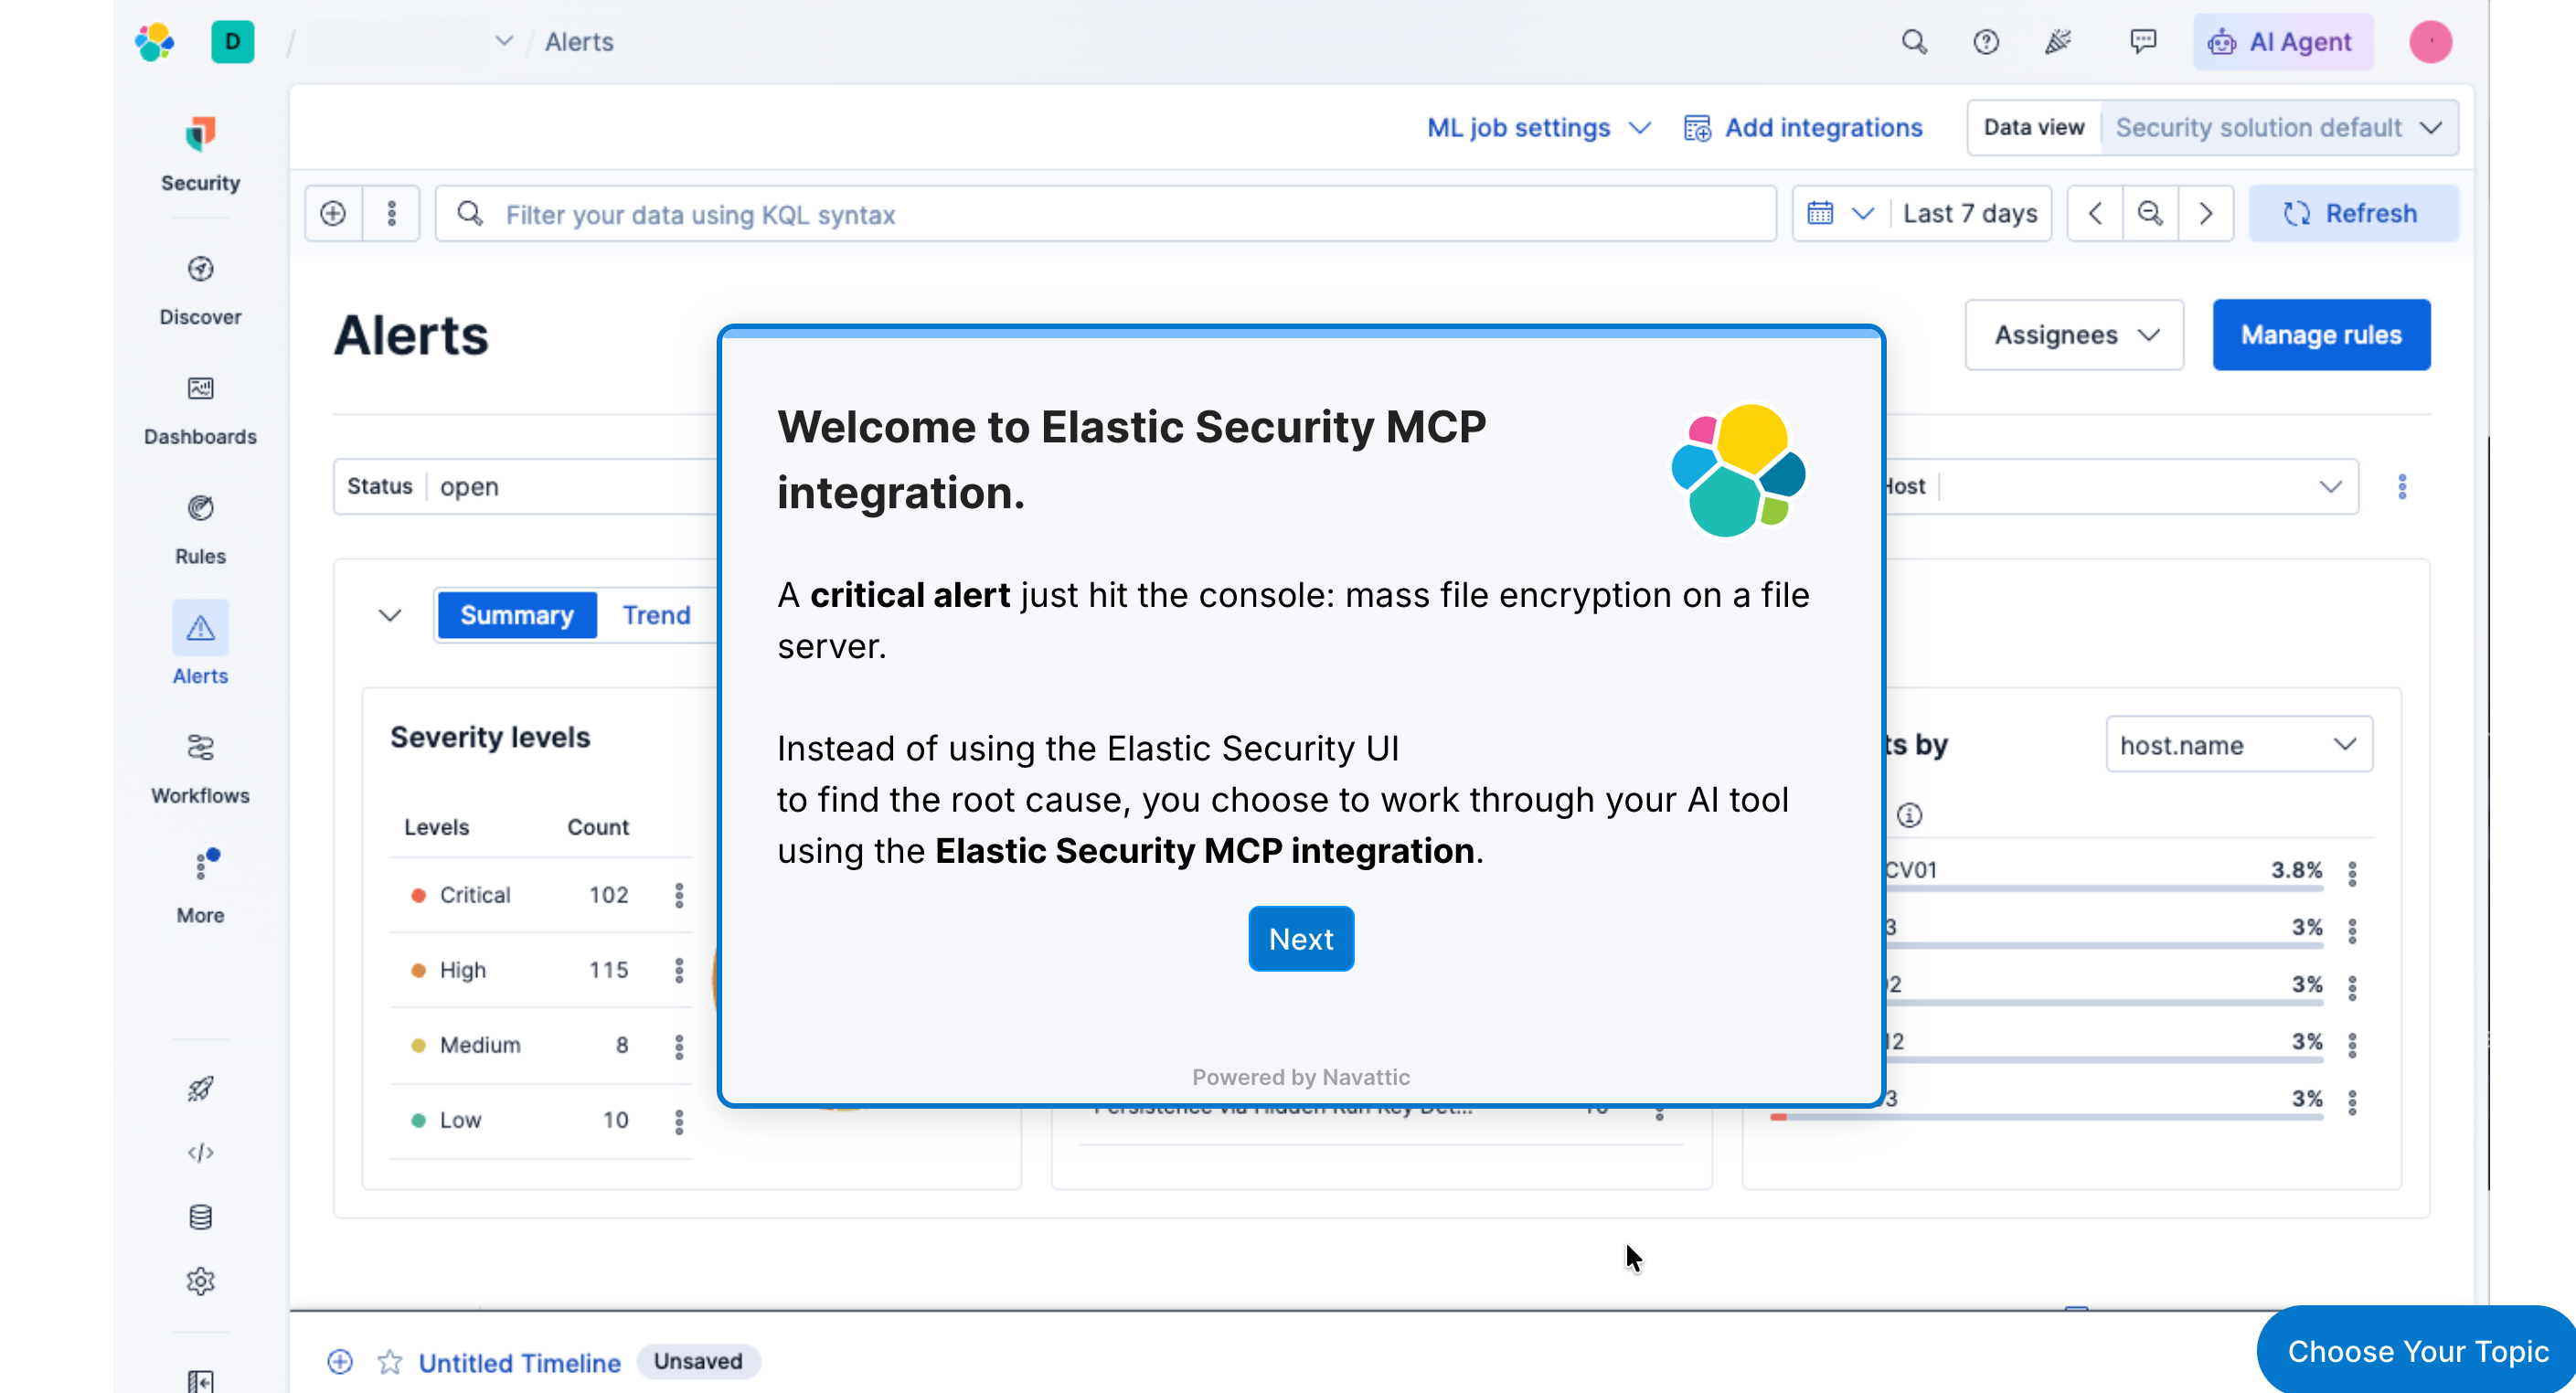
Elastic Security MCP Integration
A critical alert just hit the Elastic Security console: mass file encryption on a file server. Instead of using the web UI to find the root cause, you choose to work through your AI tool using the Elastic Security MCP integration.