Elasticデモギャラリー
KibanaダッシュボードやCanvasワークパッドから、ElasticsearchのSQLスニペットや機械学習ジョブまで、Elastic Stackの多彩な側面を体験できる小さなサンプル集です。実際に試してみる方が、ただ見るよりもずっと実感を持てます。

フィルター
タイプ
ソリューション
Elasticの機能
Observability
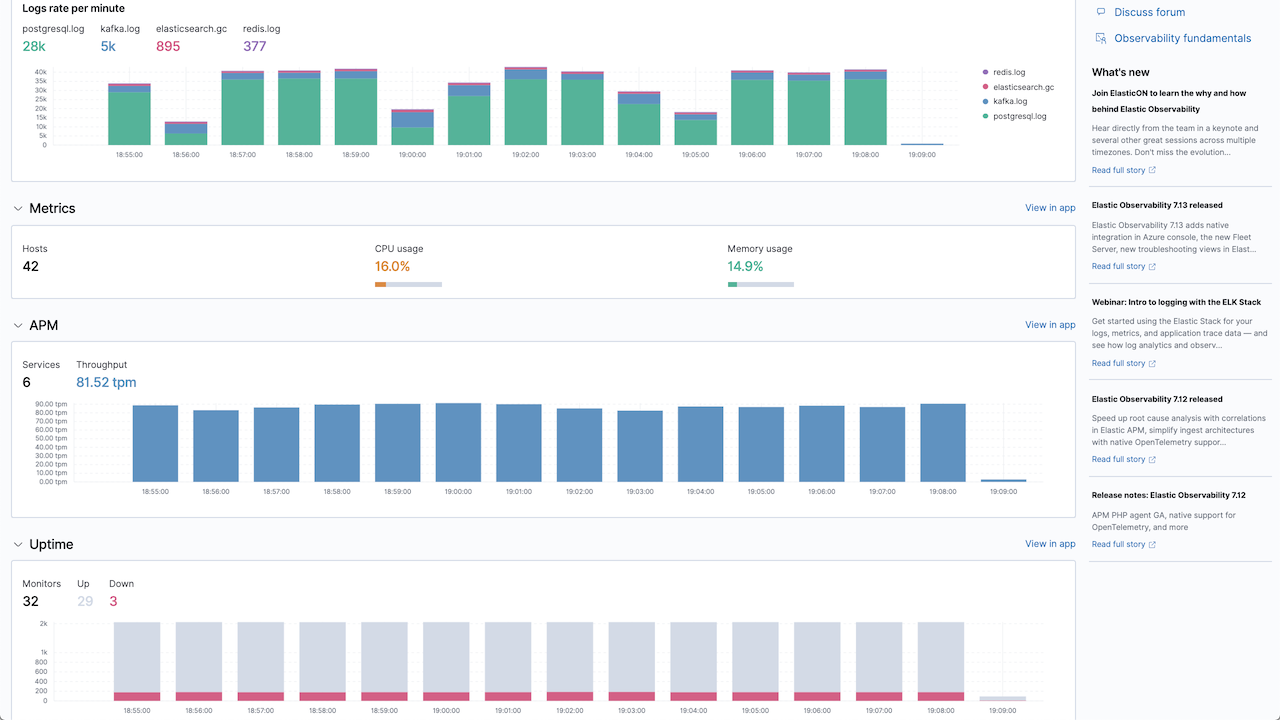
Observabilityの概要
このハンズオンデモを試して、ログ、メトリック、トレースを組み合わせてアプリケーション環境を包括的に可視化する方法を学びましょう。
Security
Accelerate data onboarding with Elastic AI Import
Elastic’s Automatic Import feature saves analysts from the lengthy process of building custom data parsers, allowing them to instead focus on threat hunting and improve their organization’s security posture. In this demo, see how Elastic AI Import feature can process both supported or unsupported log sources, normalizing and enriching them for analysts.
Security
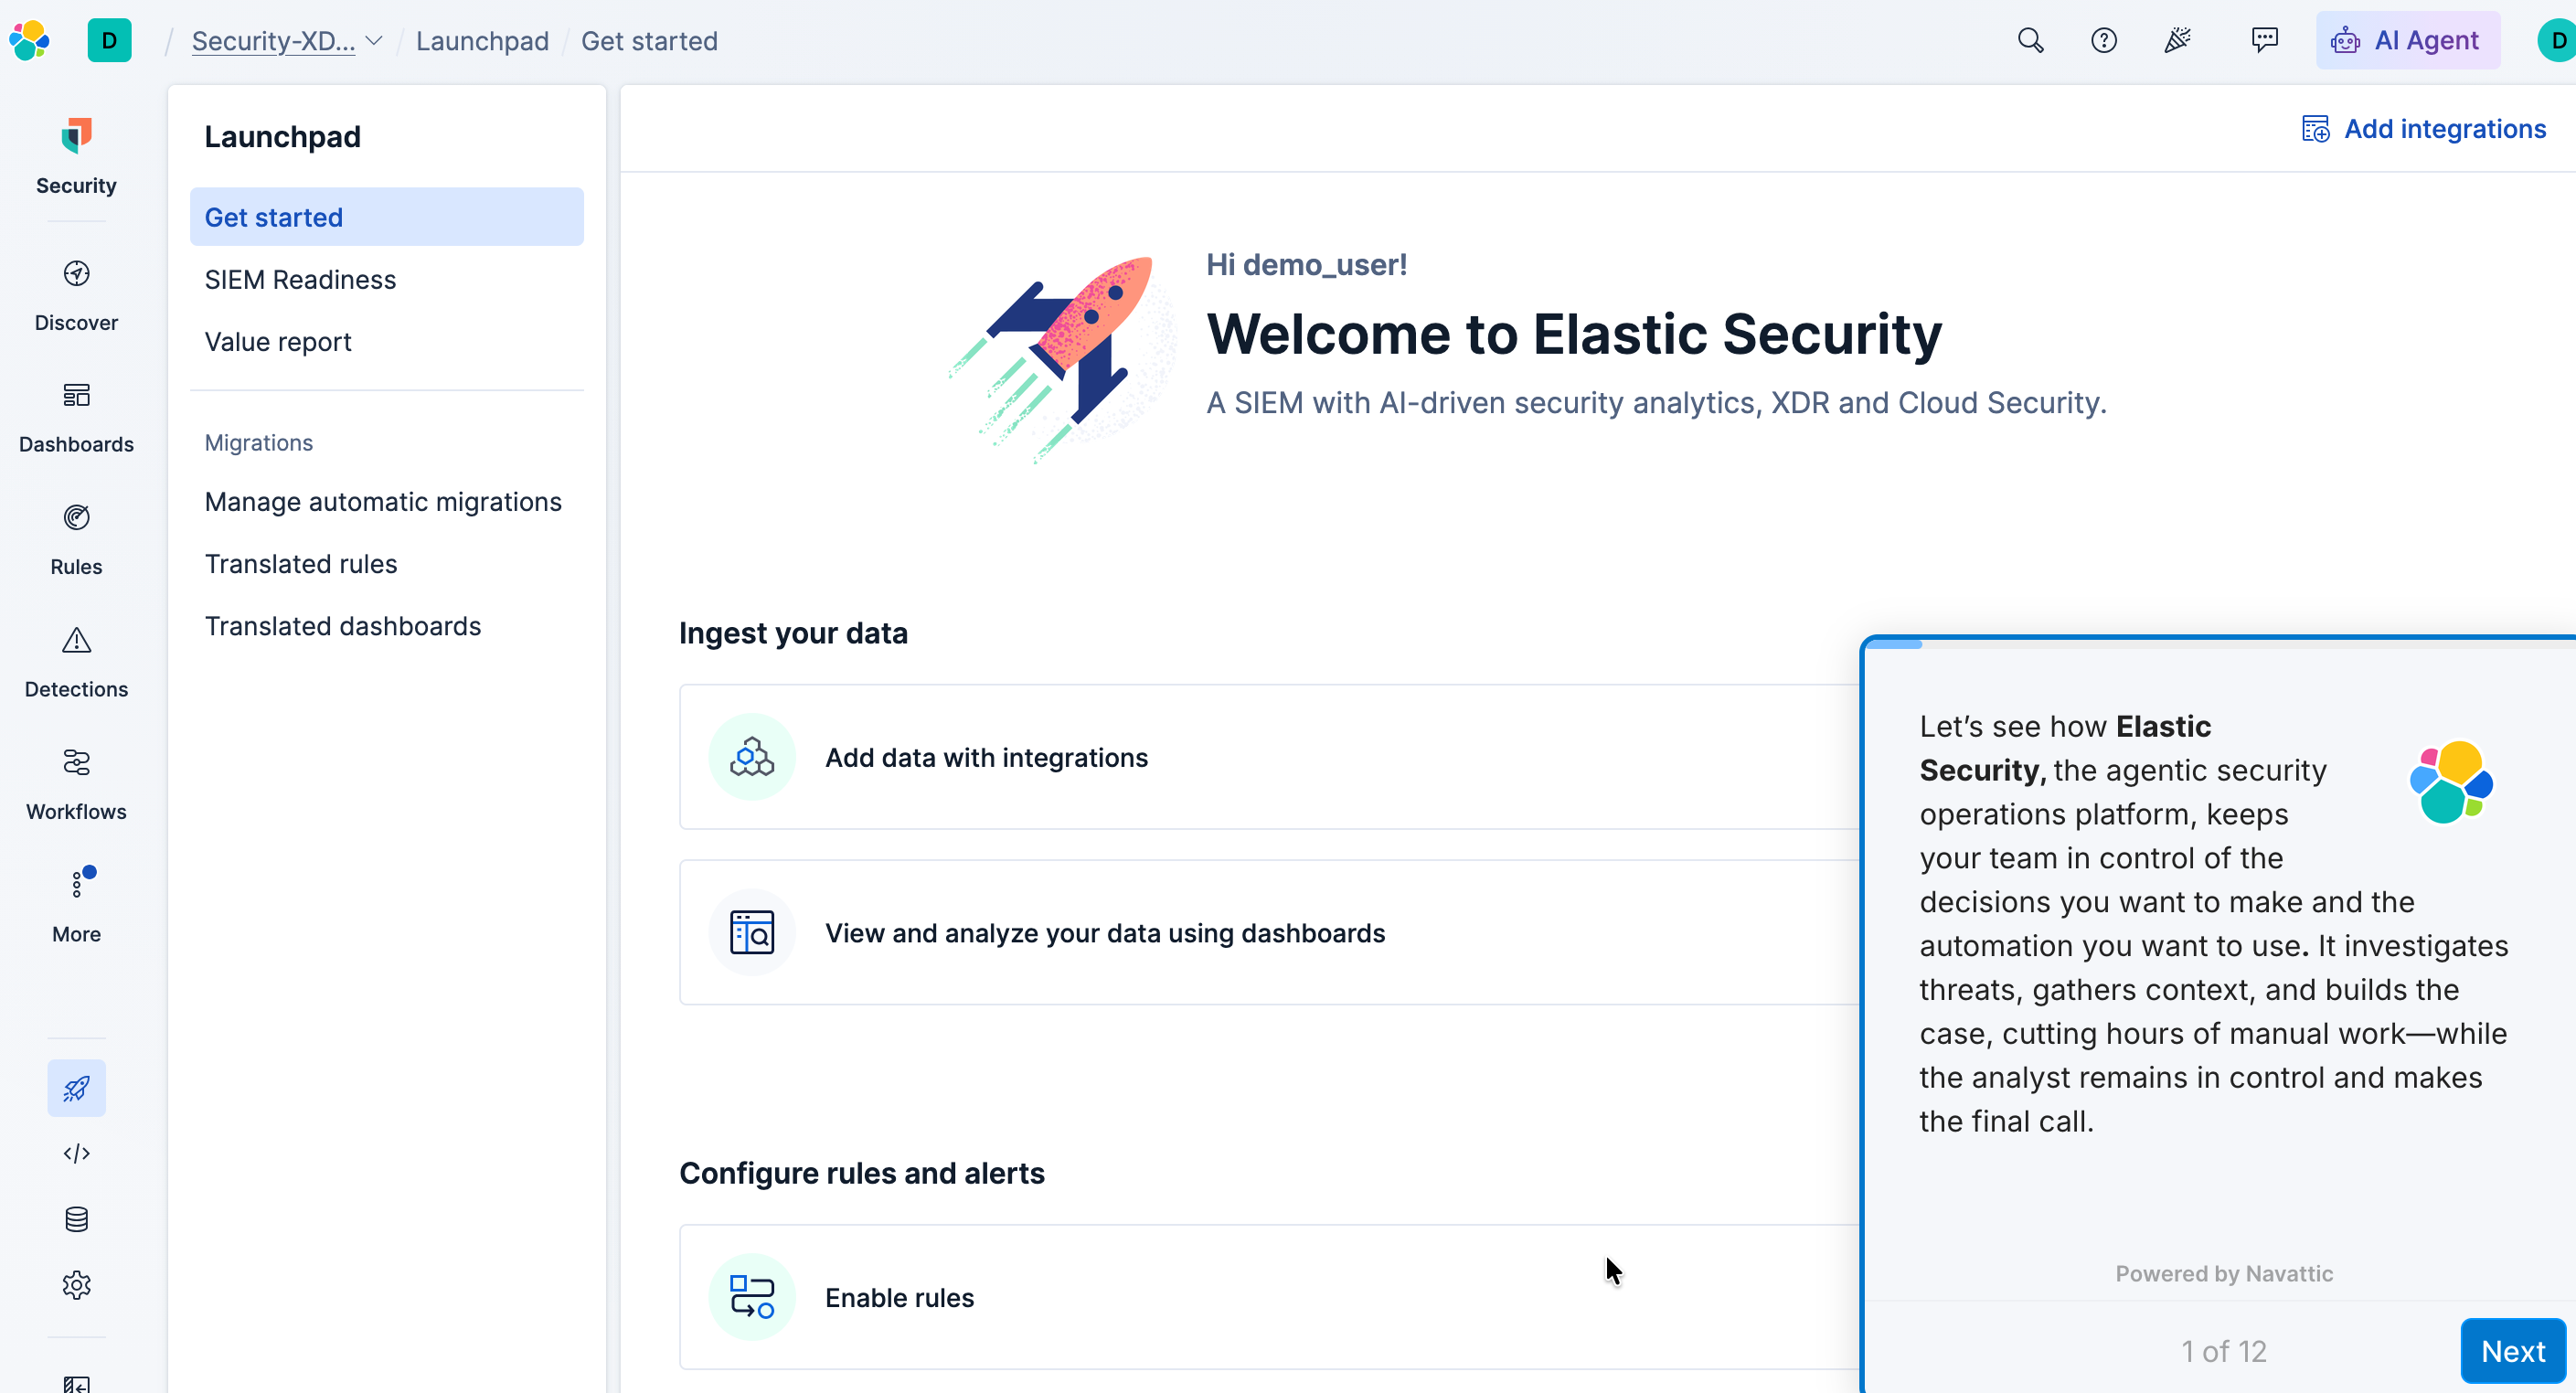
Elastic Security: Agentic Security Operations Platform
Step through Elastic’s agentic SOC live. Watch autonomous agents correlate and investigate a real alert end-to-end, then stage a response through Elastic Workflows—with deterministic playbooks and agentic reasoning working side by side. You stay in control at every gate, approving agent actions and seeing exactly how judgment and verification remain with the analyst while the busywork runs itself.
Security
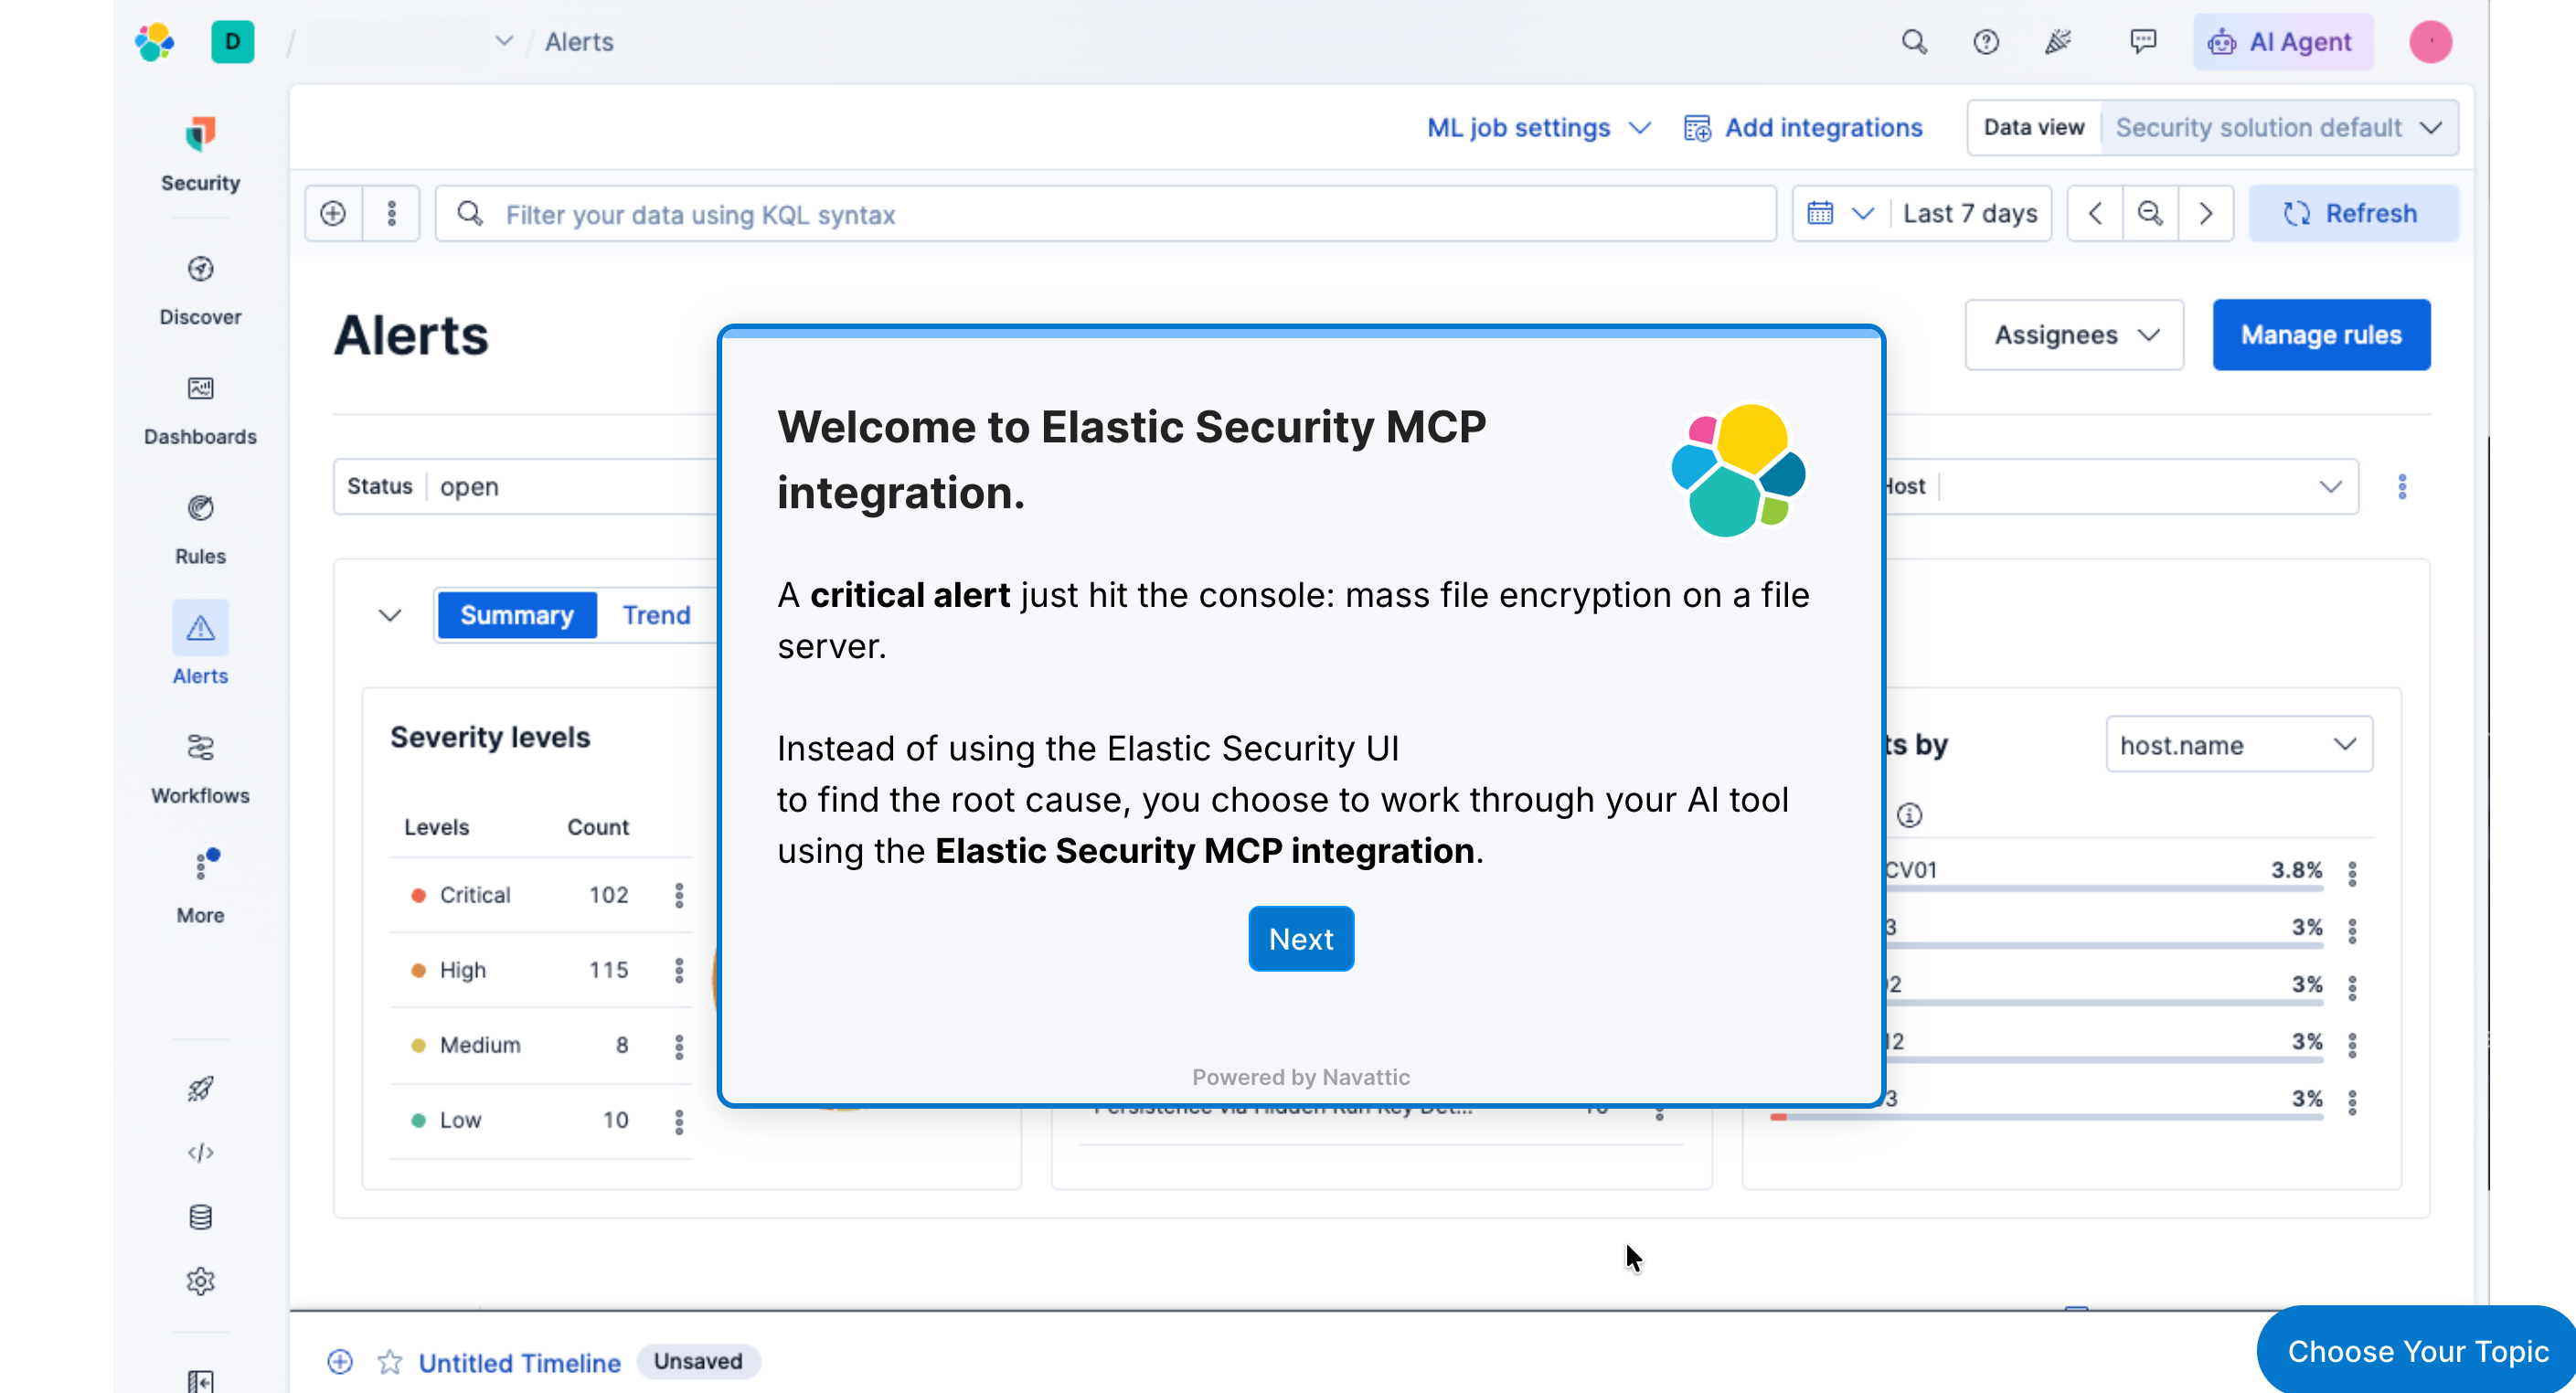
Elastic Security MCP Integration
A critical alert just hit the Elastic Security console: mass file encryption on a file server. Instead of using the web UI to find the root cause, you choose to work through your AI tool using the Elastic Security MCP integration.
Security
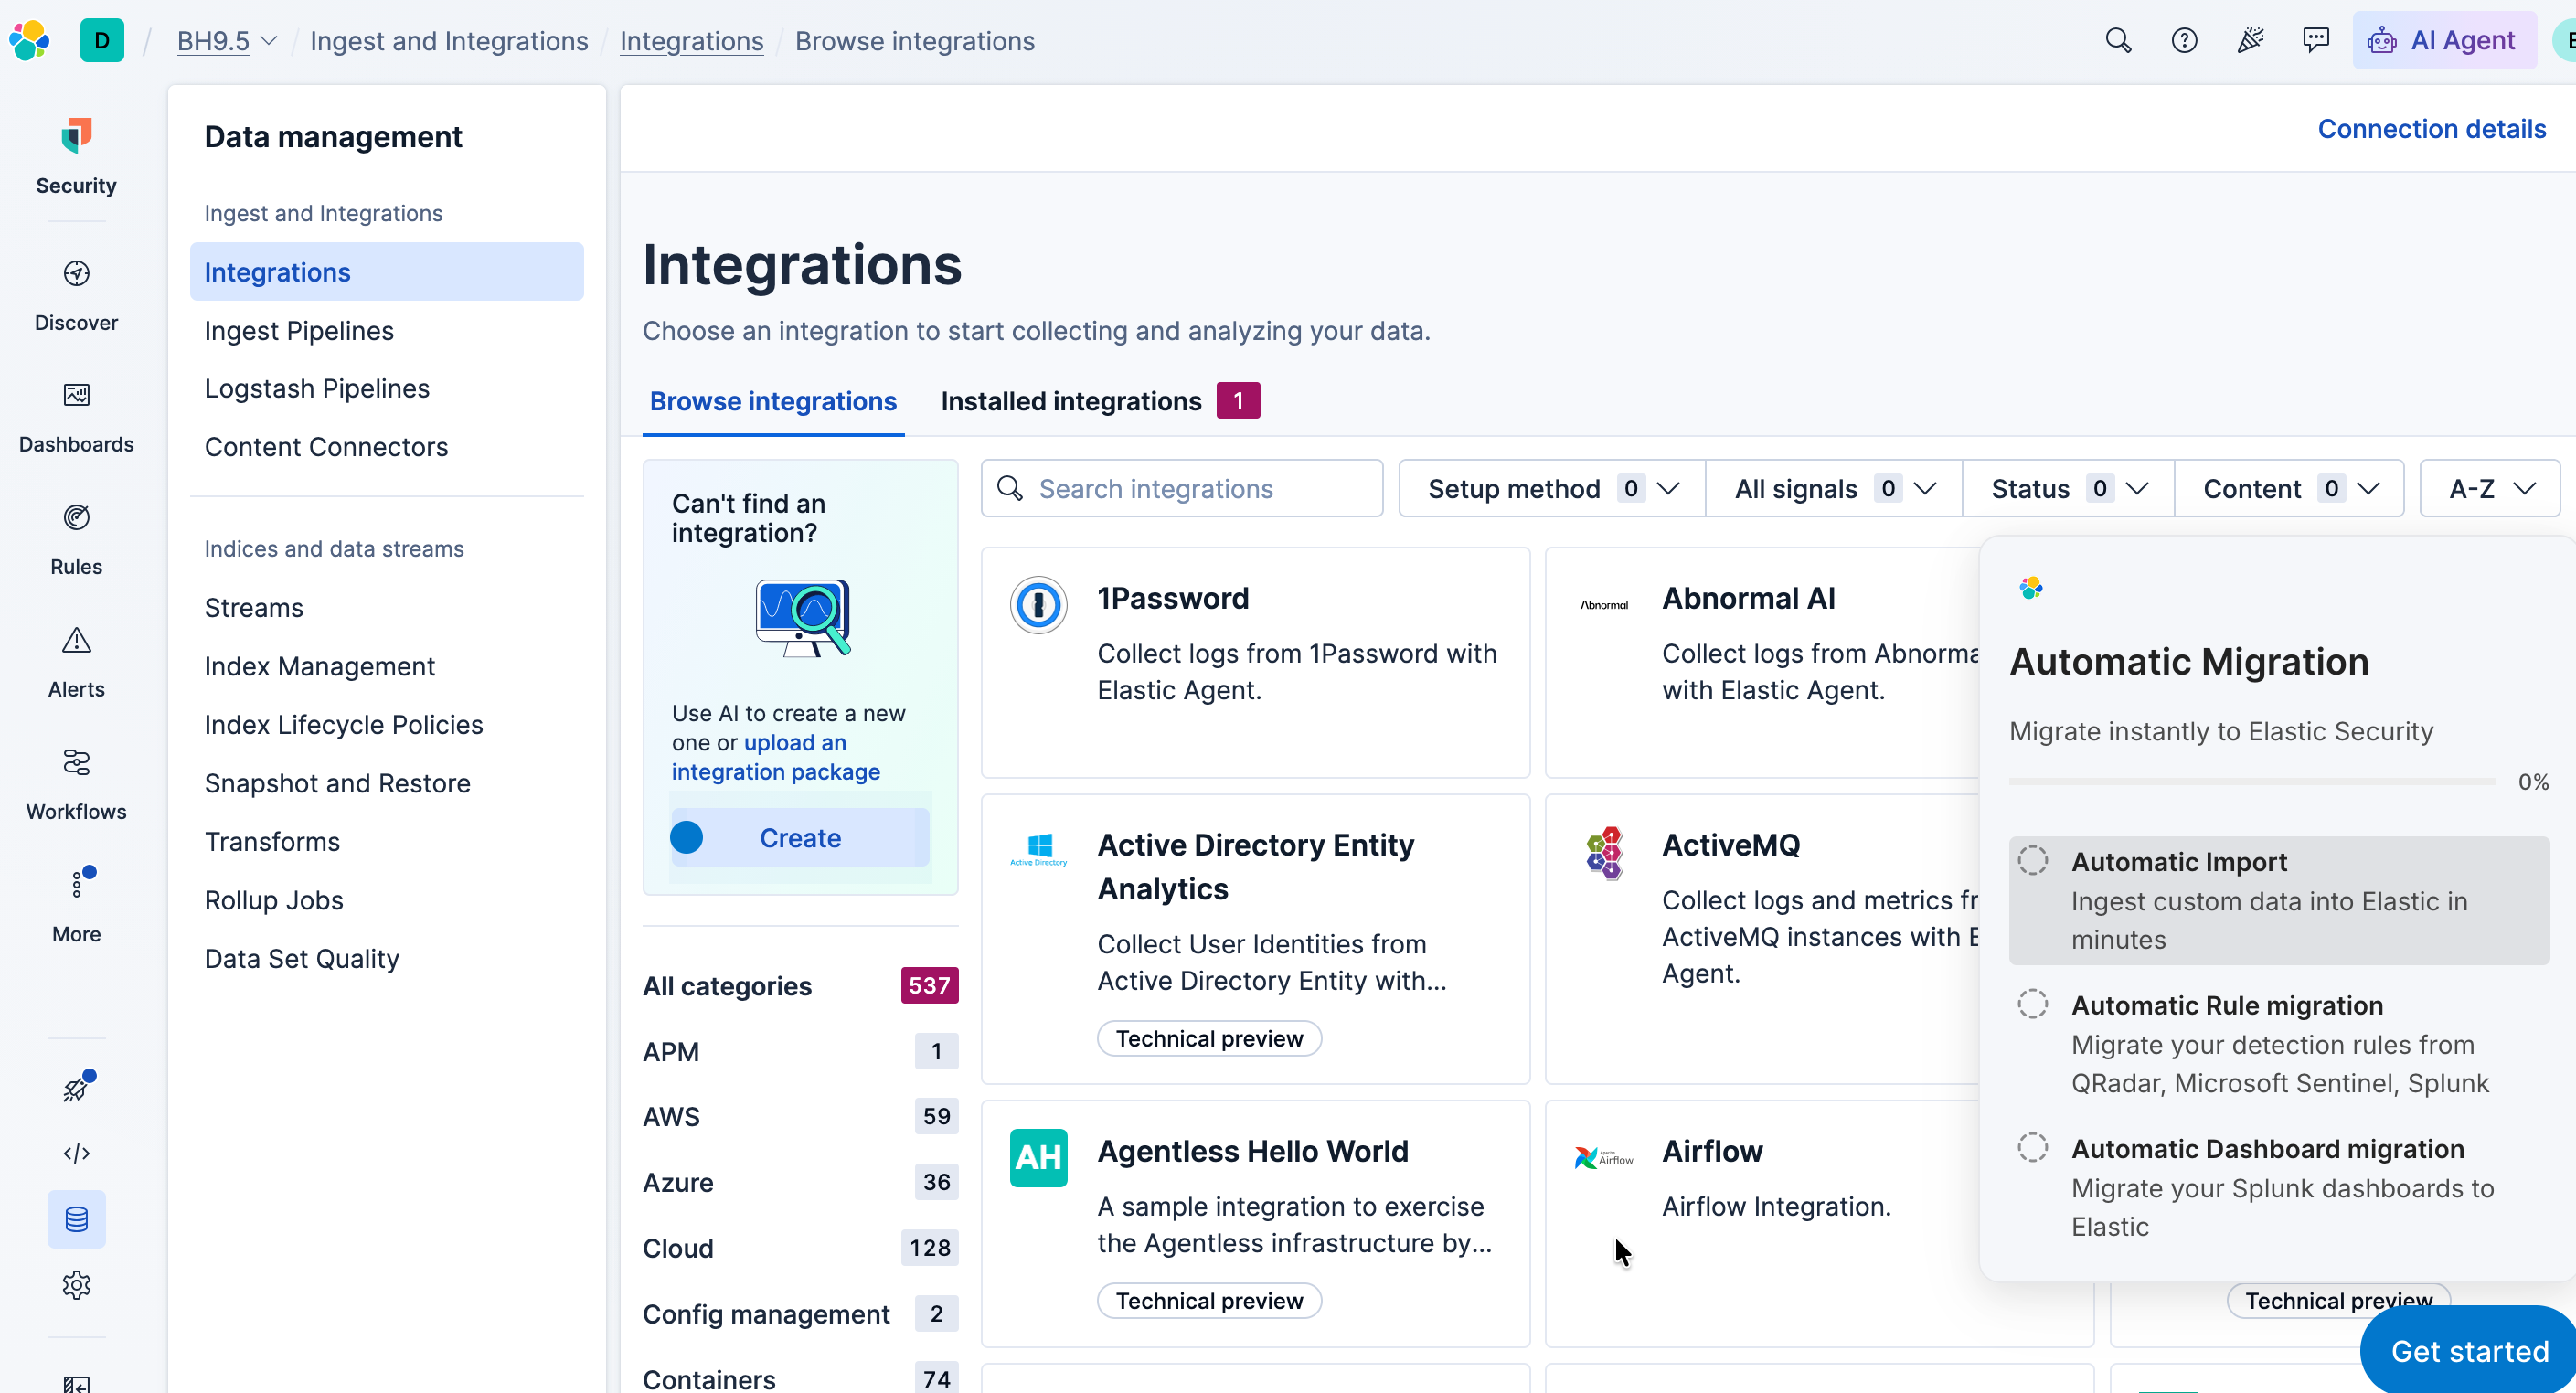
Migrate to Elastic Security
Onboard without the rip-and-replace. Watch Automatic Import build a custom integration on the fly—just upload sample logs and bring in any source—then let Automatic Migration map and convert your existing detection rules from Splunk, QRadar, and Microsoft Sentinel in minutes. Everything lands in one open schema, unified and analysis-ready the moment it arrives.
Security
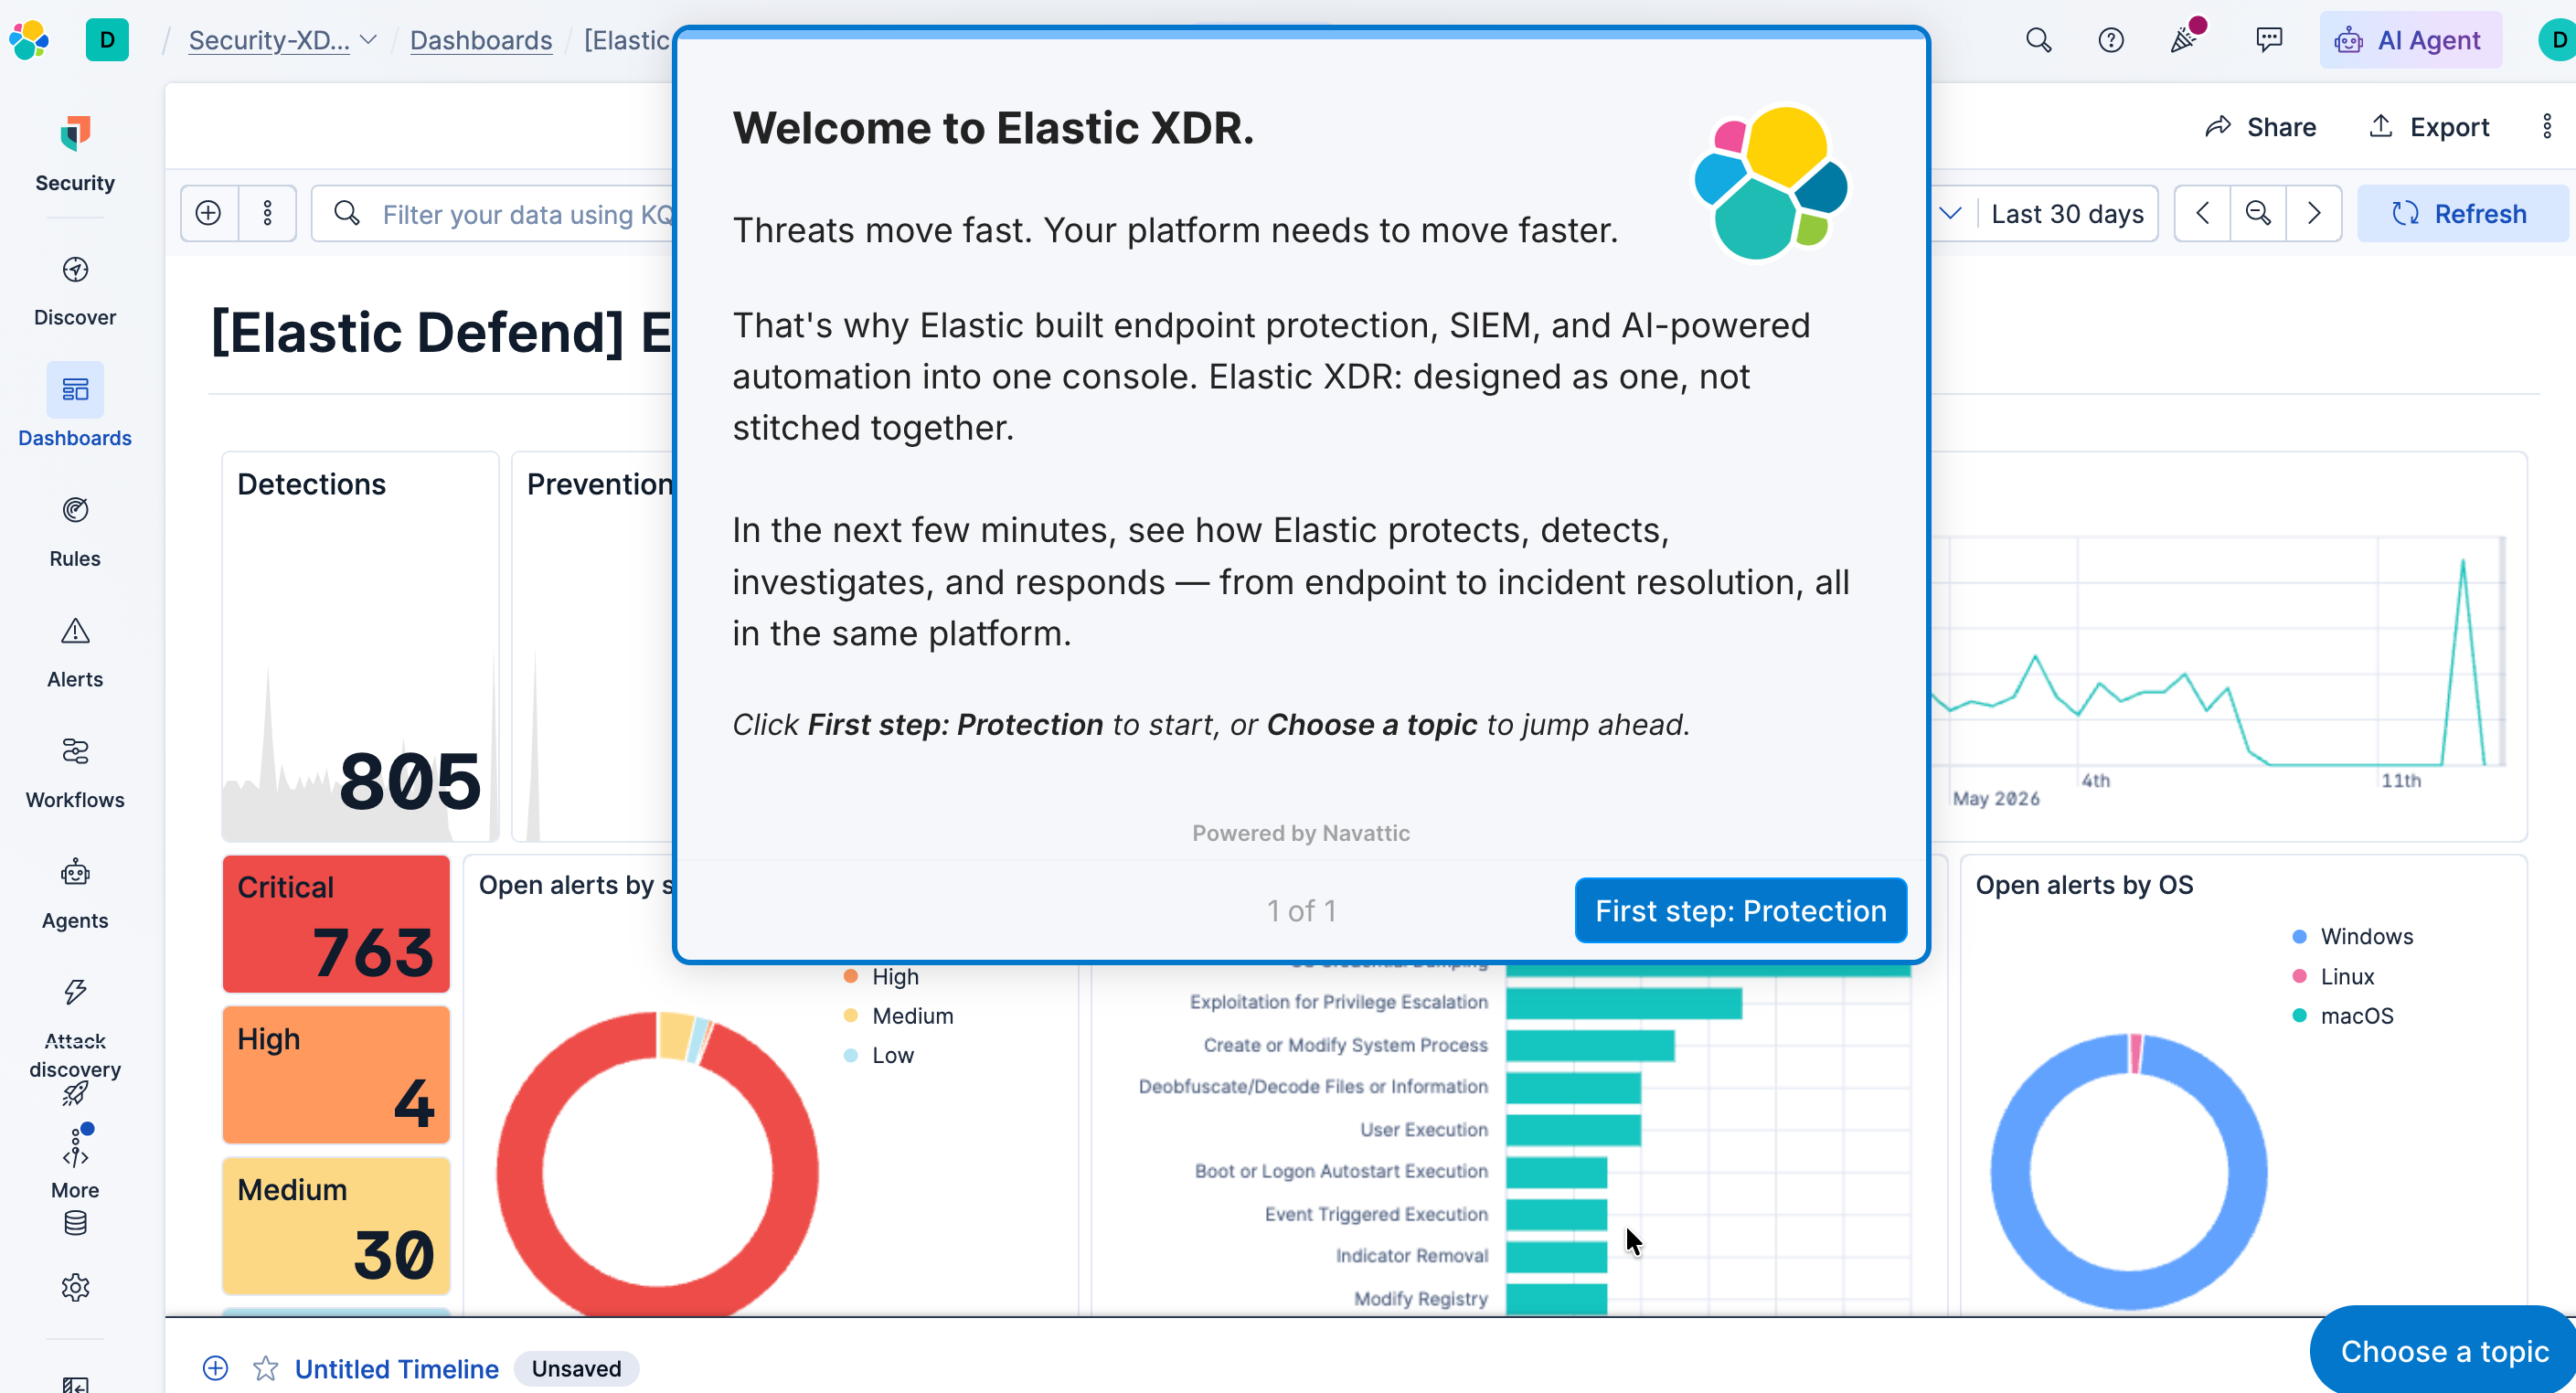
Elastic Security XDR
Threats move fast. Your platform needs to move faster. In this flow see how Elastic XDR protects, detects, investigates, and responds — from endpoint to incident resolution, all in the same platform.

Security
攻撃の発見
Attack Discoveryは、数百件ものアラートをトリアージして本当に重要な数件の攻撃に絞り込み、直感的なインターフェースで結果を返します。これにより、提示された攻撃を迅速に理解し、即座にフォローアップアクションを実行できるようになります。
Observability
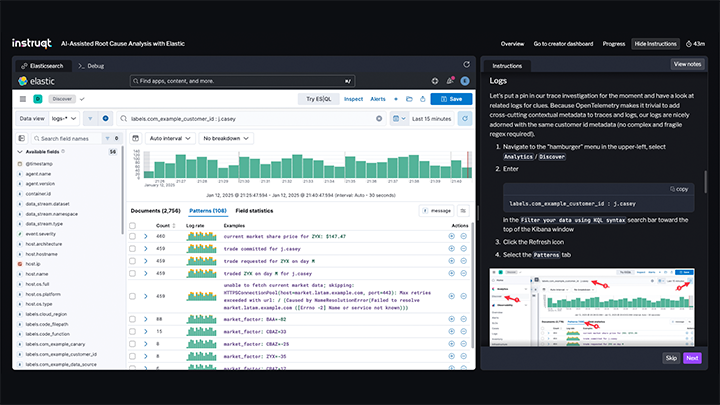
Root cause analysis with AI
Observability 101: Lesson 4 of 4 — Explore this 15 minute lab and use Elastic Observability's machine learning and AI technologies to perform Root Cause Analysis (RCA) of a customer-reported issue. Combine clues from traces and logs at scale with Elastic's AI Assistant to come to a faster resolution.
