
Linux Detection Engineering - Local Privilege Escalation
Seven of the thirteen Linux privilege escalation CVEs we tracked in 2026 turned out to be the same copy-on-write bug pointed at different kernel interfaces. We ran the public proof-of-concept for eleven exploits and two misconfigurations, and noted which rules fired.
Linux Detection Engineering - Fileless Execution
We reproduced five Linux fileless execution patterns with FENIX, including memfd_create staging, interpreter one-liners, deleted binaries, and in-memory kernel module loads, then mapped each to the Elastic Defend rules that catch it.
Not another Log4Shell: inside the Log4j 2 deserialization allowlist bypass
We reproduced this java deserialization vulnerability against official Log4j 2.26.1 JARs. Getting to command execution took two more things that Log4j itself does not ship. Here is how the bypass works, which versions carry it, and what to hunt for.
wp2shell hits WordPress: detecting pre-auth RCE from plugin drop to command execution
We ran the wp2shell WordPress RCE chain end-to-end with Elastic Defend. Detection rule walkthrough, IOCs, and hunt guidance.
Copy Fail and DirtyFrag: Linux Page Cache Bugs in the Wild
This research analyzes the Linux kernel privilege escalation vulnerabilities Copy Fail and DirtyFrag, which exploit subtle page cache corruption bugs to create reliable paths to root access. Additionally, Elastic Security Labs is releasing detection logic for these vulnerabilities.
Hooked on Linux: Rootkit Detection Engineering
In this second part of a two-part series, we explore Linux rootkit detection engineering, focusing on the limitations of static detection reliance, and the importance of rootkit behavioral detection.
Elastic releases detections for the Axios supply chain compromise
Hunting and detection rules for the Elastic-discovered Axios supply chain compromise.
Inside the Axios supply chain compromise - one RAT to rule them all
Elastic Security Labs analyzes a supply chain compromise of the axios npm package delivering a unified cross-platform RAT
Illuminating VoidLink: Technical analysis of the VoidLink rootkit framework
Elastic Security Labs analyzes VoidLink, a sophisticated Linux malware framework that combines traditional Loadable Kernel Modules with eBPF to maintain persistence.
Linux & Cloud Detection Engineering - TeamPCP Container Attack Scenario
This publication provides a real-world walkthrough of TeamPCP's multi-stage container compromise, demonstrating how Elastic's D4C surfaces runtime signals across each stage of the attack chain.
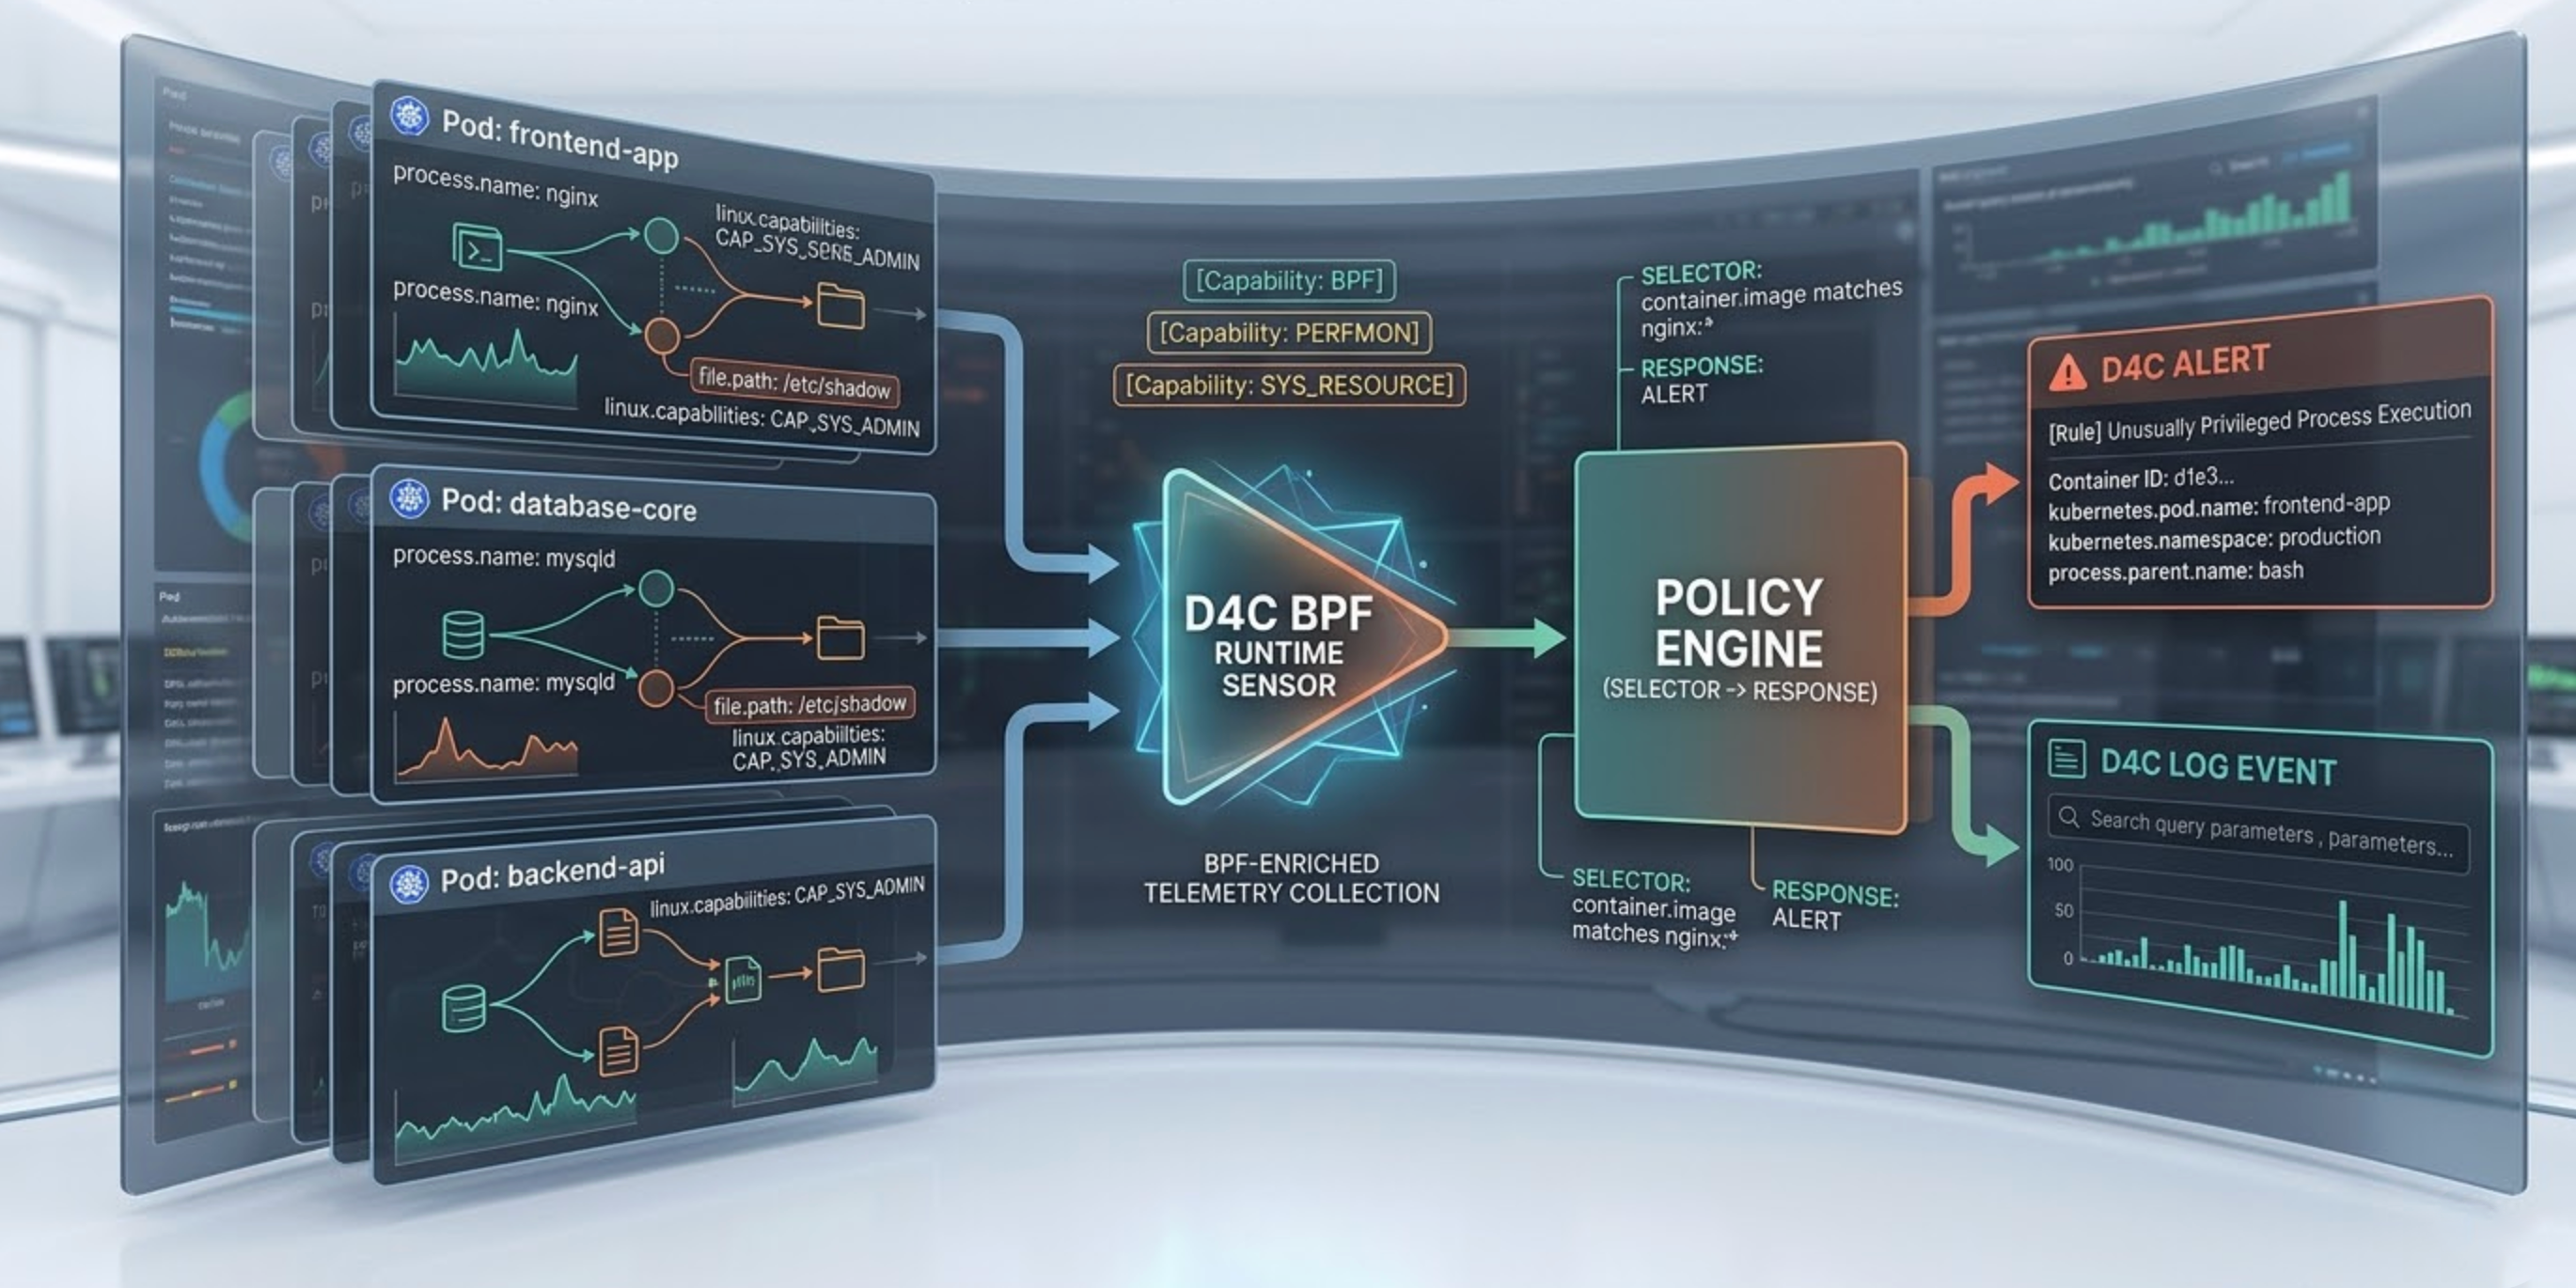
Linux & Cloud Detection Engineering - Getting Started with Defend for Containers (D4C)
This technical resource provides a comprehensive walkthrough of Elastic’s Defend for Containers (D4C) integration, covering Kubernetes-based deployment, the analysis of BPF-enriched runtime telemetry, and the practical application of policy-driven security controls to monitor and alert on activities within containerized Linux environments.
Hooked on Linux: Rootkit Taxonomy, Hooking Techniques and Tradecraft
In this first part of a two-part series, we explore Linux rootkit taxonomy, trace their evolution from userland shared object hijacking and kernel-space loadable kernel module hooking to modern eBPF- and io_uring-powered techniques.
FlipSwitch: a Novel Syscall Hooking Technique
FlipSwitch offers a fresh look at bypassing Linux kernel defenses, revealing a new technique in the ongoing battle between cyber attackers and defenders.
Outlaw Linux Malware: Persistent, Unsophisticated, and Surprisingly Effective
Outlaw is a persistent Linux malware leveraging simple brute-force and mining tactics to maintain a long-lasting botnet.
Linux Detection Engineering - The Grand Finale on Linux Persistence
By the end of this series, you'll have a robust knowledge of both common and rare Linux persistence techniques; and you'll understand how to effectively engineer detections for common and advanced adversary capabilities.
Linux Detection Engineering - Approaching the Summit on Persistence Mechanisms
Building on foundational concepts and techniques explored in the previous publications, this post discusses some creative and/or complex persistence mechanisms.
Linux Detection Engineering - A Continuation on Persistence Mechanisms
This document continues the exploration of Linux detection engineering, emphasizing advancements in monitoring persistence mechanisms. By building on past practices and insights, it provides a roadmap for improving detection strategies in complex environments.
Declawing PUMAKIT
PUMAKIT is a sophisticated loadable kernel module (LKM) rootkit that employs advanced stealth mechanisms to hide its presence and maintain communication with command-and-control servers.
Cups Overflow: When your printer spills more than Ink
Elastic Security Labs discusses detection and mitigation strategies for vulnerabilities in the CUPS printing system, which allow unauthenticated attackers to exploit the system via IPP and mDNS, resulting in remote code execution (RCE) on UNIX-based systems such as Linux, macOS, BSDs, ChromeOS, and Solaris.
Betting on Bots: Investigating Linux malware, crypto mining, and gambling API abuse
The REF6138 campaign involved cryptomining, DDoS attacks, and potential money laundering via gambling APIs, highlighting the attackers' use of evolving malware and stealthy communication channels.
Linux Detection Engineering - A Sequel on Persistence Mechanisms
In this final part of this Linux persistence series, we'll continue exploring persistence mechanisms on Linux systems, focusing on more advanced techniques and how to detect them.
Linux Detection Engineering - A primer on persistence mechanisms
In this second part of the Linux Detection Engineering series, we map multiple Linux persistence mechanisms to the MITRE ATT&CK framework, explain how they work, and how to detect them.
Linux detection engineering with Auditd
In this article, learn more about using Auditd and Auditd Manager for detection engineering.
An Elastic approach to large-scale dynamic malware analysis
This research reveals insights into some of the large-scale malware analysis performed by Elastic Security Labs, and complements research related to the Detonate framework.