Elastic 데모 갤러리
Kibana 대시보드와 Canvas 작업 패드에서 Elasticsearch SQL 스니펫과 Machine Learning 작업에 이르기까지, Elastic Stack의 다양한 측면을 탐색할 수 있도록 설계된 예제를 사용해 직접 체험해 보세요.
.
필터
유형
솔루션
Elastic 기능
통합 가시성
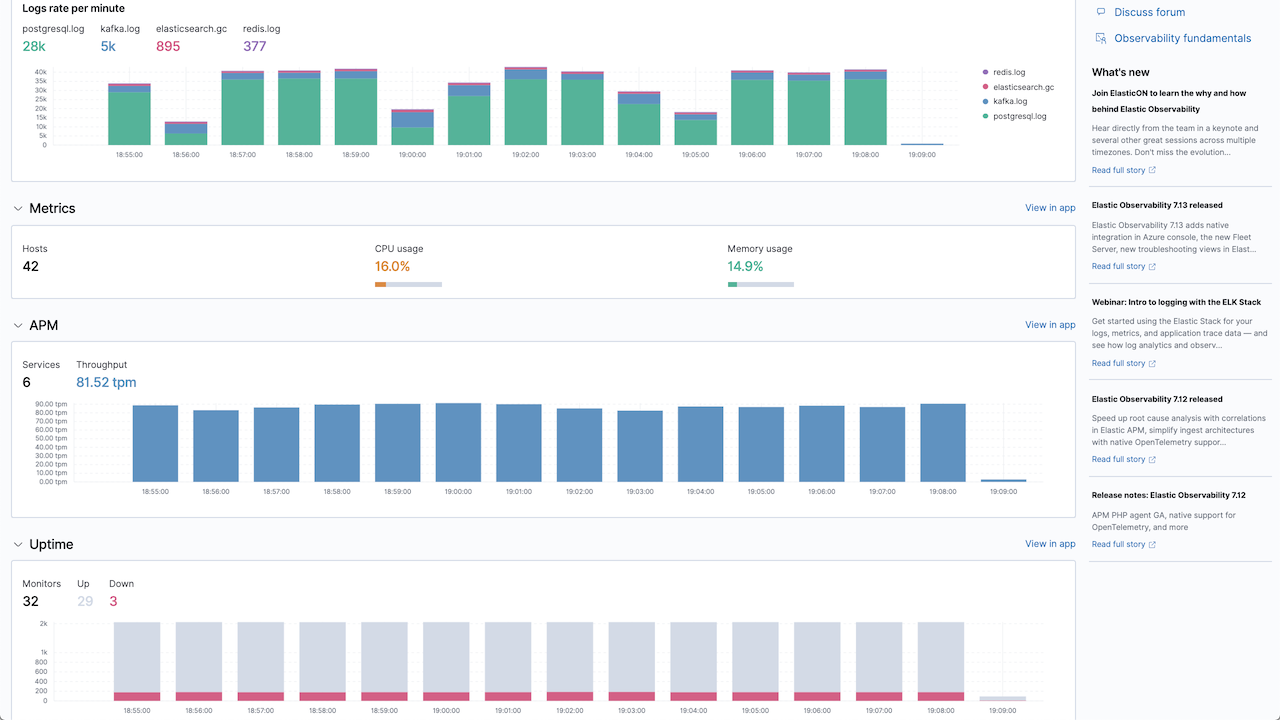
Observability 개요
이 실습 데모를 통해 로그, 메트릭 및 추적 정보를 통합하여 애플리케이션 환경을 완벽하게 파악하는 방법을 알아보세요.
Security
Accelerate data onboarding with Elastic AI Import
Elastic’s Automatic Import feature saves analysts from the lengthy process of building custom data parsers, allowing them to instead focus on threat hunting and improve their organization’s security posture. In this demo, see how Elastic AI Import feature can process both supported or unsupported log sources, normalizing and enriching them for analysts.
Security
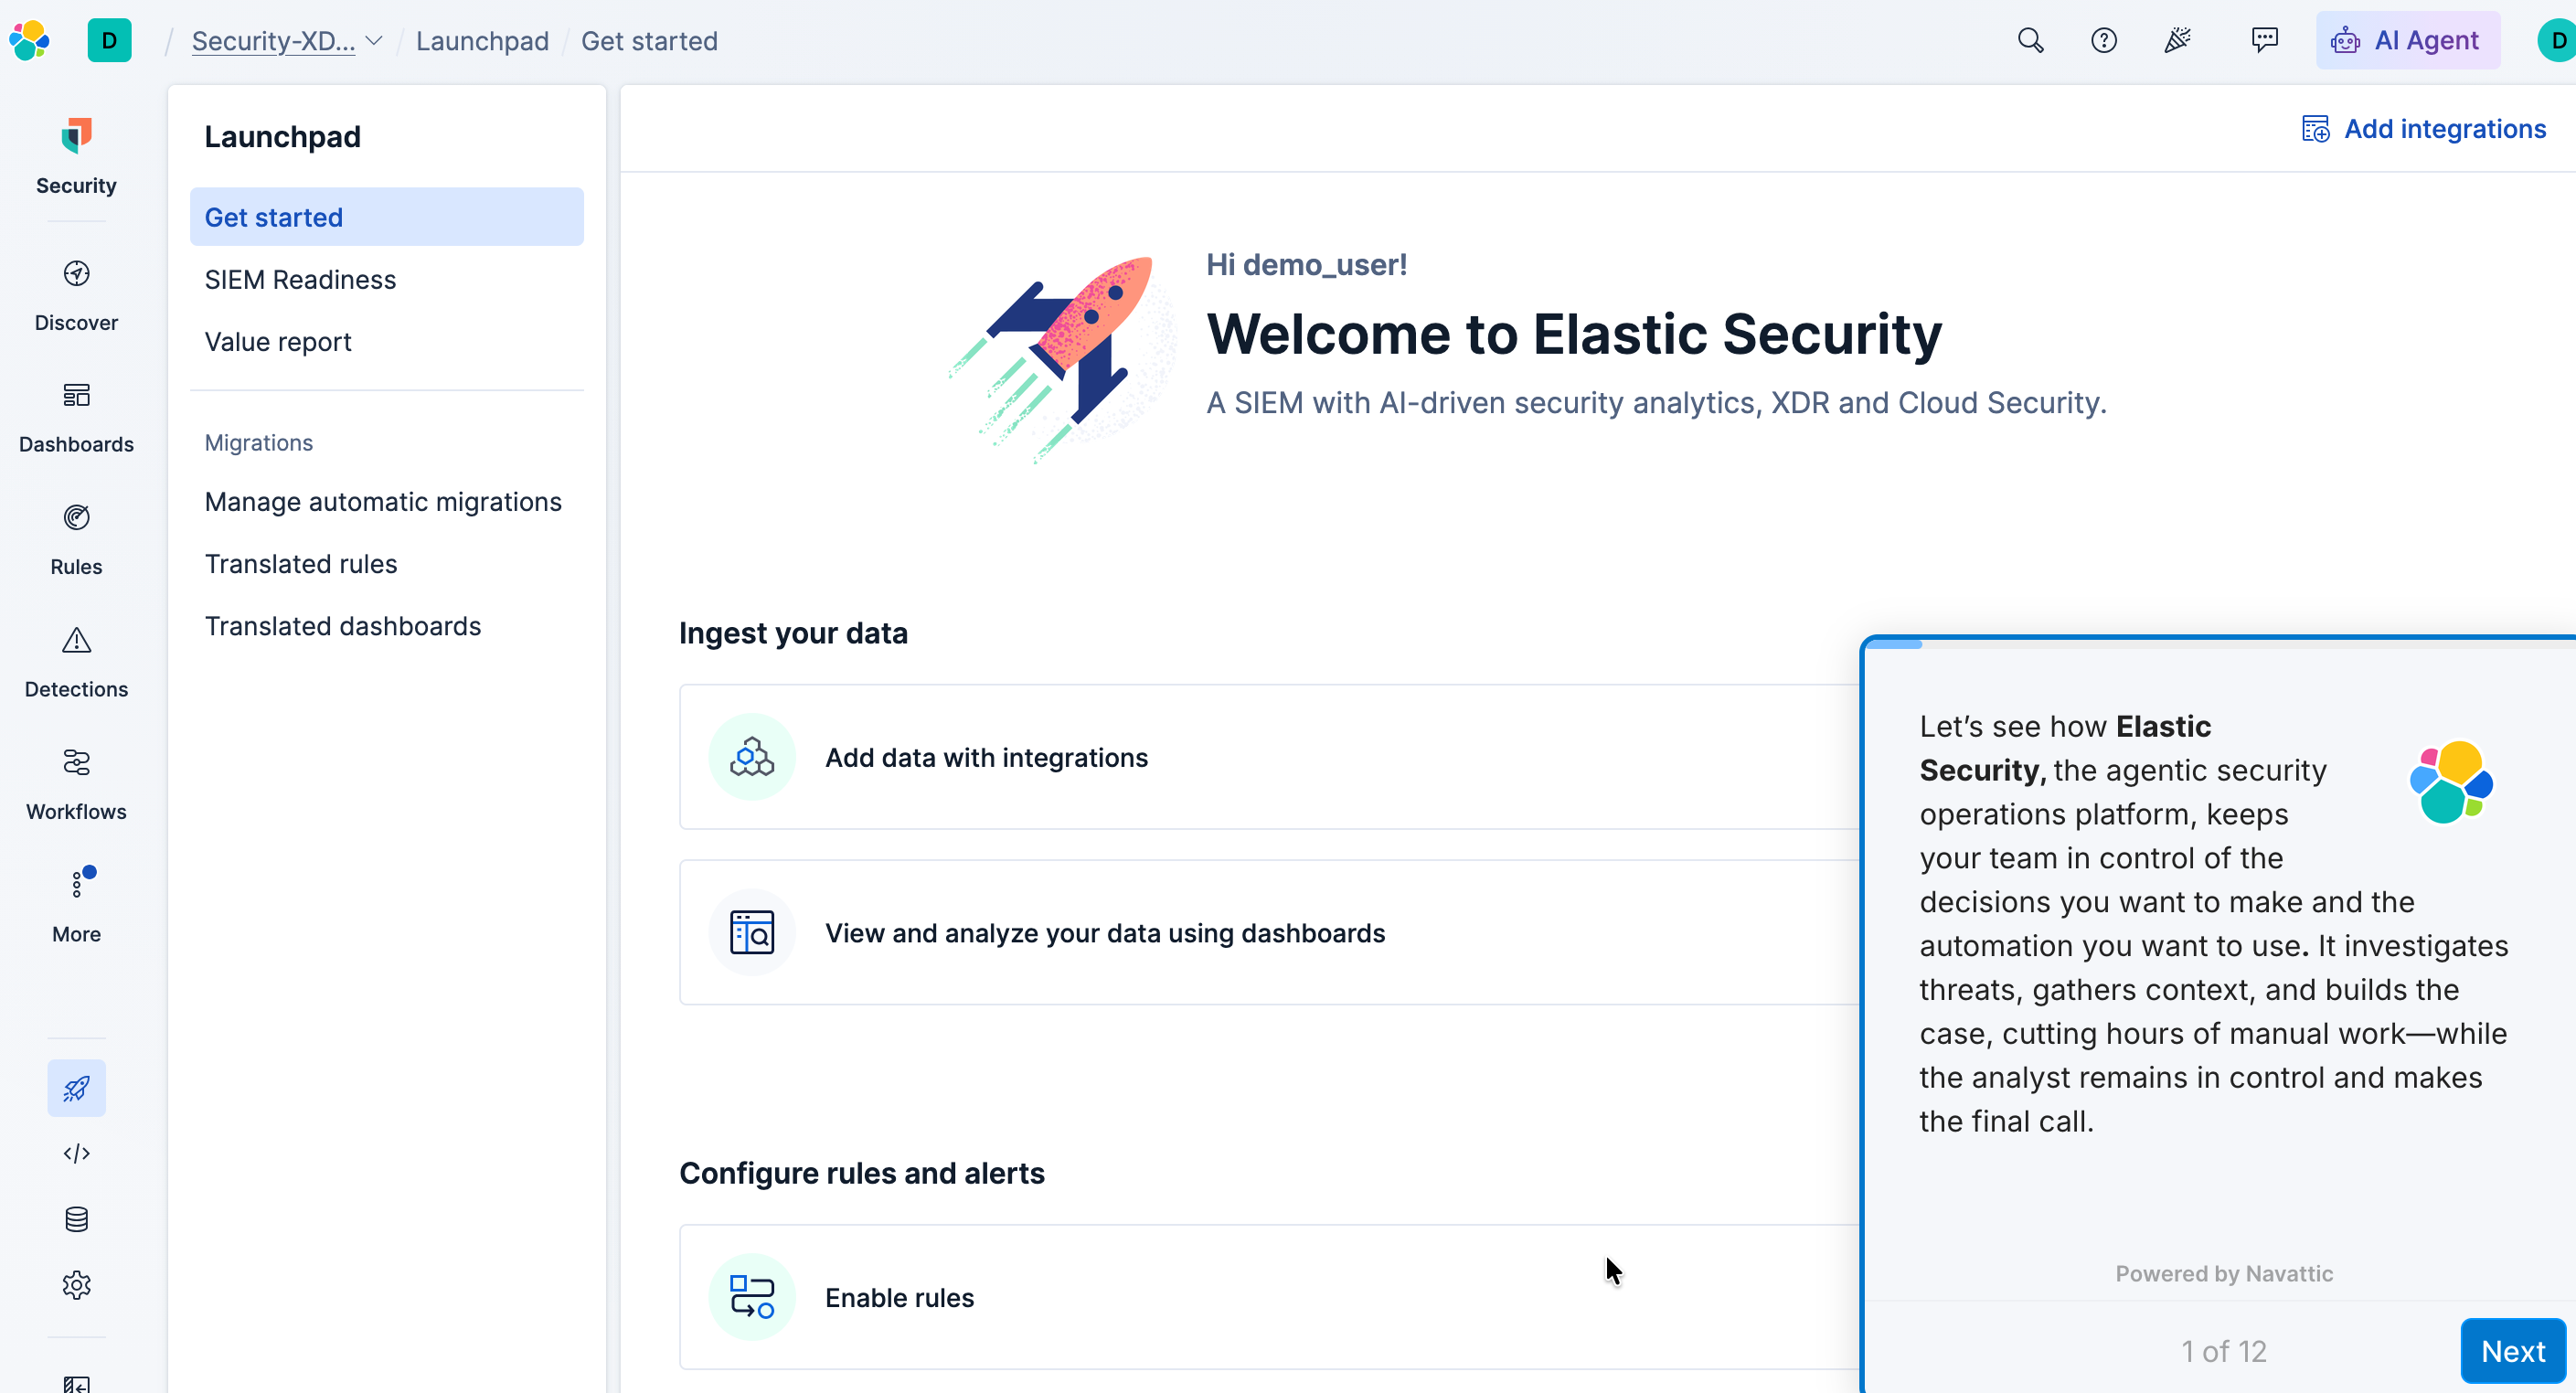
Elastic Security: Agentic Security Operations Platform
Step through Elastic’s agentic SOC live. Watch autonomous agents correlate and investigate a real alert end-to-end, then stage a response through Elastic Workflows—with deterministic playbooks and agentic reasoning working side by side. You stay in control at every gate, approving agent actions and seeing exactly how judgment and verification remain with the analyst while the busywork runs itself.
Security
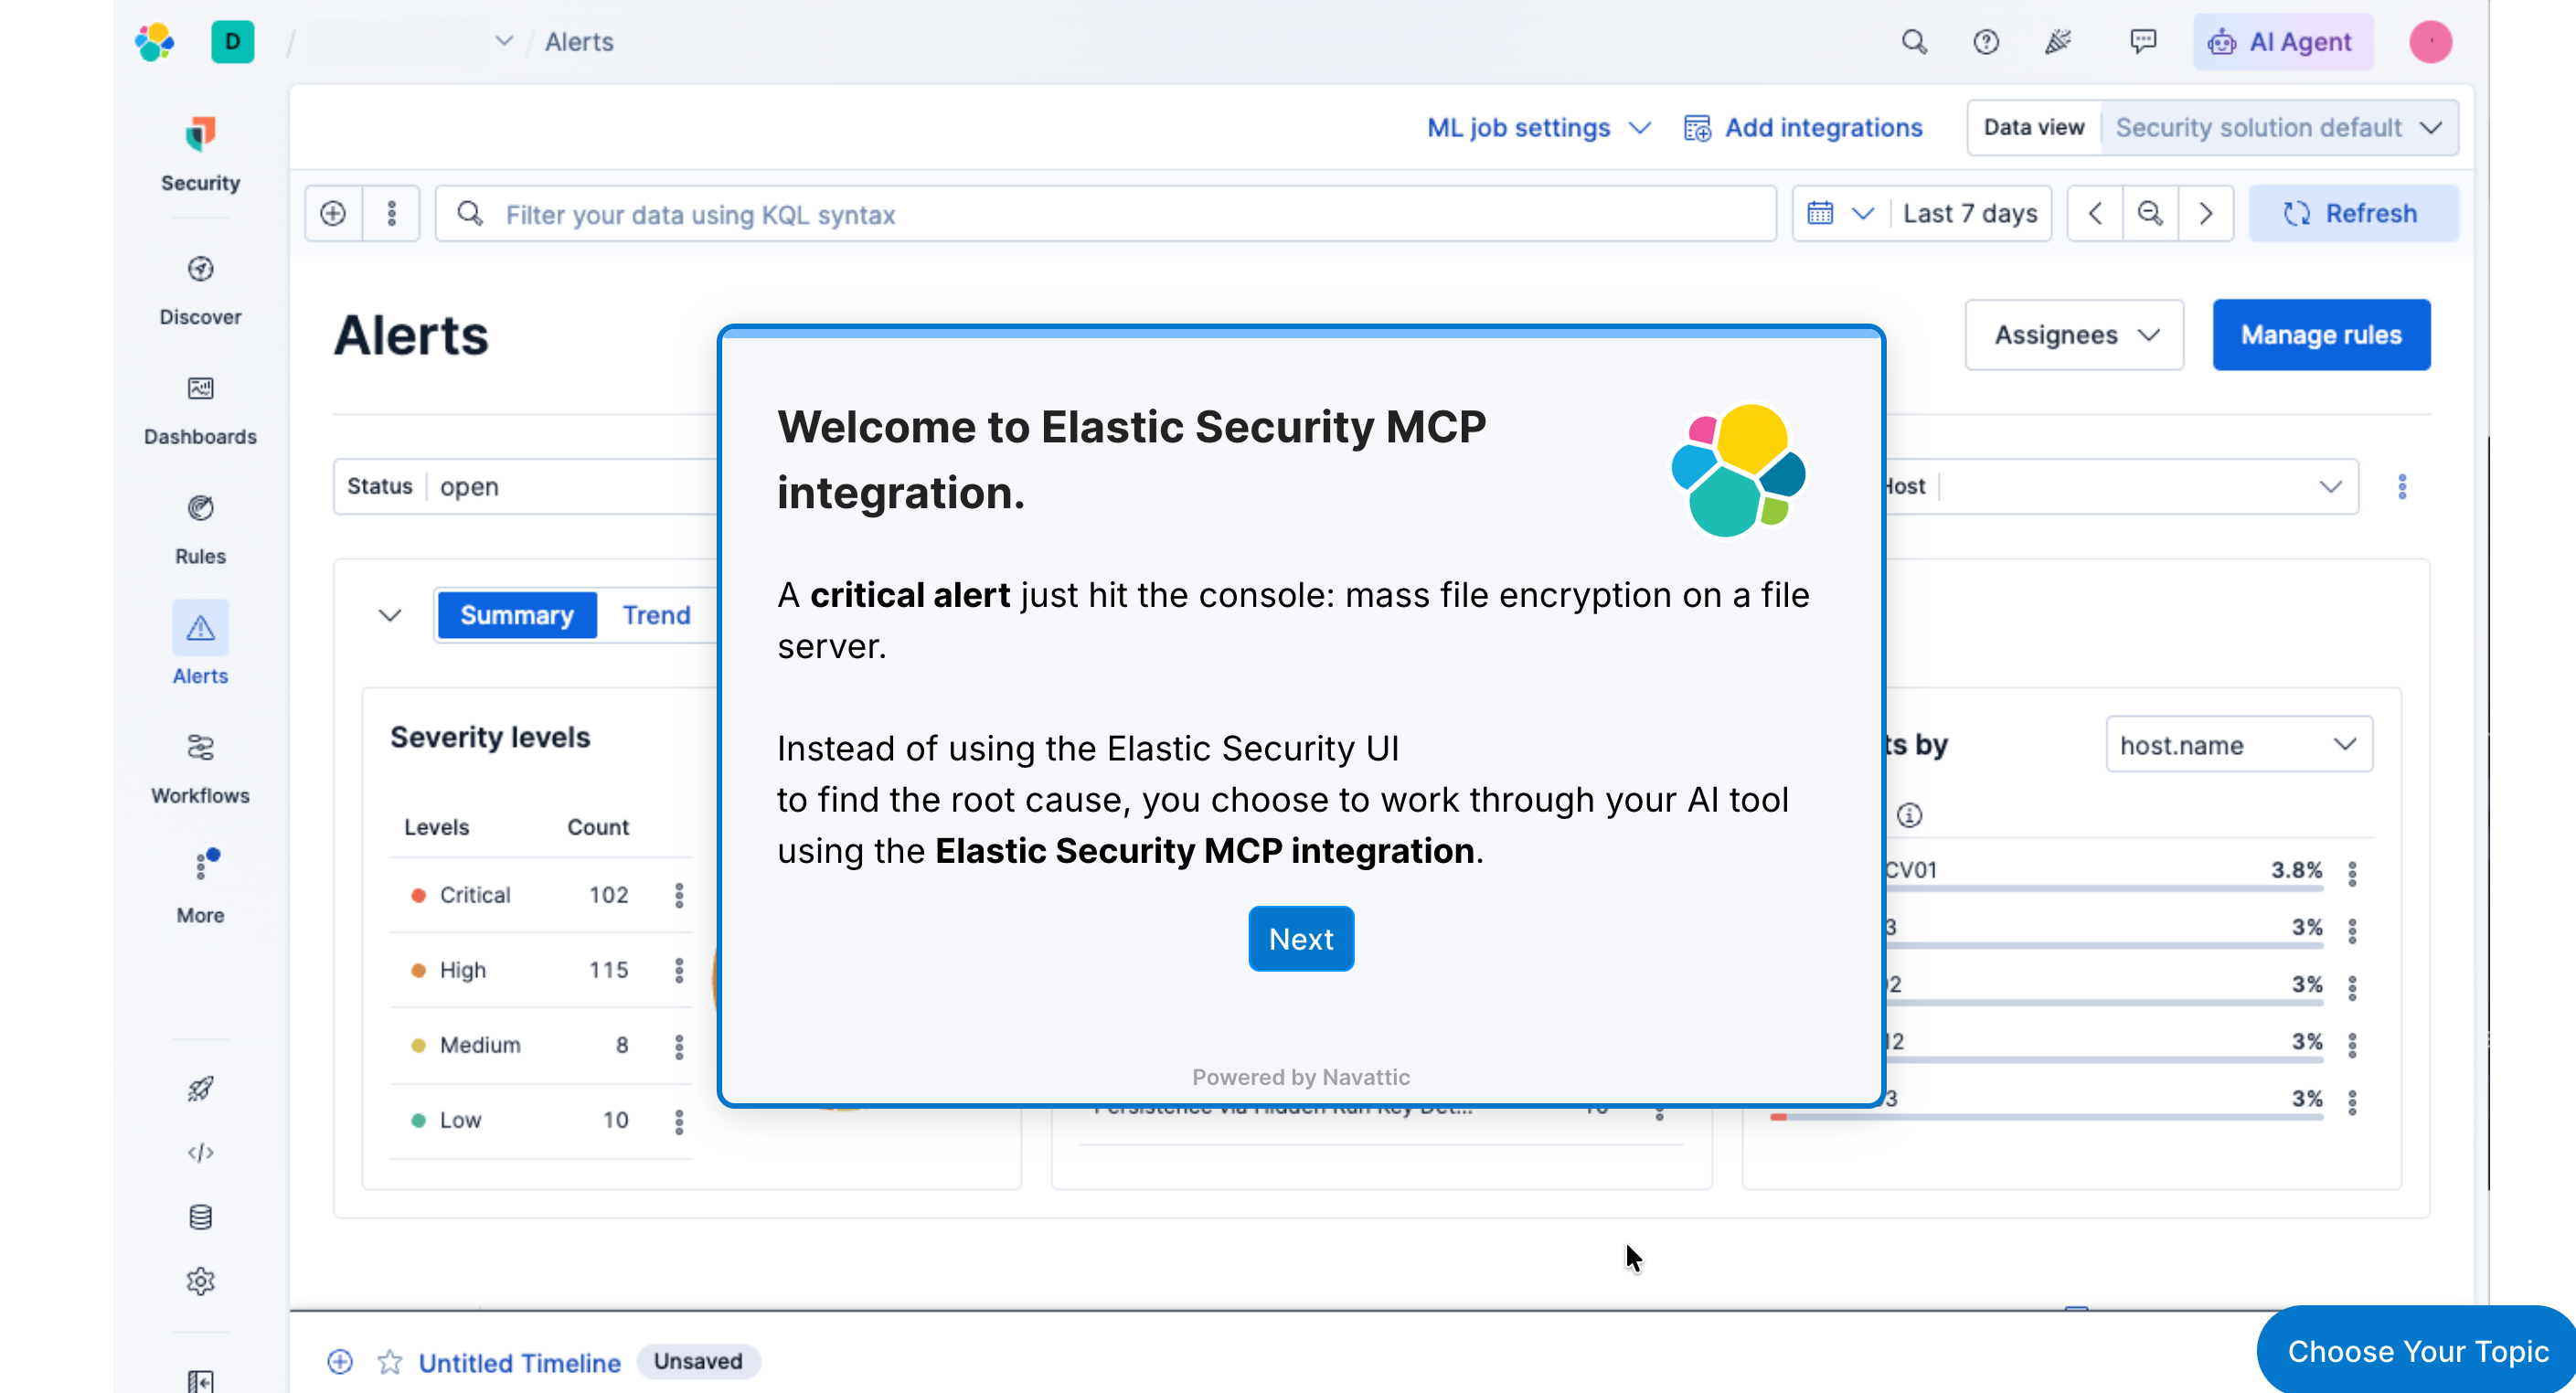
Elastic Security MCP Integration
A critical alert just hit the Elastic Security console: mass file encryption on a file server. Instead of using the web UI to find the root cause, you choose to work through your AI tool using the Elastic Security MCP integration.
Security
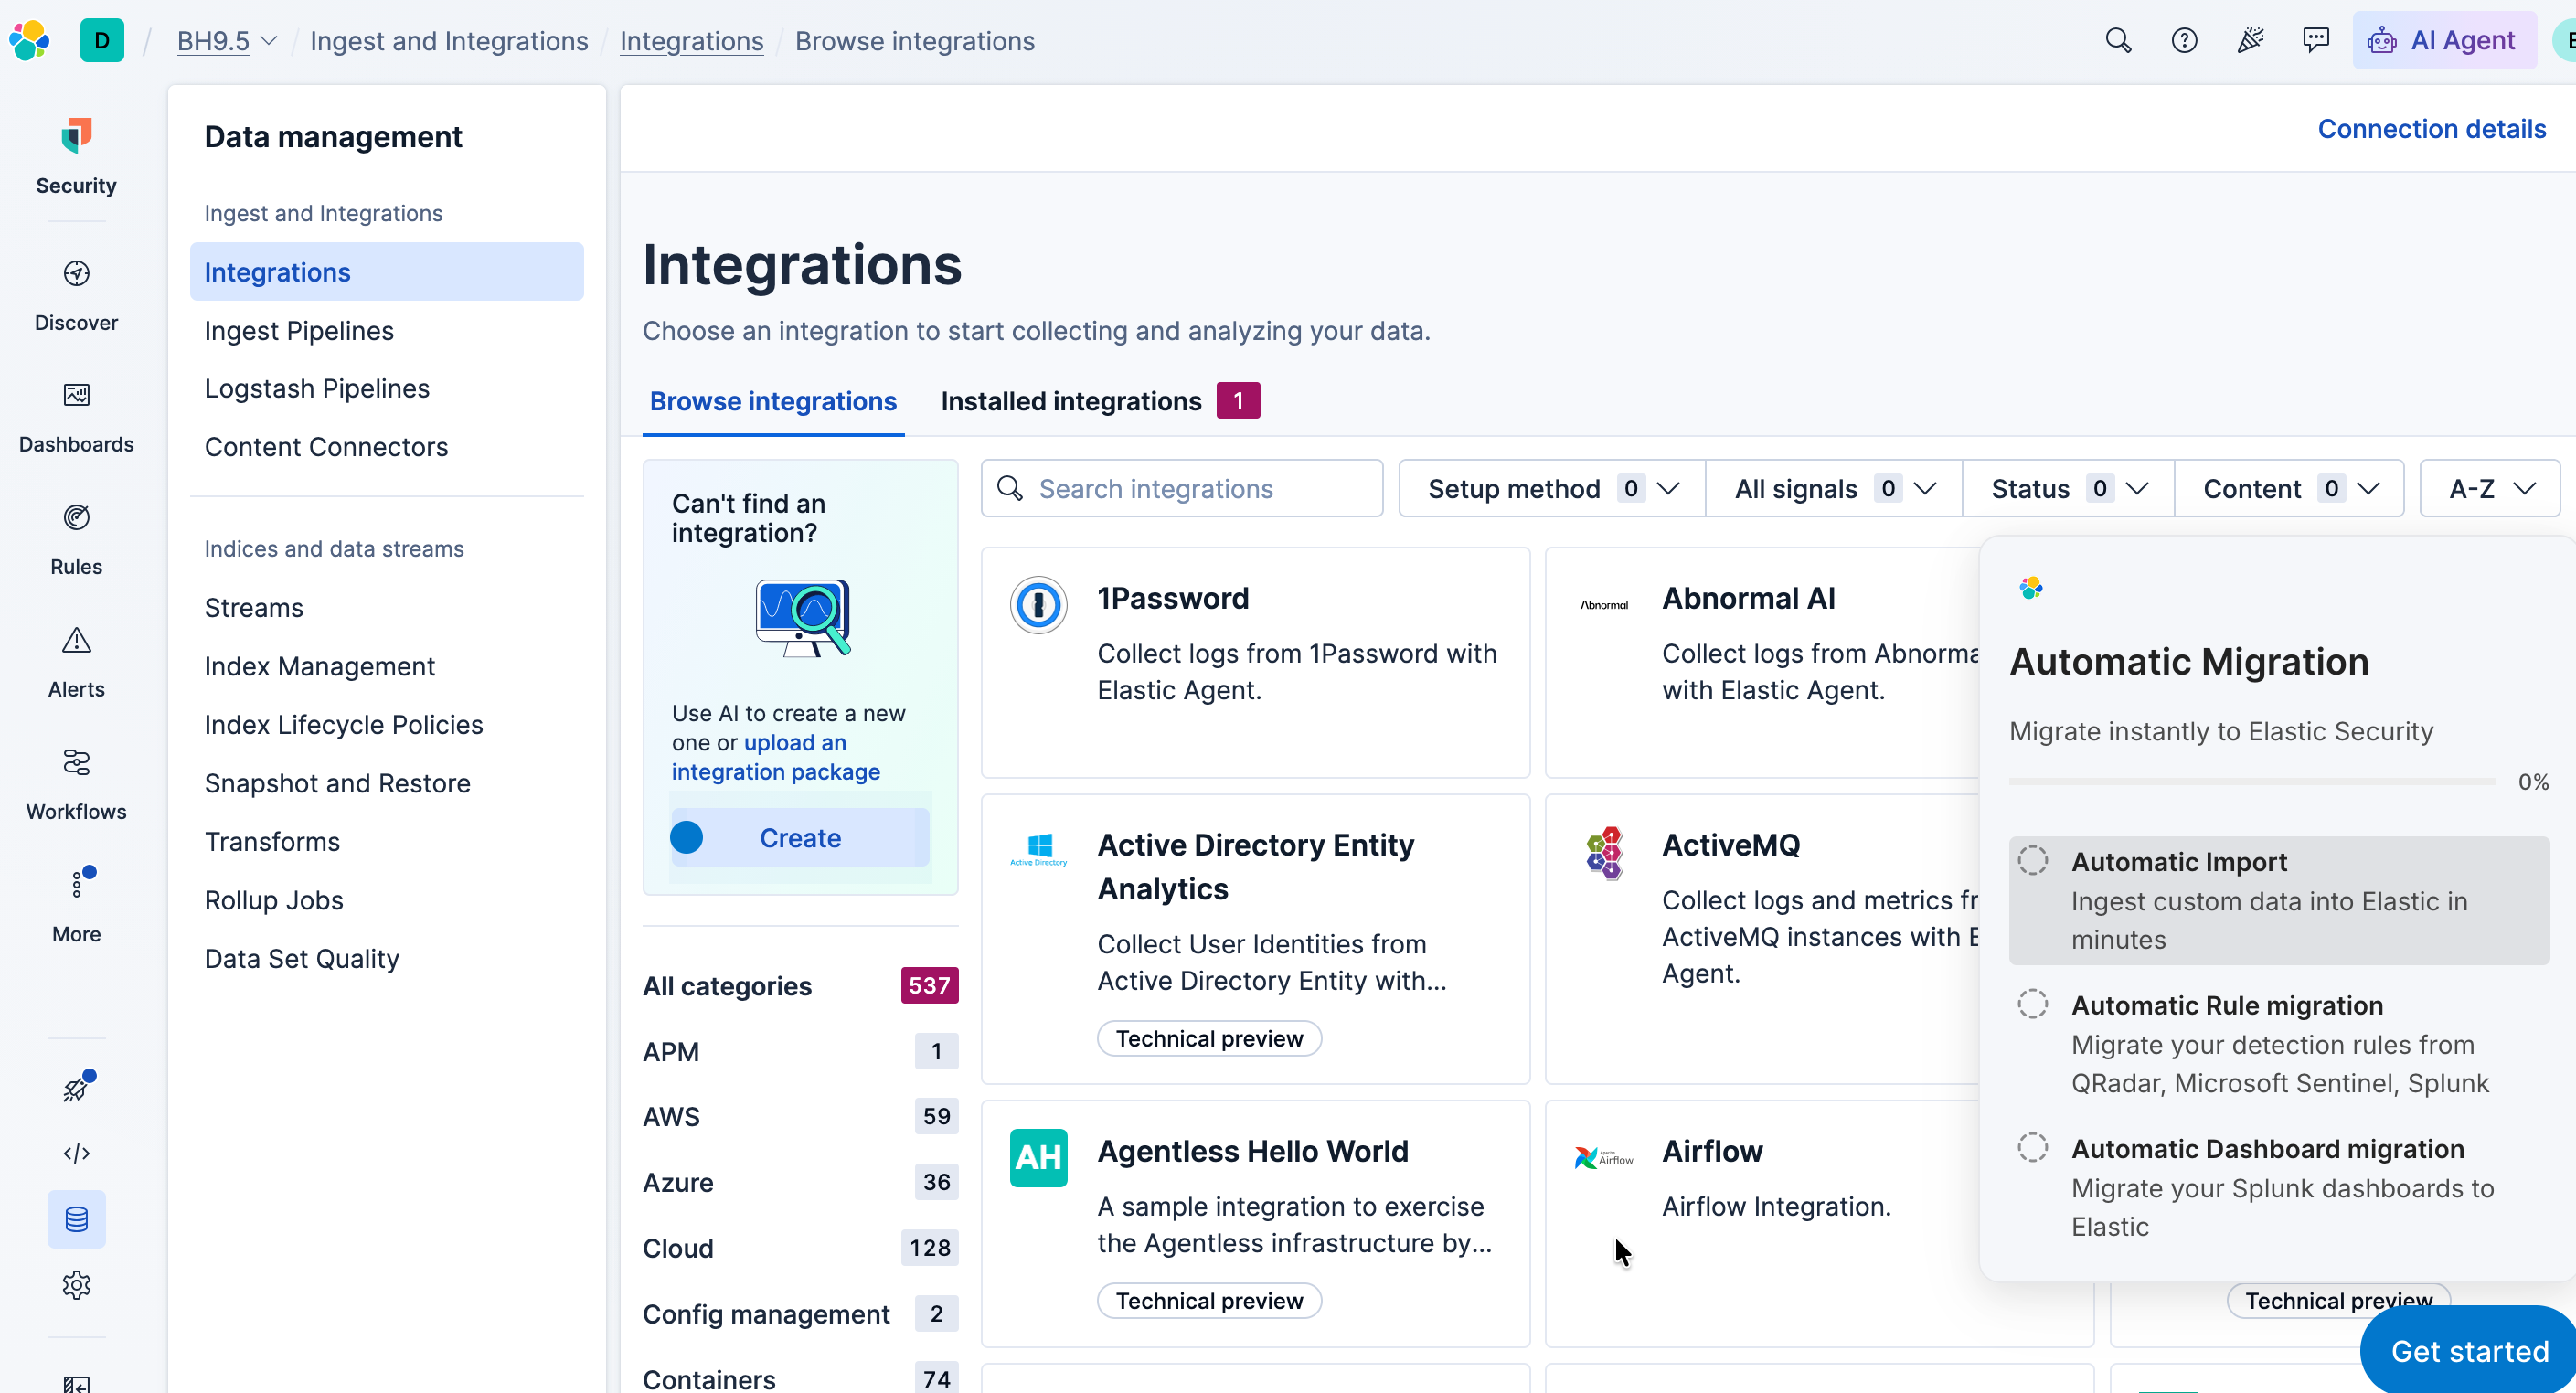
Migrate to Elastic Security
Onboard without the rip-and-replace. Watch Automatic Import build a custom integration on the fly—just upload sample logs and bring in any source—then let Automatic Migration map and convert your existing detection rules from Splunk, QRadar, and Microsoft Sentinel in minutes. Everything lands in one open schema, unified and analysis-ready the moment it arrives.
Security
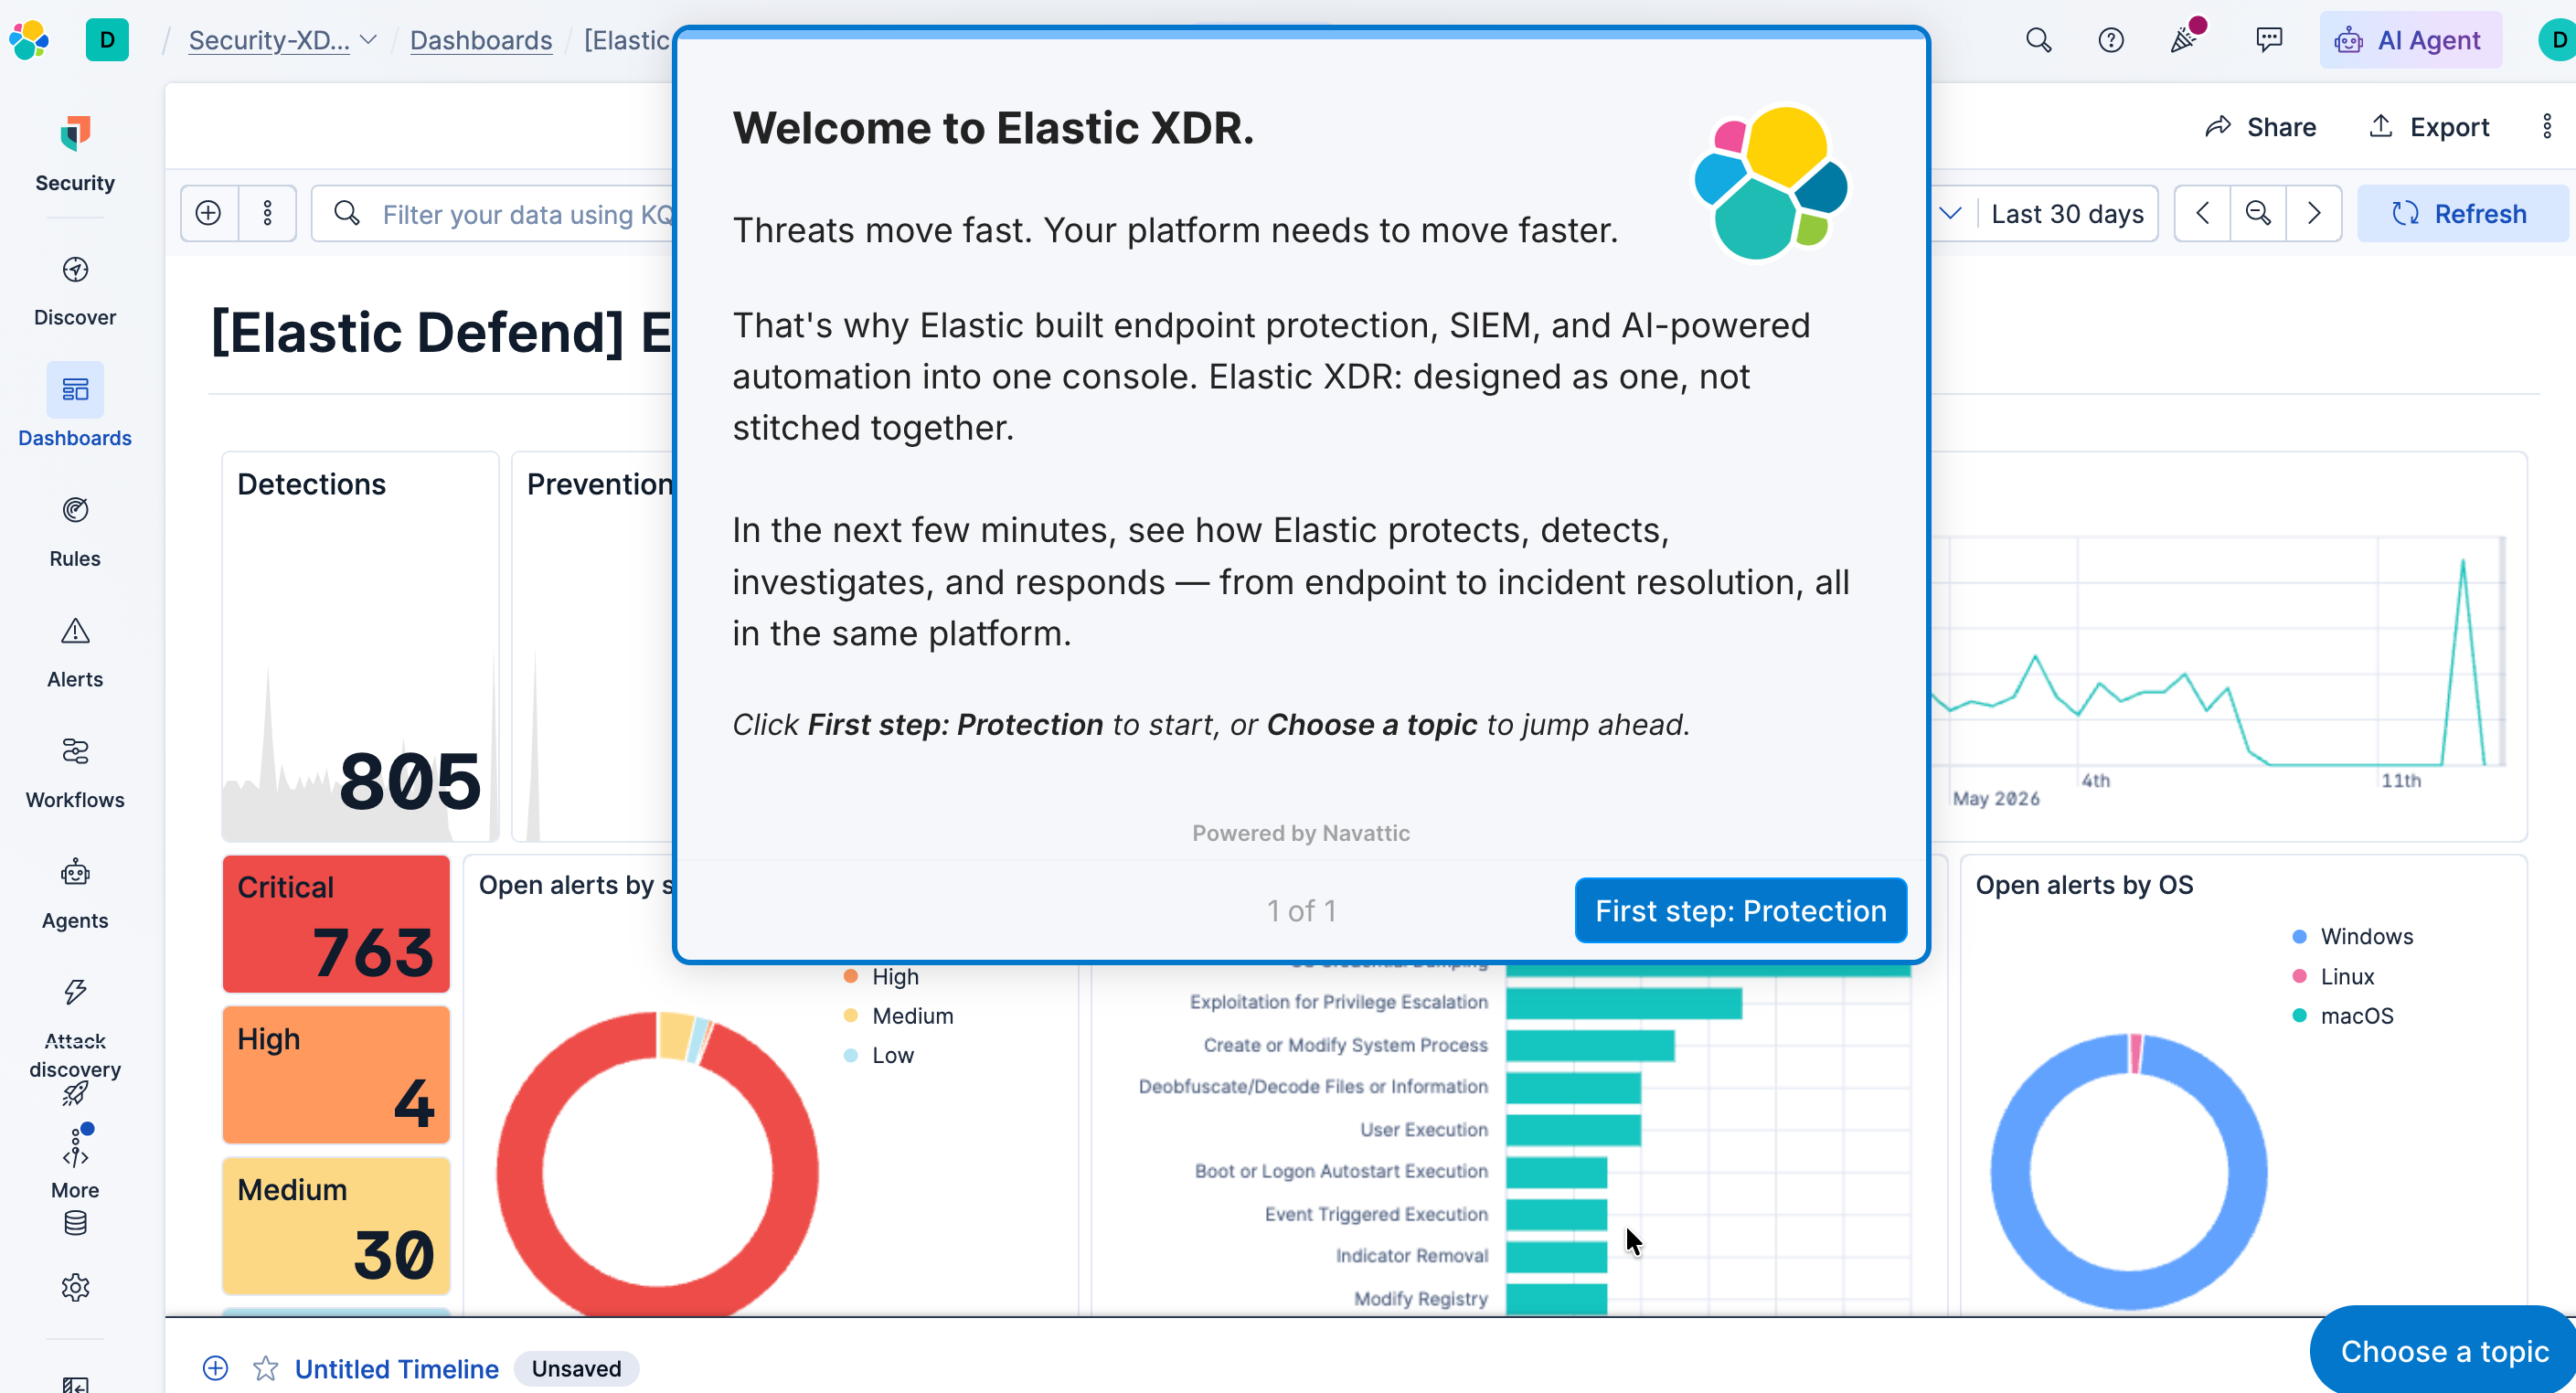
Elastic Security XDR
Threats move fast. Your platform needs to move faster. In this flow see how Elastic XDR protects, detects, investigates, and responds — from endpoint to incident resolution, all in the same platform.

보안
공격 탐지
공격 탐지(Attack Discovery)는 수백 개의 경보를 중요한 몇 가지 공격으로 분류하고 결과를 직관적인 인터페이스로 반환하여, 제시된 공격을 신속하게 이해하고 즉각적인 후속 조치를 취할 수 있도록 지원합니다.
보안
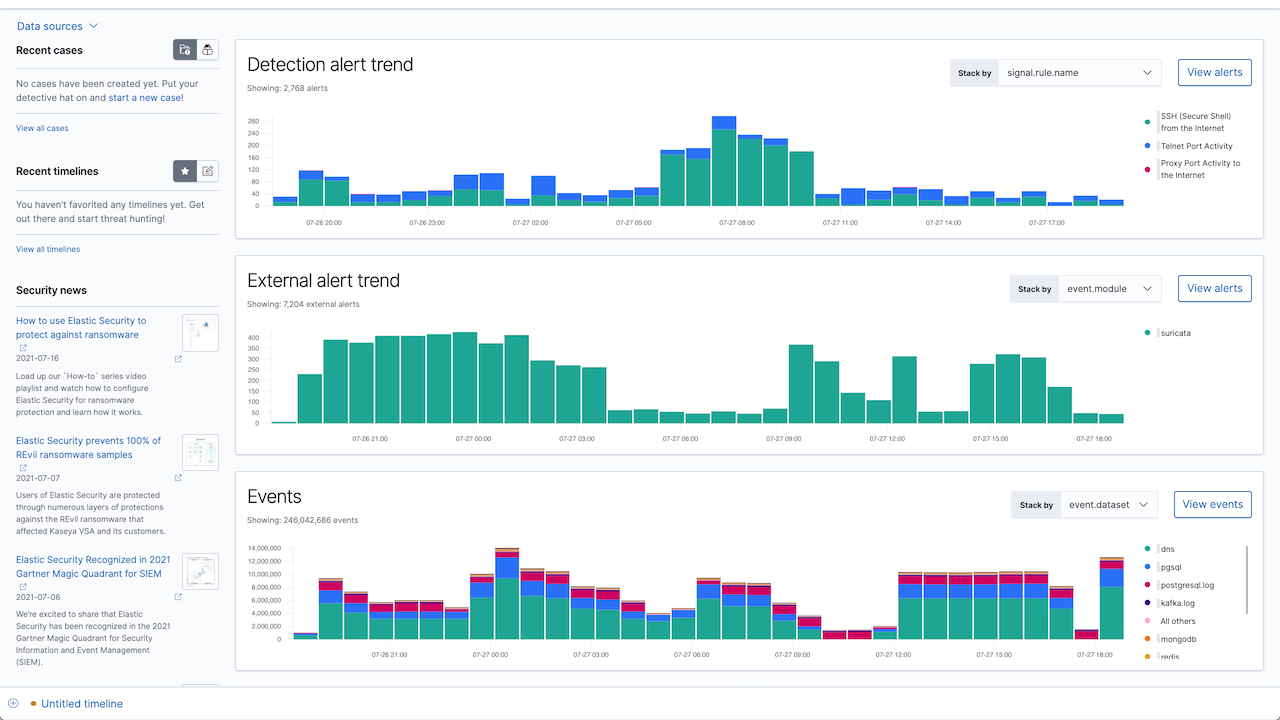
Security 개요
Elastic Security는 SIEM, Endpoint Security, 위협 헌팅, 클라우드 모니터링 등 다양한 기능을 제공해 분석가가 위협을 예방, 탐지 및 대응할 수 있도록 지원합니다.
