Security Labs
Elastic Security Labs empowers security teams across the globe with novel security intelligence research and free to use tools.

Linux Detection Engineering - Local Privilege Escalation
Seven of the thirteen Linux privilege escalation CVEs we tracked in 2026 turned out to be the same copy-on-write bug pointed at different kernel interfaces. We ran the public proof-of-concept for eleven exploits and two misconfigurations, and noted which rules fired.
Blog
Hand-picked stories from our editors — threat detection, audit logging, and security operations insights.
Not another Log4Shell: inside the Log4j 2 deserialization allowlist bypass
We reproduced this java deserialization vulnerability against official Log4j 2.26.1 JARs. Getting to command execution took two more things that Log4j itself does not ship. Here is how the bypass works, which versions carry it, and what to hunt for.
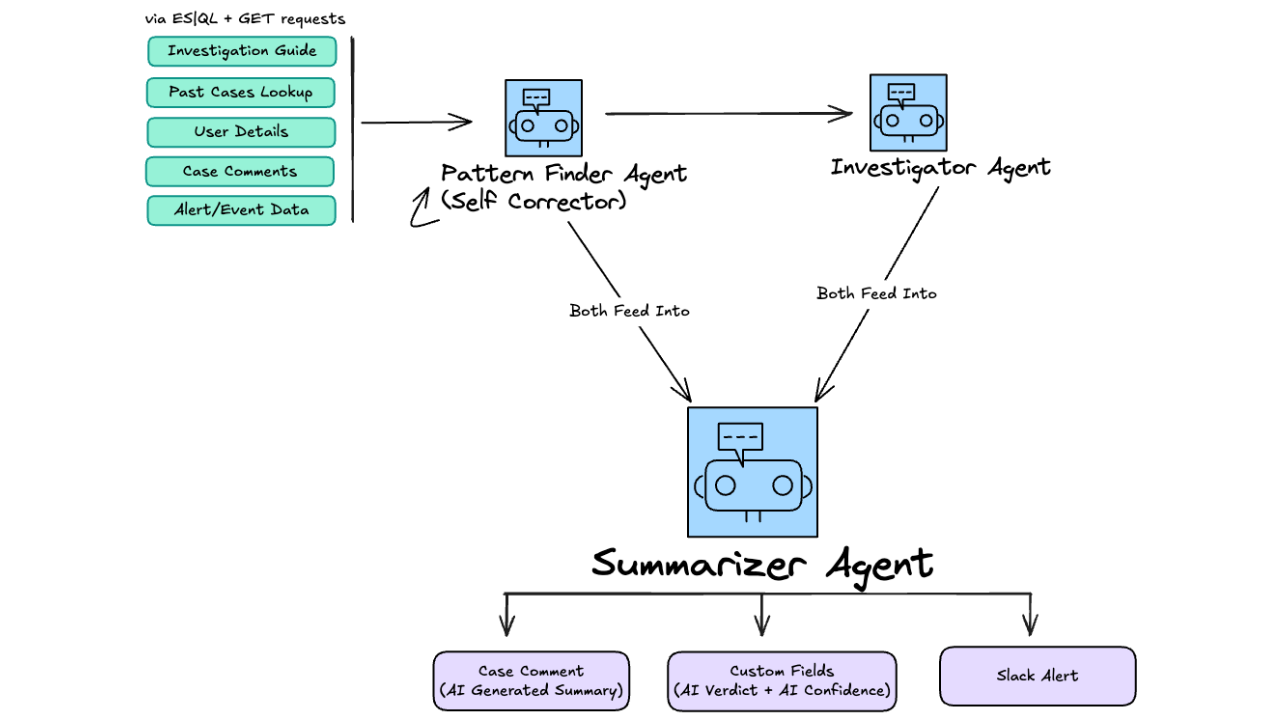
Inside Elastic's agentic SOC: How we took AI alert triage from 60% to 92% accuracy
Elastic's InfoSec team runs three agents that read the detection rule's investigation guide and the closure reasons on 30 days of past cases. Analysts now clear most alerts with a single click in Slack.
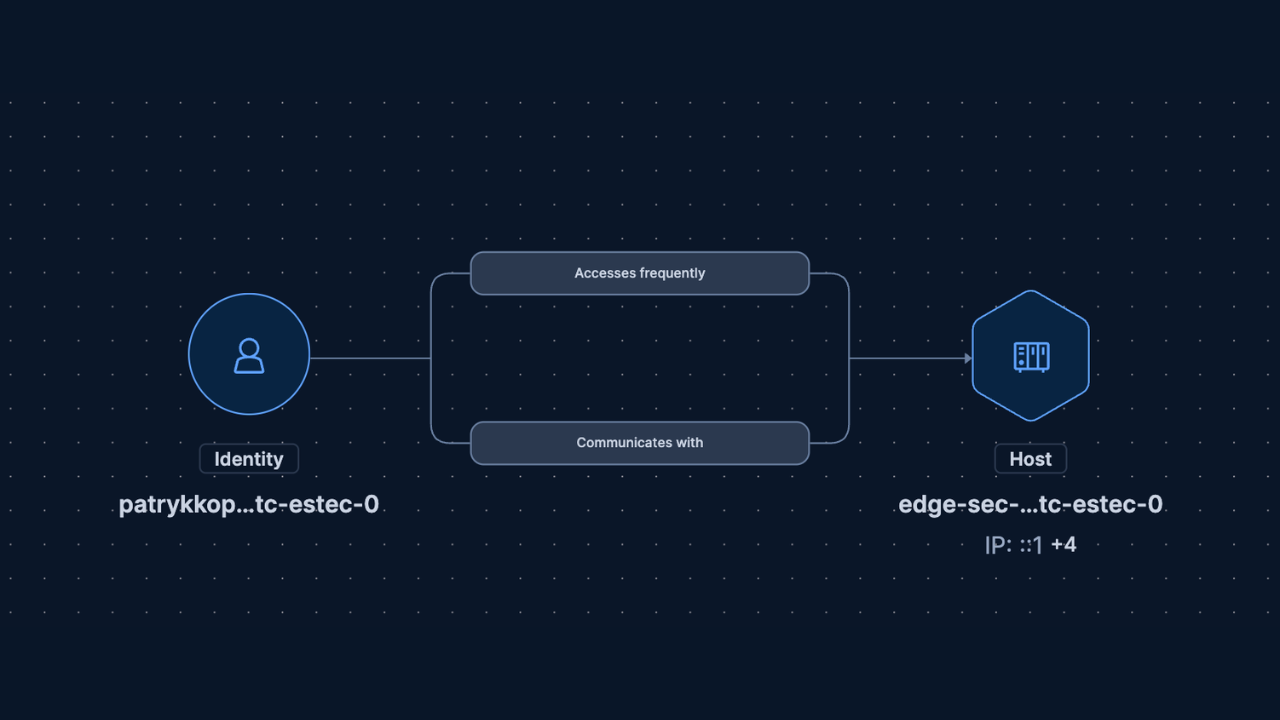
How a team of entity maintainers monitors, connects and scores entities in Elastic Security
Inside Elastic Security, background jobs called maintainers each own one piece of every user, host and service record, from building entities out of raw logs to resolving identities and scoring risk.
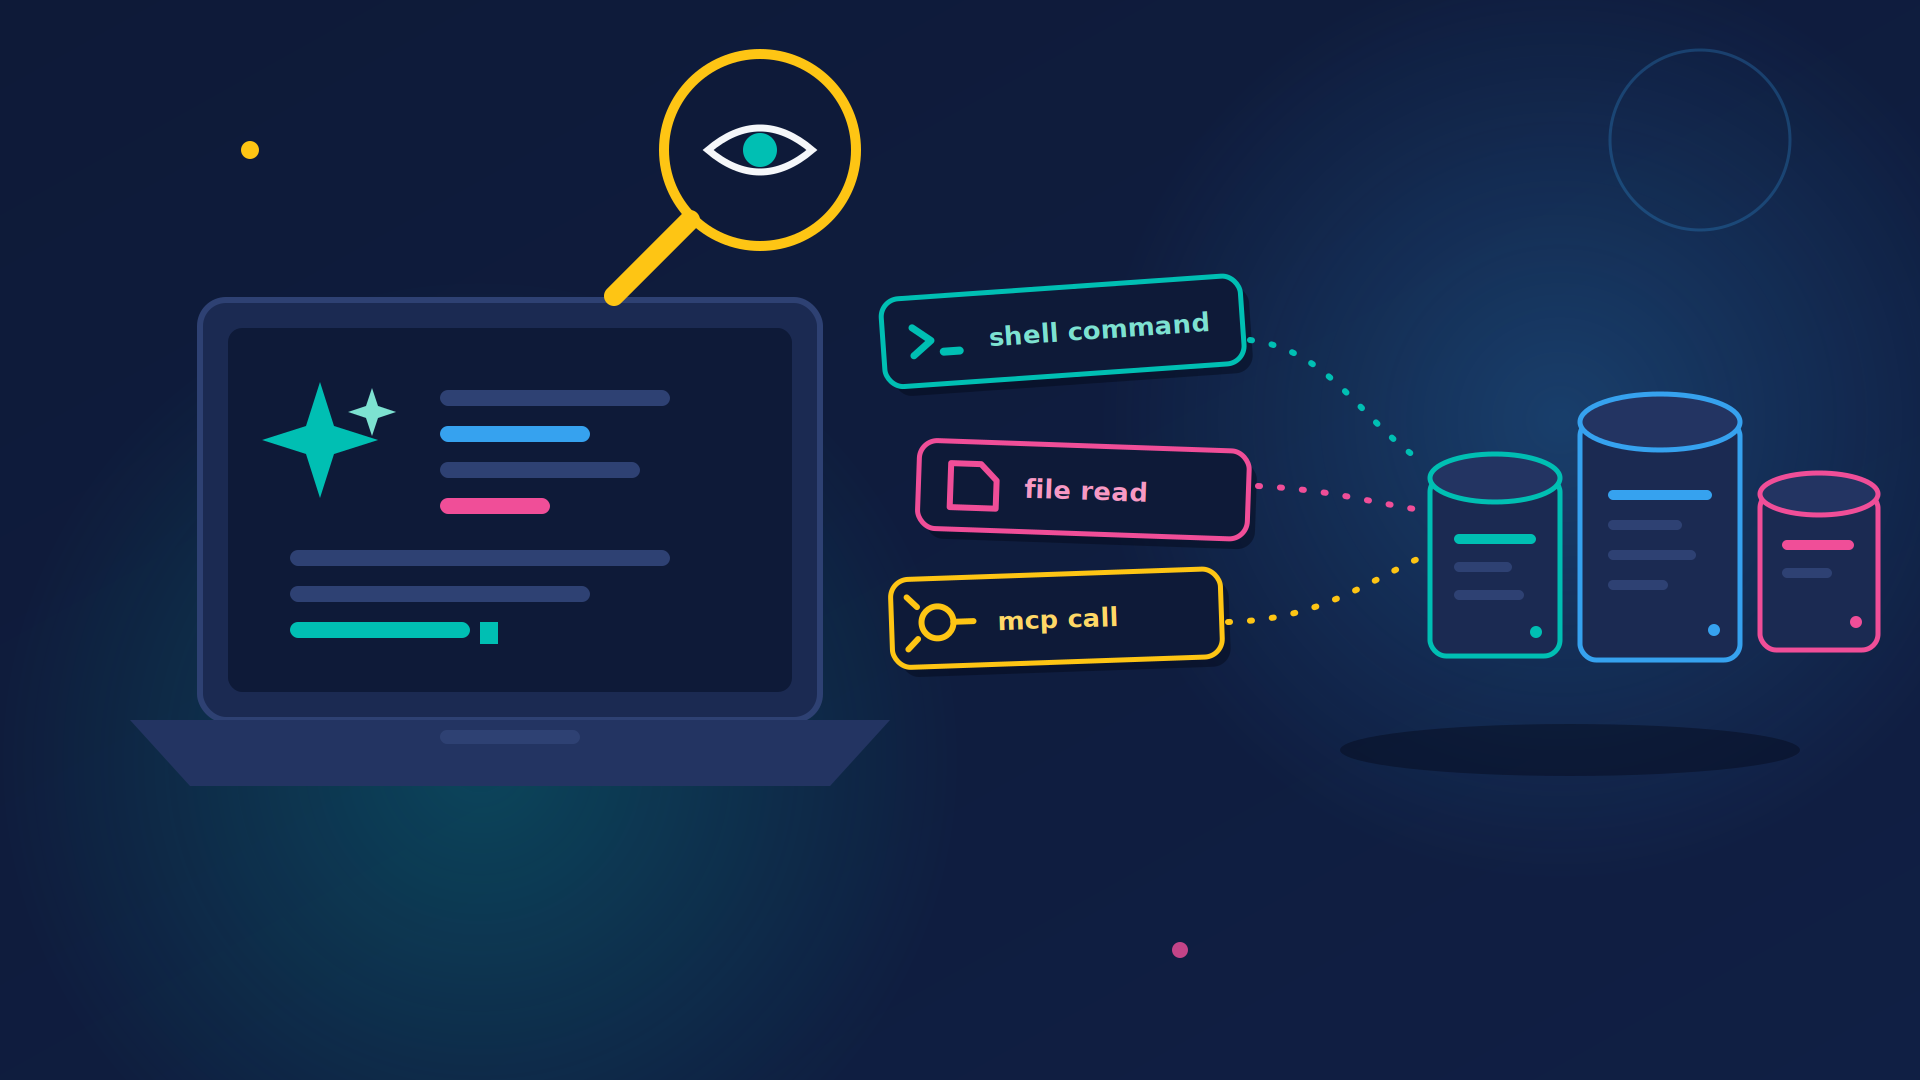
13 million tool calls: auditing every AI coding agent action with Elastic Agent
Cursor hooks and Elastic Agent capture every tool call, shell command, file read and MCP request as structured events you can hunt with ES|QL.
The security signal log tailing can't see: tracking npm cooldown removals with Elastic Agent
A 40-line CEL integration snapshots .npmrc files every 6 hours to catch cooldown removals. This post walks through the three ways we broke filestream before landing on snapshot semantics.
Agents vs. agents: how we triage HackerOne reports for $2 each, 85% as well as a human
LLMs made it cheap to flood bug bounty programs with submissions. Here's how Elastic built an AI triage agent that matches human decisions 85% of the time, including the architecture, threat model and calibration against 3,300 real reports
SOC case management and detection rule history in Elastic Security
Elastic Security now tracks every detection rule change with one-click rollback and makes case data queryable out of the box, so SOC teams get audit trails and reporting without configuring anything.
Elastic goes all-in on Hacker Summer Camp at Black Hat and DEF CON in Las Vegas
Attack Discovery turns raw alerts into validated threats and Elastic Defend closes vulnerable driver gaps as fast as they're disclosed. Watch it all run against real attacks at the booth.
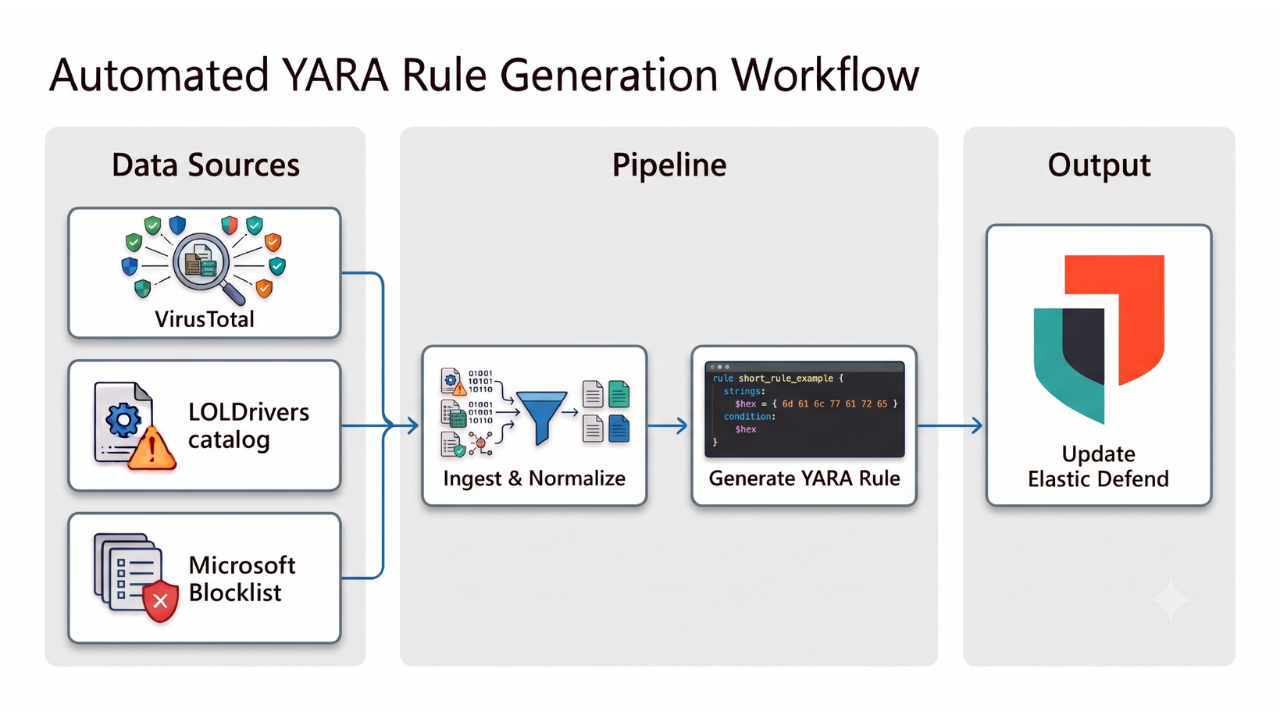
What's new in Elastic Defend: 800+ vulnerable driver rules, automated troubleshooting, and ARM support
Elastic Defend automatically generates and instantly deploys vulnerable driver YARA rules from VirusTotal, LOLDrivers and Microsoft's blocklist, closing the gap BYOVD attacks depend on. Plus a new troubleshooting skill and ARM endpoint protection.
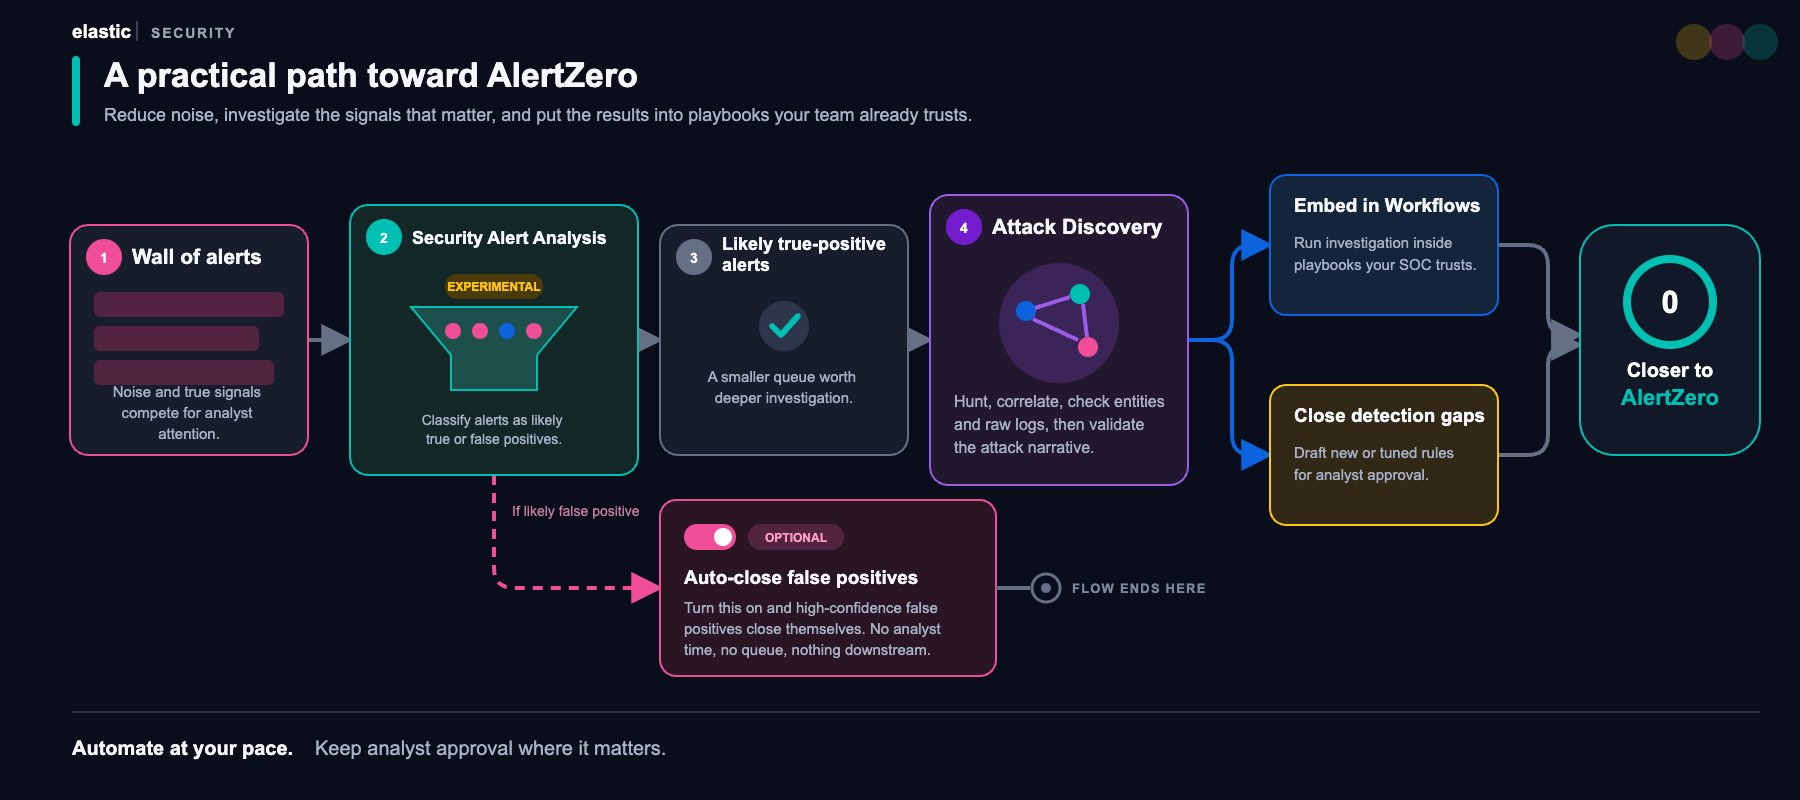
Alert Zero: AI-driven alert triage and attack investigation for the agentic SOC
Elastic Security 9.5 gives SOC teams AI that handles first-pass alert triage and investigation, so analysts can get back to threat hunting and detection engineering instead of working through queue noise.
Stop rewriting detection rules by hand: automatic Sentinel-to-Elastic migration is here
Elastic's first automatic migration from a modern SIEM. Translate your Sentinel detection rules into Elastic Security without rebuilding them.
Inside Elastic InfoSec's agentic SOC: How we cut AI agent LLM calls by 60%
We run fourteen AI agents that triage Elastic InfoSec alerts. They were taking 19 LLM calls to do work that needed 8. Here's the five-step optimization loop we run across the fleet, plus the prompt template you can use with any AI assistant.
Inside Elastic InfoSec's agentic SOC: When to inline your agent's skills for a 5× cost reduction
We tested two agentic SOC architectures in parallel across 36,822 real Agent Builder conversations. One won by 5.7x: a specialized workflow triaging alerts for $0.69 each, against $3.42 for a single agent juggling 14 Skills. The data and the decision framework are both below.
wp2shell hits WordPress: detecting pre-auth RCE from plugin drop to command execution
We ran the wp2shell WordPress RCE chain end-to-end with Elastic Defend. Detection rule walkthrough, IOCs, and hunt guidance.
How Elasticsearch ES|QL COMPLETION turns noisy curl and wget rules into high-fidelity cloud security alerts
Elastic InfoSec tested this detection rule pattern on their own cloud fleet, filtering noisy curl and wget events with deterministic logic and LLM triage so only genuine threats reach an analyst.