AI-native SIEM that shows its work
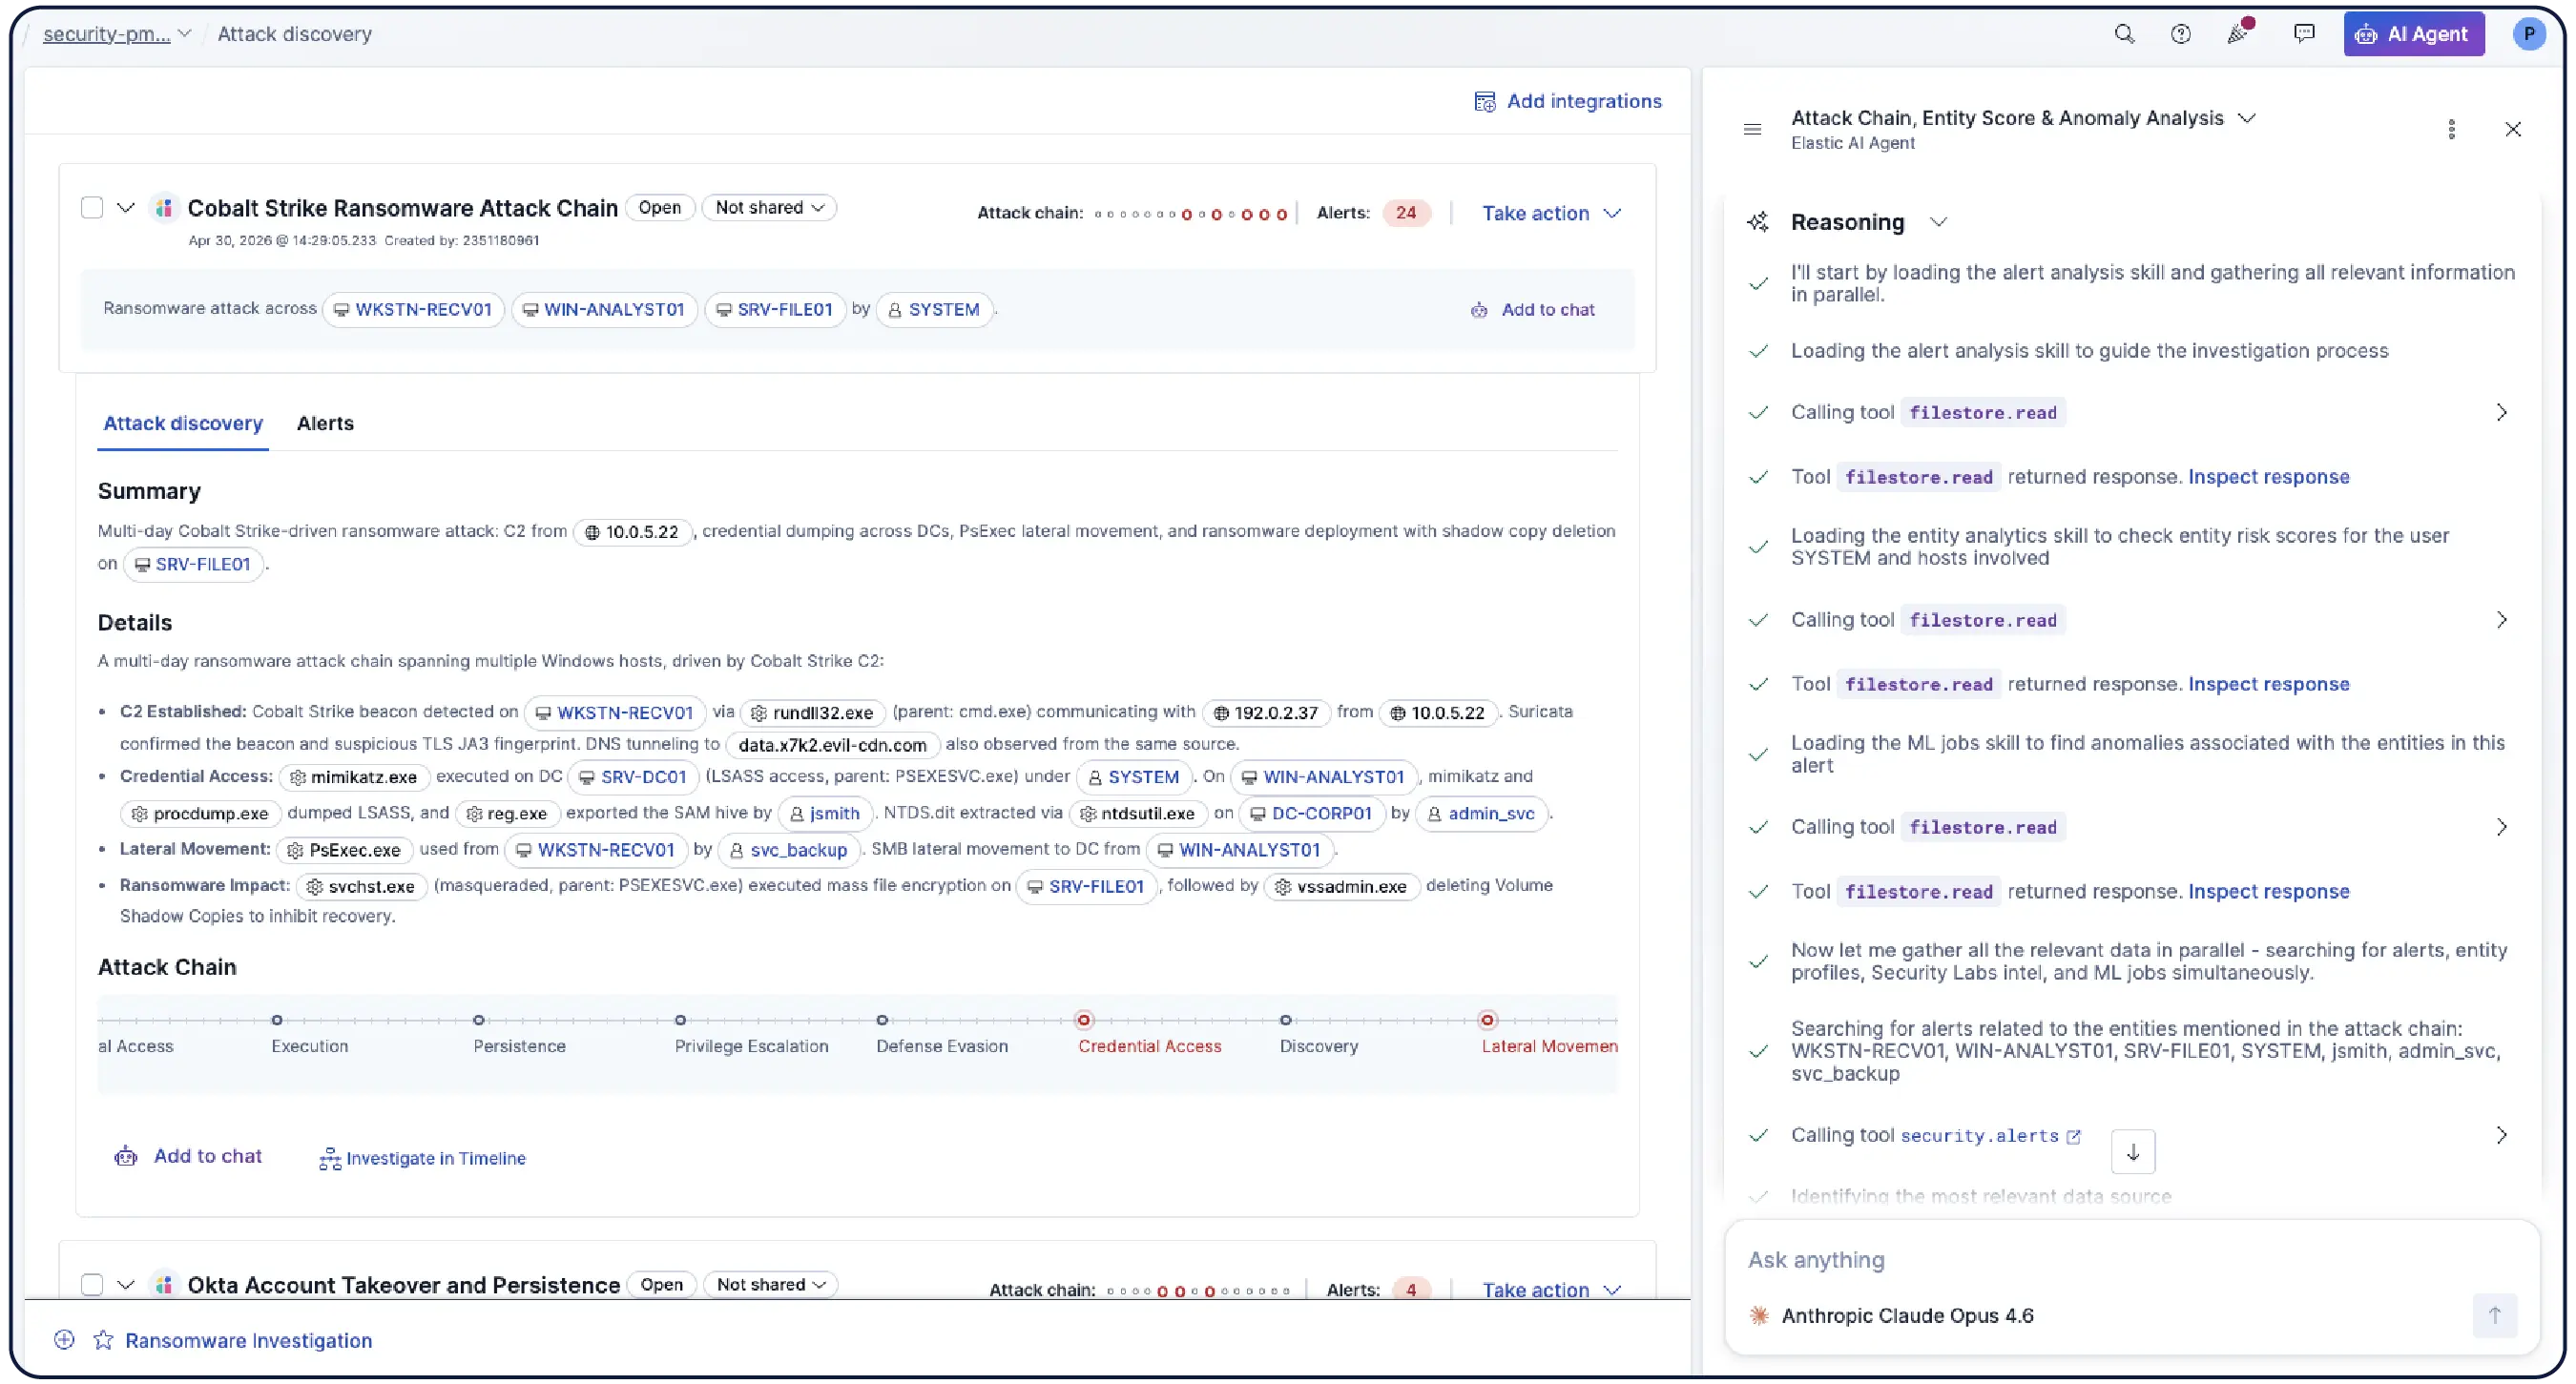
Building on detection and correlation, AlertZero, the agentic layer of Elastic Security, connects triage, threat hunting, detection engineering, and forensics. Every alert gets a verdict and evidence, and every decision stays yours.

DIFFERENTIATORS
Built by security users, for security users
Elastic Security brings AI-native SIEM, endpoint protection, native automation, and agentic security operations together on one open platform. Agents reason over your data where it lives, on the model you choose, and show how they reached each conclusion. Elastic removes the vendor-imposed barriers, so nothing stands between your team and getting security done.


You're in good company
Customer spotlight
 Airtel improves cyber posture with Elastic’s AI capabilities, boosting SOC efficiency by 40% and accelerating investigations by 30%.
Customer spotlight
California EDD reduced mean time to response by 99%, using Attack Discovery to prioritize alerts across 80,000 monthly events and surface the most critical threats.
Customer spotlight

Mimecast centralizes visibility, drives investigations, and cuts critical incidents by 95%, transforming global SecOps.
DETECT. INVESTIGATE. RESPOND.
The SIEM built for the agentic SOC
Detection to response, all in one platform. Autonomous agents run the full lifecycle. Your analysts handle judgment, verification, and approval.
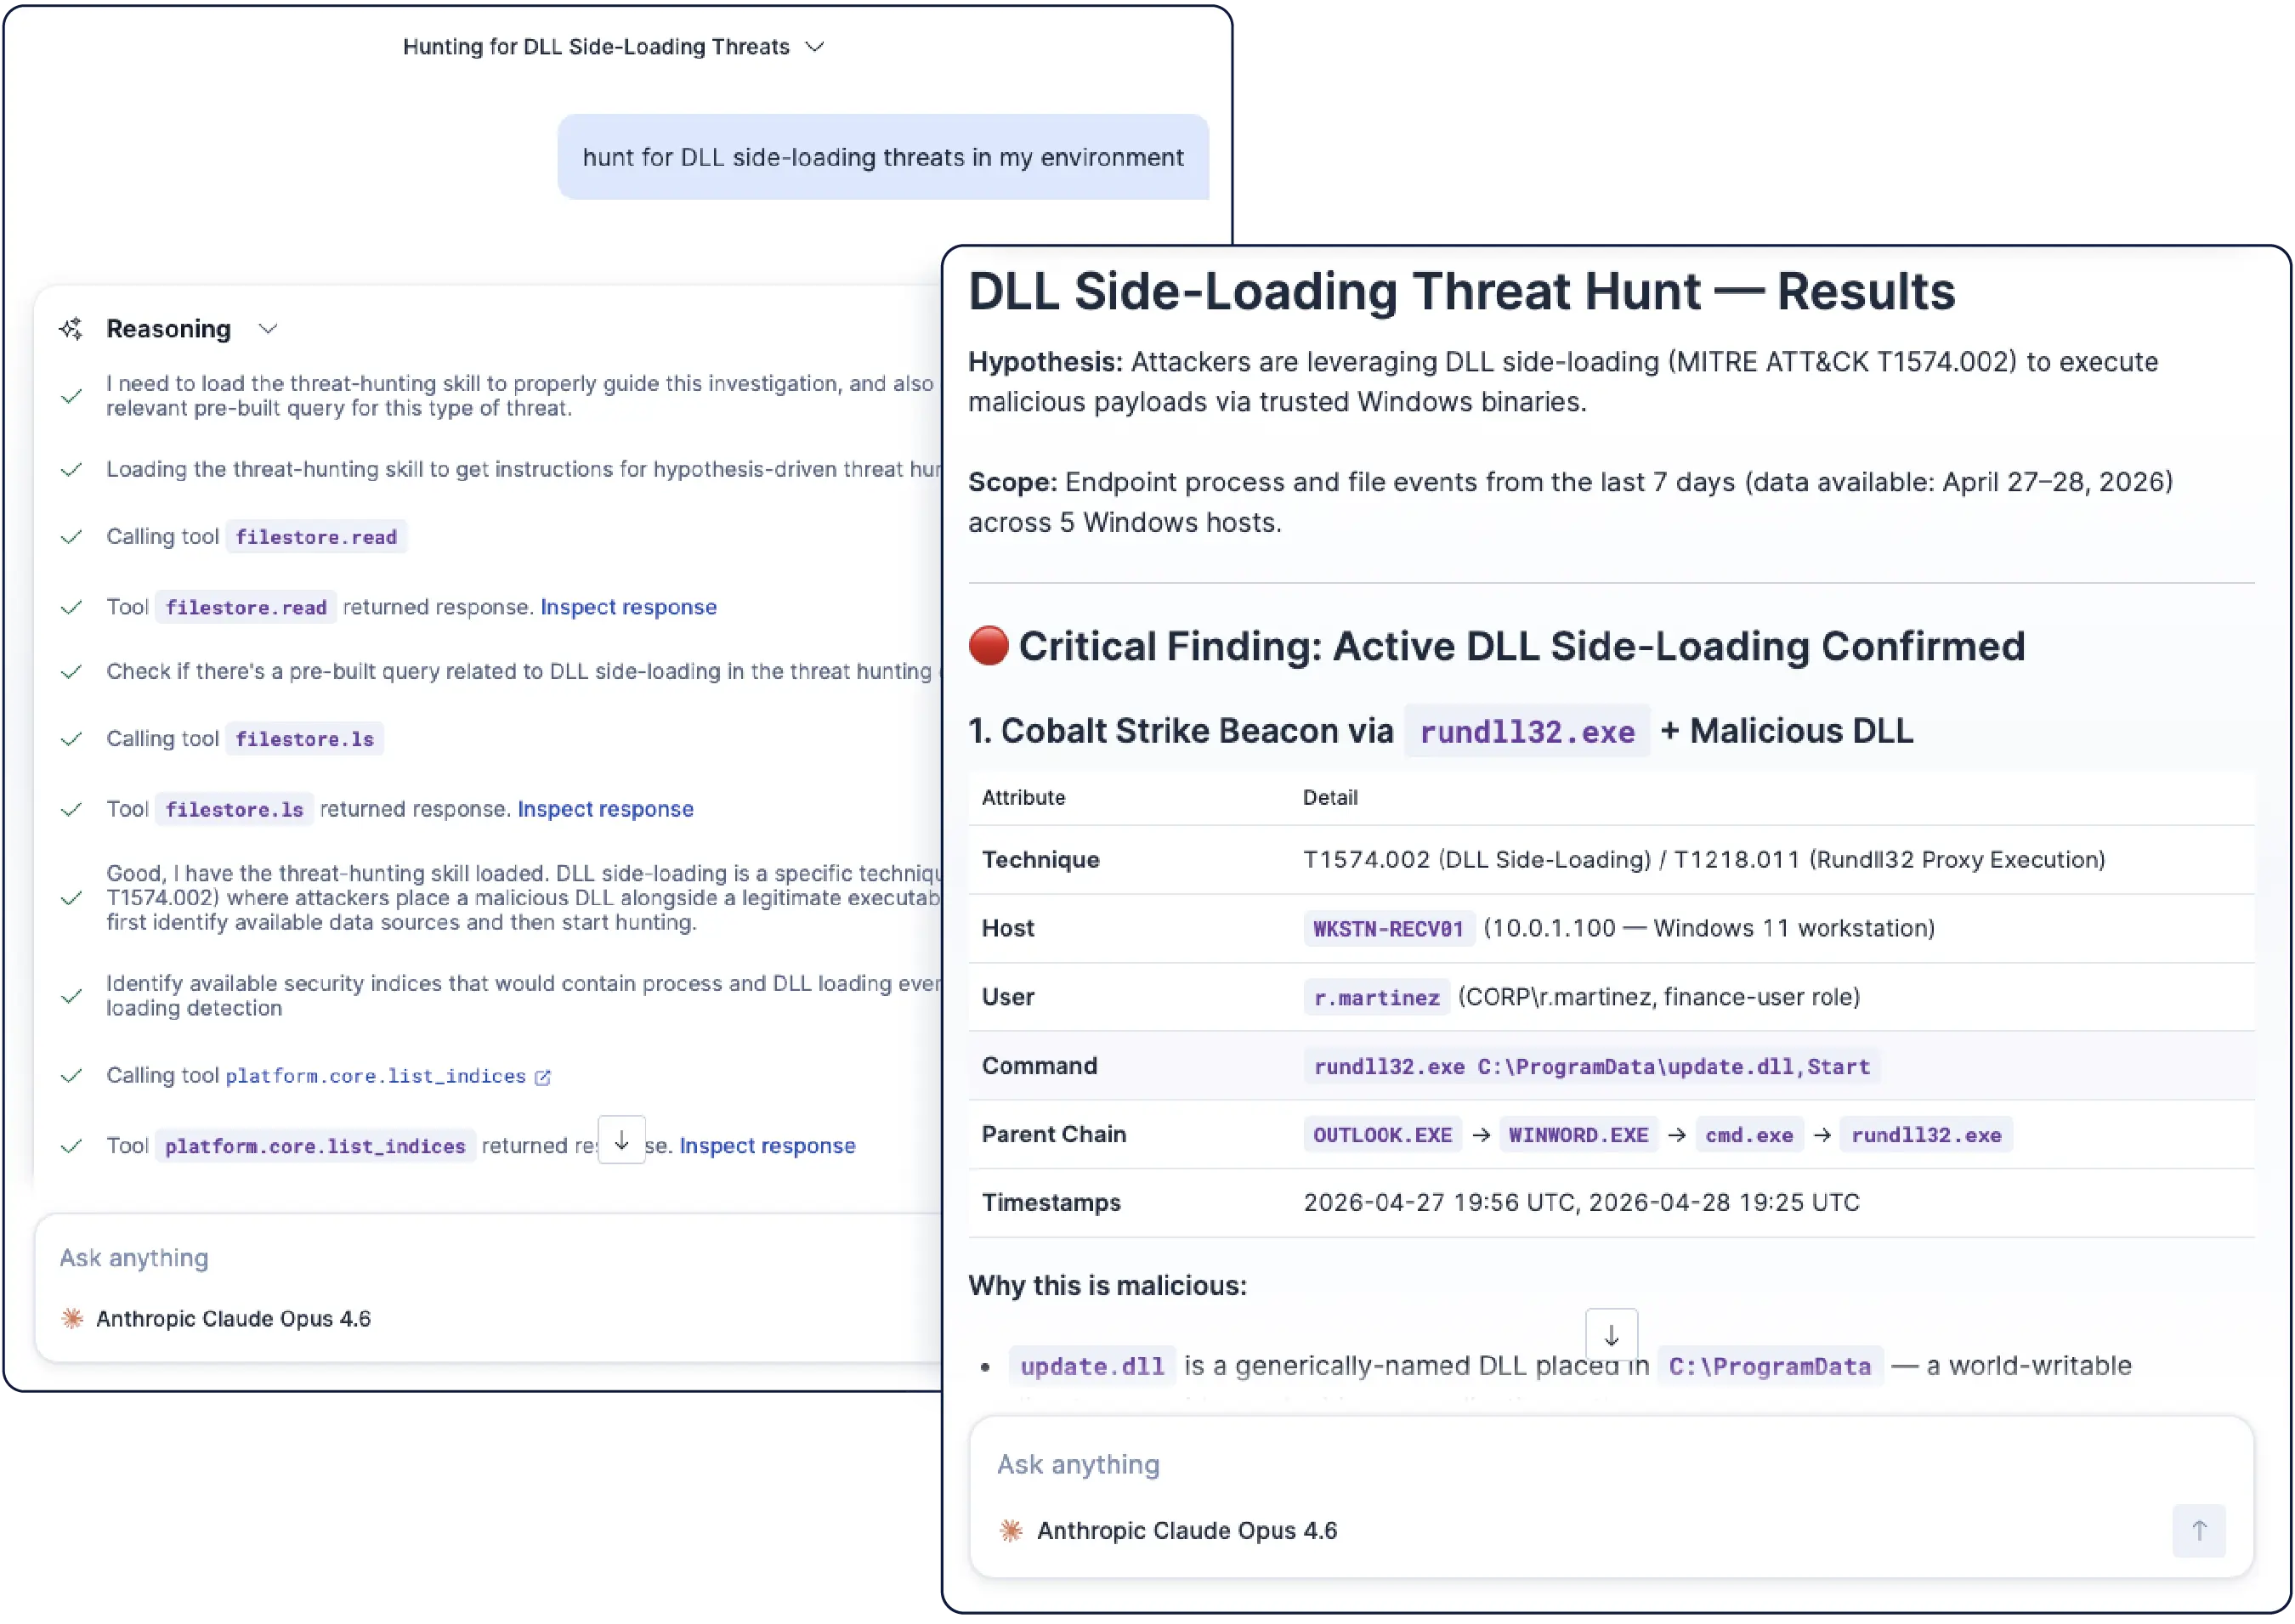
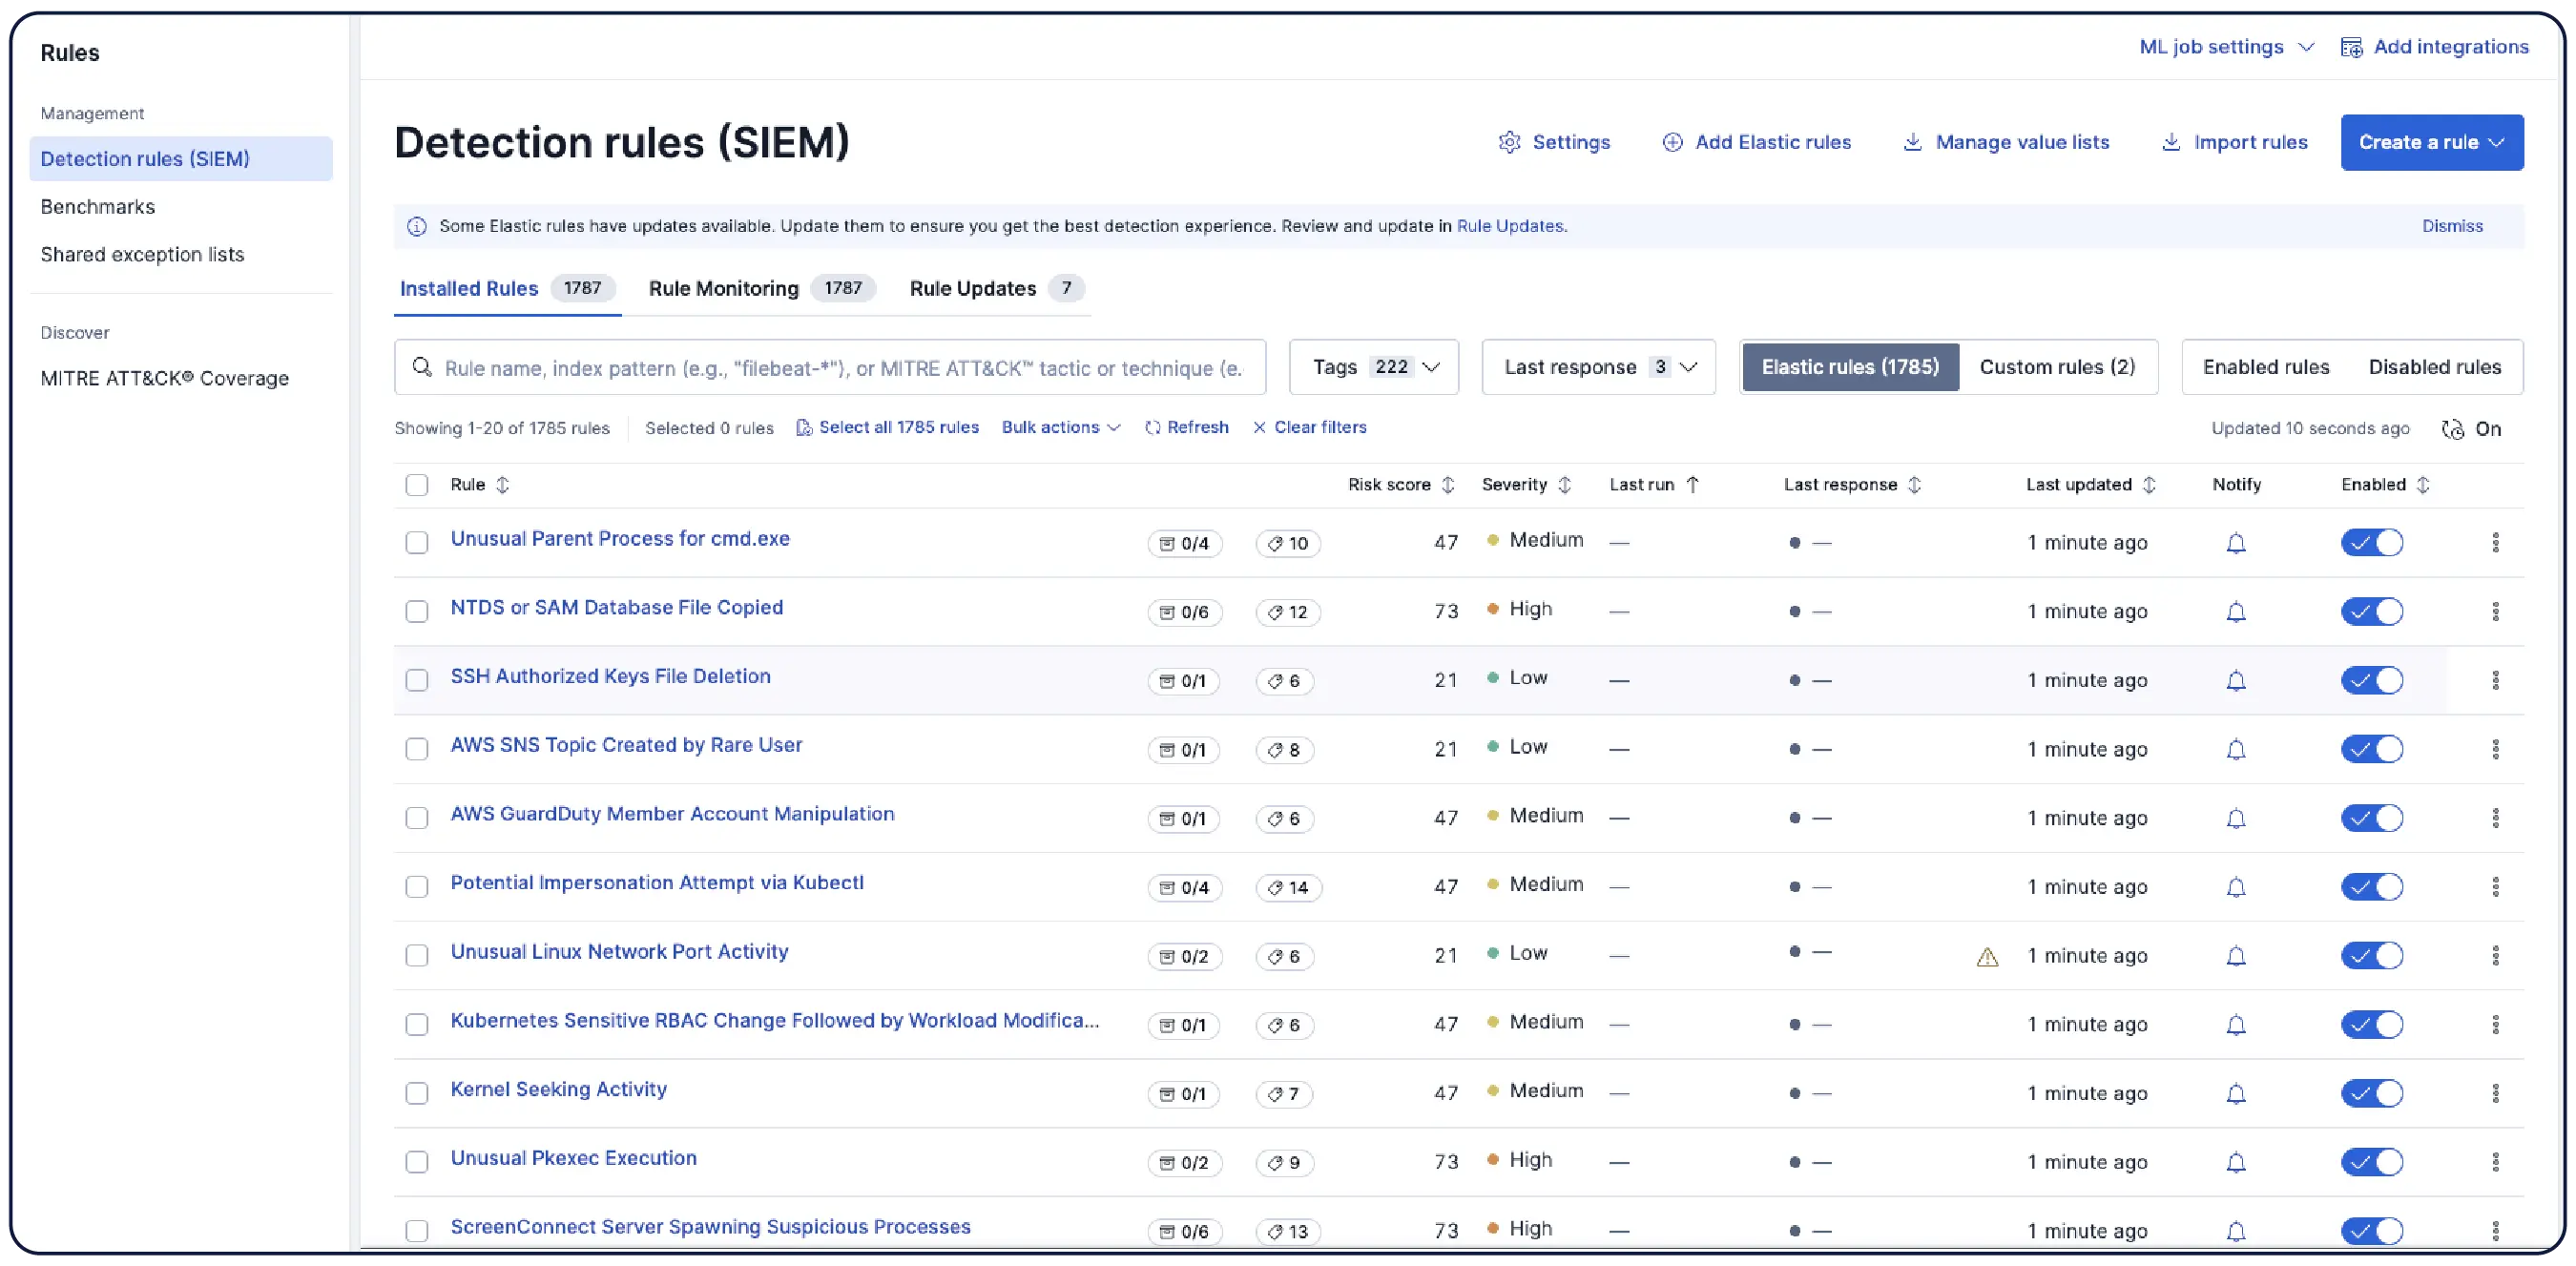
Find threats before they surface as alerts. The Threat Hunt skill executes hypothesis-driven hunts from threat intel, runs ES|QL queries against live data, and maps findings to MITRE ATT&CK automatically. For on-demand hunts, describe the threat in plain language and get a validated query built by Elastic Security Threat Command researchers.
Security where you work
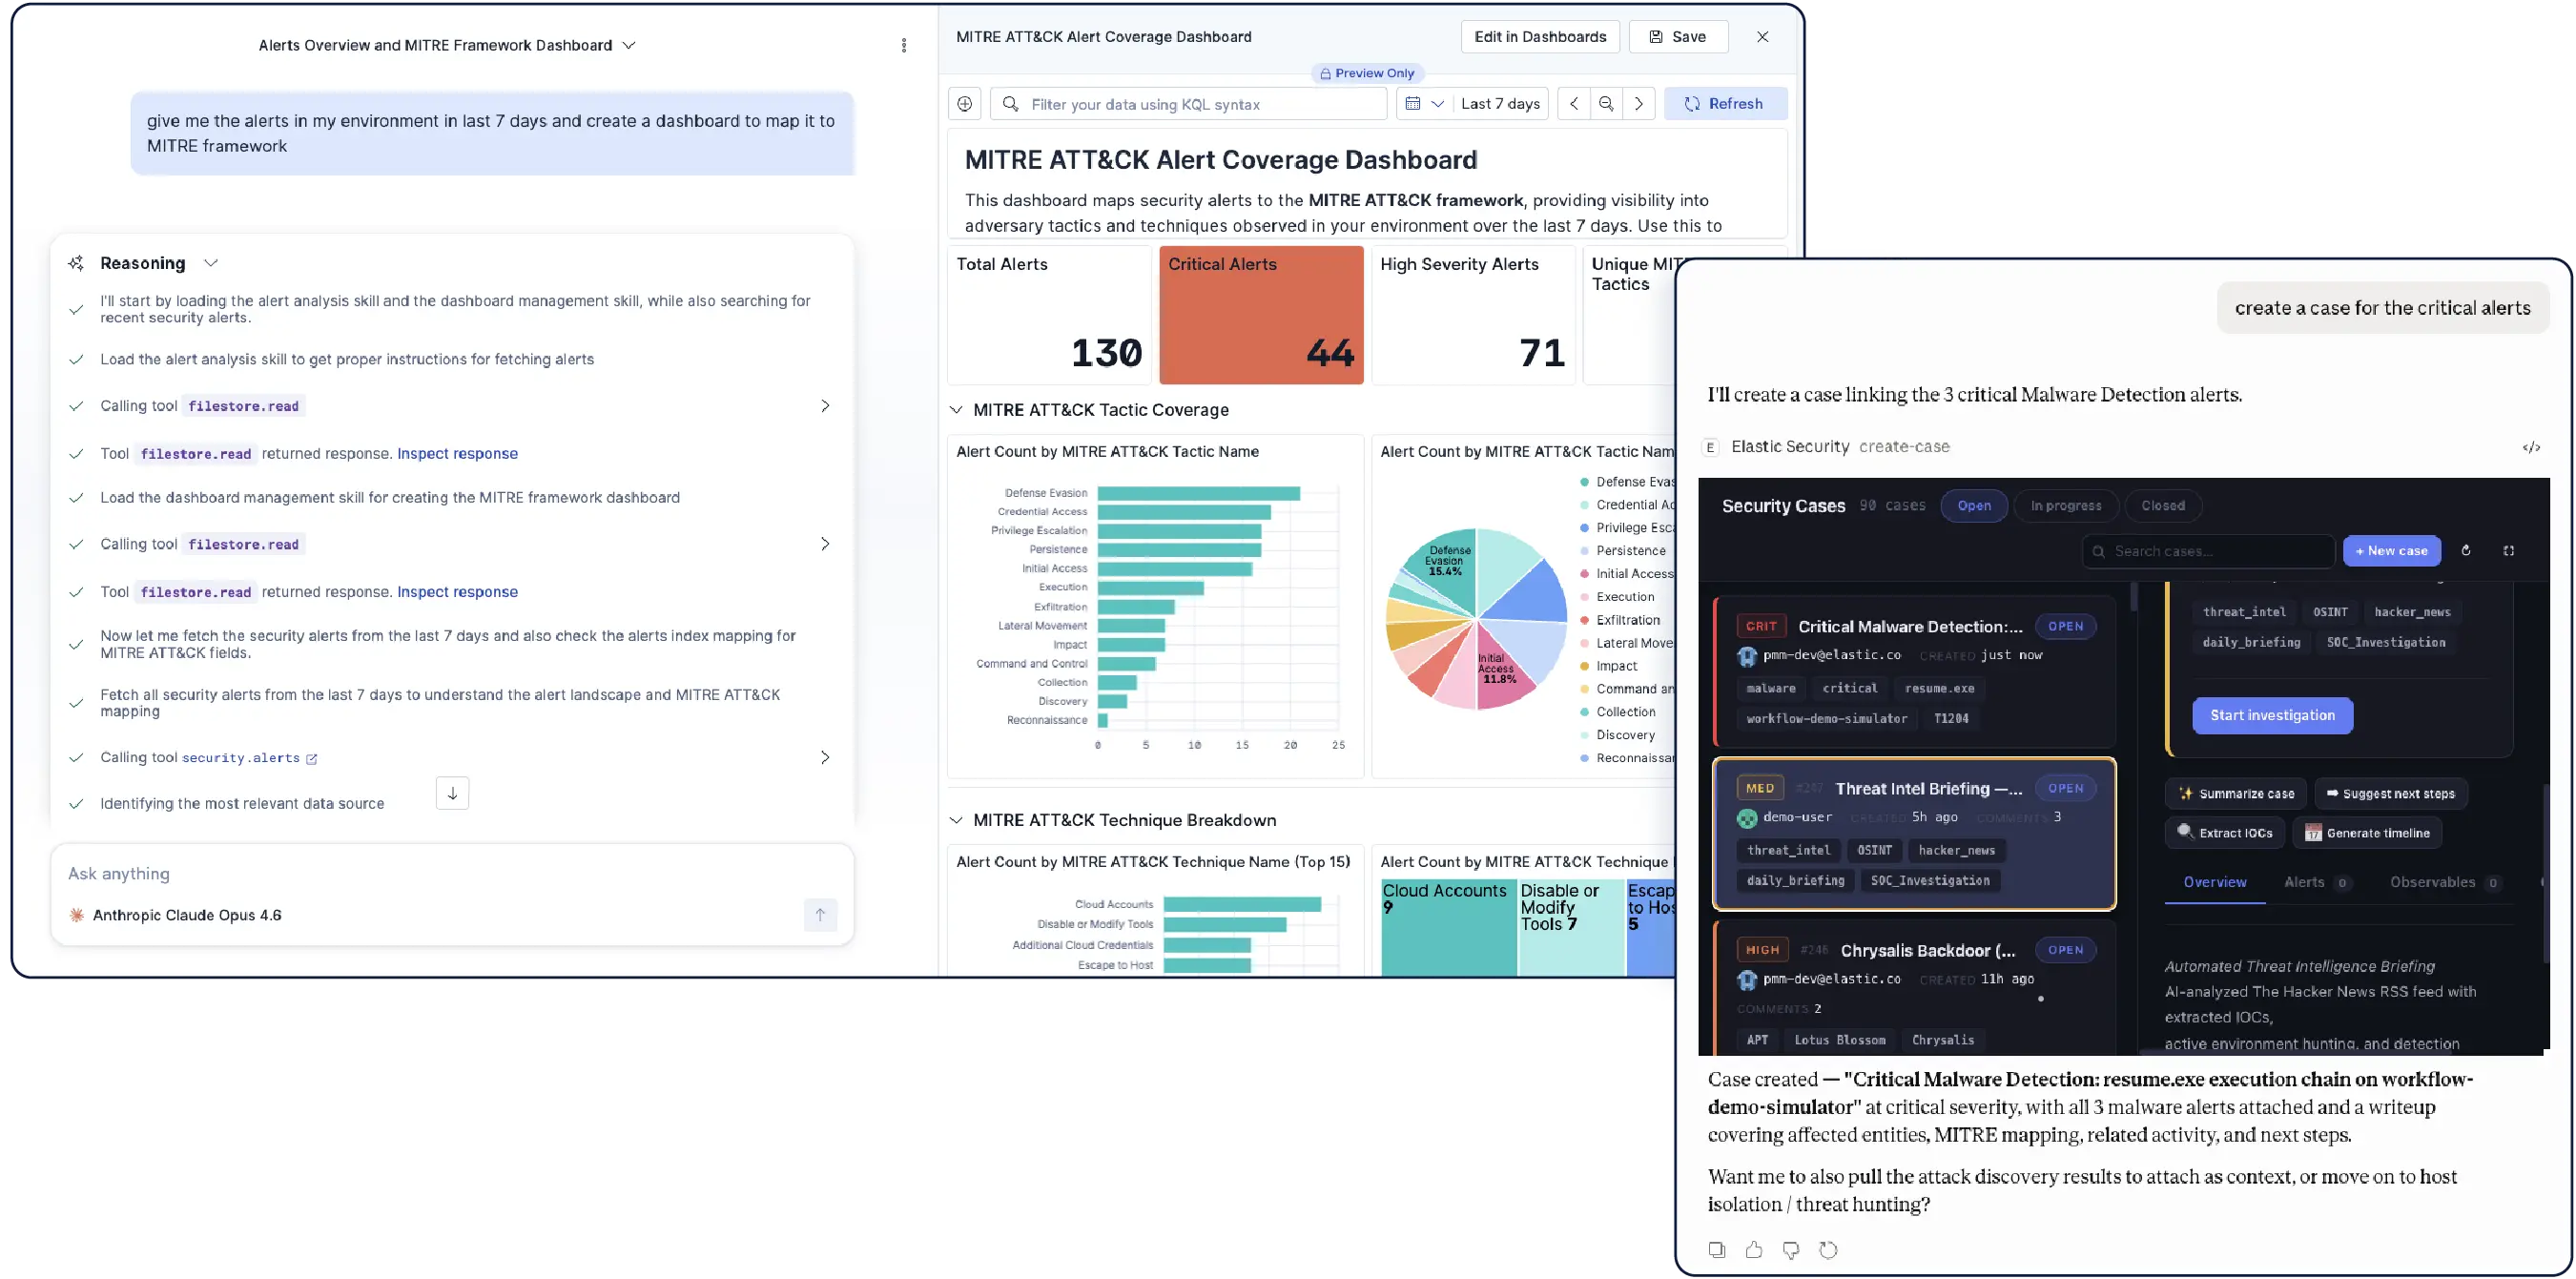
The same composable AI skills, across every surface security analysts use
Chat-first, wherever you work
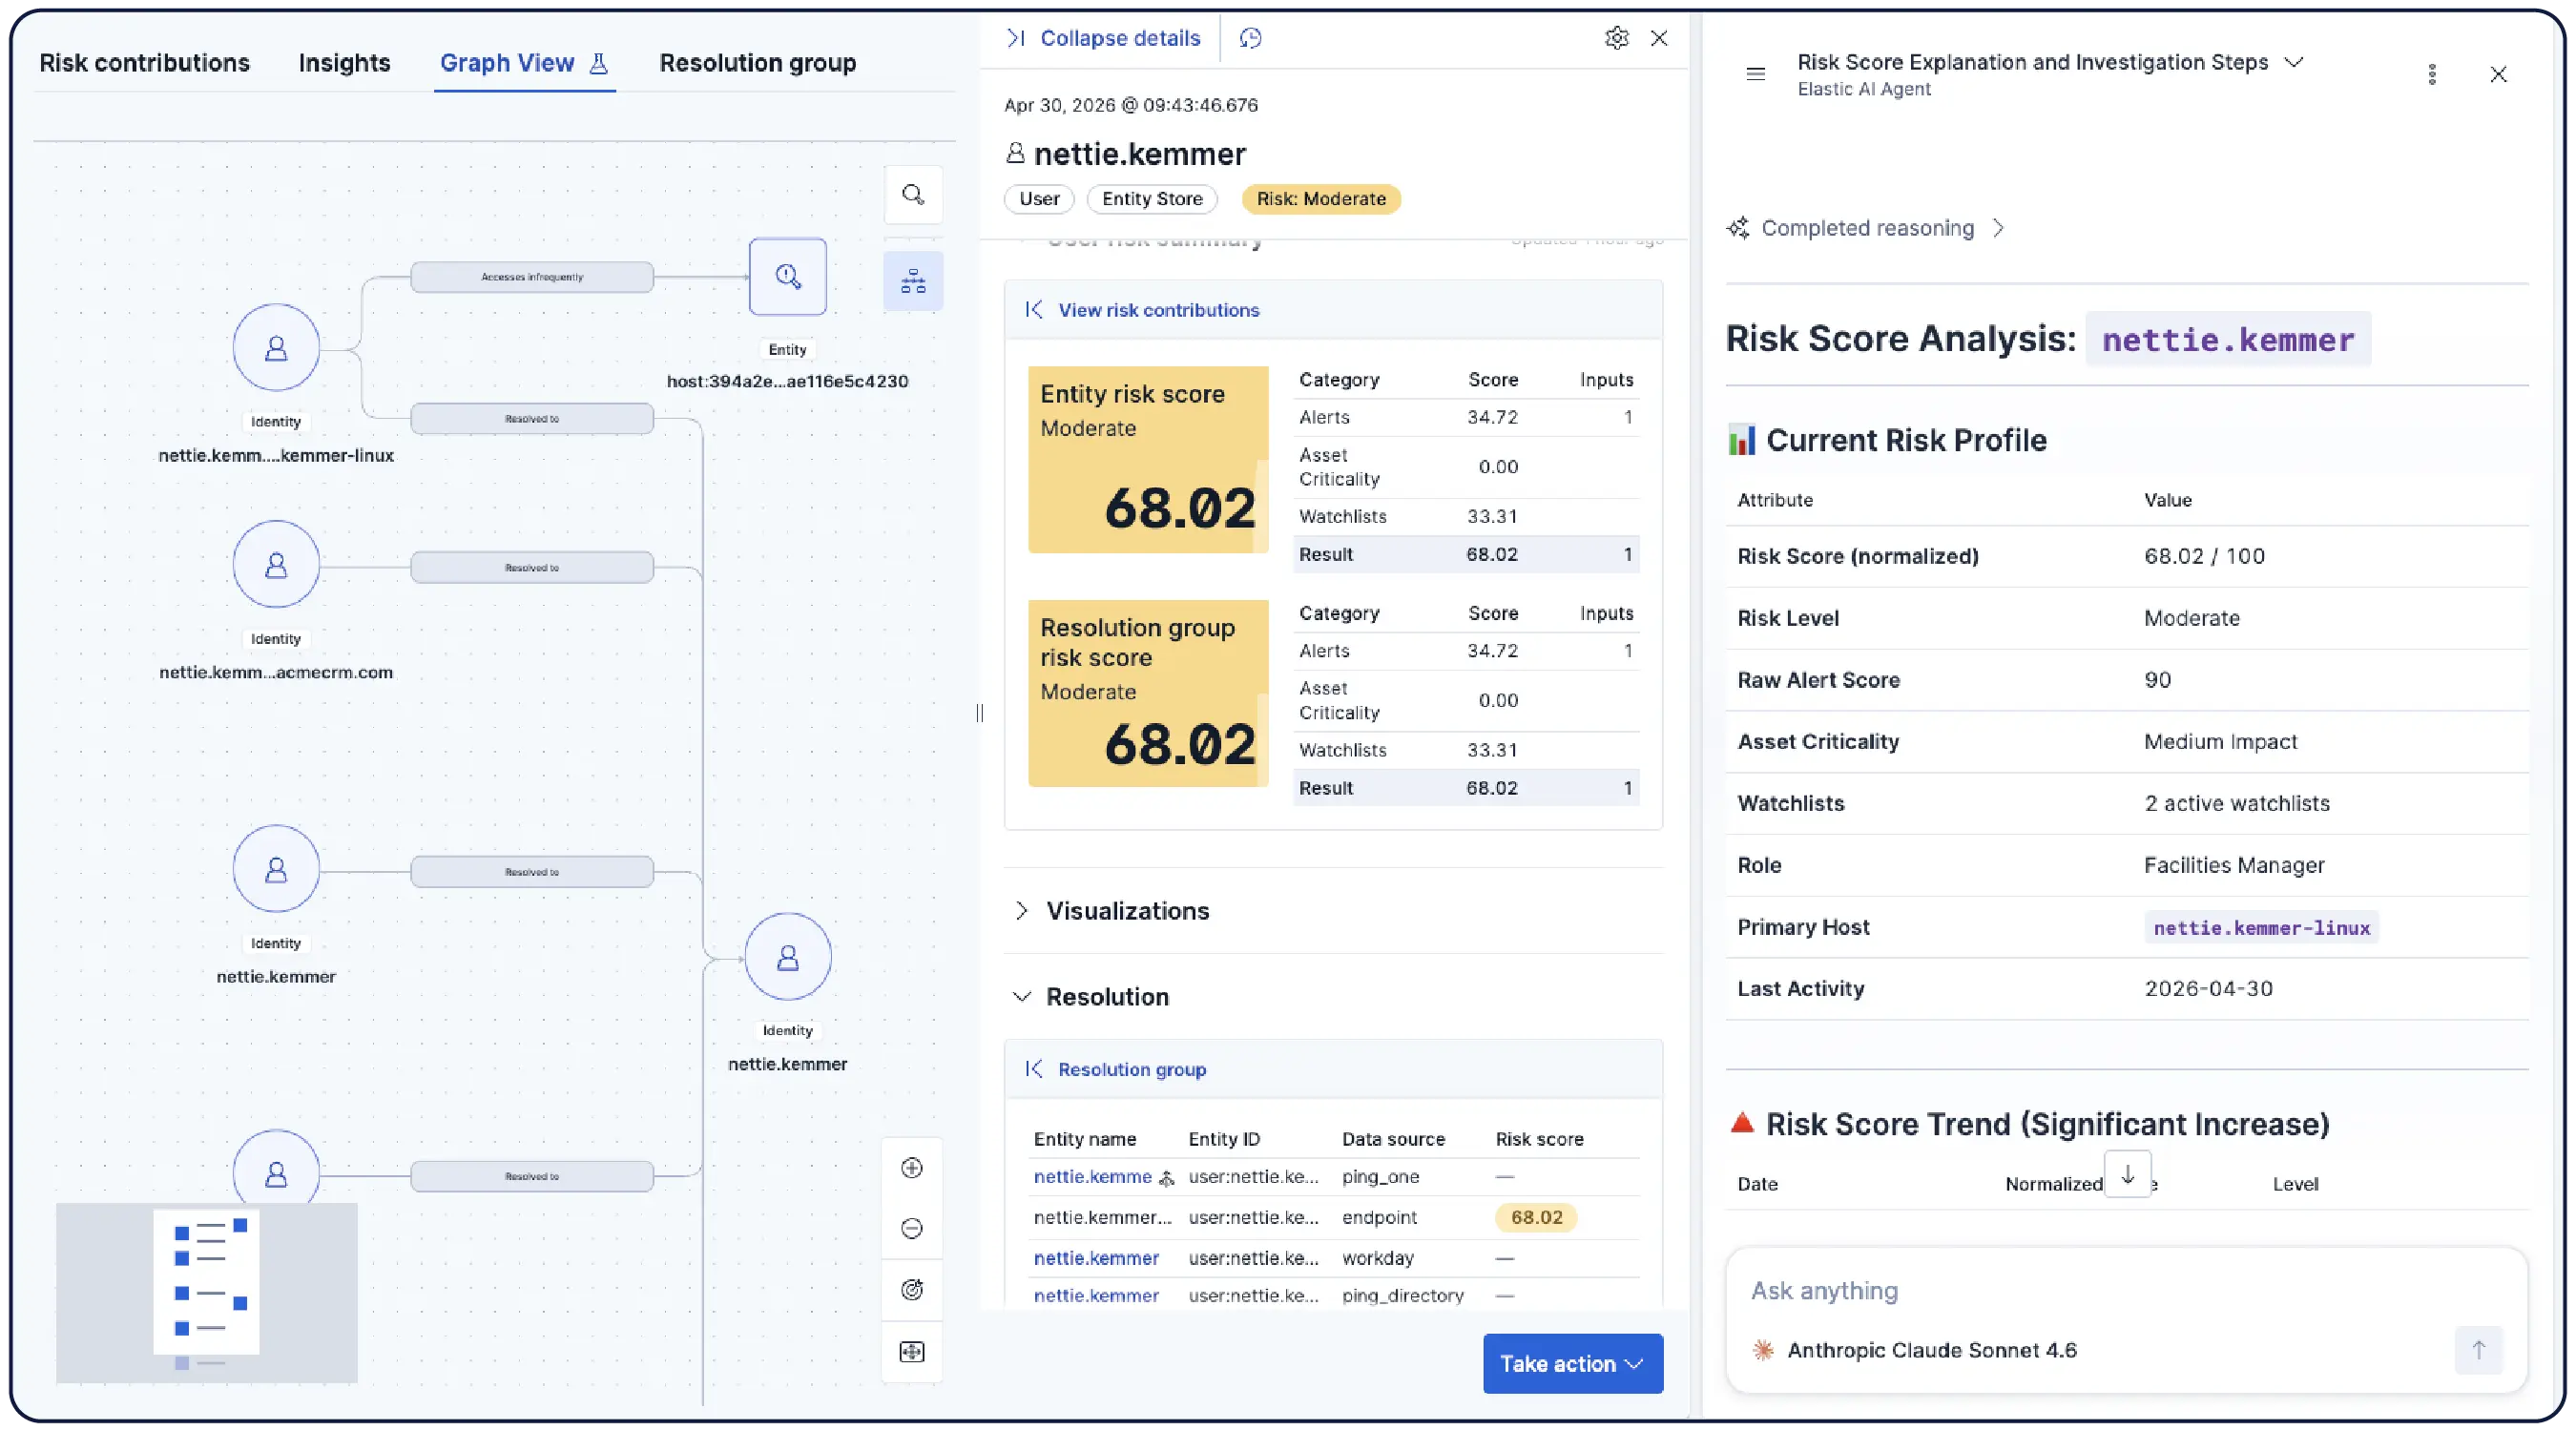
Ask questions and get interactive triage dashboards, investigation graphs, editable detection rules, attack chains, and case actions — from inside Elastic Security or directly from Claude, VS Code, Cursor, and any MCP-compatible AI tool.
Purpose-built product views
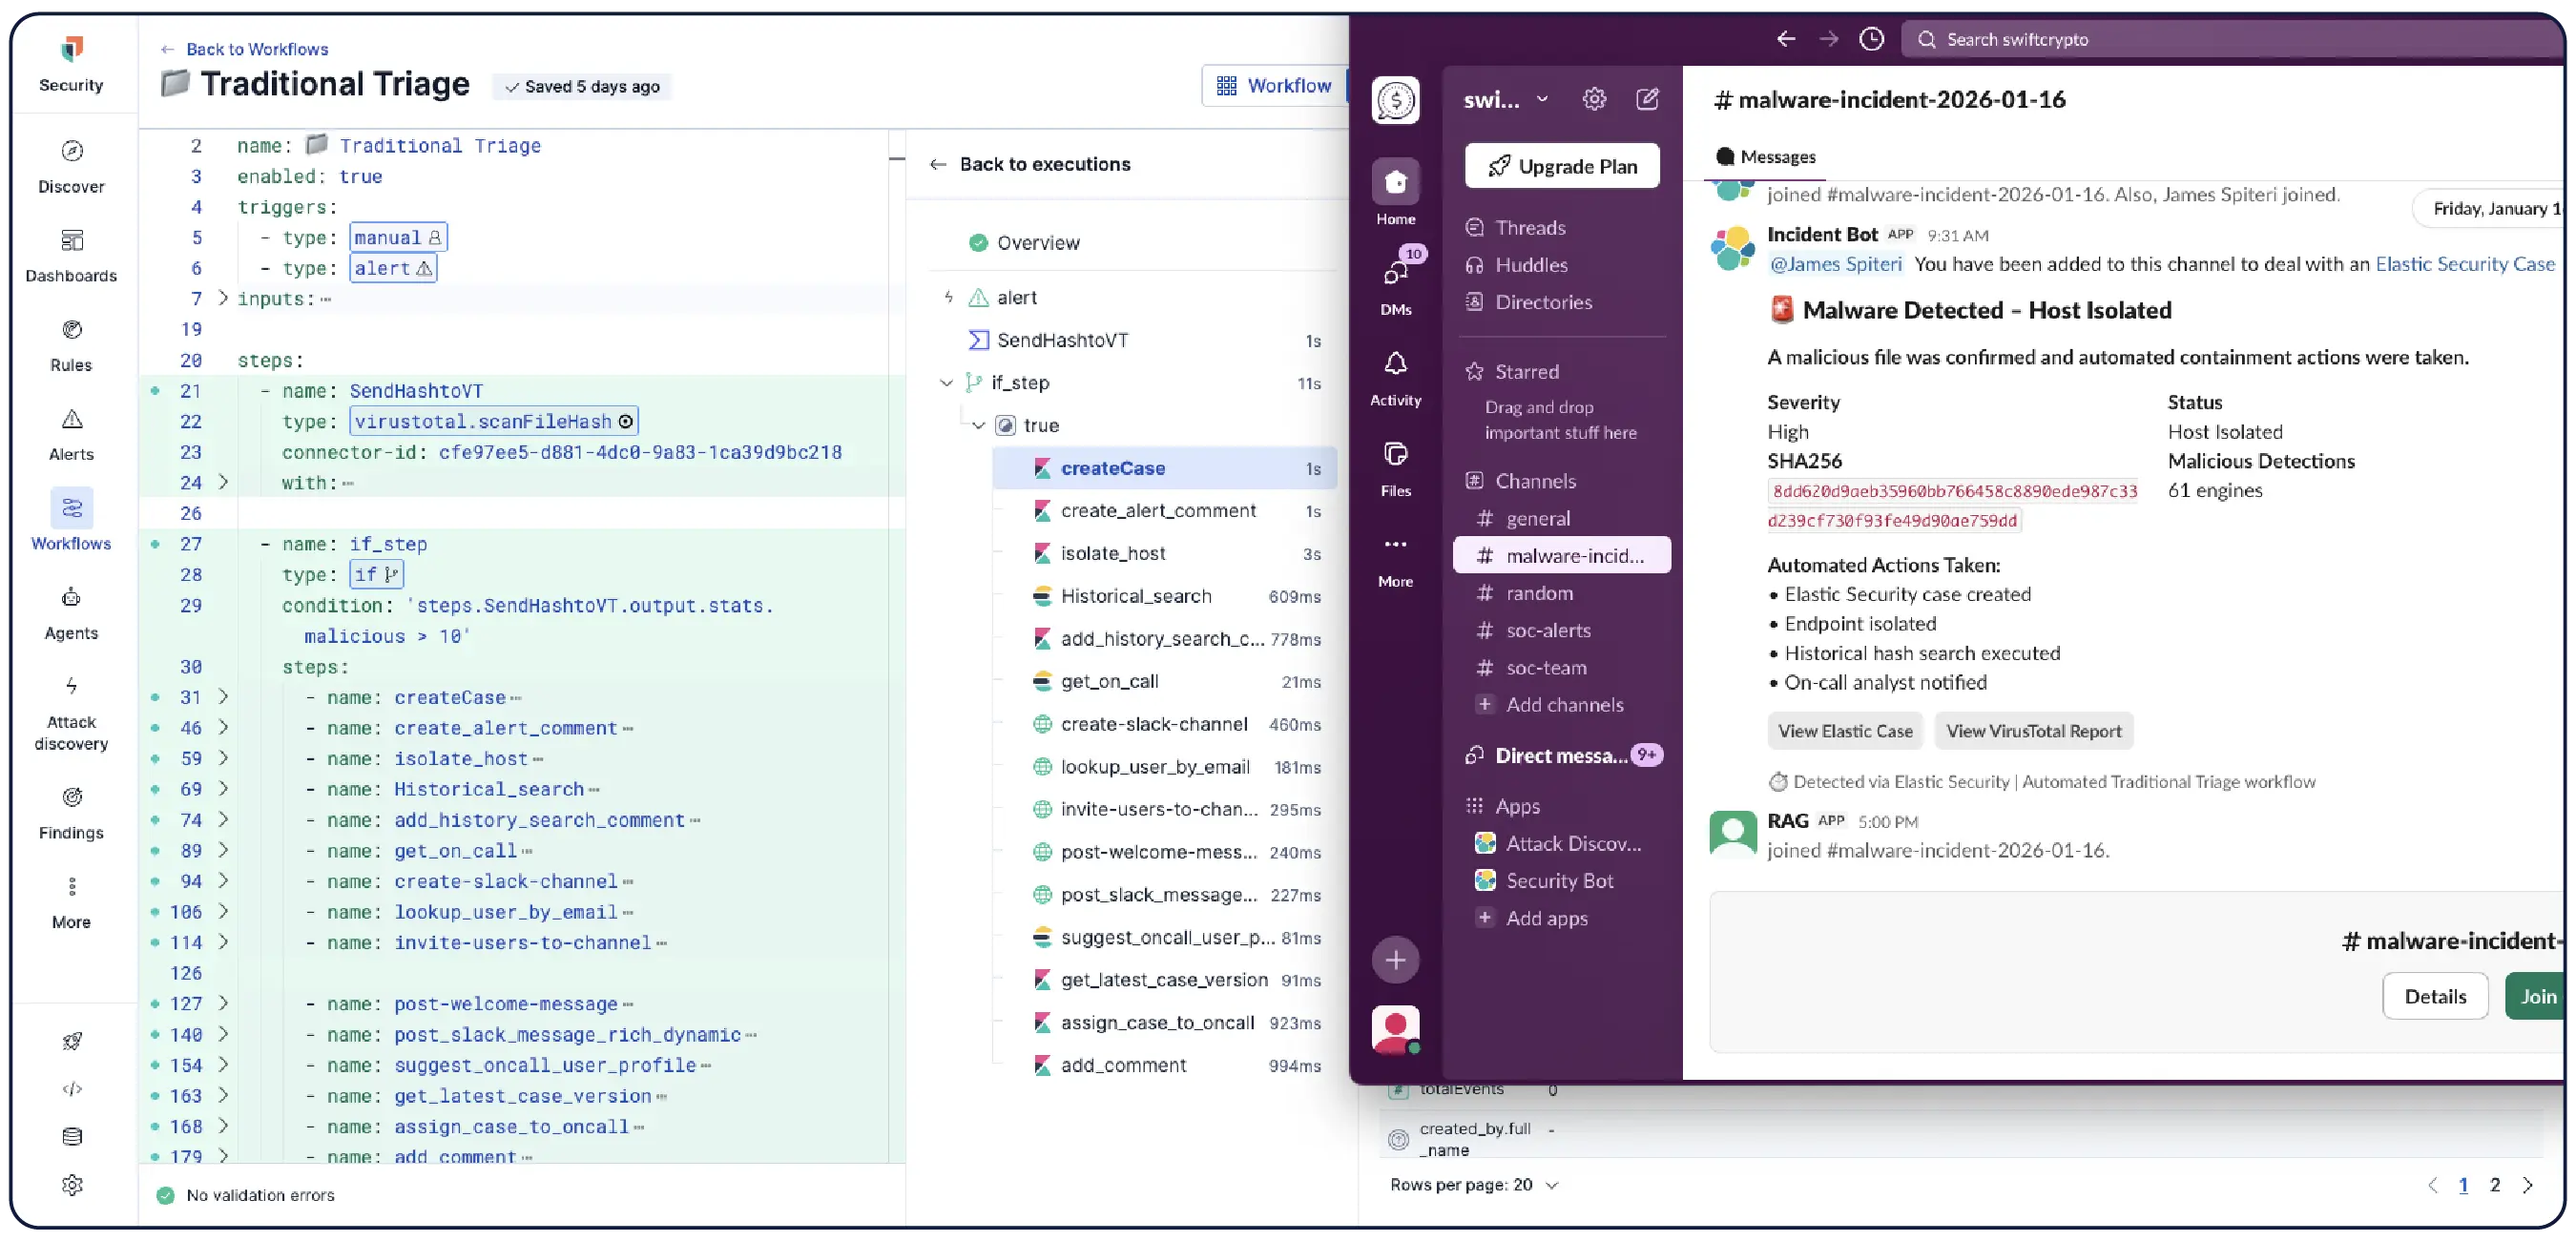
Implement structured workflows for the full SOC lifecycle. Triage queues, incident response with approval gates, case management, detection engineering, and AI skill monitoring all happen in one platform, no console switching.
Getting started is easy with AI


From data to response in minutes


Join the chat
Connect to Elastic Security's global community — from open conversations and collaboration to hardening our product.

Frequently asked questions
What is a SIEM?
What is a SIEM?
A SIEM (security information and event management) is the platform at the center of security operations. It collects and correlates data across an environment, detects threats, and gives analysts the visibility to investigate and respond. Modern SIEMs have evolved into agentic security operations platforms, with AI-driven detection, automated investigation, and native response across the full SOC lifecycle. Agents work the alerts and propose actions, and analysts make the consequential calls.
What is an AI-native SIEM?
What is an AI-native SIEM?
An AI-native SIEM is a security information and event management platform with AI in its core architecture, applied across data ingestion, normalization, detection, correlation, investigation, and response. The AI reasons across all ingested data, not just isolated alerts. Elastic's AI-native SIEM runs on Elasticsearch, the search database for AI, works with the model you choose, and shows the evidence and queries behind every conclusion, so analysts can check the work before acting.
How does Elastic SIEM support agentic security operations?
How does Elastic SIEM support agentic security operations?
Elastic Security is the open, agentic security operations platform, with SIEM, endpoint security, and native automation included. AlertZero, the agentic layer of Elastic Security, works the full lifecycle from ingestion through response: correlating alerts, investigating entities, and staging response plans as Proposed Actions. Elastic Workflows executes the response, with scripted playbooks for defined tasks and agentic reasoning for complex investigations. Elastic AI Agent ships with purpose-built skills for every SOC stage. Analysts handle judgment, verification, and approval.
What are AI skills in security operations?
What are AI skills in security operations?
AI skills are purpose-built capabilities that teach an AI agent how to perform a specific security task: threat hunting, alert analysis, detection engineering, entity analytics, and more. Unlike general-purpose AI, skills are designed for the exact workflows SOC analysts run every day. Each skill packages specialized instructions and tools for a single job, loading only when needed, which keeps the agent lightweight and accurate rather than overloaded with a bloated system prompt. Skills also work together without the analyst managing each handoff. Alert Analysis hands off to Entity Analytics, and Threat Hunting feeds the detection pipeline.
How do AI skills run in Elastic Security?
How do AI skills run in Elastic Security?
Elastic ships security skills out of the box with the Elastic AI Agent, with no configuration required. Out-of-the-box security skills cover threat hunting, alert analysis, detection engineering, entity analytics, and anomaly investigation. Platform skills for dashboard creation, workflow authoring, and graph creation are also available, letting analysts build dashboards, write automation, and visualize attack paths through conversation. Skills invoke each other automatically and run via Workflows or on-demand through Agent Builder. Teams can also build custom skills tailored to their environment. Skills are accessible inside Elastic Security or from any MCP-compatible AI tool including Claude, Cursor, and VS Code. Every reasoning step is visible and auditable.
How does Elastic SIEM work with AI tools like Claude and Cursor?
How does Elastic SIEM work with AI tools like Claude and Cursor?
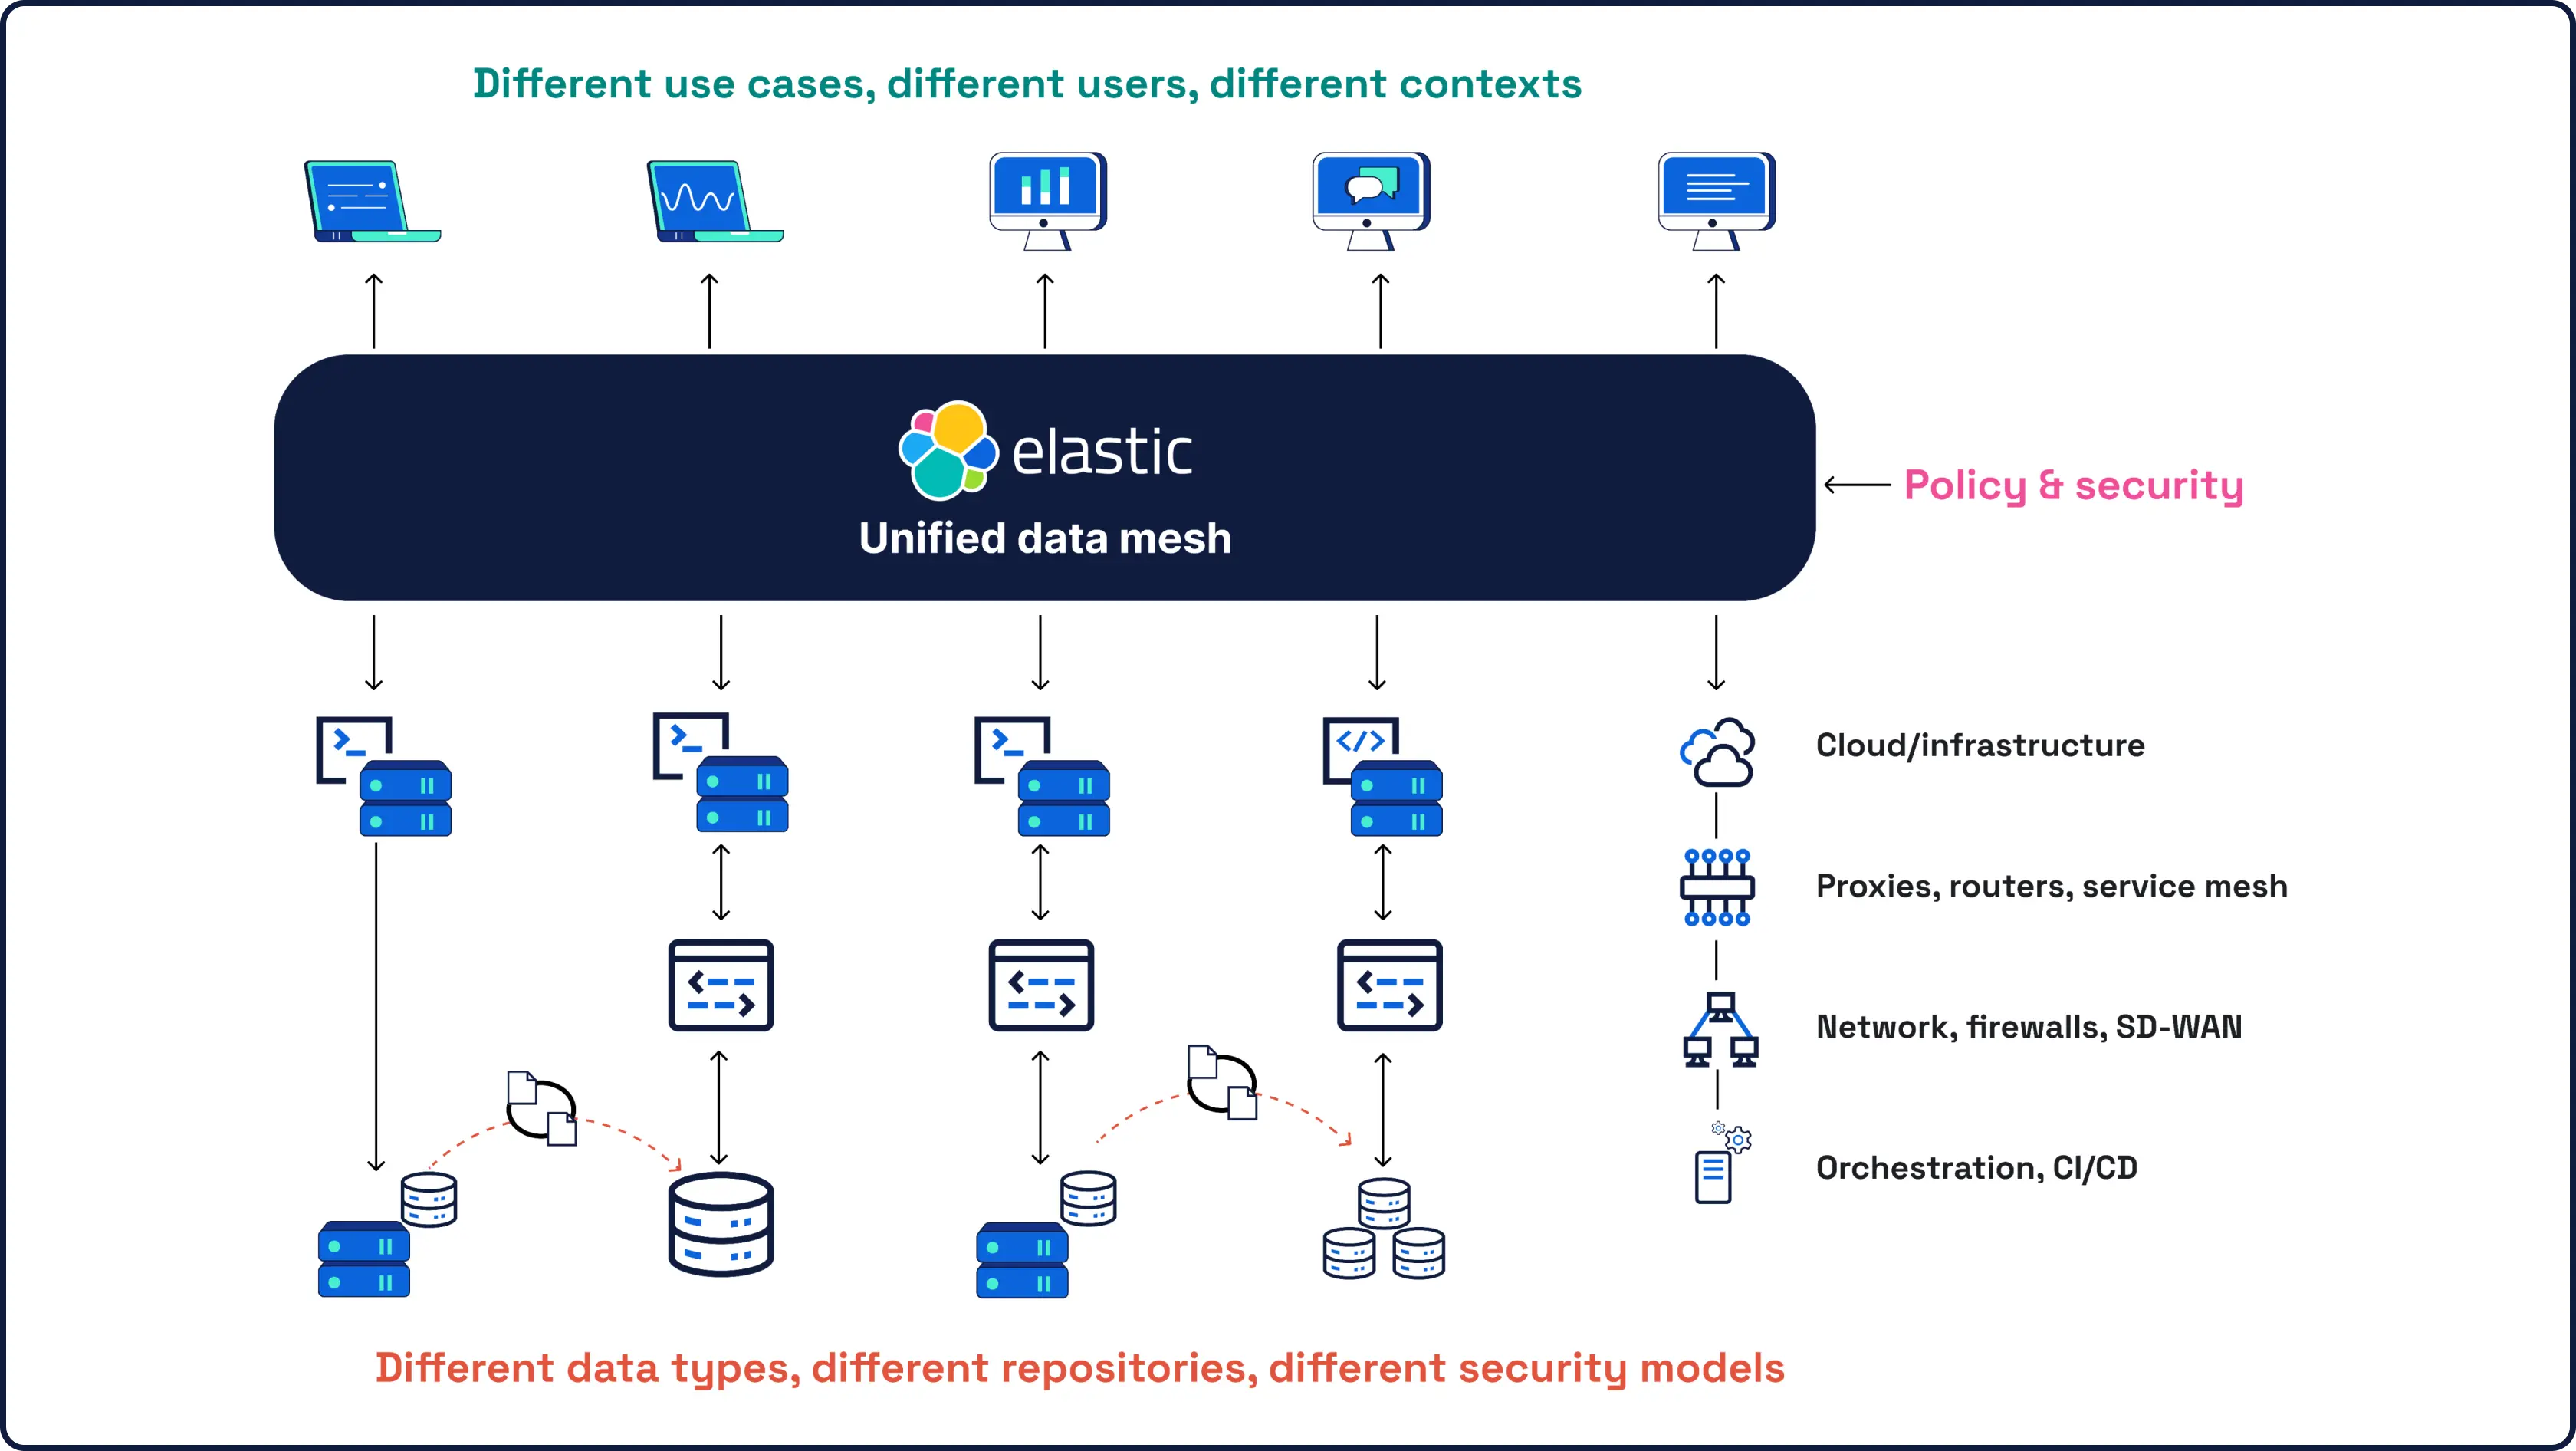
Elastic Security is accessible from any MCP-compatible AI tool, including Claude, Cursor, VS Code, and GitHub Copilot. Through the Elastic Security MCP App, analysts can triage alerts, run threat hunts, manage cases, and interact with detection rules without leaving the AI tool they're already working in. The same skills available inside Elastic Security are available externally. Security work happens wherever the analyst is, not just inside a dedicated console.
Does Elastic SIEM include SOAR?
Does Elastic SIEM include SOAR?
Yes. Elastic Workflows brings native SOAR directly into Elastic Security, where your security data already lives in the SIEM. It automates triage, enrichment, response, notification, and case management across every alert and investigation. Workflows combines scripted automation for defined tasks and agentic reasoning for complex investigations, enabling AI agents to act on their findings. There’s no separate SOAR to buy, integrate, or maintain, and no integration that breaks during an active incident.
What makes Elastic SIEM different from legacy SIEM platforms?
What makes Elastic SIEM different from legacy SIEM platforms?
Elastic is the agentic security operations platform that unifies SIEM, XDR, and native automation. Detection rules are developed by Elastic Security Threat Command, validated by the community, and open for review. The platform deploys on-premises, in the cloud, or in air-gapped environments without moving data. Where legacy SIEMs add barriers on endpoints, automation, AI, and data access, Elastic removes them.
What barriers do legacy SIEM platforms create?
What barriers do legacy SIEM platforms create?
Legacy security platforms add four barriers between SOC teams and the speed they need. Each was inefficient before adversarial AI and is now a liability.
- The endpoint barrier: Per-device pricing forces coverage tradeoffs, so teams leave endpoints unmonitored because full coverage costs too much. Elastic includes XDR and endpoint telemetry with no per-device fee, so a pricing model never decides which endpoints are covered.
- The integration barrier: A separate SOAR license is required to make the SIEM take action. Elastic Workflows is native to the platform, with no separate product to buy, integrate, or maintain.
- The black-box AI barrier: Proprietary AI hides its reasoning, leaving teams unable to validate decisions made on their behalf. Elastic's AI shows the prompts, queries, and reasoning behind every decision and works with any LLM, including on-premises models for air-gapped environments.
- The data access barrier: Rehydration delays and ingestion caps put historical data out of reach during active investigations. Elastic queries data where it lives, with years of historical data searchable in the same query as live data and no rehydration wait or penalty.
Together, these four barriers fragment security operations and create gaps adversaries exploit. Elastic is designed to remove all four.
Can Elastic SIEM run in air-gapped or on-premises environments?
Can Elastic SIEM run in air-gapped or on-premises environments?
Yes. Elastic deploys on-premises, in the cloud, or in air-gapped environments with no data movement required. Federated search runs queries across distributed deployments without centralizing data. AI reasoning supports on-premises LLMs for air-gapped environments, with no dependency on a vendor's cloud model. Elastic Cloud holds certifications including PCI DSS, HIPAA, FedRAMP, GDPR, and TISAX, with full documentation available in our Trust Center. This makes Elastic the platform of choice for defense, government, and regulated industries with strict data residency and compliance requirements.
What data sources does Elastic SIEM support?
What data sources does Elastic SIEM support?
When a new source connects, the platform identifies the data type, maps the schema automatically, and recommends detection rules, with no pipeline engineering required. Data is normalized to the Elastic Common Schema (ECS), an open source standard aligned with OpenTelemetry, so a detection written once works across sources and OpenTelemetry data is supported natively.