Elastic 演示画廊
从 Kibana 仪表板、Canvas 工作区、Elasticsearch SQL 代码片段到机器学习作业,这些小示例将带您探索 Elastic Stack 的方方面面。别只是看看,亲自试试吧。
 
筛选
类型
解决方案
Elastic 功能
Observability
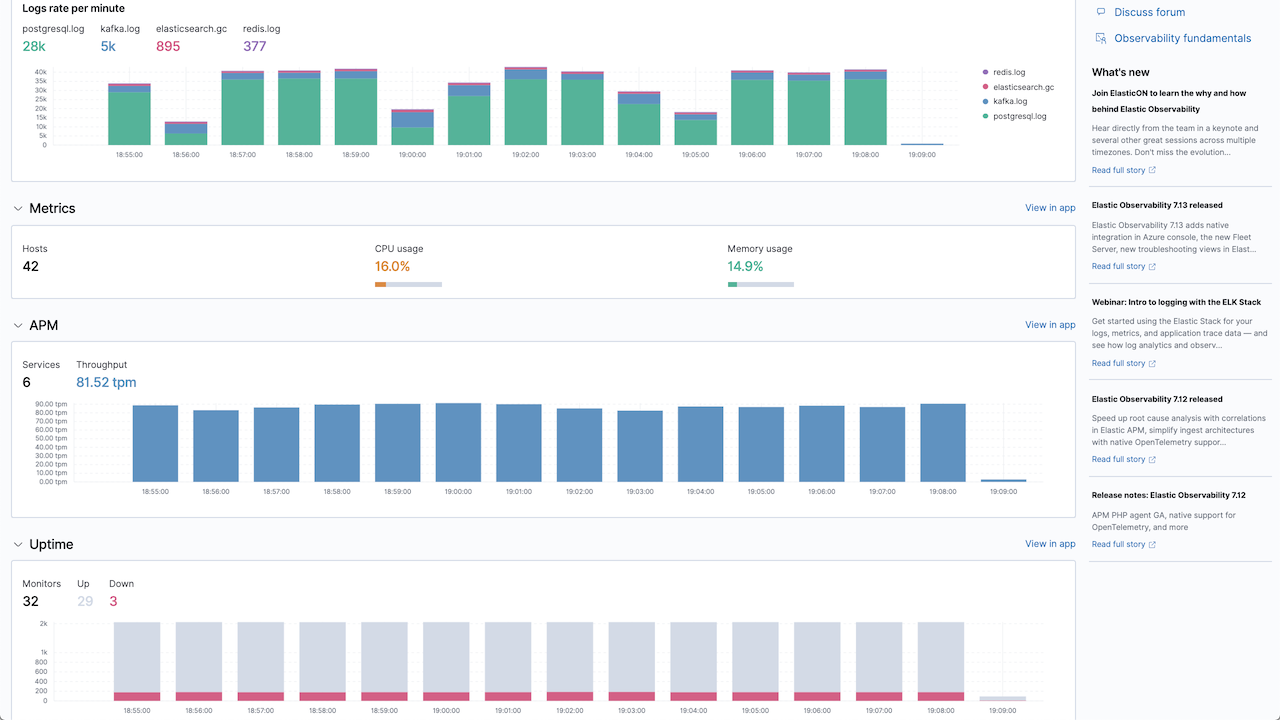
可观测性概述
尝试此动手演示,了解如何将日志、指标和痕迹整合在一起,从而全面了解您的应用环境。
Security
Accelerate data onboarding with Elastic AI Import
Elastic’s Automatic Import feature saves analysts from the lengthy process of building custom data parsers, allowing them to instead focus on threat hunting and improve their organization’s security posture. In this demo, see how Elastic AI Import feature can process both supported or unsupported log sources, normalizing and enriching them for analysts.
Security
Elastic Security: Agentic Security Operations Platform
Step through Elastic’s agentic SOC live. Watch autonomous agents correlate and investigate a real alert end-to-end, then stage a response through Elastic Workflows—with deterministic playbooks and agentic reasoning working side by side. You stay in control at every gate, approving agent actions and seeing exactly how judgment and verification remain with the analyst while the busywork runs itself.
Security
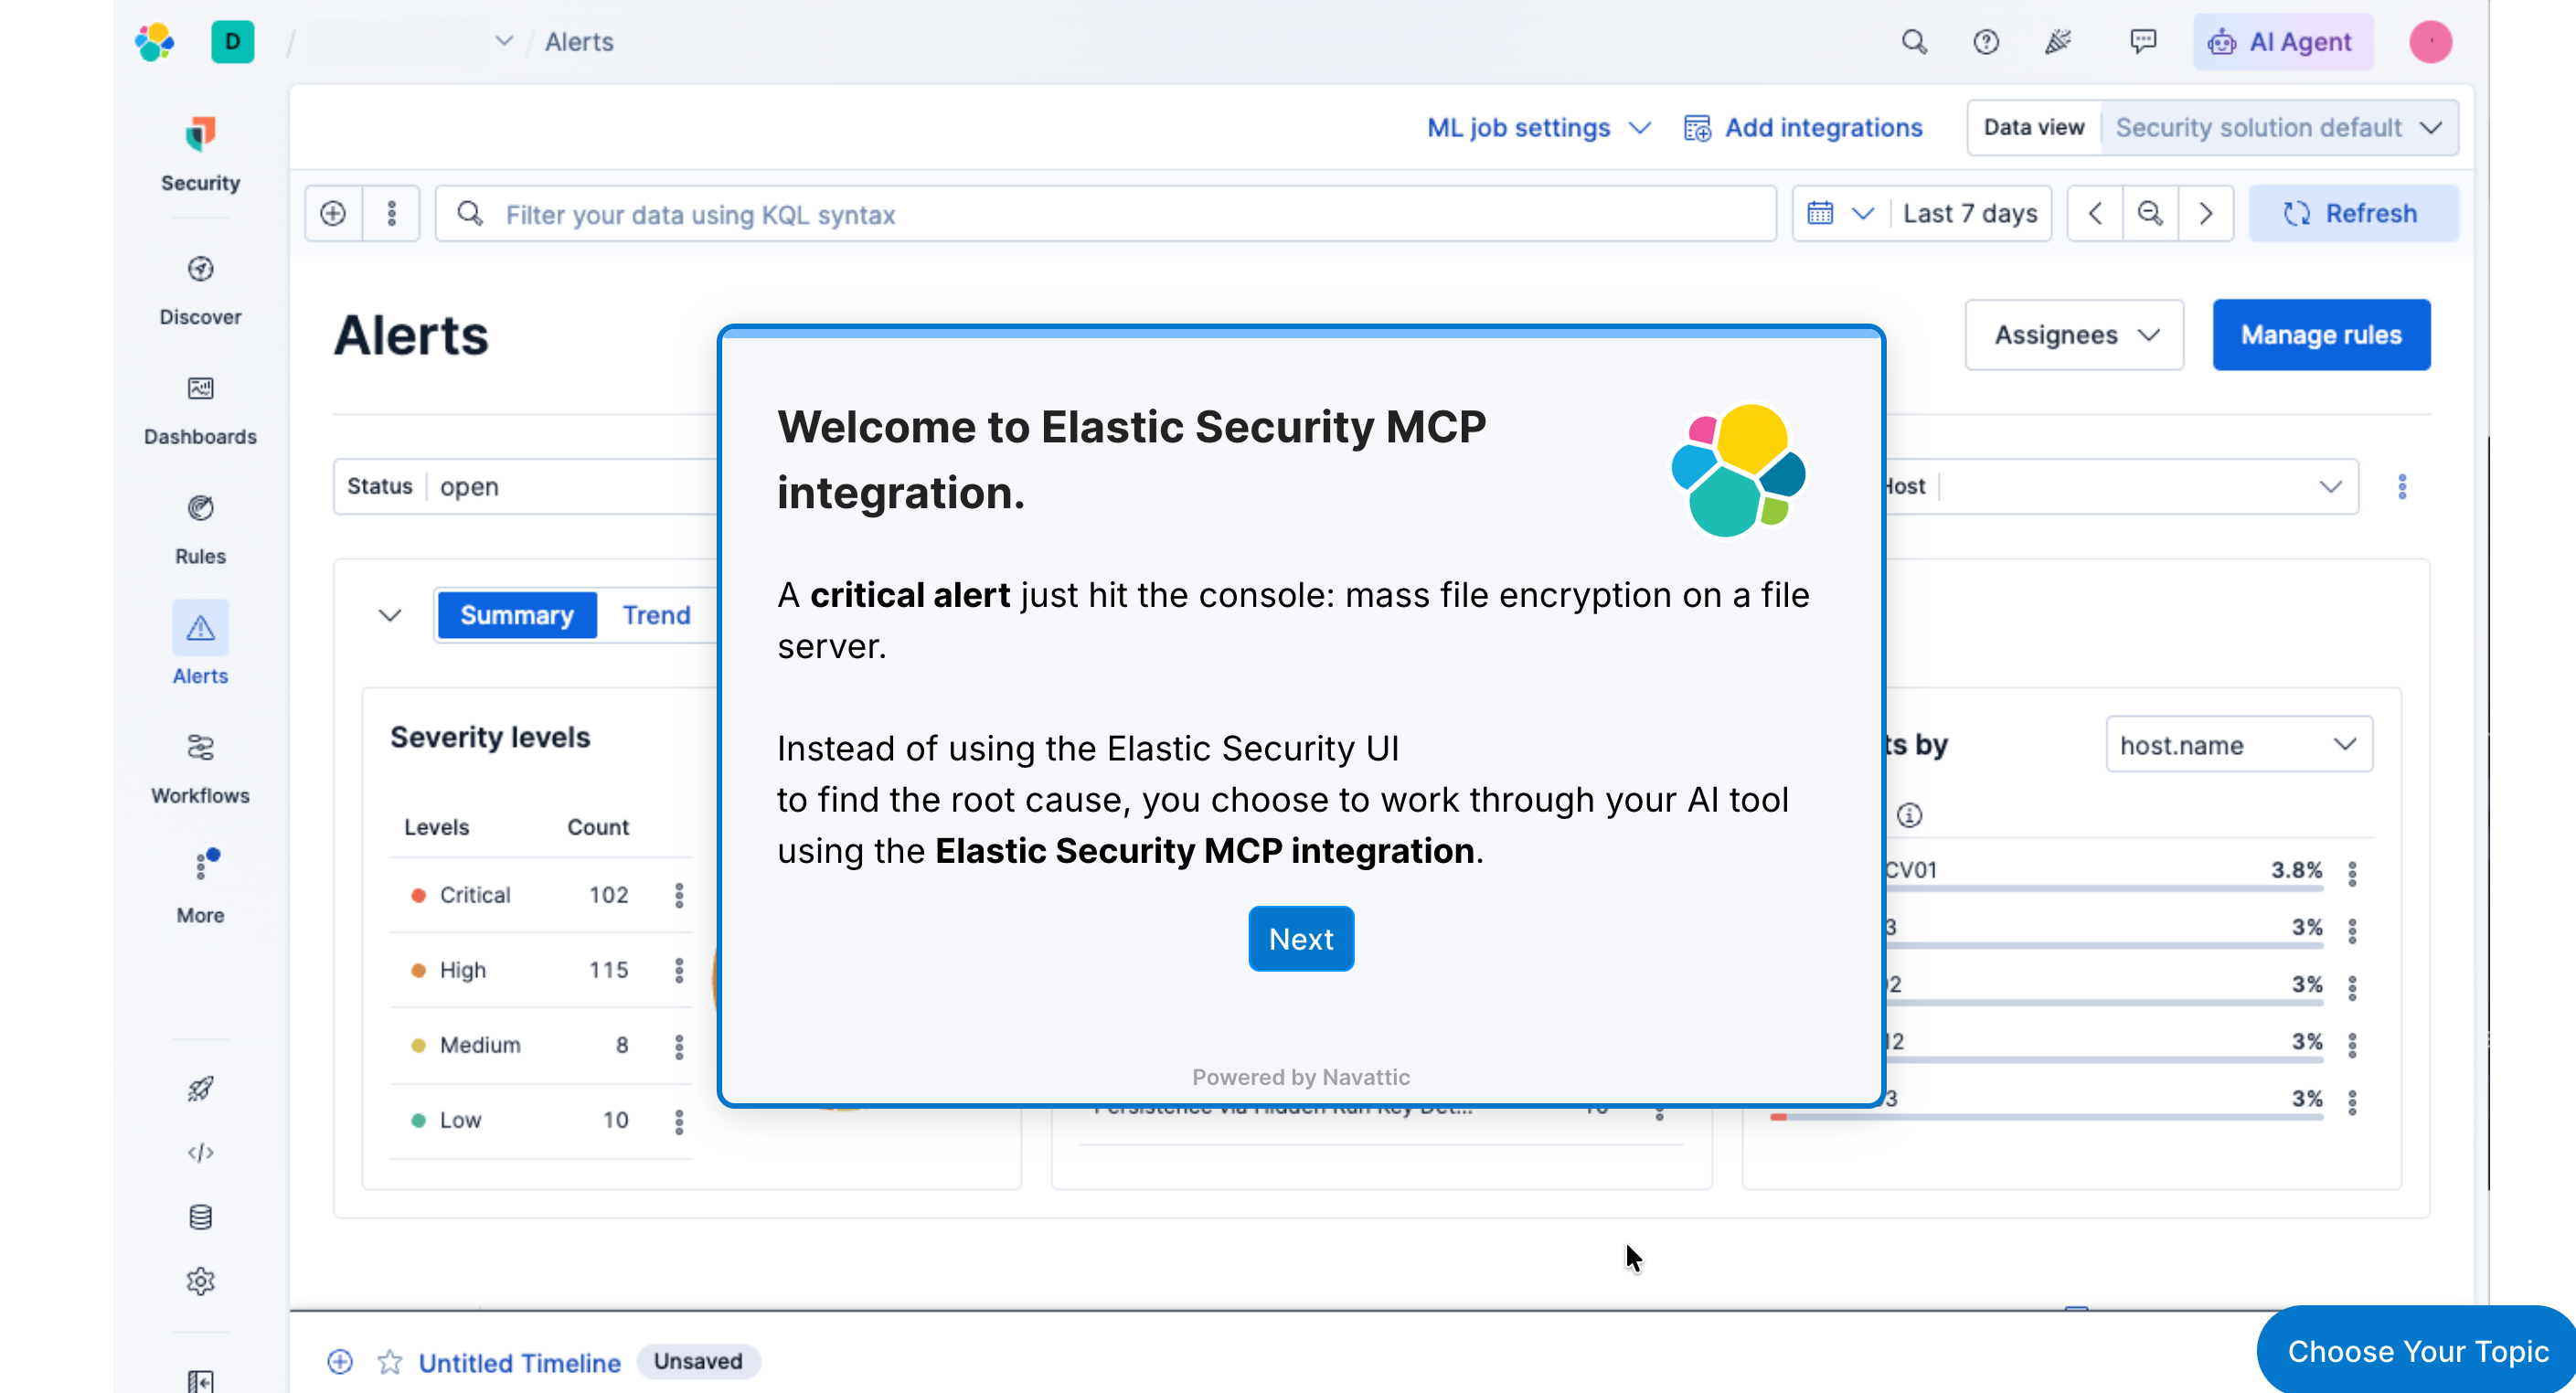
Elastic Security MCP Integration
A critical alert just hit the Elastic Security console: mass file encryption on a file server. Instead of using the web UI to find the root cause, you choose to work through your AI tool using the Elastic Security MCP integration.
Security
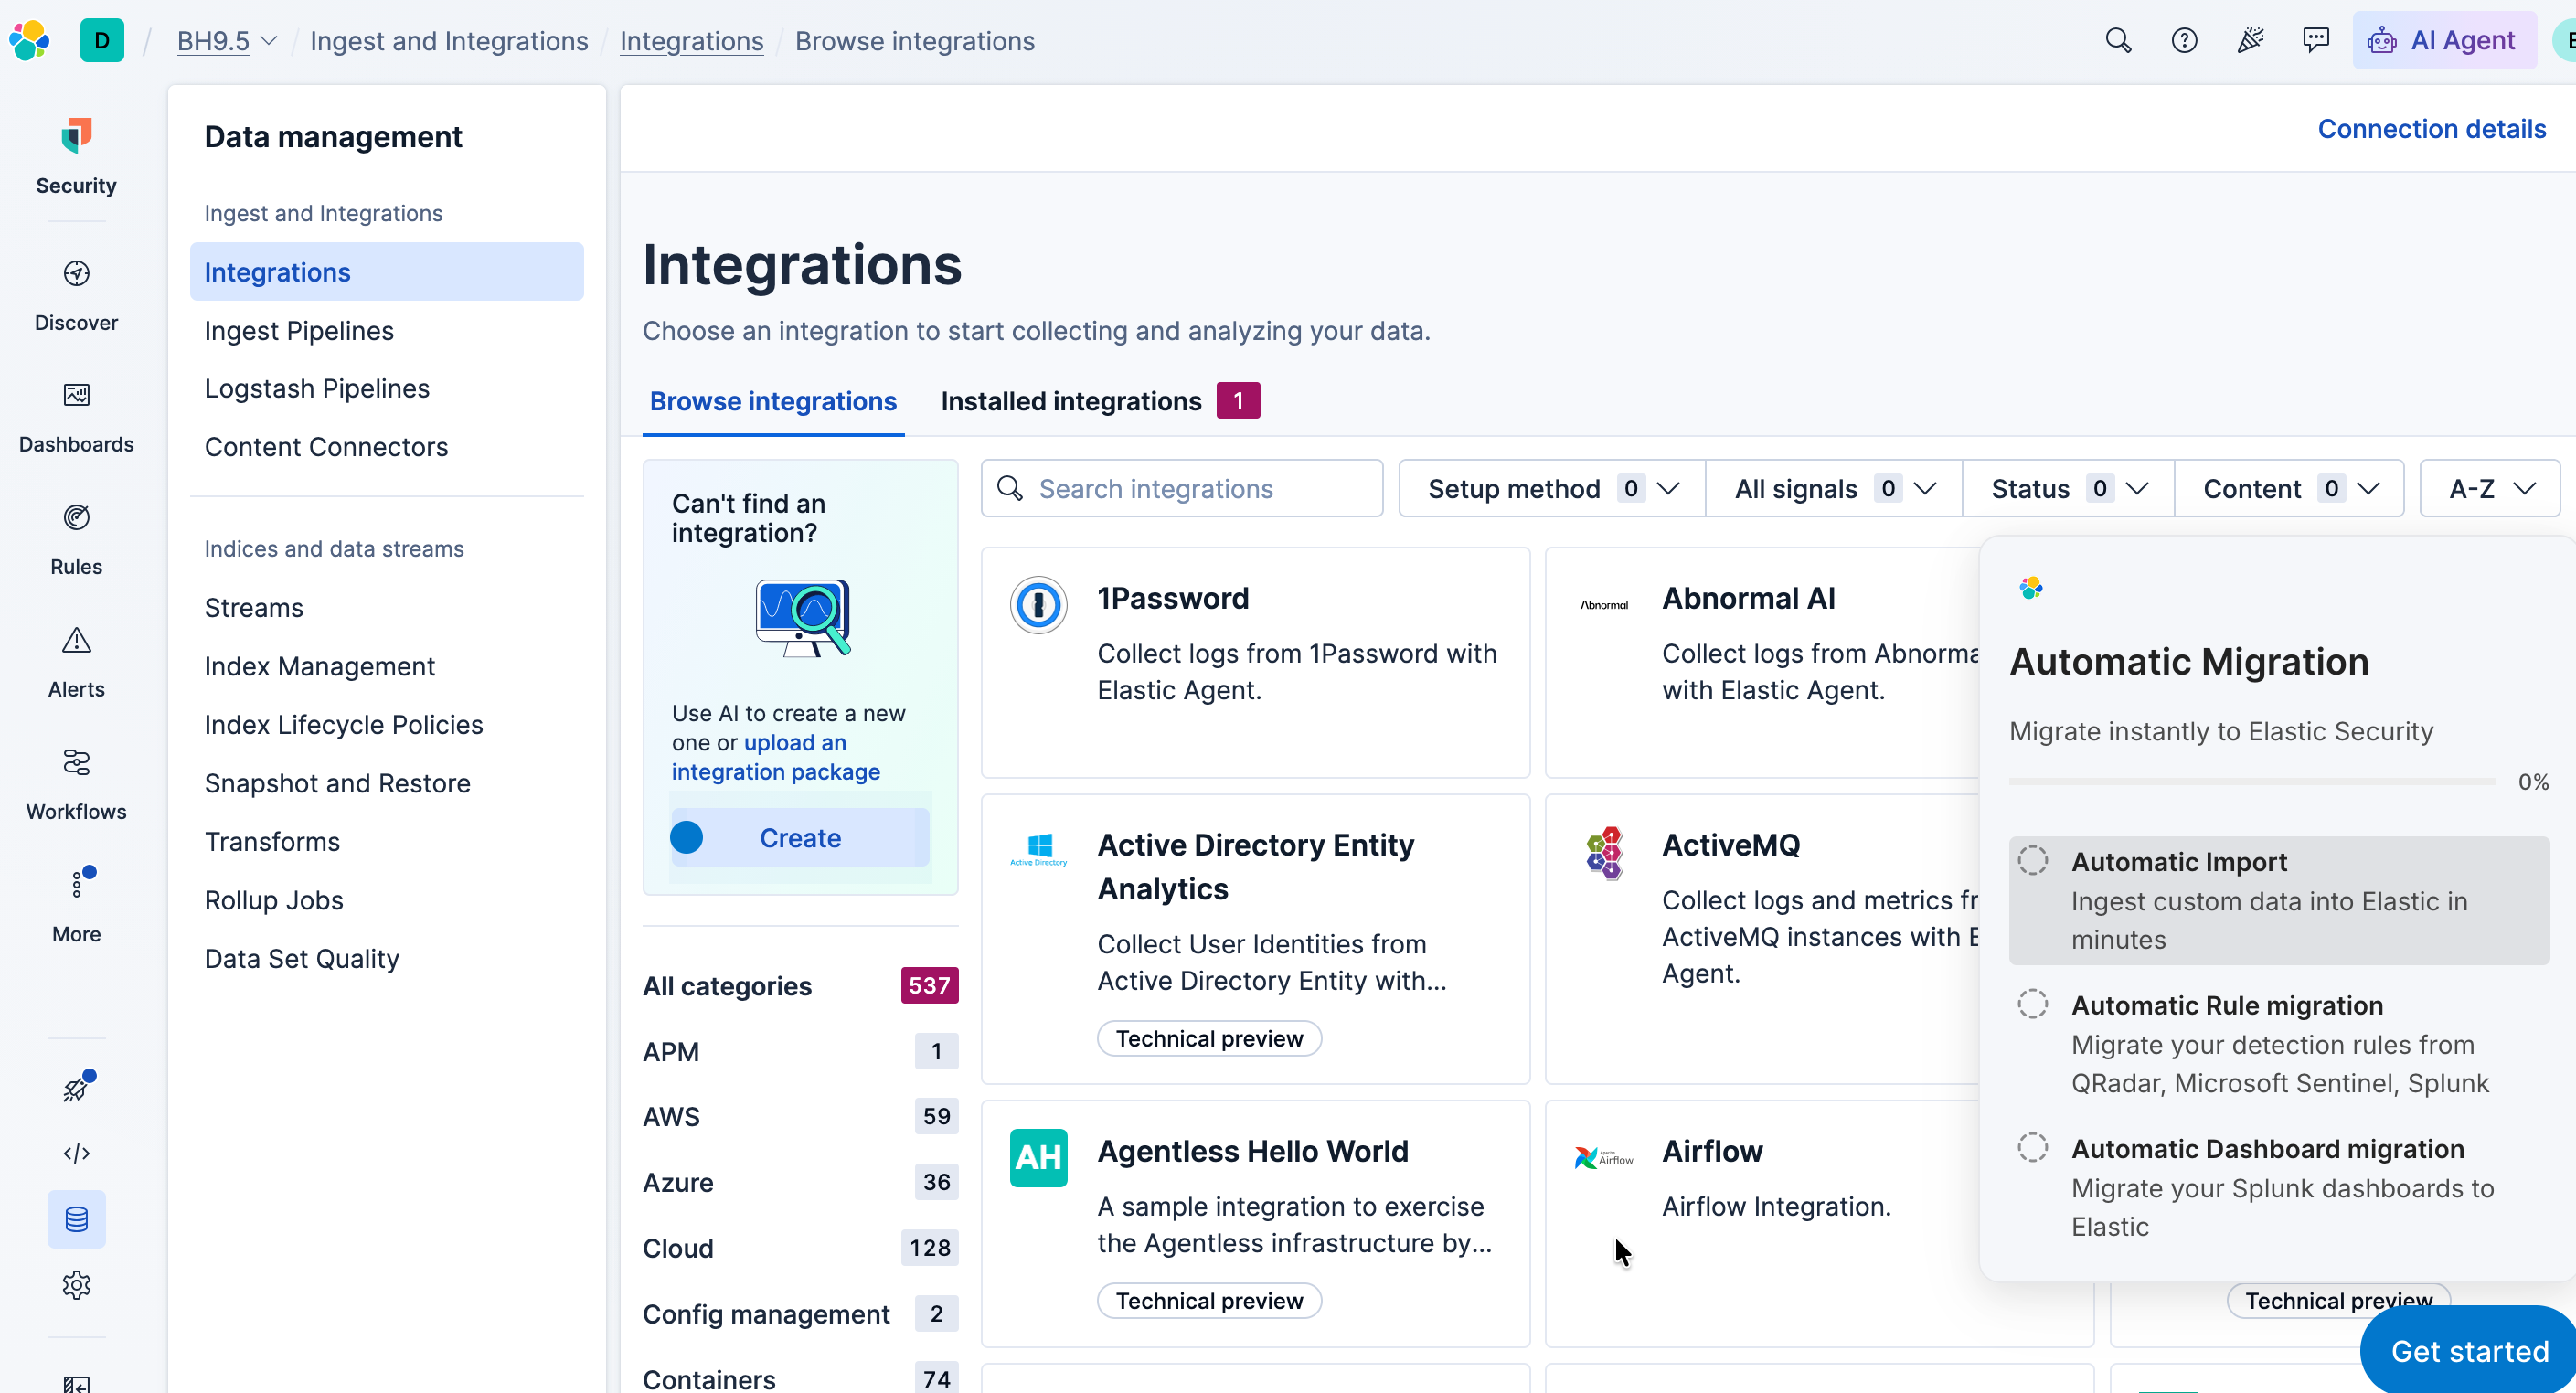
Migrate to Elastic Security
Onboard without the rip-and-replace. Watch Automatic Import build a custom integration on the fly—just upload sample logs and bring in any source—then let Automatic Migration map and convert your existing detection rules from Splunk, QRadar, and Microsoft Sentinel in minutes. Everything lands in one open schema, unified and analysis-ready the moment it arrives.
Security
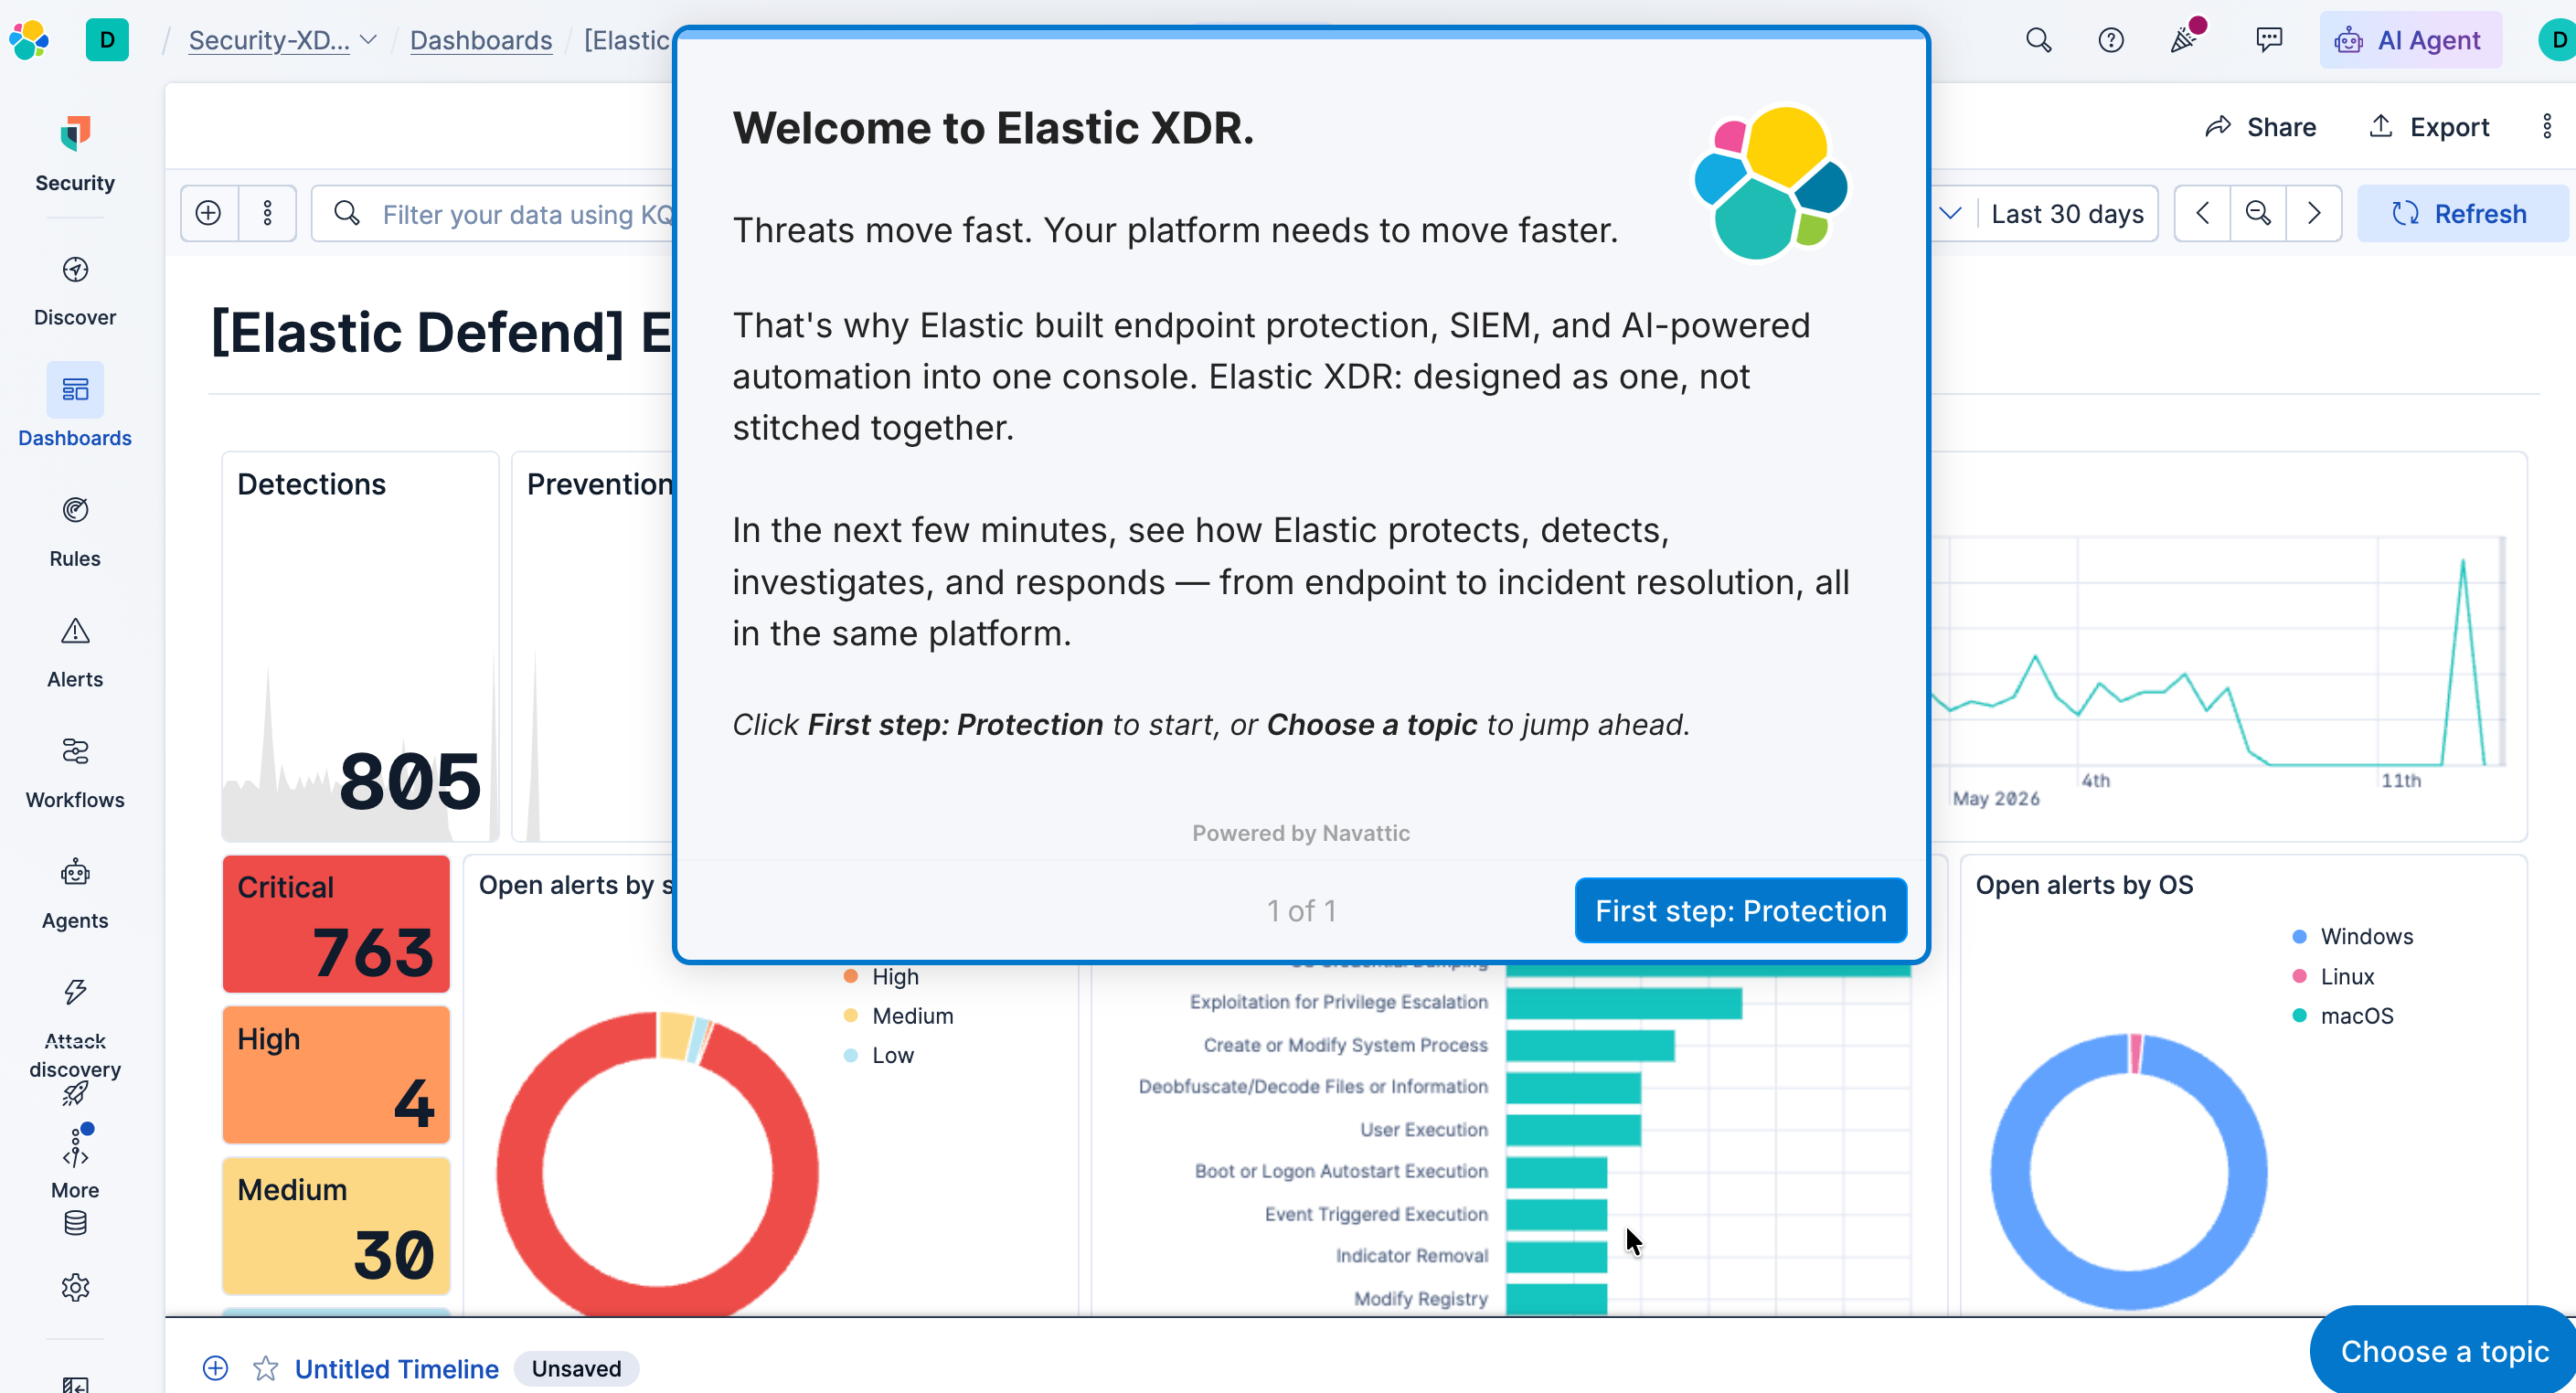
Elastic Security XDR
Threats move fast. Your platform needs to move faster. In this flow see how Elastic XDR protects, detects, investigates, and responds — from endpoint to incident resolution, all in the same platform.

安全性
Attack Discovery
Attack Discovery 可将数百个警报分类为少数真正重要的攻击,并在直观的接口中返回结果,让您能够快速了解所呈现的攻击并立即采取后续行动,等等。

Observability
使用 OpenTelemetry 摄取日志、指标和链路追踪数据
Observability 101:第 2 课(共 4 课):使用 Elastic Distribution for OpenTelemetry (EDOT) 接入日志、指标和链路追踪数据,开启 Elastic Observability 之旅。在这个 15 分钟的实操练习中,使用 OpenTelemetry (OTel) 采集器,让日志结构清晰、定义明确。
